

Chimera
 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
ids-ips-evasionpayload-developmentpayload-generation+2
1.6k
tokyoneon/chimeraChimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
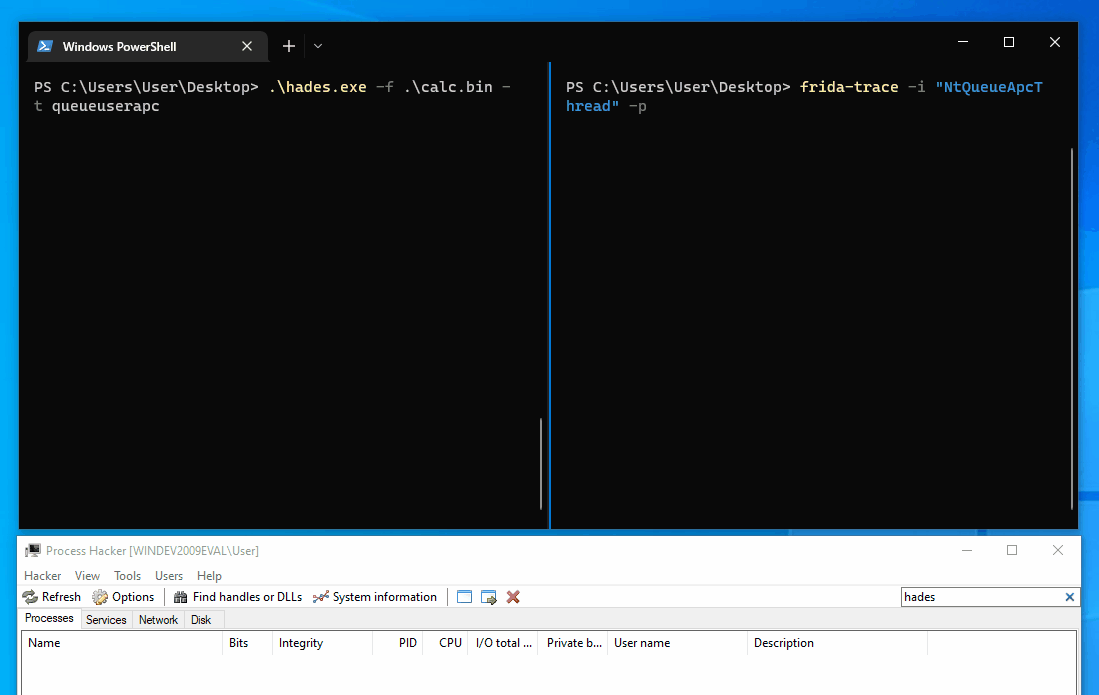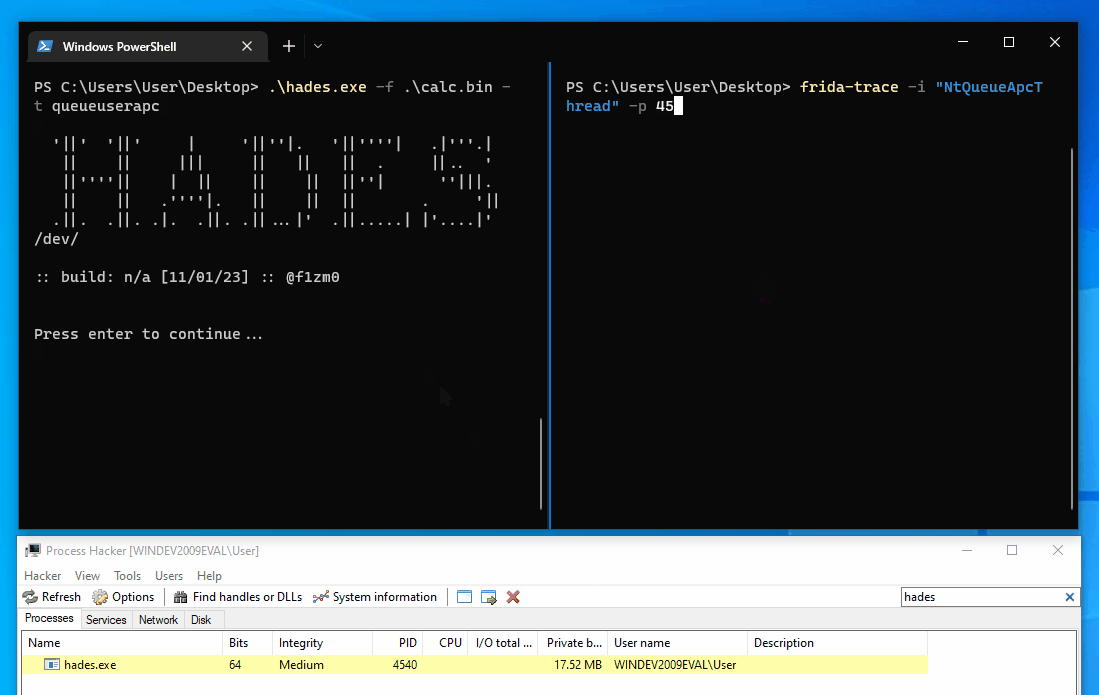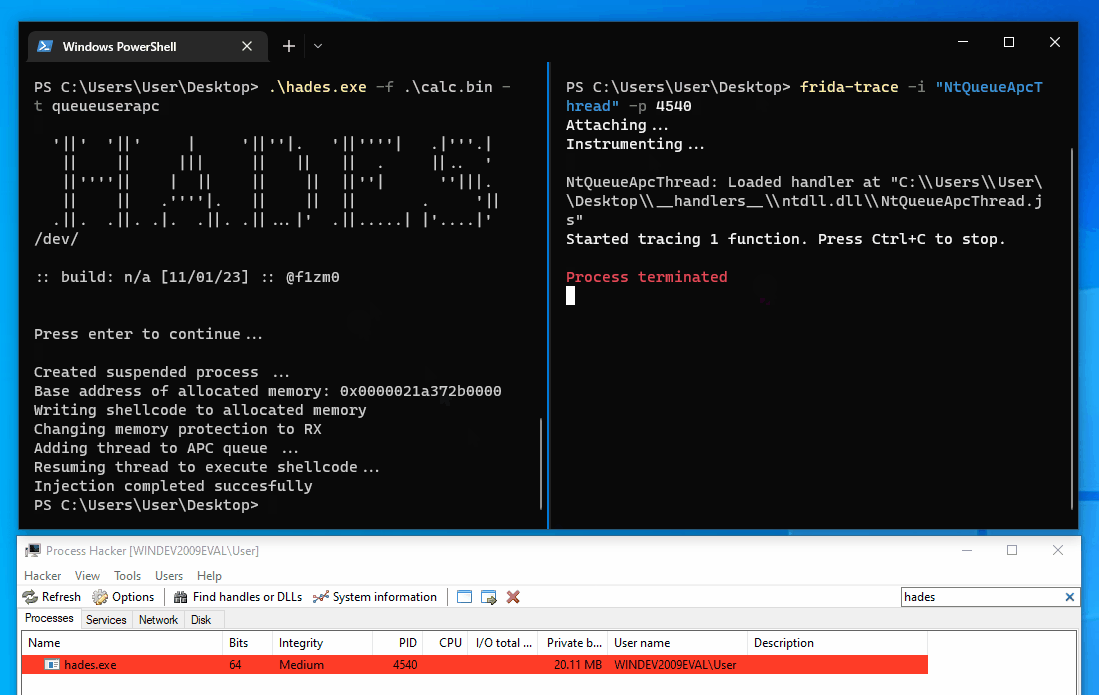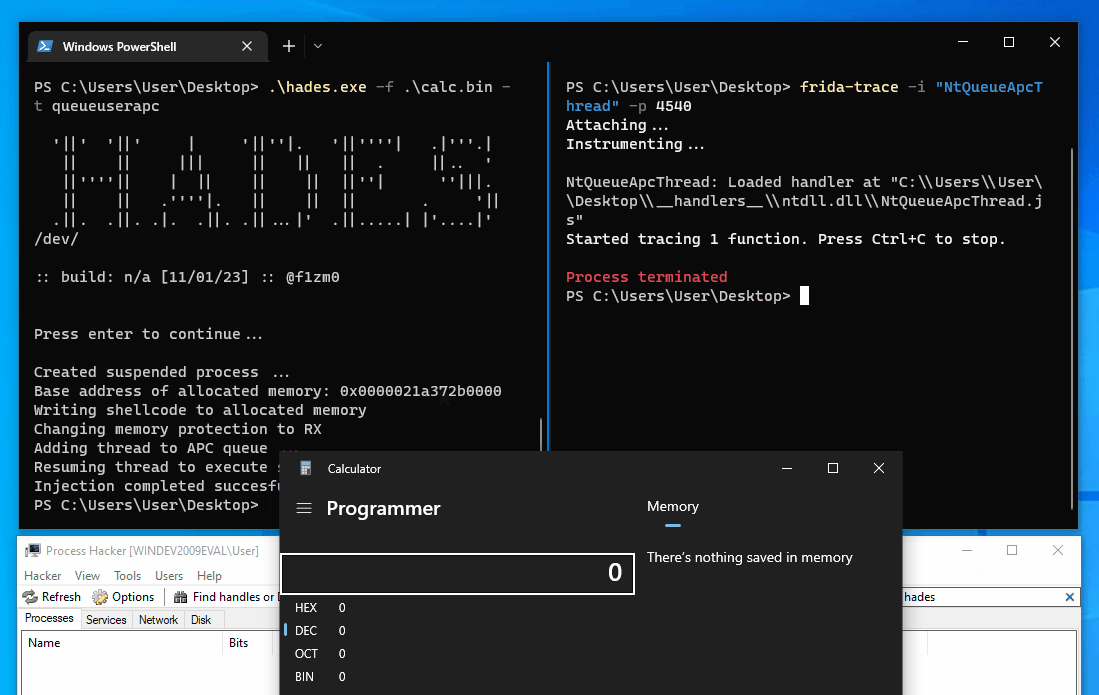 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 whu-enjoy/cve-2012-1889
这里保存着我学习CVE-2012-1889这个漏洞的利用所用到的文件
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听