
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
99 results
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k3 days ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
ShellcodeCompiler preview

ShellcodeCompiler

GitHubnytrorst/shellcodecompiler

Shellcode Compiler

binary-exploitationexploitationpayload-development+2
1.2k2 years ago
donutCS preview

donutCS

GitHubn1xbyte/donutcs

dem sharp donuts

exploit-frameworkspayload-generationpenetration-testing+1
2015 years ago
nimcrypt preview

nimcrypt

GitHubicyguider/nimcrypt

PE Crypter written in Nim

binary-analysiscode-analysiseducation+9
1025 years ago
watchTowr-vs-Citrix-Netscaler-PreAuth-RCE-CVE-2026-8452 preview

watchTowr-vs-Citrix-Netscaler-PreAuth-RCE-CVE-2026-8452

GitHubwatchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452

CVE-2026-8452 PreAuth RCE

exploitationpayload-developmentred-teaming+3
651 month ago
xeca preview

xeca

GitHubpostrequest/xeca

PowerShell payload generator

command-and-controlctfexploitation+6
1215 years ago
CVE-2026-6307 preview

CVE-2026-6307

GitHub0xsha/cve-2026-6307

Google Chrome CVE-2026-6307 PoC

binary-exploitationeducationexploitation+6
673 months ago
Neo preview

Neo

GitHubstillbigjosh/neo

The NeoC2 Framework

command-and-controlexploit-frameworksids-ips-evasion+8
3815 days ago
CVE-2021-40444 preview

CVE-2021-40444

GitHubmracumen/cve-2021-40444

Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit

binary-analysisexploitationmalware-analysis+3
24 years ago
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
268 days ago
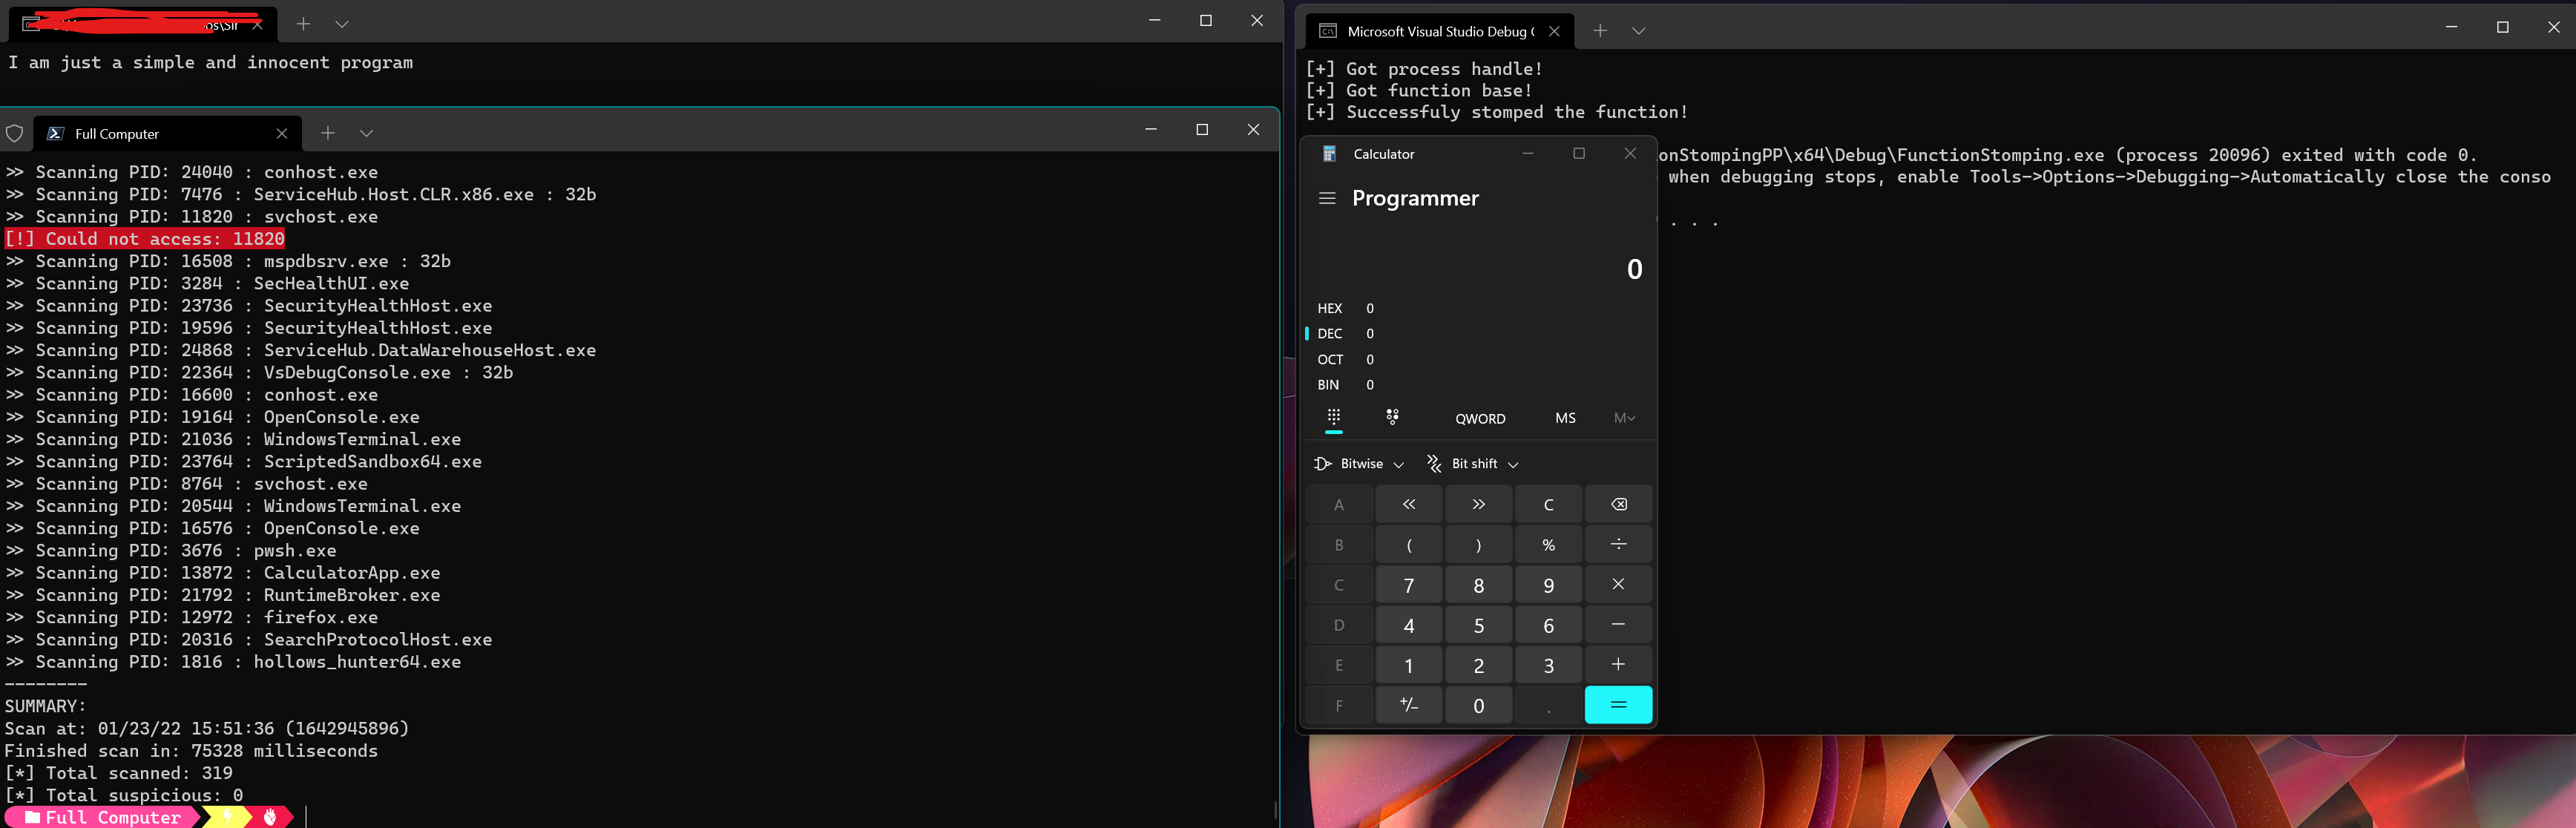
FunctionStomping preview
Archived

FunctionStomping

GitHubidov31/functionstomping

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

binary-exploitationdefensive-toolsexploitation+7
7063 years ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
EQGRP preview

EQGRP

GitHubx0rz/eqgrp

Decrypted content of eqgrp-auction-file.tar.xz

command-and-controldata-exfiltrationexploitation+8
4.2k9 years ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
Winpayloads preview

Winpayloads

GitHubnccgroup/winpayloads

Undetectable Windows Payload Generation

command-and-controlexploit-frameworkslateral-movement+9
1.6k7 years ago
SysWhispers2 preview

SysWhispers2

GitHubjthuraisamy/syswhispers2

AV/EDR evasion via direct system calls.
binary-exploitationdefensive-toolsids-ips-evasion+5
1.8k4 years ago
pe_to_shellcode preview

pe_to_shellcode

GitHubhasherezade/pe_to_shellcode

Converts PE into a shellcode

binary-exploitationexploitationids-ips-evasion+5
2.8k1 year ago
Previous123456Next
