Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
156 results
ShellcodeFluctuation preview

ShellcodeFluctuation

GitHubmgeeky/shellcodefluctuation

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

adversarial-attackpayload-developmentpayload-generation+4
1.1k
4 years ago
Clematis preview

Clematis

GitHubcblabresearch/clematis

PE to shellcode

exploitationpayload-developmentpayload-generation+3
2861 year ago
hacking-team-windows-kernel-lpe preview

hacking-team-windows-kernel-lpe

GitHubvlad902/hacking-team-windows-kernel-lpe

Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.

binary-exploitationexploitationpayload-generation+2
20311 years ago
micr0_shell preview

micr0_shell

GitHubsenzee1984/micr0_shell

micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.

exploitationpayload-developmentpayload-generation+2
2245 months ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

binary-analysisencryption-decryption-toolsexploitation+5
18817 days ago
SILVERPICK preview

SILVERPICK

GitHubwinterknife/silverpick

Windows User-Mode Shellcode Development Framework (WUMSDF)

exploitationpayload-developmentred-teaming+2
1592 months ago
DbgNexum preview

DbgNexum

GitHubdis0rder0x00/dbgnexum

Shellcode injection using the Windows Debugging API

binary-exploitationexploitationpayload-development+6
1818 months ago
watchTowr-vs-Citrix-Netscaler-PreAuth-RCE-CVE-2026-8452 preview

watchTowr-vs-Citrix-Netscaler-PreAuth-RCE-CVE-2026-8452

GitHubwatchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452

CVE-2026-8452 PreAuth RCE

exploitationpayload-developmentred-teaming+3
631 month ago
xeca preview

xeca

GitHubpostrequest/xeca

PowerShell payload generator

command-and-controlctfexploitation+6
1204 years ago
malasada preview

malasada

GitHubsliverarmory/malasada

Linux Shared Library to Shellcode Loader

binary-exploitationexploitationpayload-development+5
1017 months ago
CVE-2021-40444 preview

CVE-2021-40444

GitHubmracumen/cve-2021-40444

Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit

binary-analysisexploitationmalware-analysis+3
24 years ago
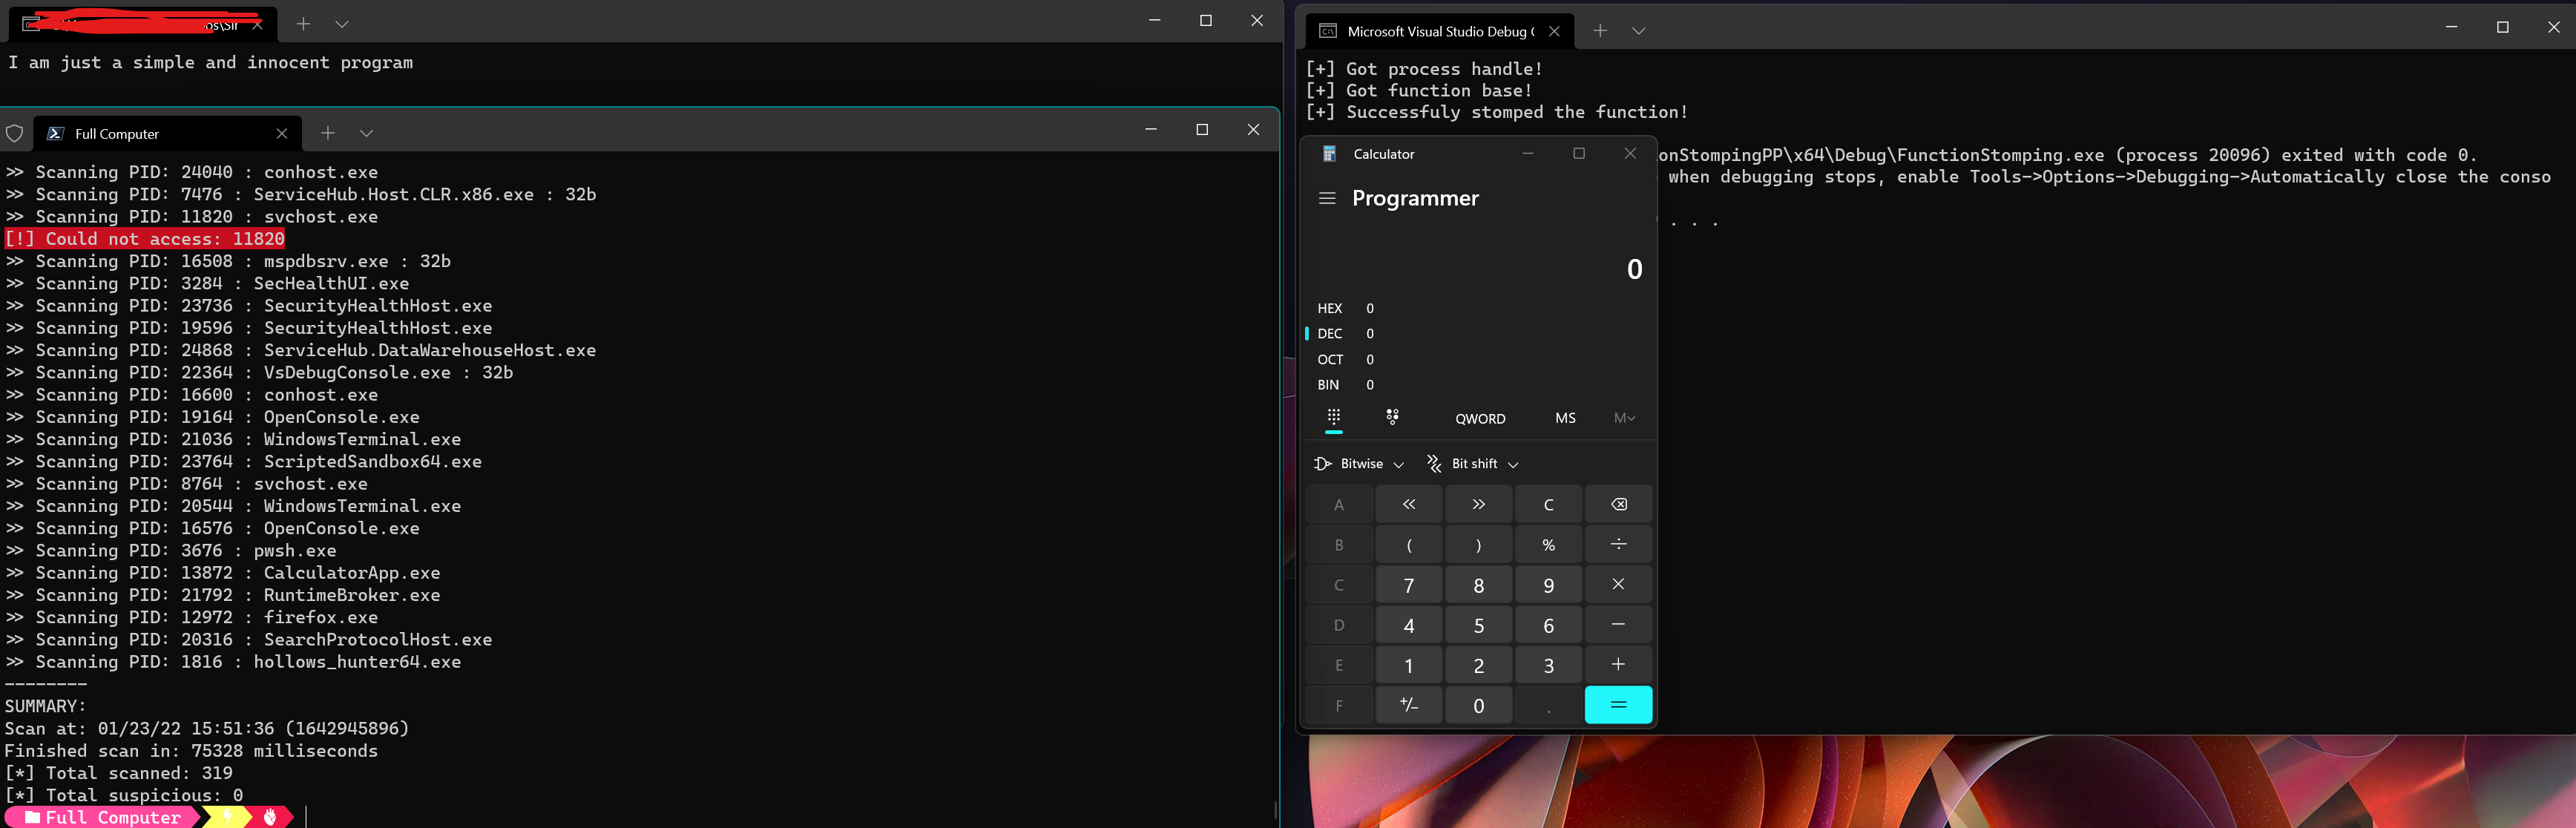
FunctionStomping preview
Archived

FunctionStomping

GitHubidov31/functionstomping

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

binary-exploitationdefensive-toolsexploitation+7
7062 years ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
11.8k1 day ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k9 days ago
EQGRP preview

EQGRP

GitHubx0rz/eqgrp

Decrypted content of eqgrp-auction-file.tar.xz

command-and-controldata-exfiltrationexploitation+8
4.2k9 years ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
SysWhispers2 preview

SysWhispers2

GitHubjthuraisamy/syswhispers2

AV/EDR evasion via direct system calls.

binary-exploitationdefensive-toolsids-ips-evasion+5
1.8k4 years ago
pe_to_shellcode preview

pe_to_shellcode

GitHubhasherezade/pe_to_shellcode

Converts PE into a shellcode

binary-exploitationexploitationids-ips-evasion+5
2.8k1 year ago
Previous1…345…9Next