

Ghostfuscator
 alberties/ghostfuscator
The Python Password-Protected Obfuscator
encryption-decryption-toolspayload-generationshellcode-generation
alberties/ghostfuscatorThe Python Password-Protected Obfuscator
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
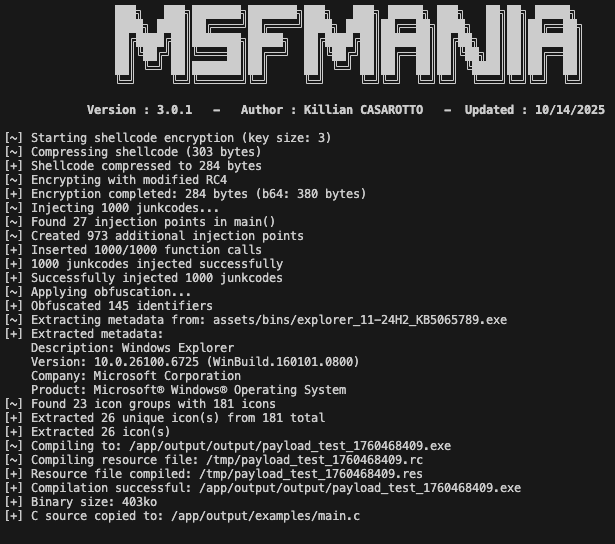 lepotekil/msfmania
Python AV Evasion Tools
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
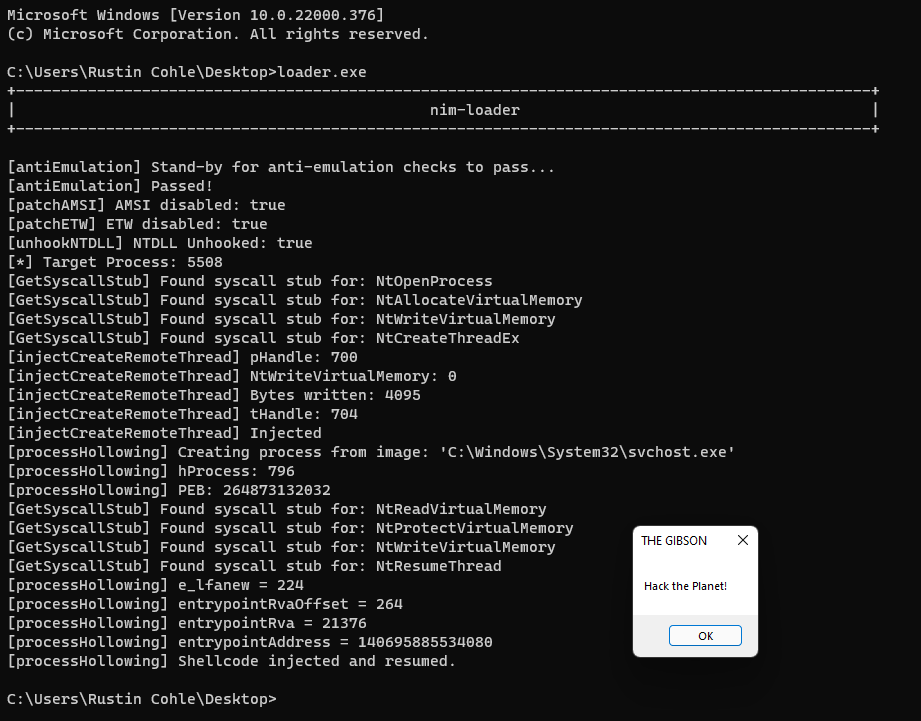 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
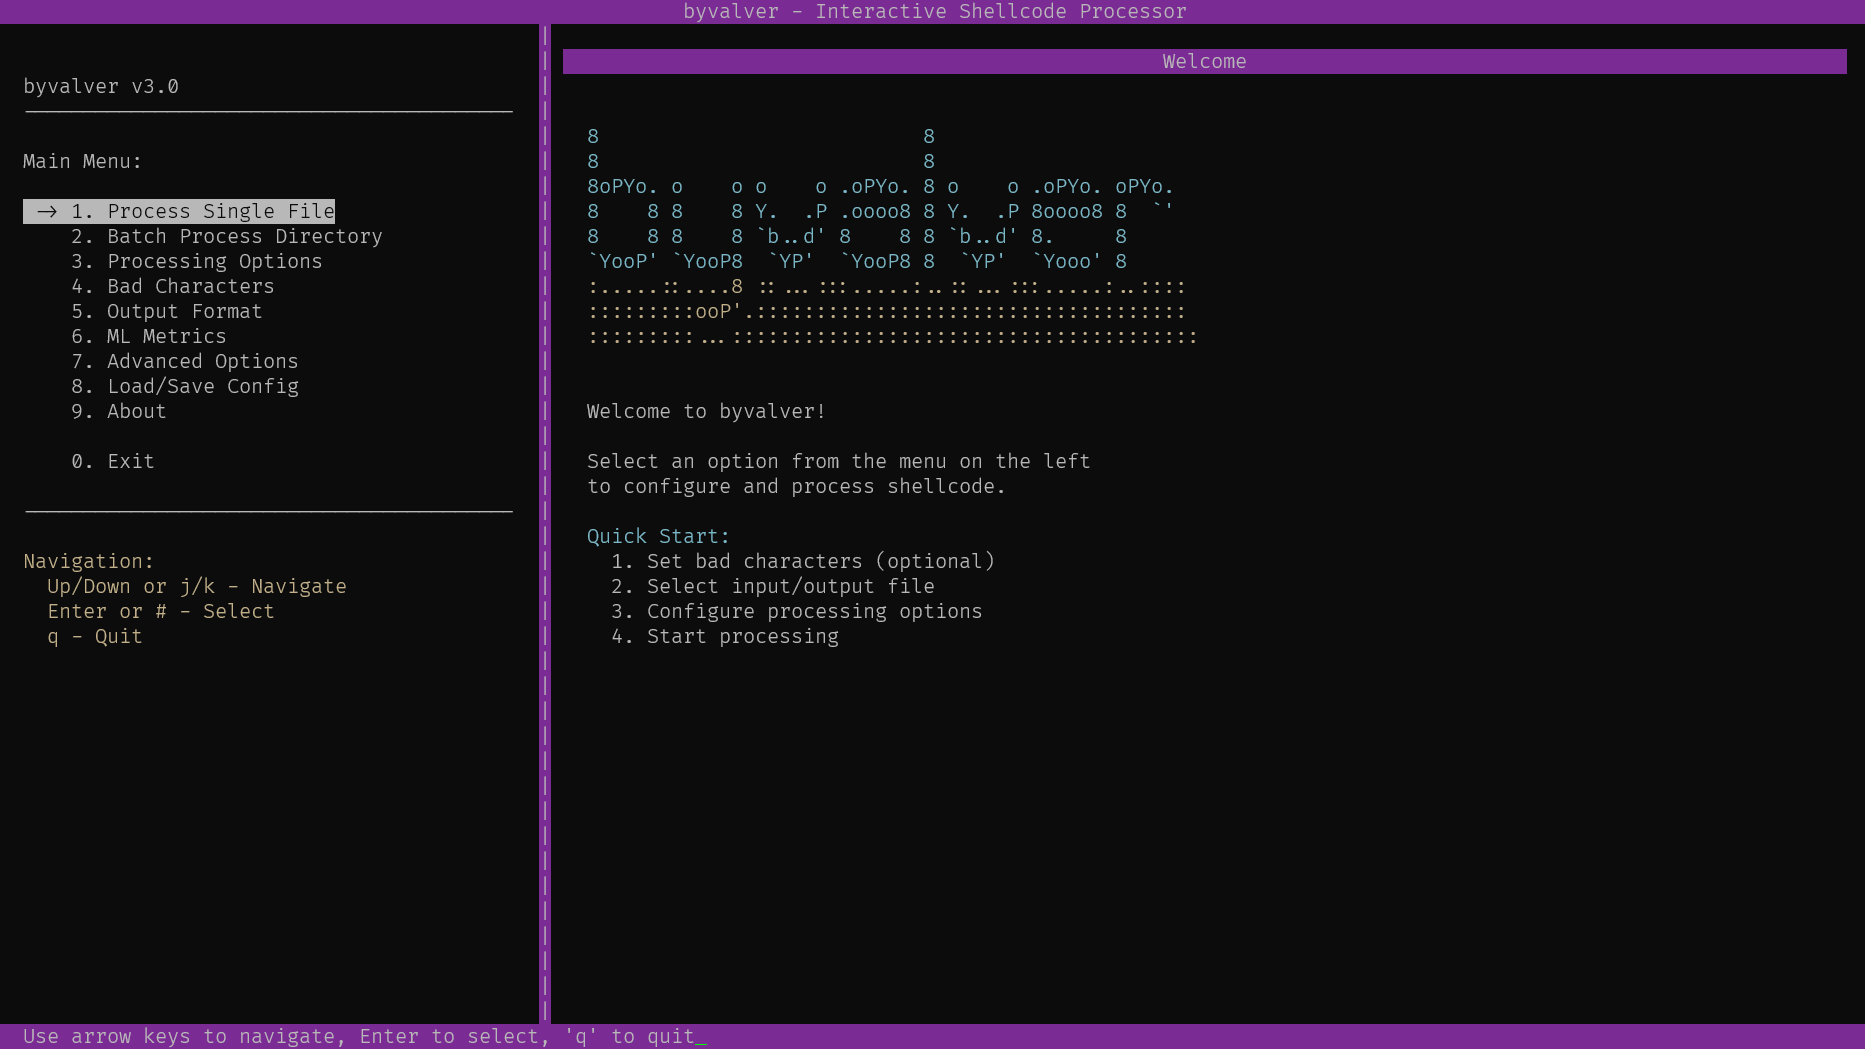 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
 hexastrike/cve-2008-4654
A fully functional exploit for a stack-based buffer overflow vulnerability in VideoLan’s VLC Media Player 0.9.4 when processing TiVo files.

 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.

 havocframework/havoc
The Havoc Framework
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…