
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
82 results
ShellcodeCompiler preview

ShellcodeCompiler

GitHubnytrorst/shellcodecompiler

Shellcode Compiler

binary-exploitationexploitationpayload-development+2
1.2k2 years ago
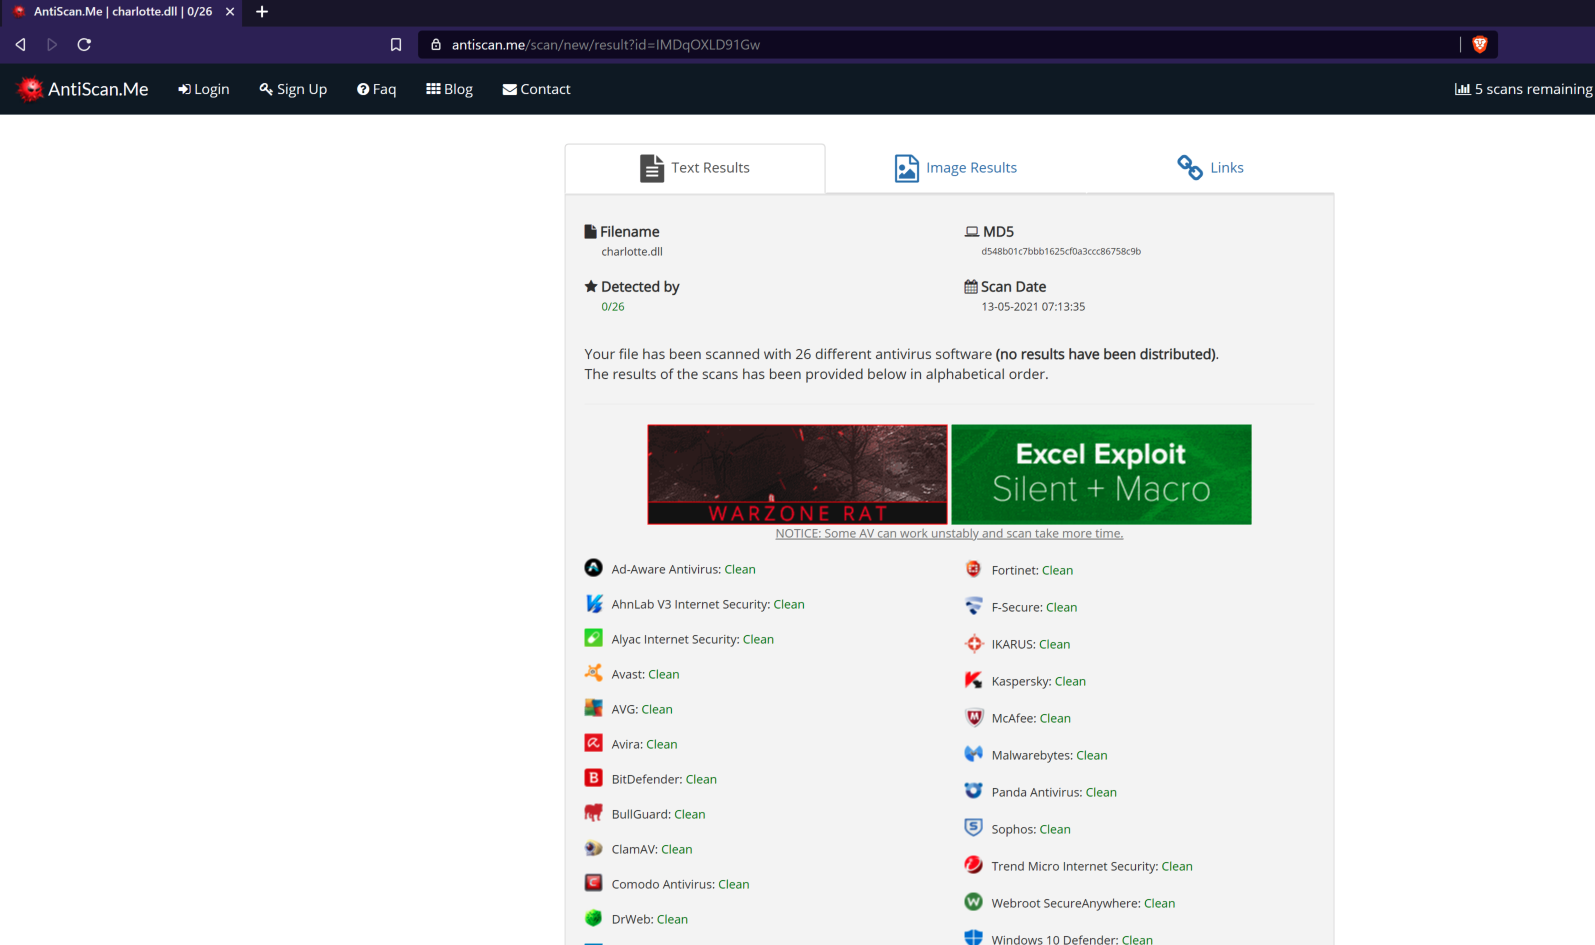
charlotte preview

charlotte

GitHub9emin1/charlotte

c++ fully undetected shellcode launcher ;)
anti-botexploitationids-ips-evasion+6
9745 years ago
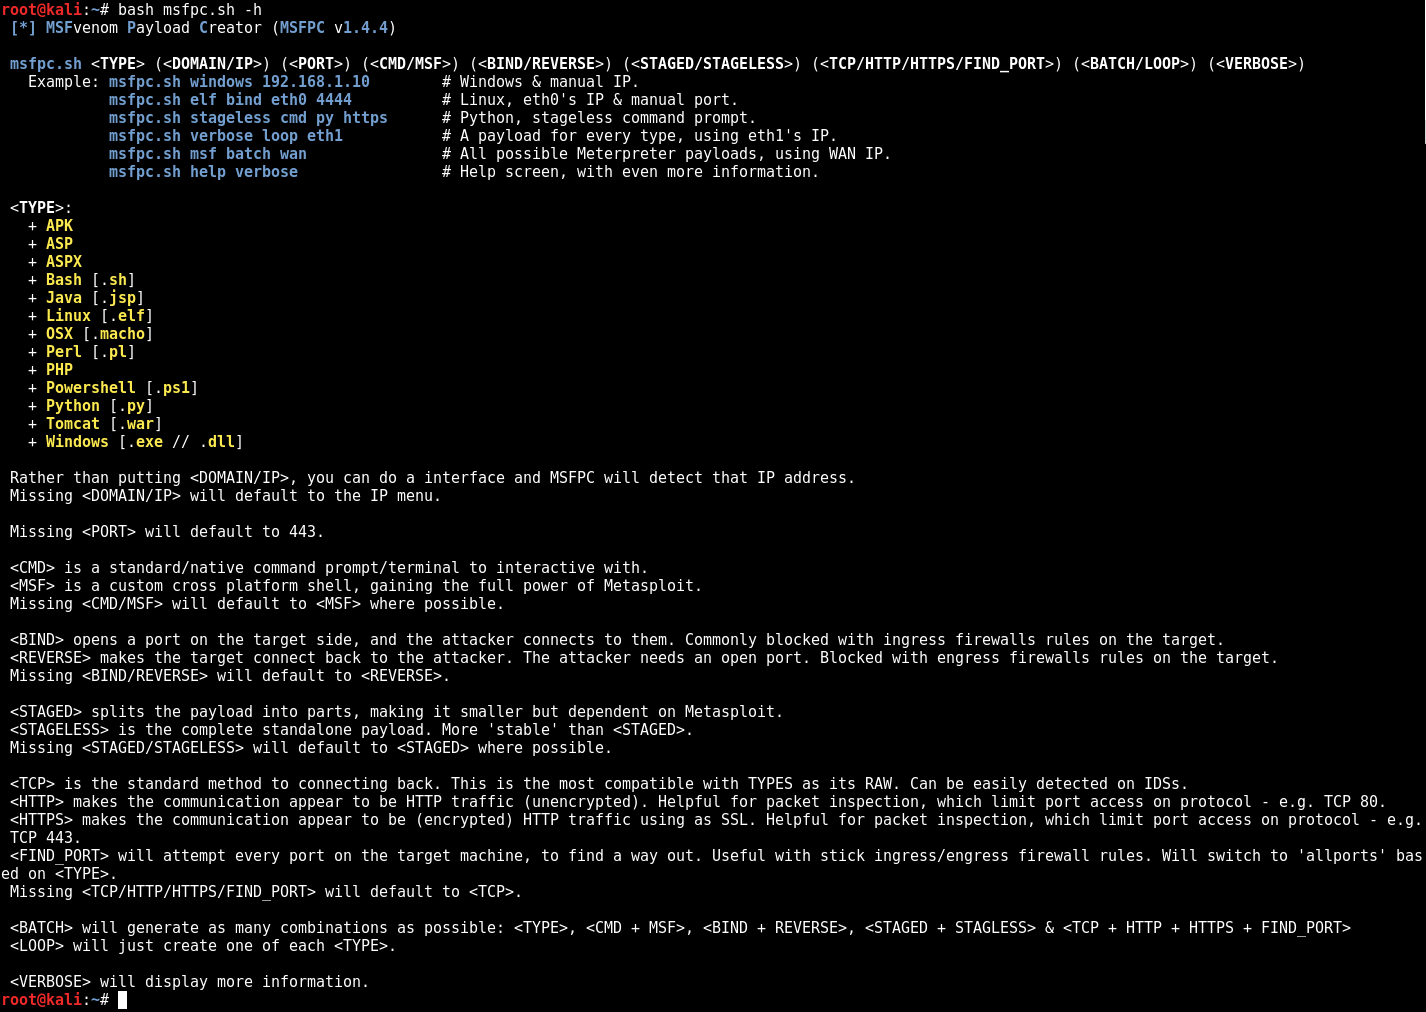
msfpc preview

msfpc

GitHubg0tmi1k/msfpc

MSFvenom Payload Creator (MSFPC)

command-and-controlexploit-frameworkspayload-development+5
1.3k5 years ago
EXOCET-AV-Evasion preview

EXOCET-AV-Evasion

GitHubtanc7/exocet-av-evasion

EXOCET - AV-evading, undetectable, payload delivery tool

command-and-controlcryptographyeducation+9
8414 years ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

command-and-controlexploit-frameworkslateral-movement+8
2122 months ago
hacking-team-windows-kernel-lpe preview

hacking-team-windows-kernel-lpe

GitHubvlad902/hacking-team-windows-kernel-lpe

Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
binary-exploitationexploitationpayload-generation+2
20311 years ago
ShellCodeEmulator preview

ShellCodeEmulator

GitHubohjeongwook/shellcodeemulator

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
1276 years ago
CrystalSliver preview

CrystalSliver

GitHublicitrasimone/crystalsliver

Crystal Palace Evasion kit for Sliver

command-and-controlexploit-frameworksids-ips-evasion+9
1183 months ago
payloadgenerator preview

payloadgenerator

GitHubrburrito/payloadgenerator

A wrapper for MSFvenom that allows for easy generation of payloads
exploit-frameworkspayload-developmentpayload-generation+2
64 years ago
CVE-2021-40444 preview

CVE-2021-40444

GitHubtiagob0b/cve-2021-40444

Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…

binary-exploitationexploitationpayload-generation+3
4 years ago
Kage preview
Archived

Kage

GitHubzerx0r/kage

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

command-and-controleducationexploit-frameworks+9
1.2k4 years ago
Phantom-Evasion preview
Archived

Phantom-Evasion

GitHuboddcod3/phantom-evasion

Python antivirus evasion tool
dynamic-analysis-sandboxingexploit-frameworkspayload-development+6
1.4k2 years ago
Veil preview
Archived

Veil

GitHubveil-framework/veil

Veil 3.1.X (Check version info in Veil at runtime)

command-and-controlexploit-frameworkspayload-generation+2
4.2k2 years ago
Freeze preview
Archived

Freeze

GitHuboptiv/freeze

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

exploit-frameworksids-ips-evasionpayload-development+8
1.5k3 years ago
Veil-Evasion preview
Archived

Veil-Evasion

GitHubveil-framework/veil-evasion

Veil Evasion is no longer supported, use Veil 3.0!
command-and-controlexploit-frameworkspayload-generation+2
1.8k5 years ago
MS17-010 preview

MS17-010

GitHubworawit/ms17-010

MS17-010

binary-exploitationexploitationpayload-development+4
2.3k3 years ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…

command-and-controlexploitationids-ips-evasion+8
5995 years ago
Zerodoor preview

Zerodoor

GitHubsouhardya/zerodoor

A script written lazily for generating cross-platform backdoors on the go :)

payload-developmentpayload-generationpenetration-testing+2
1877 years ago
Previous12345Next