staged-DLL-Injection-SMB-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).


Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.

Proof of concept python script for regreSSHion exploit.

Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…

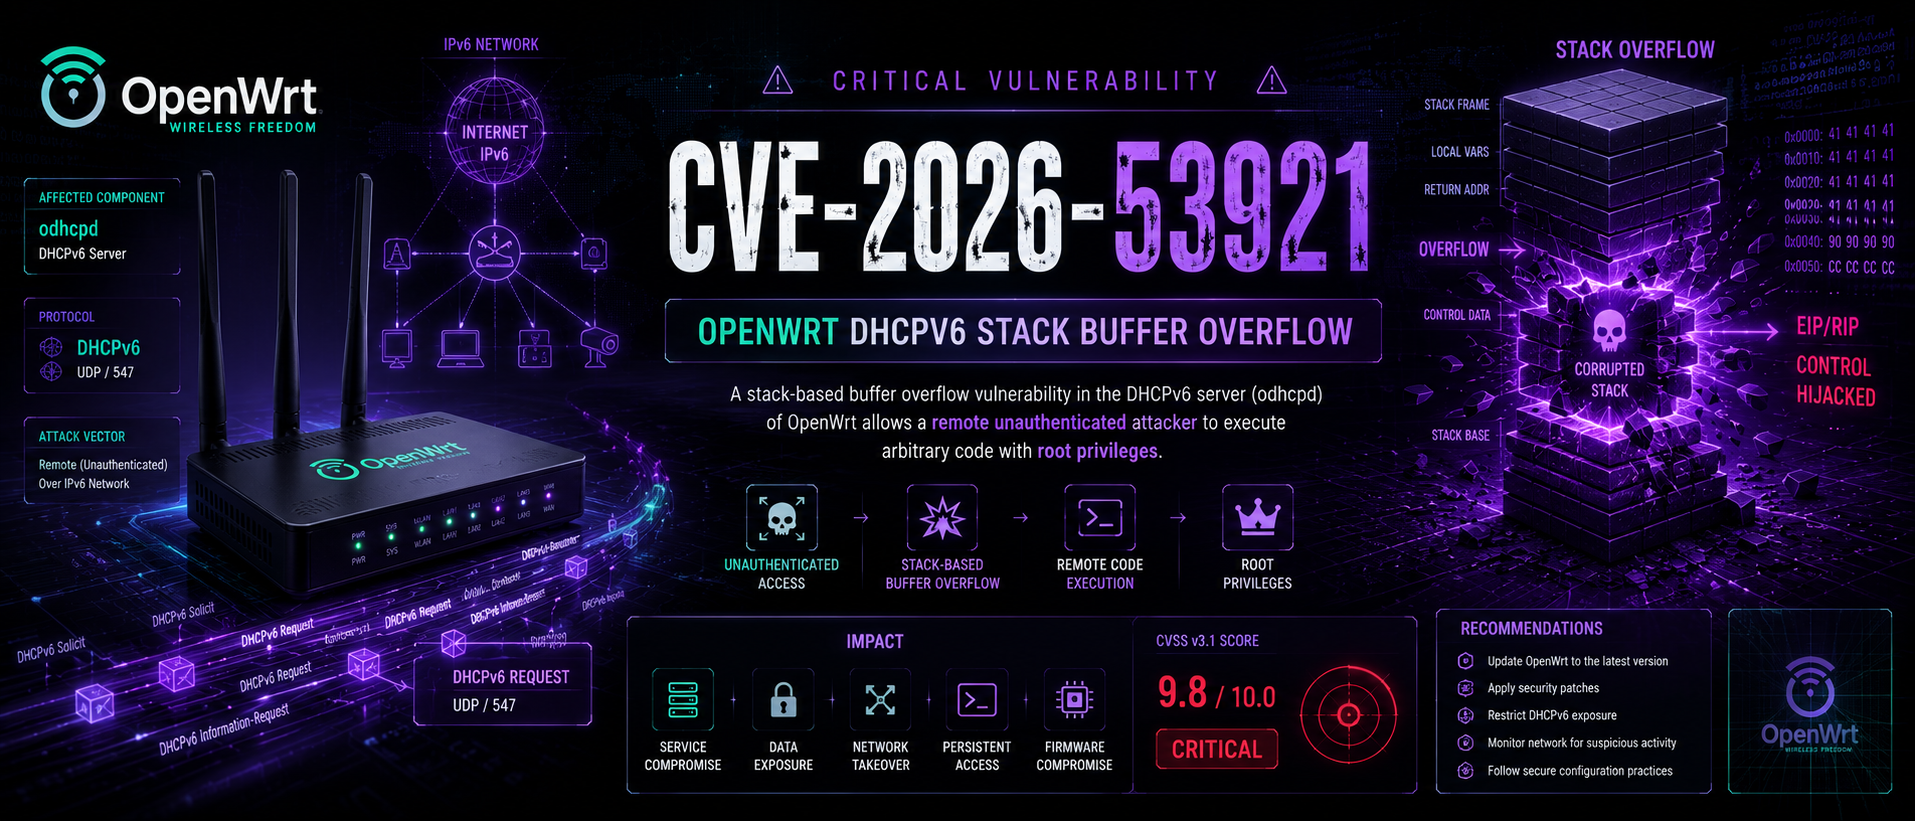
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…

Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.

Palo Alto - CVE-2026-0300 exploit

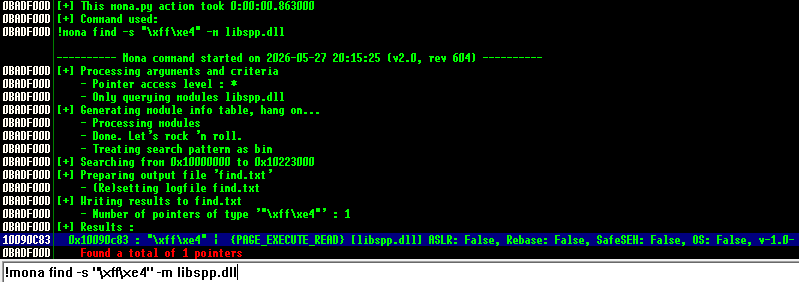
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

OpenSTAManager RCE Exploit (CVE-2026-38751)

C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…

Suite for reverse shell handling geared toward working within the native shell

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

EGESPLOIT is a golang library for malware development

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

Automated Tool That Generates The Perfect Meterpreter Powershell Payload