
fudshell
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
payload-generationshellcode-generation
machine1337/fudshellAn efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
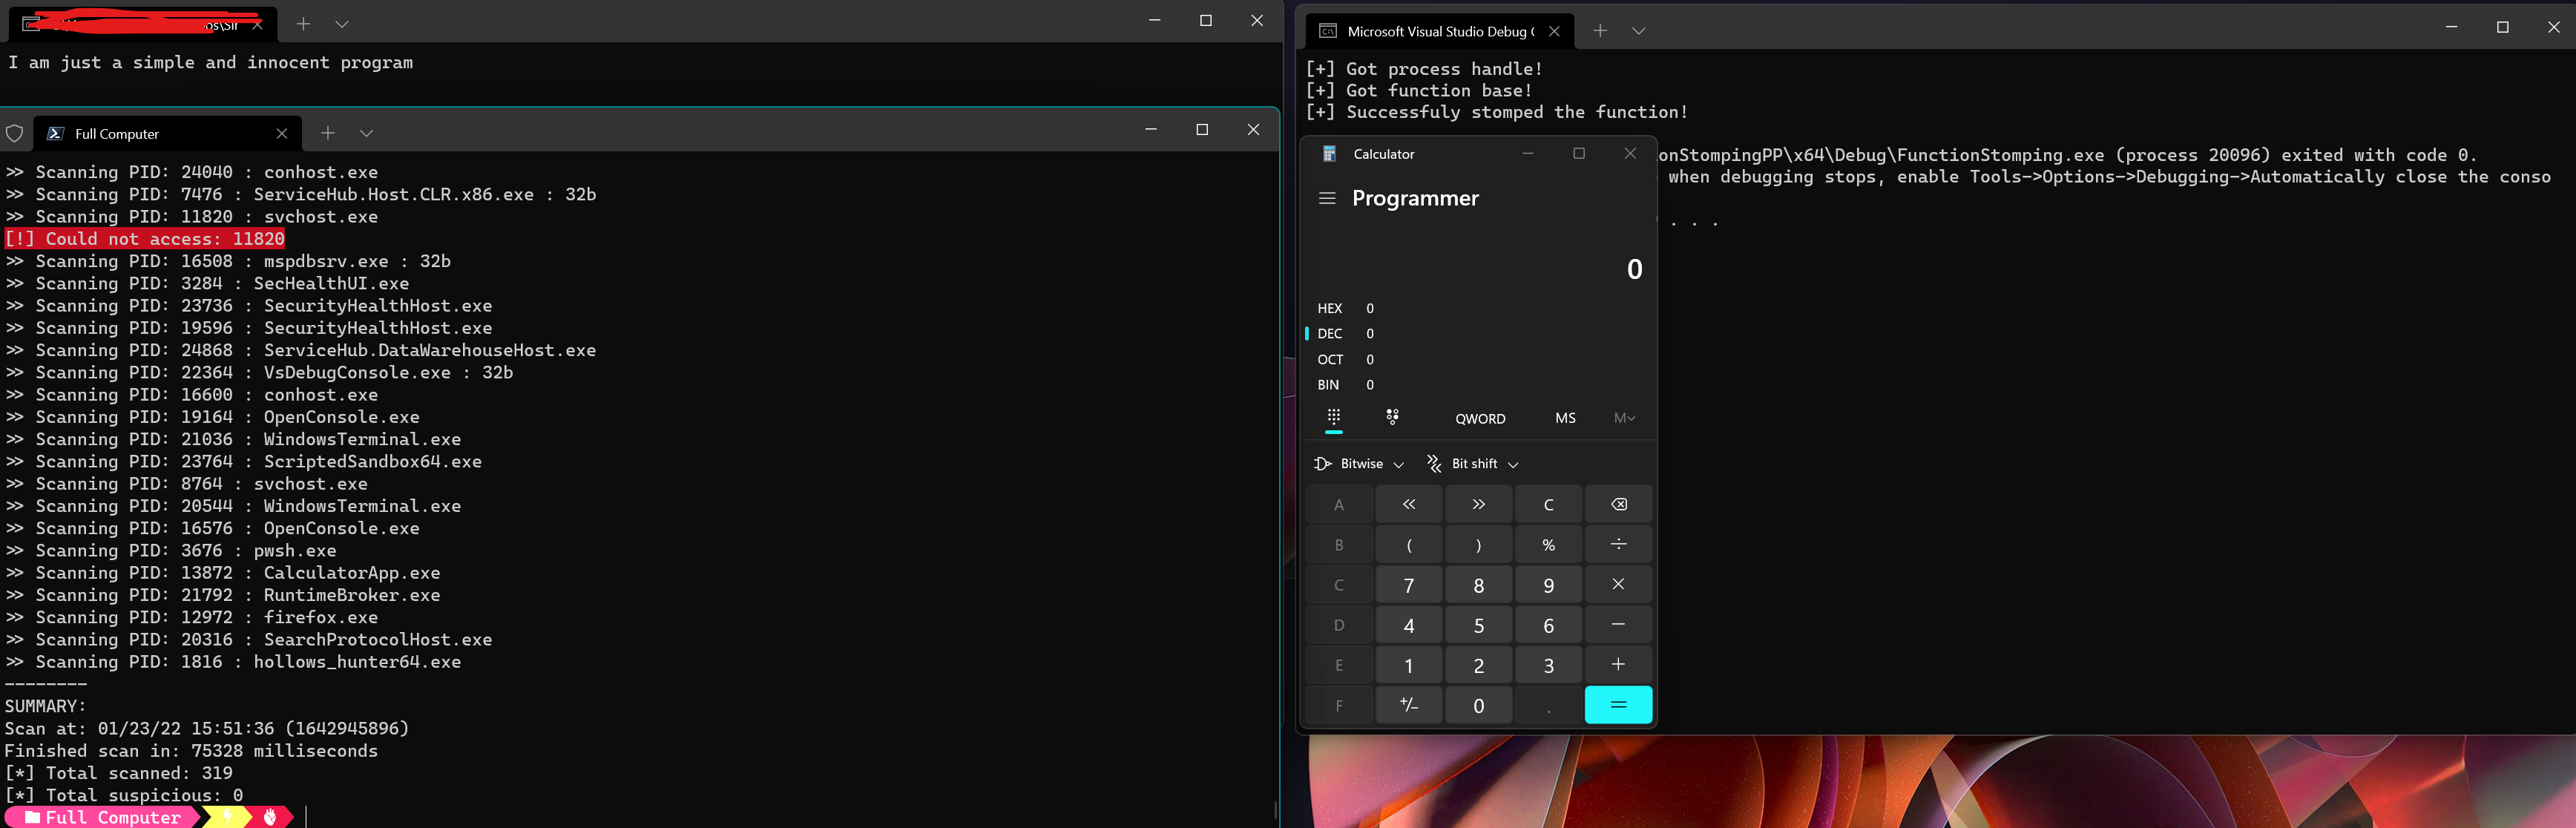 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
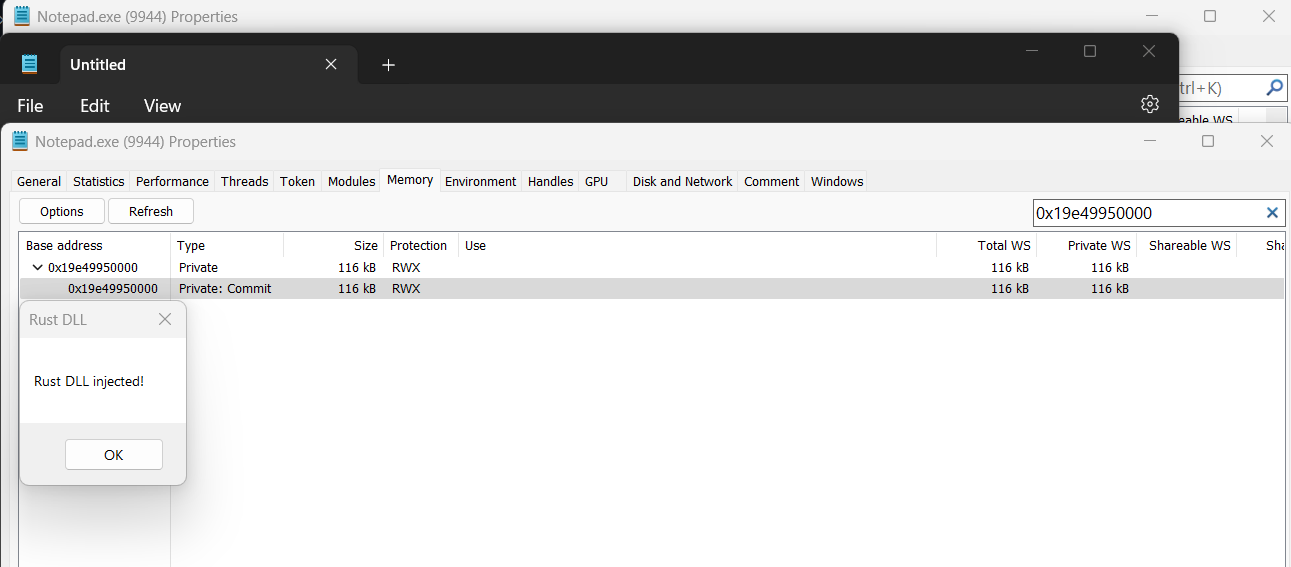 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
 bishopfox/sliver
Adversary Emulation Framework
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.