
BrokenFlow
 enkomio/brokenflow
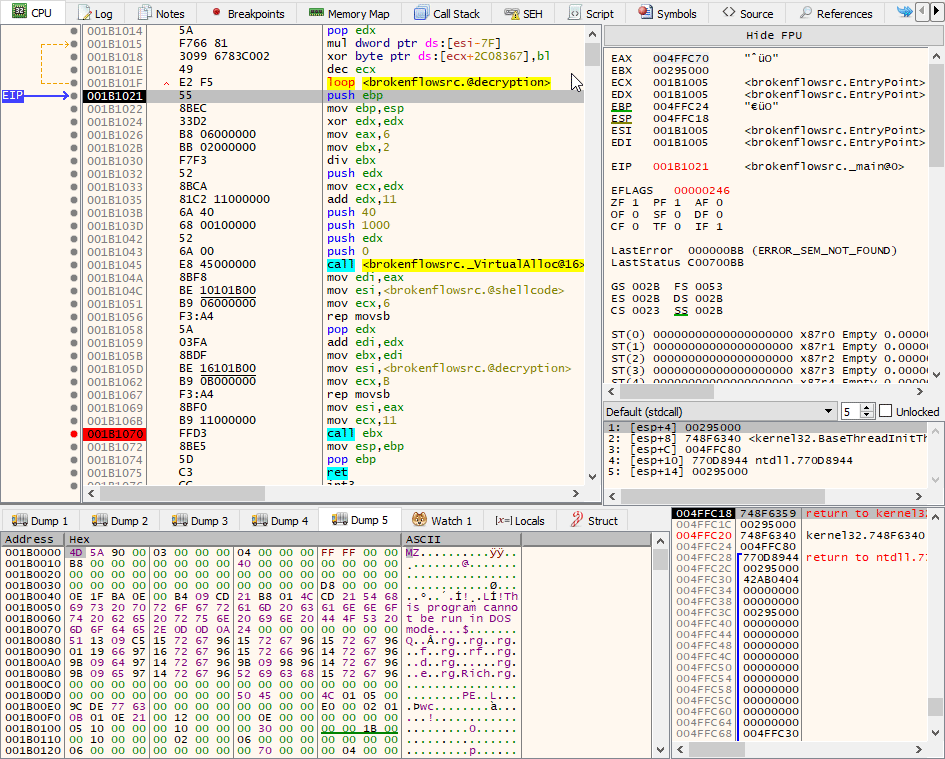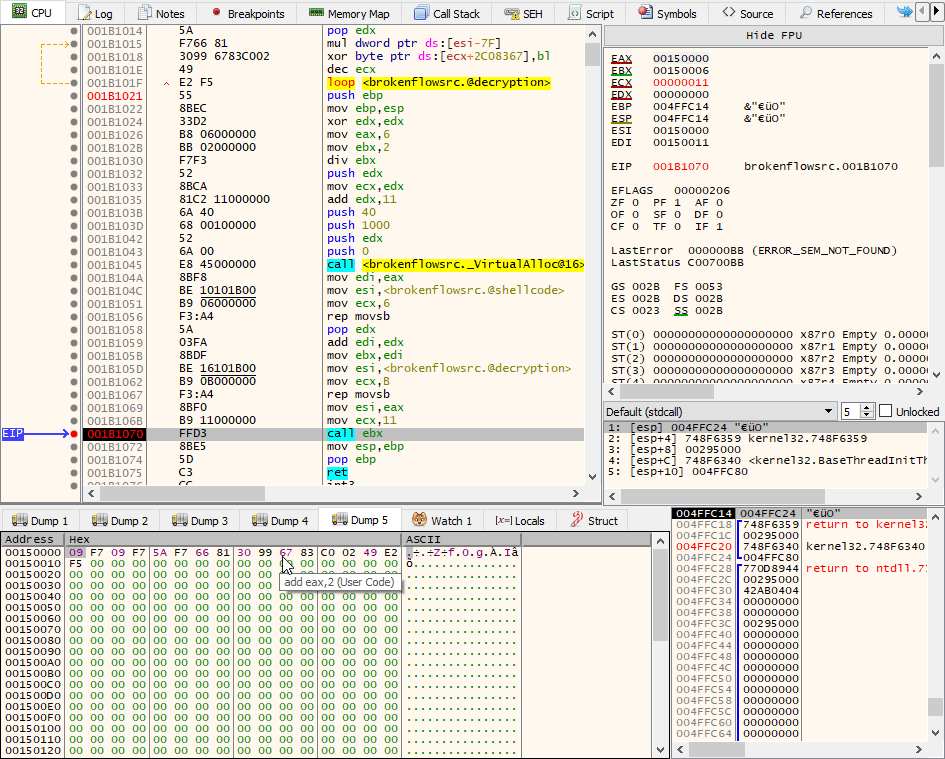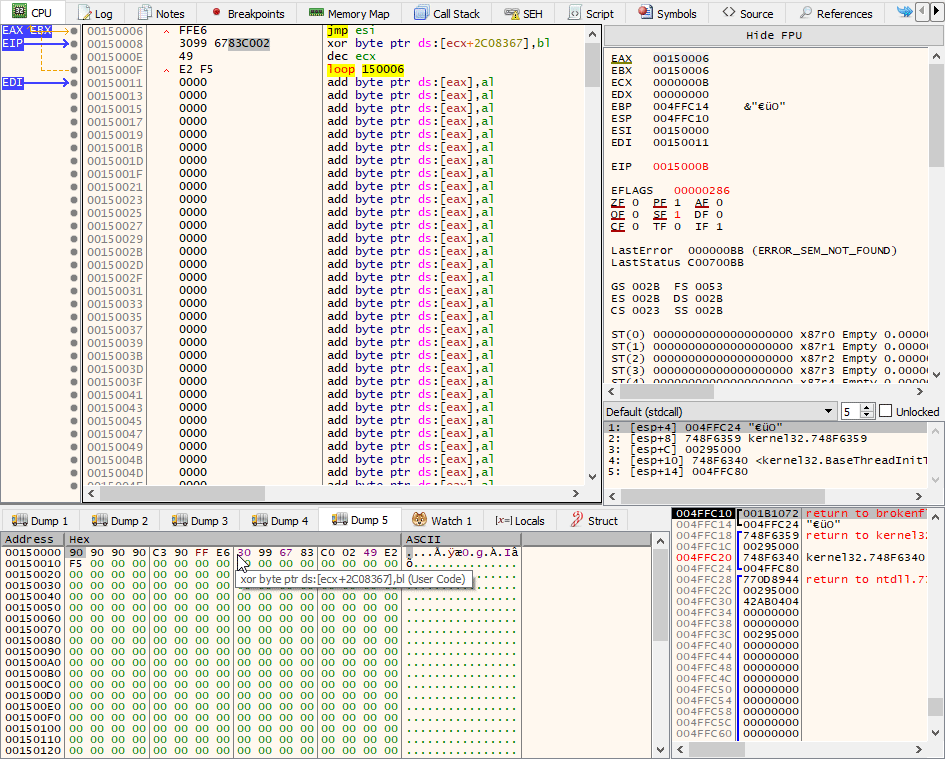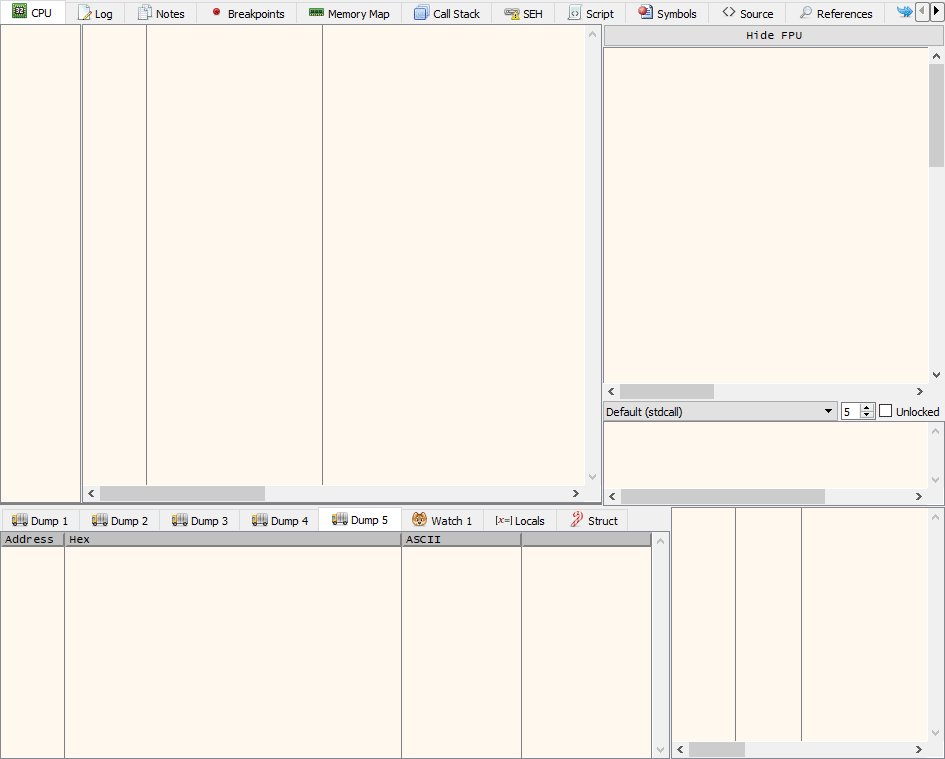
A simple PoC to invoke an encrypted shellcode by using an hidden call
binary-exploitationencryption-decryption-toolsexploitation+4
enkomio/brokenflowA simple PoC to invoke an encrypted shellcode by using an hidden call
 bishopfox/joro
A collaborative web exploitation framework.
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
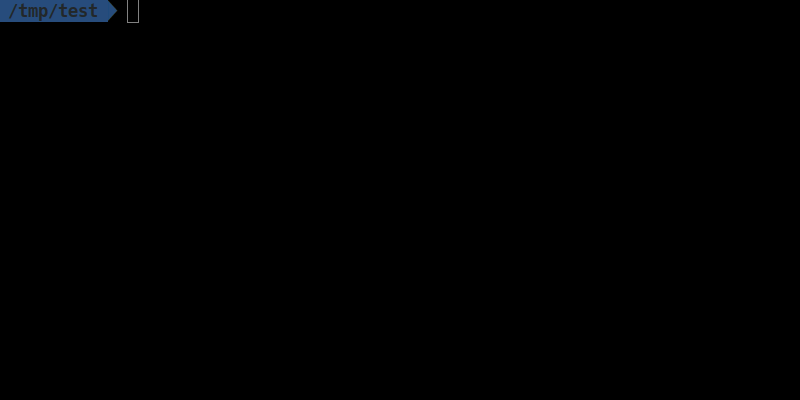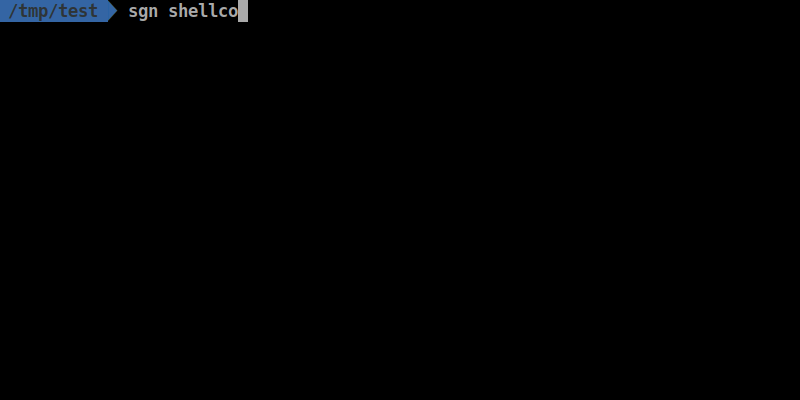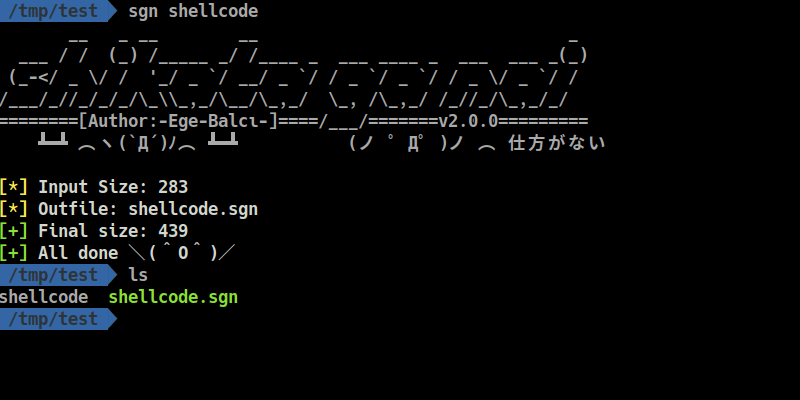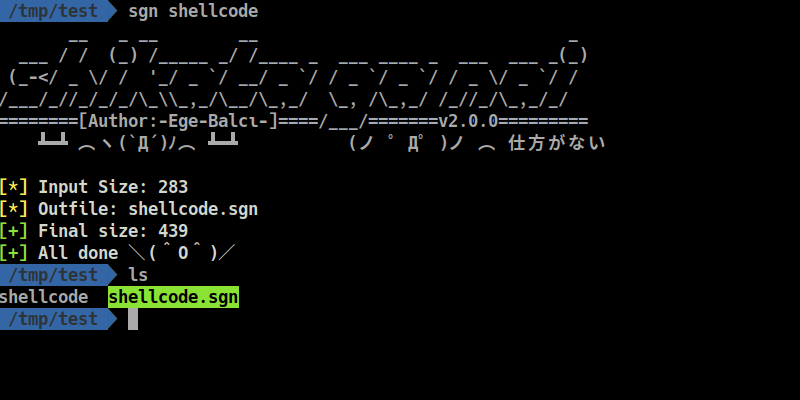 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver