metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

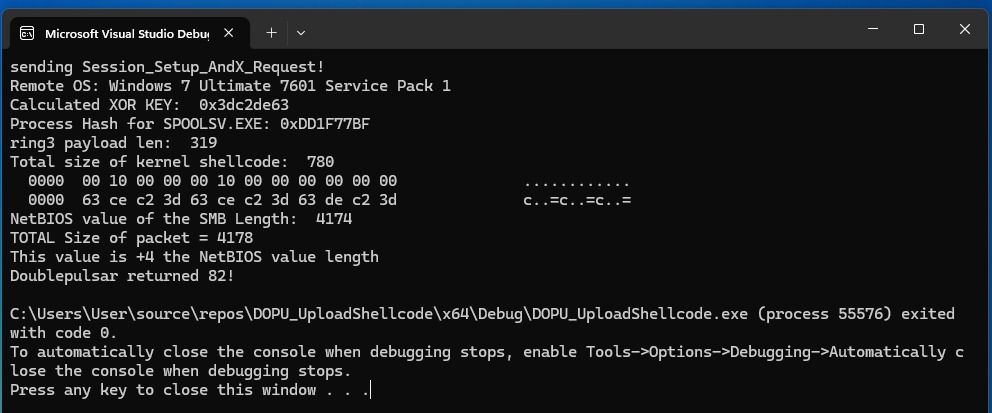
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

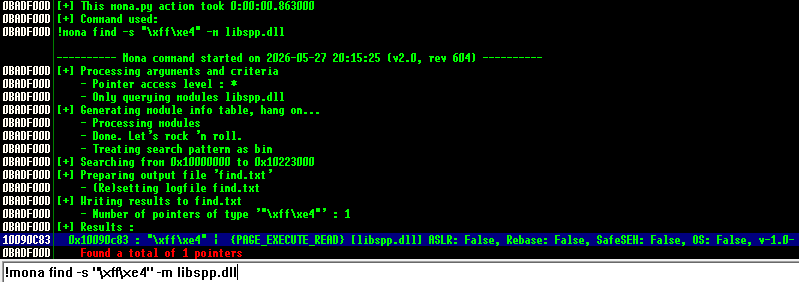
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

Palo Alto - CVE-2026-0300 exploit

OpenSTAManager RCE Exploit (CVE-2026-38751)

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

A fully functional exploit for a stack-based buffer overflow vulnerability in VideoLan’s VLC Media Player 0.9.4 when processing TiVo files.

Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.

Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…

Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit

Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…