metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…

Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…

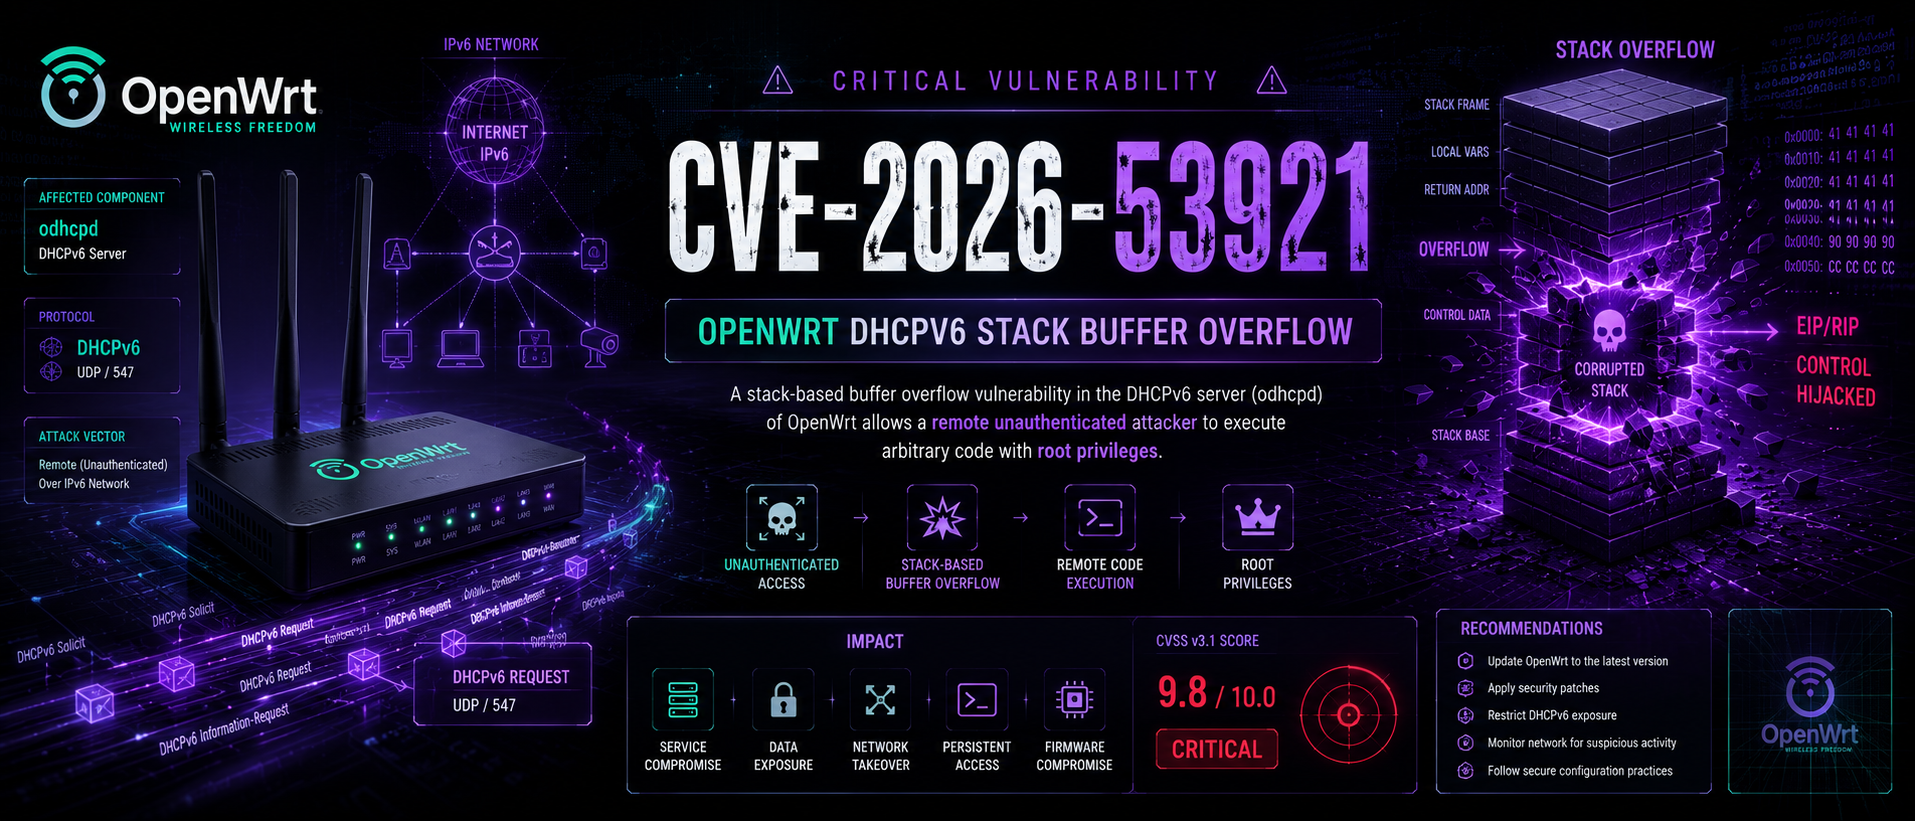
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…

Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

UNIX-like reverse engineering framework and command-line toolset.

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)