

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
54 results
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
3011 days ago
voidsec-proxy preview

voidsec-proxy

GitHubvoidsecsoftwares/voidsec-proxy

Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
data-exfiltrationdigital-forensicsdns-subdomain-enumeration+8
41 month ago
CVE-2017-14980 preview

CVE-2017-14980

GitHubgodoy-sec/cve-2017-14980

Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

binary-exploitationdebuggerseducation+5
12 months ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
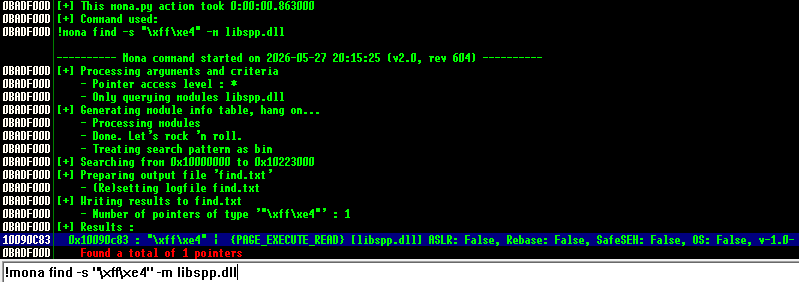
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9578 months ago
POC-CVE-2026-0300-exploit preview

POC-CVE-2026-0300-exploit

GitHubsam00/poc-cve-2026-0300-exploit

Palo Alto - CVE-2026-0300 exploit
binary-exploitationexploitationnetwork-security+6
2 months ago
LibTP_Gadget preview

LibTP_Gadget

GitHubsaerxcit/libtp_gadget

Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.

adversarial-attackids-ips-evasionpayload-development+3
2311 months ago
metasploitavevasion preview

metasploitavevasion

GitHubnccgroup/metasploitavevasion

Metasploit AV Evasion Tool
command-and-controlexploitationids-ips-evasion+4
25610 years ago
Bypass-PayloadRestrictions.dll-wdeg-rop-mitigation- preview

Bypass-PayloadRestrictions.dll-wdeg-rop-mitigation-

GitHubspiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-

C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
binary-exploitationexploitationids-ips-evasion+3
12 years ago
CVE-2026-53921-PoC-Exploit preview

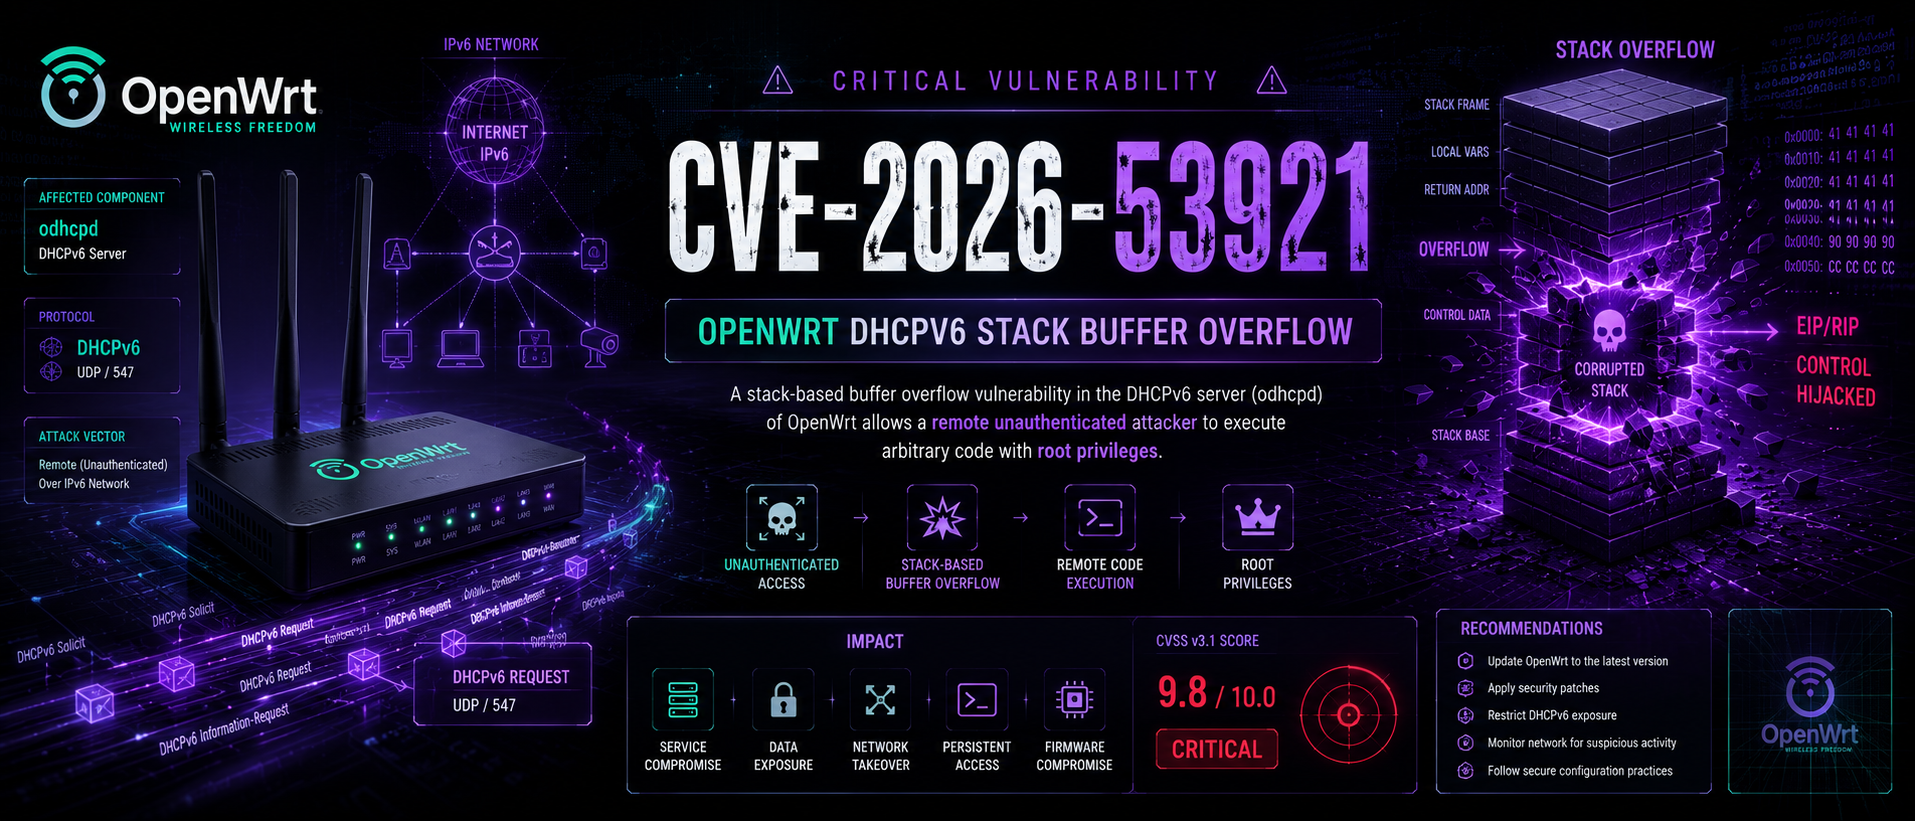
CVE-2026-53921-PoC-Exploit

GitHubtc4dy/cve-2026-53921-poc-exploit

CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…


binary-exploitationembedded-systems-securityexploitation+8
62 days ago
ZeroRAT preview

ZeroRAT

GitHub5alt/zerorat

ZeroRAT是一款windows上的一句话远控

command-and-controldata-exfiltrationexploitation+9
6410 years ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

command-and-controlexploit-frameworkslateral-movement+8
2122 months ago
Harmonic preview

Harmonic

GitLabrunik/harmonic

Suite for reverse shell handling geared toward working within the native shell

command-and-controlinformation-gatheringpayload-development+7
8 years ago
JYso preview

JYso

GitHubqi4l/jyso

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
command-and-controlctfexploit-frameworks+5
1.8k3 months ago
staged-DLL-Injection-SMB- preview

staged-DLL-Injection-SMB-

GitHubkasturixbm5/staged-dll-injection-smb-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

educationexploitationlabs-practice+5
424 months ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

binary-analysiscommand-and-controlexploit-frameworks+9
1333 months ago
CrystalSliver preview

CrystalSliver

GitHublicitrasimone/crystalsliver

Crystal Palace Evasion kit for Sliver
command-and-controlexploit-frameworksids-ips-evasion+9
1184 months ago
CVE-2024-6387 preview

CVE-2024-6387

GitHubl-urk/cve-2024-6387

Proof of concept python script for regreSSHion exploit.

binary-exploitationexploitationnetwork-security+6
121 year ago
Previous123Next