

rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
rizinorg/rizinUNIX-like reverse engineering framework and command-line toolset.
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 that-guy-steve/cve-2022-28368-handler
This repository contains a python script that will handle the majority of the dompdf cached font exploit (CVE-2022-28368), all you need to do is…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
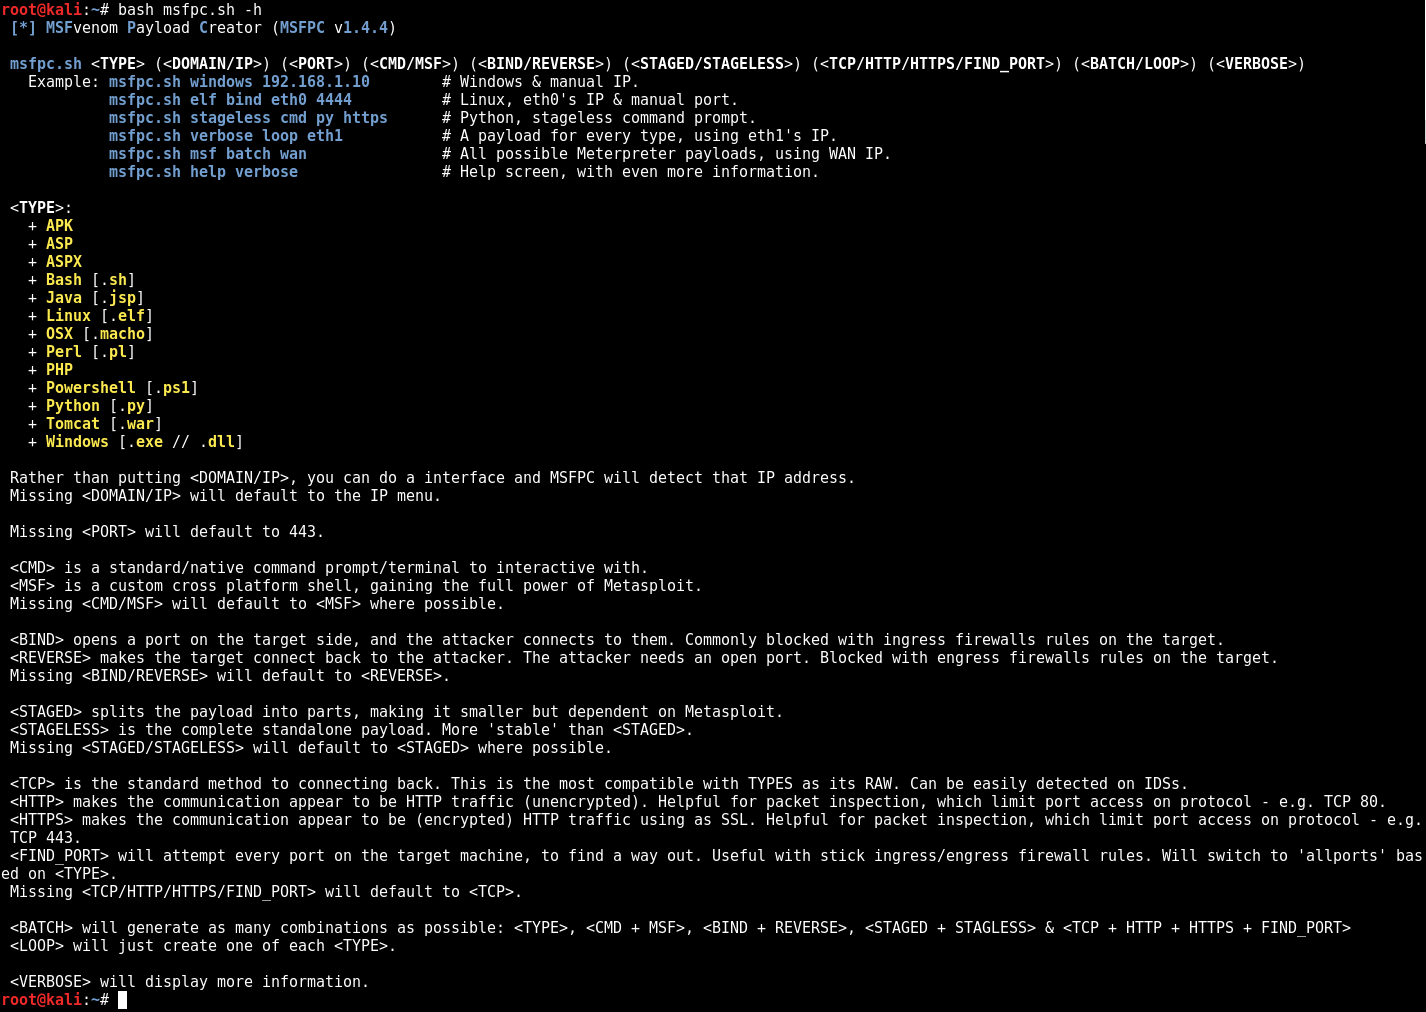 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)