

reverse-shell-generator
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
ctfexploitationpayload-development+6
4.1k
0dayctf/reverse-shell-generatorHosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 zznop/sploit
Go package that aids in binary analysis and exploitation
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
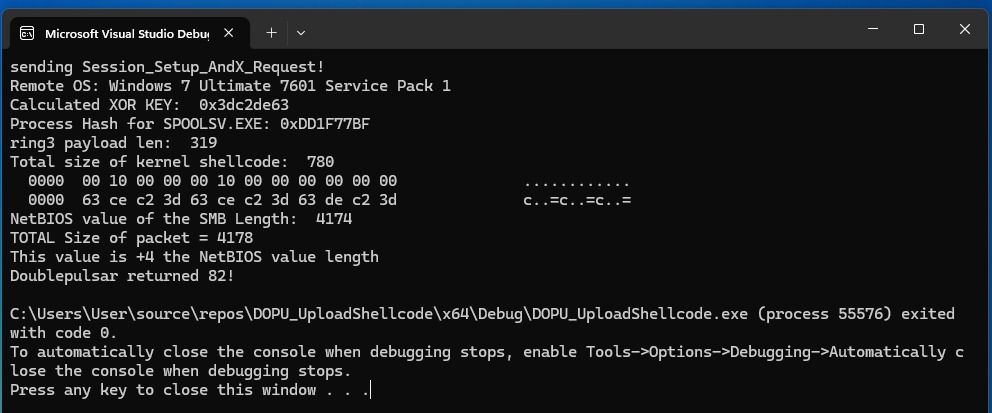 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
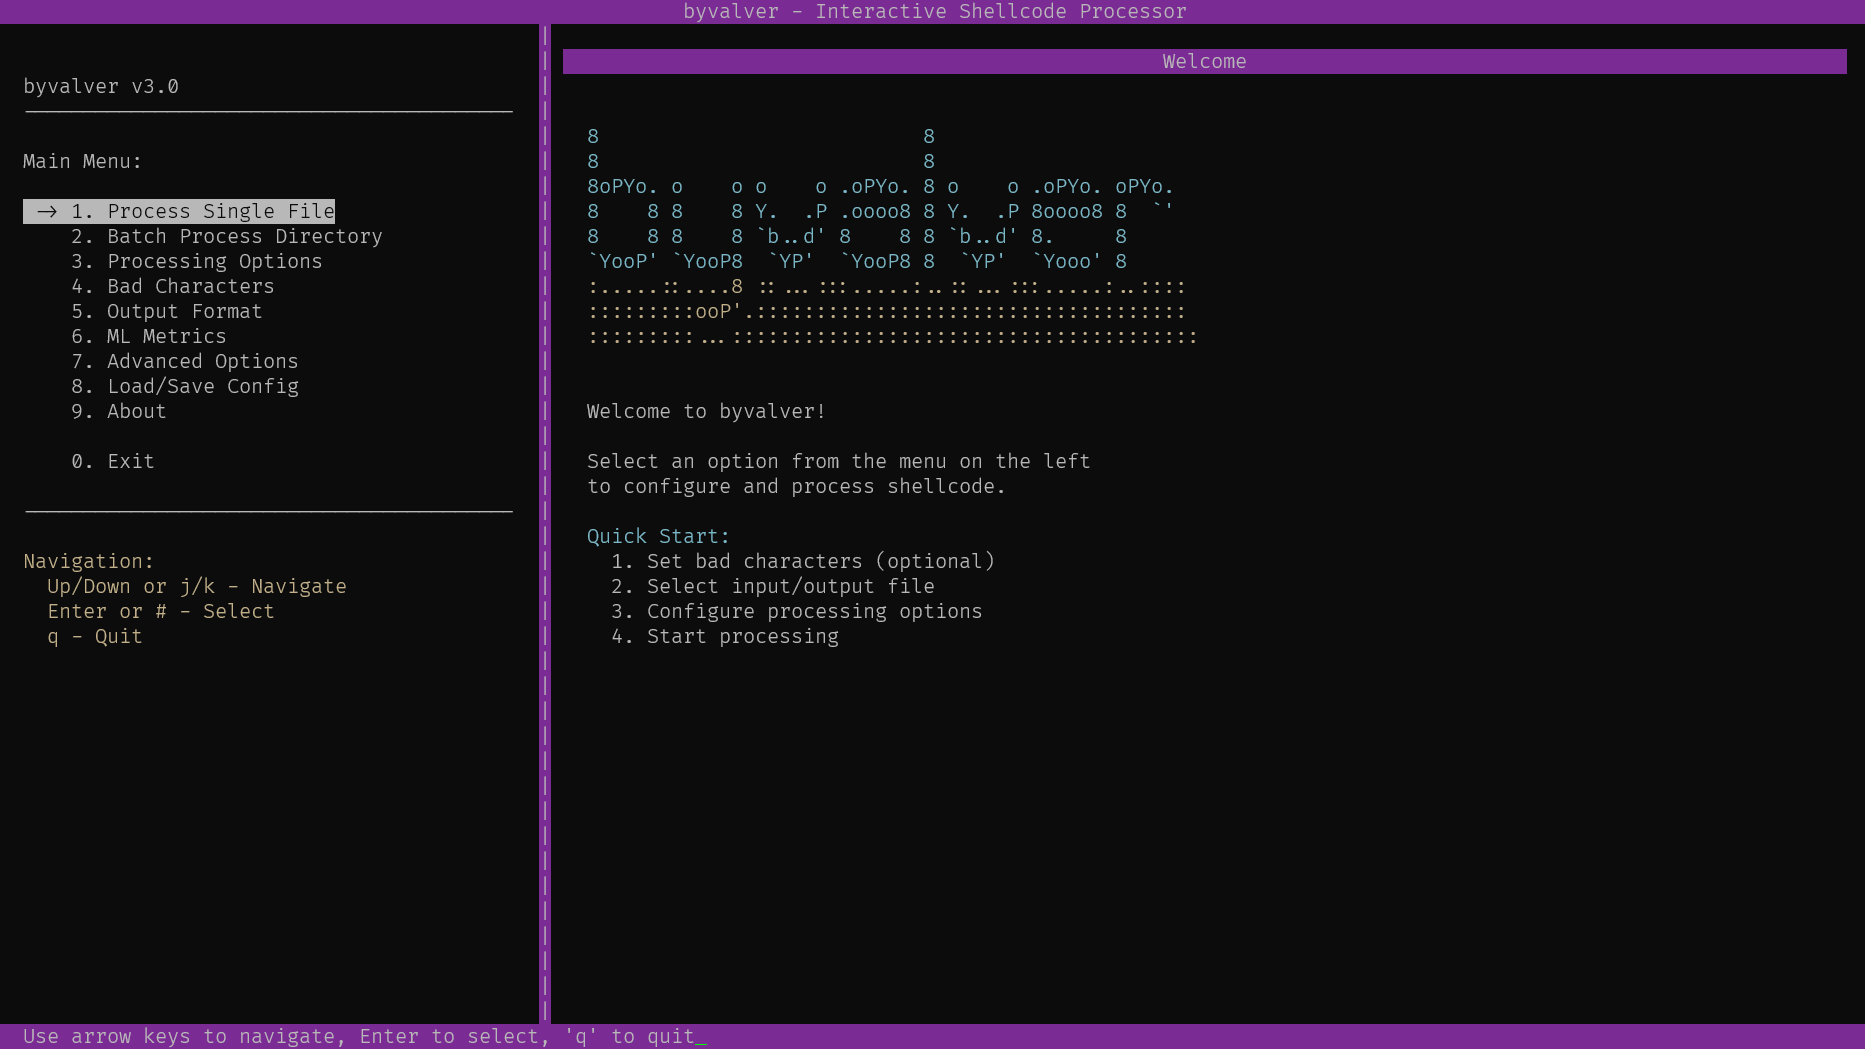 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 havocframework/havoc
The Havoc Framework
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.