staged-DLL-Injection-SMB-

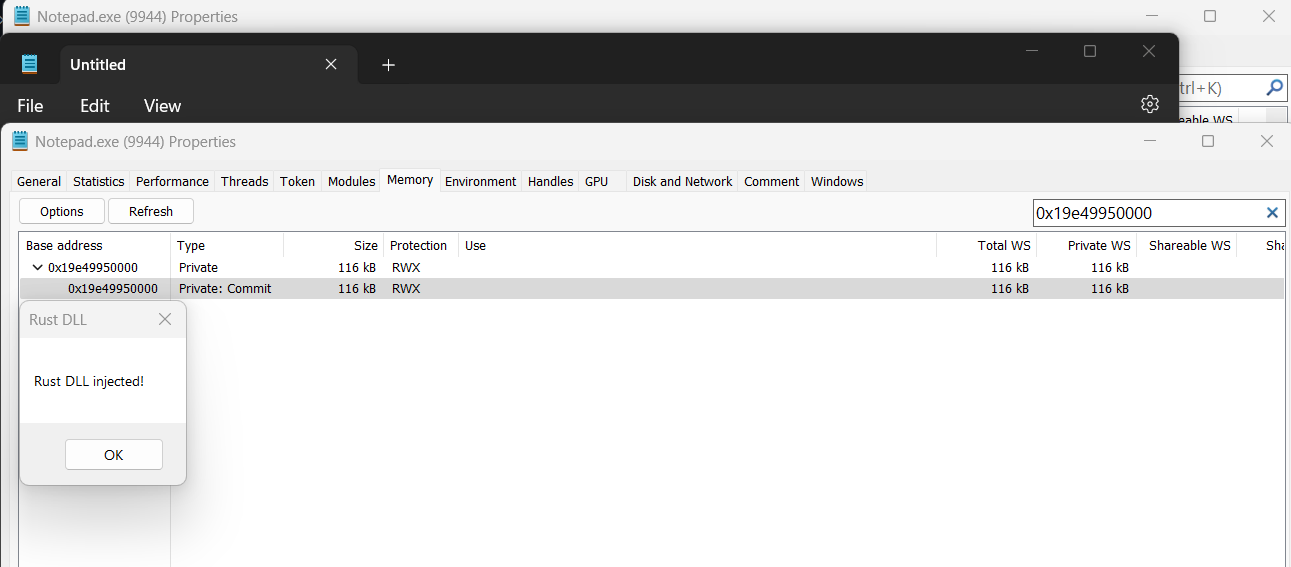
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Shellcode injection using the Windows Debugging API

Shellcode Encrypter & Decrypter via XOR Cipher

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Threadless Process Injection using remote function hooking.

Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

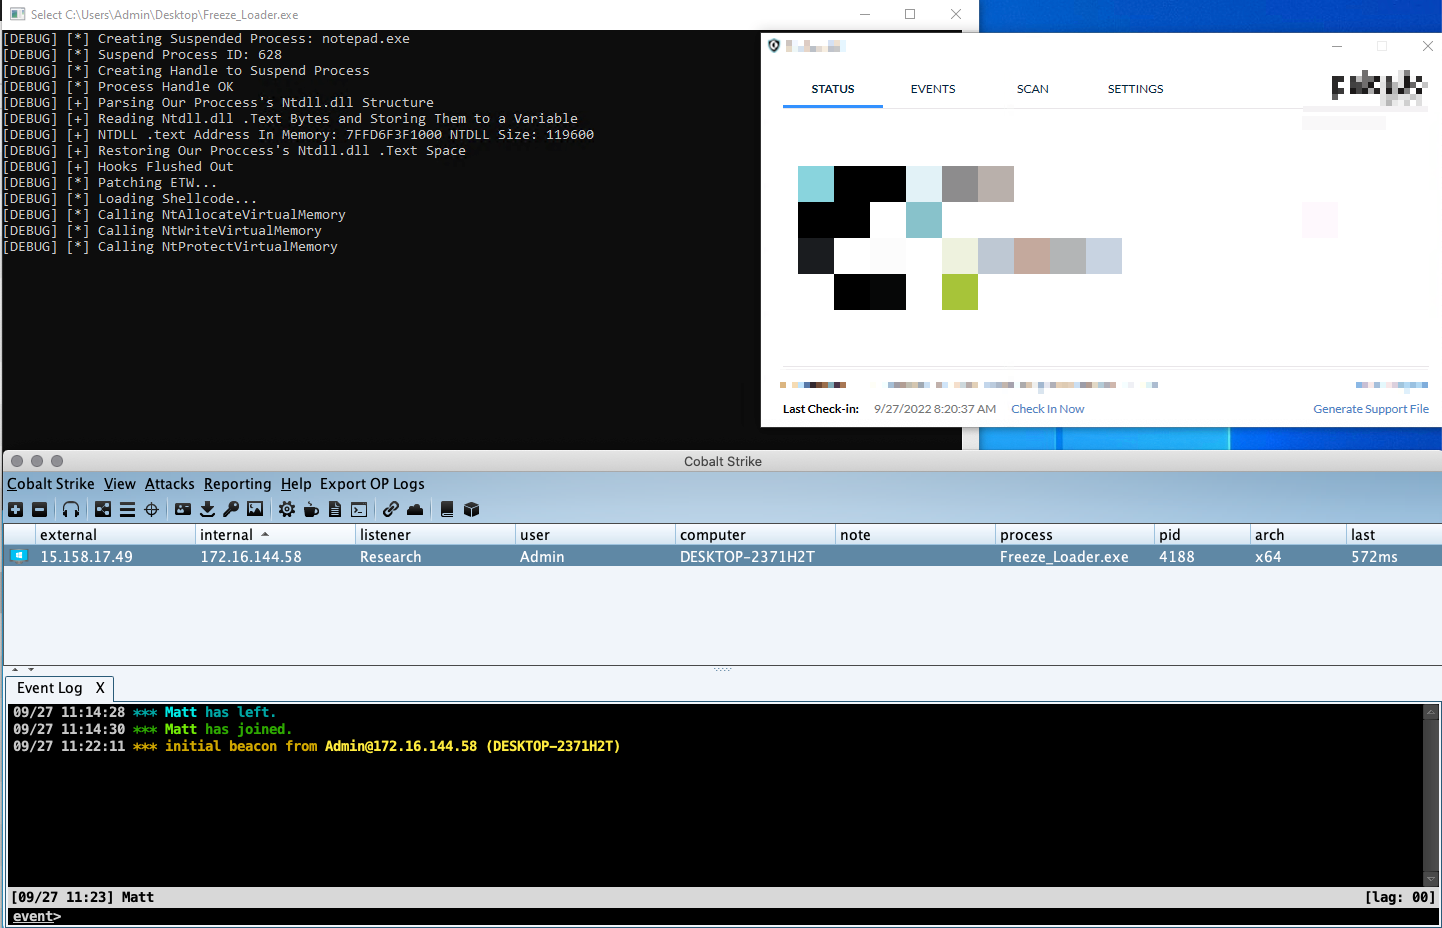
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

Windows User-Mode Shellcode Development Framework (WUMSDF)

Python based tool for generating Shellcode from PIC C

The Python Password-Protected Obfuscator

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

A simple PoC to invoke an encrypted shellcode by using an hidden call