

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.2k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 zznop/sploit
Go package that aids in binary analysis and exploitation
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
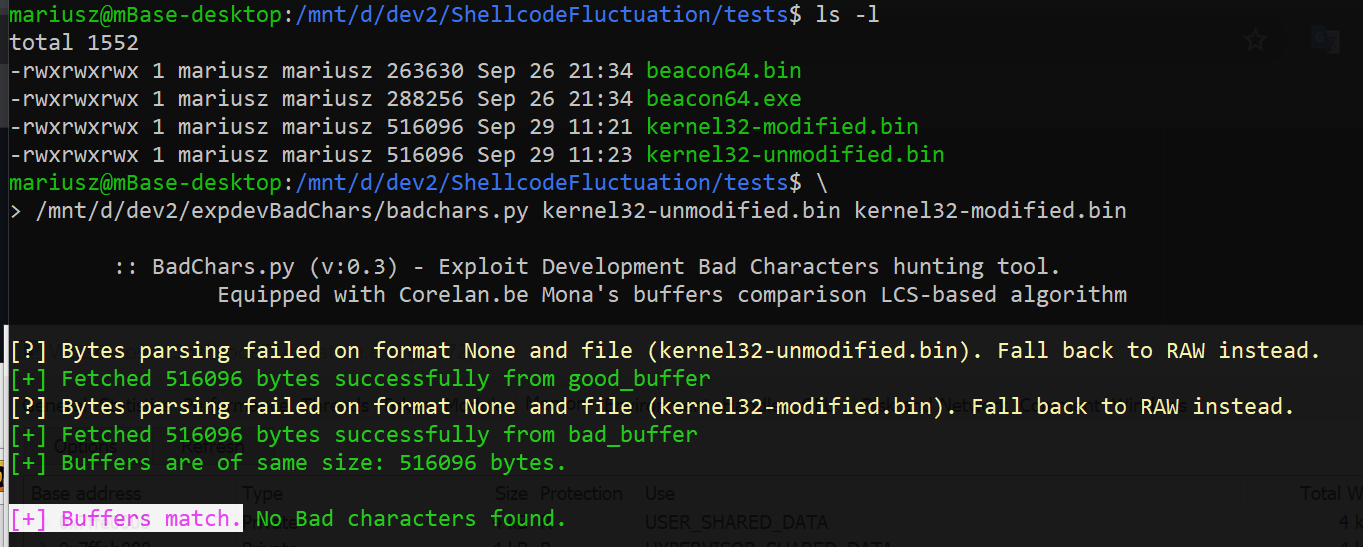 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
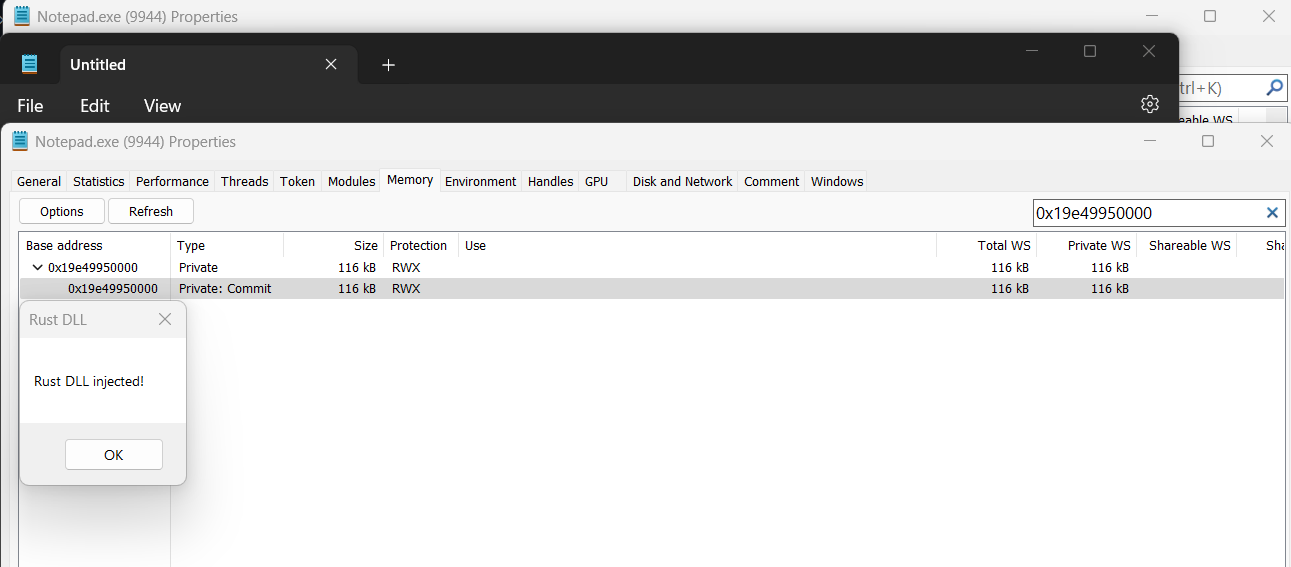 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
 veil-framework/veil-evasion
Veil Evasion is no longer supported, use Veil 3.0!
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 nytrorst/shellcodecompiler
Shellcode Compiler
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload