

Blackbone
 darthton/blackbone
Windows memory hacking library
binary-analysisdebuggersdynamic-analysis-sandboxing+9
darthton/blackboneWindows memory hacking library

 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
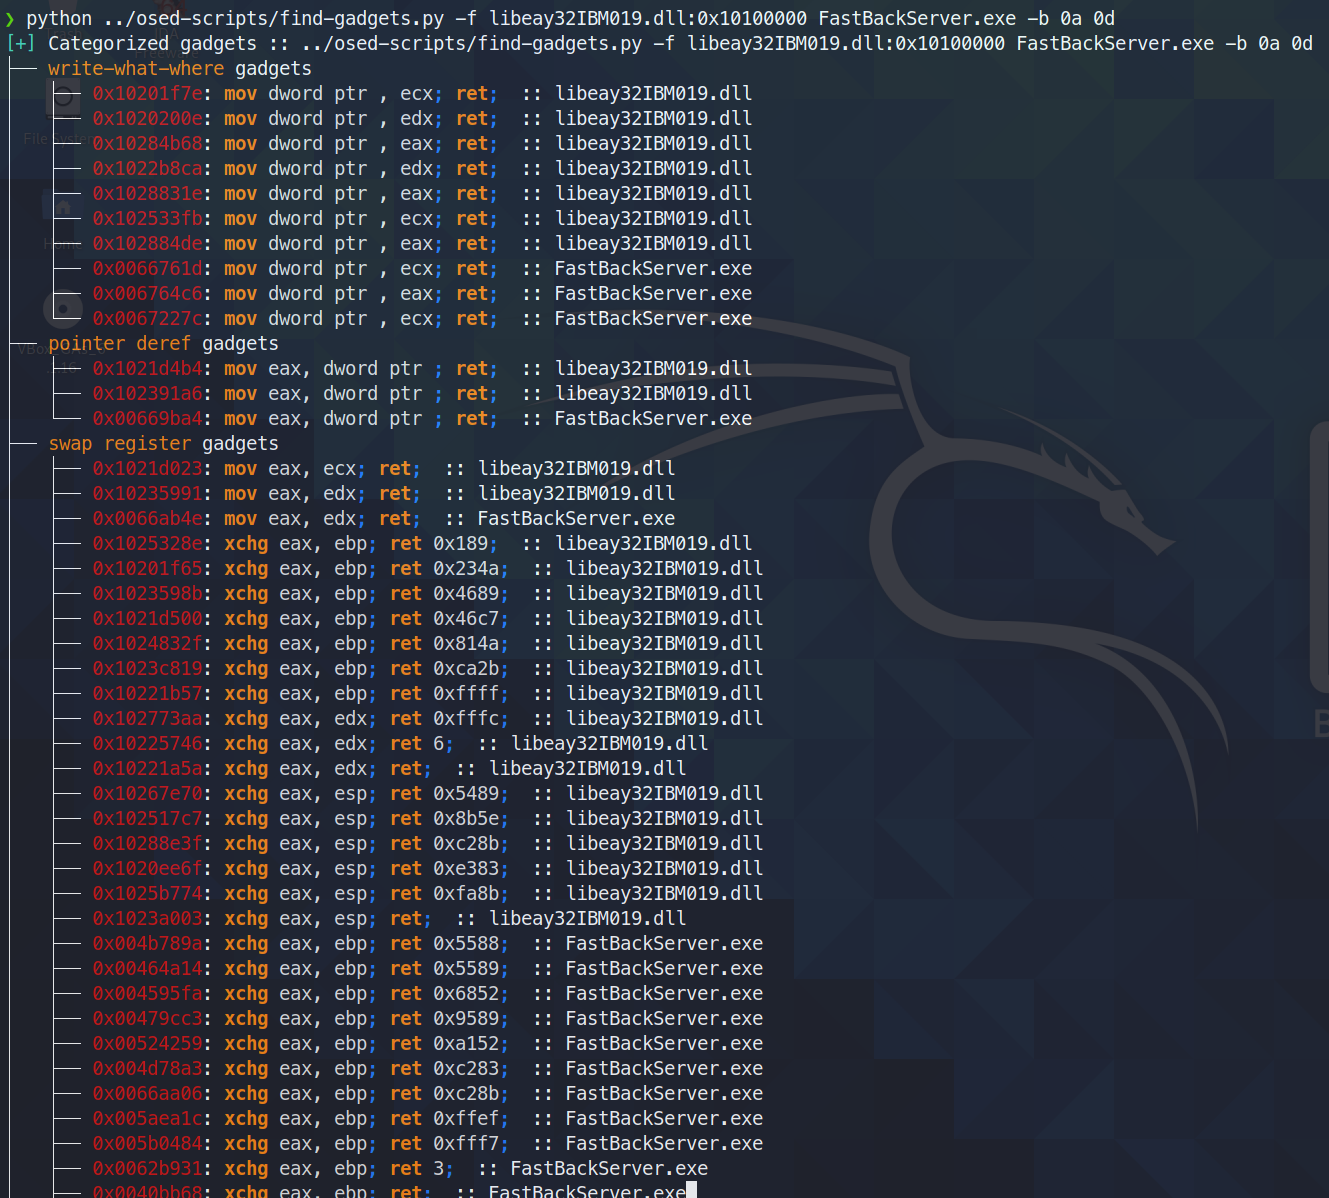 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 oddcod3/phantom-evasion
Python antivirus evasion tool
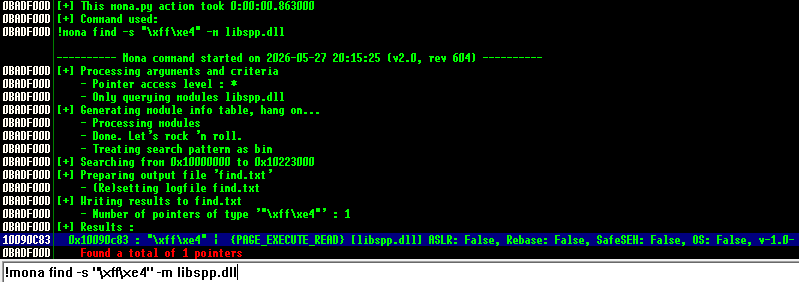 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 theman001/cve-2025-62215
CVE-2025-62215: Windows Kernel Race Condition + Double-Free EoP
 whu-enjoy/cve-2012-1889
这里保存着我学习CVE-2012-1889这个漏洞的利用所用到的文件