

sploit
 zznop/sploit
Go package that aids in binary analysis and exploitation
binary-analysisbinary-exploitationctf+6
zznop/sploitGo package that aids in binary analysis and exploitation
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
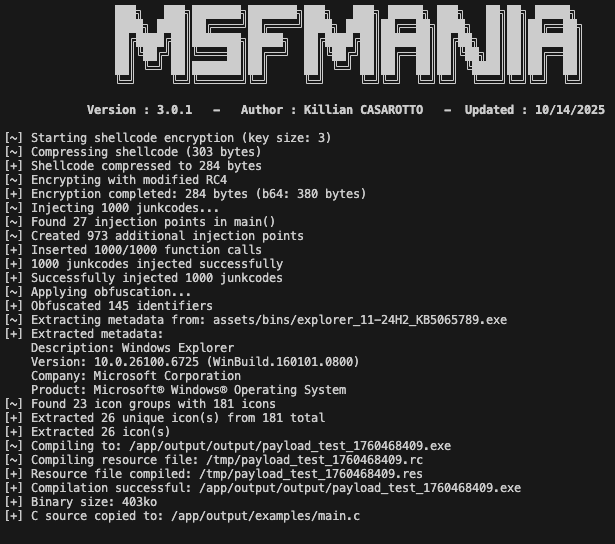 lepotekil/msfmania
Python AV Evasion Tools


 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.