

peda
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
exploit-frameworksexploitationreverse-engineering+5
longld/pedaPEDA - Python Exploit Development Assistance for GDB
 nytrorst/shellcodecompiler
Shellcode Compiler
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell

 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
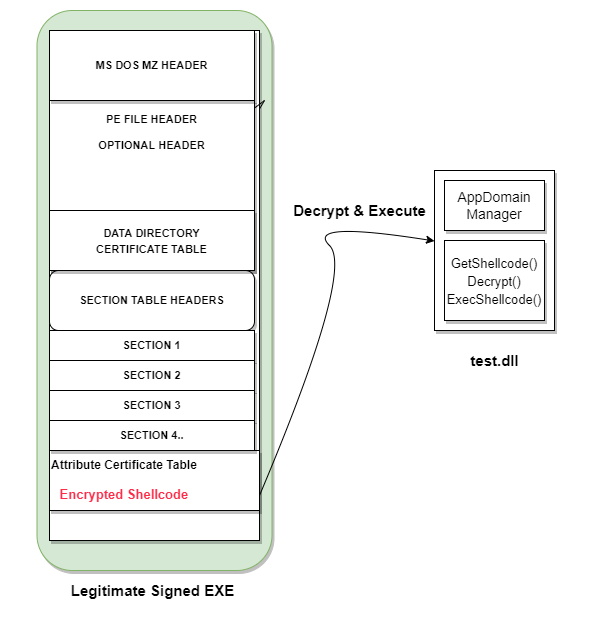 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 lepotekil/msfmania
Python AV Evasion Tools

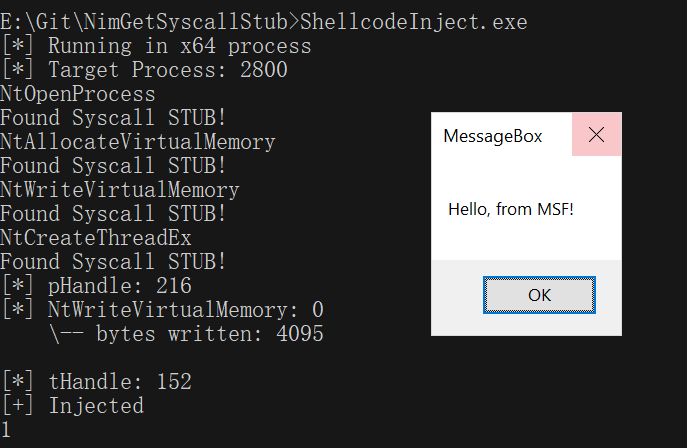 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…