
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
exploits preview

exploits

GitHubgkweb76/exploits

Collection of shellcode and proof-of-concept exploits for known vulnerabilities, intended for local testing and verifying software or network…

curated-resourcesexploitationpayload-development+3
2
9 years ago
exploitation-course preview

exploitation-course

GitHubashemery/exploitation-course

Offensive Software Exploitation Course

binary-exploitationeducationexploitation+7
2.5k3 years ago
libpeconv preview

libpeconv

GitHubhasherezade/libpeconv

Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…

binary-analysismalware-analysismemory-forensics+4
1.4k5 months ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.

binary-analysisbinary-exploitationmalware-analysis+3
3962 years ago
Lucky-Spark preview

Lucky-Spark

GitHubschich/lucky-spark

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.

binary-analysiscommand-and-controlexploitation+6
632 months ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
Rig-Exploit-for-CVE-2018-8174 preview

Rig-Exploit-for-CVE-2018-8174

GitHuborf53975/rig-exploit-for-cve-2018-8174

Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…

command-and-controlexploitationmalware-analysis+3
8 years ago
Rusty-Playground preview

Rusty-Playground

GitHubblacksnufkin/rusty-playground

Some Rust program I wrote while learning Malware Development
binary-analysisexploitationmalware-analysis+6
1621 year ago
the-backdoor-factory preview

the-backdoor-factory

GitHubsecretsquirrel/the-backdoor-factory

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
binary-exploitationexploitationmalware-analysis+6
3.4k2 years ago
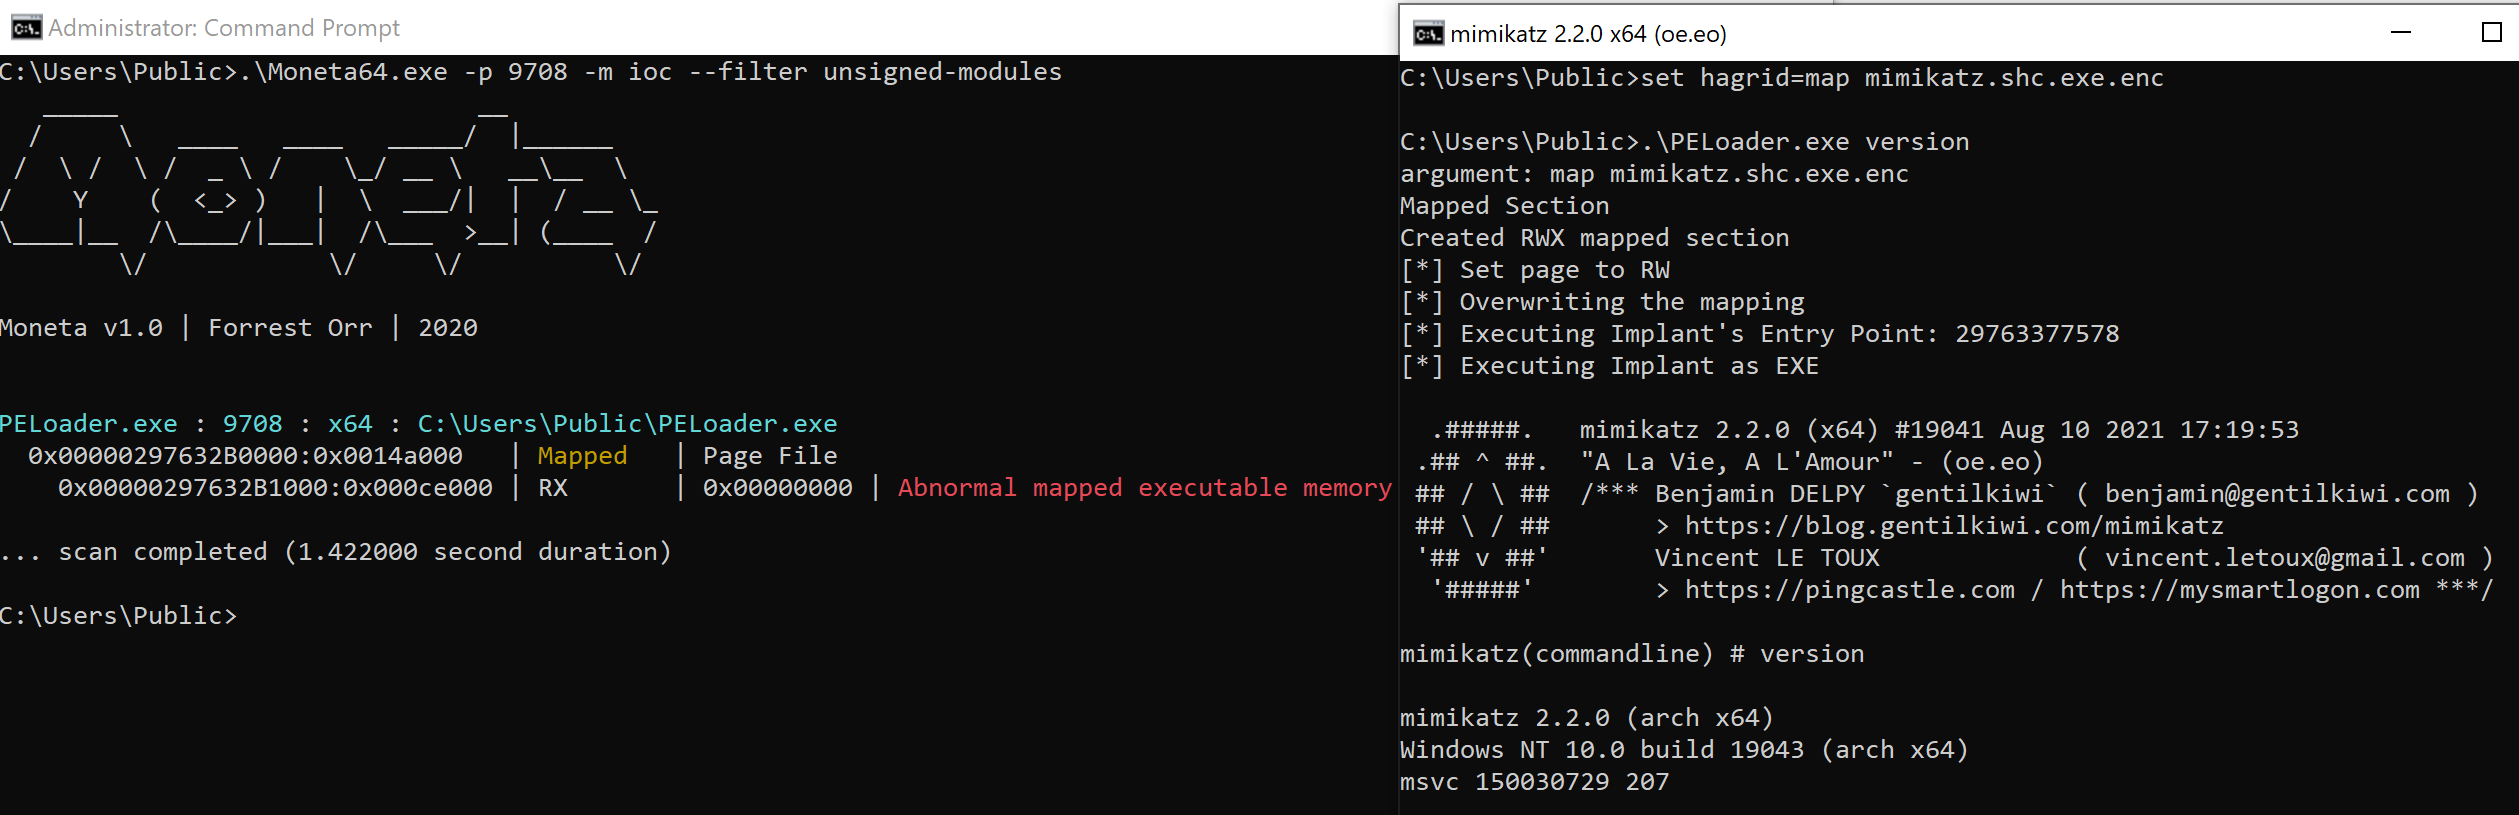
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques
binary-analysisexploitationmalware-analysis+4
4603 years ago
mkPIVM preview

mkPIVM

GitHubd7ead/mkpivm

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
exploitationmalware-analysispayload-generation+3
3871 month ago
Nim-RunPE preview

Nim-RunPE

GitHubs3cur3th1ssh1t/nim-runpe

A Nim implementation of reflective PE-Loading from memory
binary-exploitationexploitationmalware-analysis+3
2942 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

exploitationforensicsmalware-analysis+5
2282 years ago
Shelltropy preview

Shelltropy

GitHubkleiton0x00/shelltropy

A technique of hiding malicious shellcode via Shannon encoding.

exploitationmalware-analysispayload-development+1
2693 years ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
binary-exploitationexploitationmalware-analysis+3
3242 years ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
12610 months ago
flowinspect preview

flowinspect

GitHub7h3ram/flowinspect

A Network Inspection Tool

forensicsfuzzingintrusion-detection+5
828 years ago
byvalver preview

byvalver

GitHubumpolungfish/byvalver

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

binary-analysisexploitationmachine-learning+6
627 months ago
Previous12Next