
SysWhispers
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
exploitationids-ips-evasionpayload-development+3
jthuraisamy/syswhispersAV/EDR evasion via direct system calls.
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
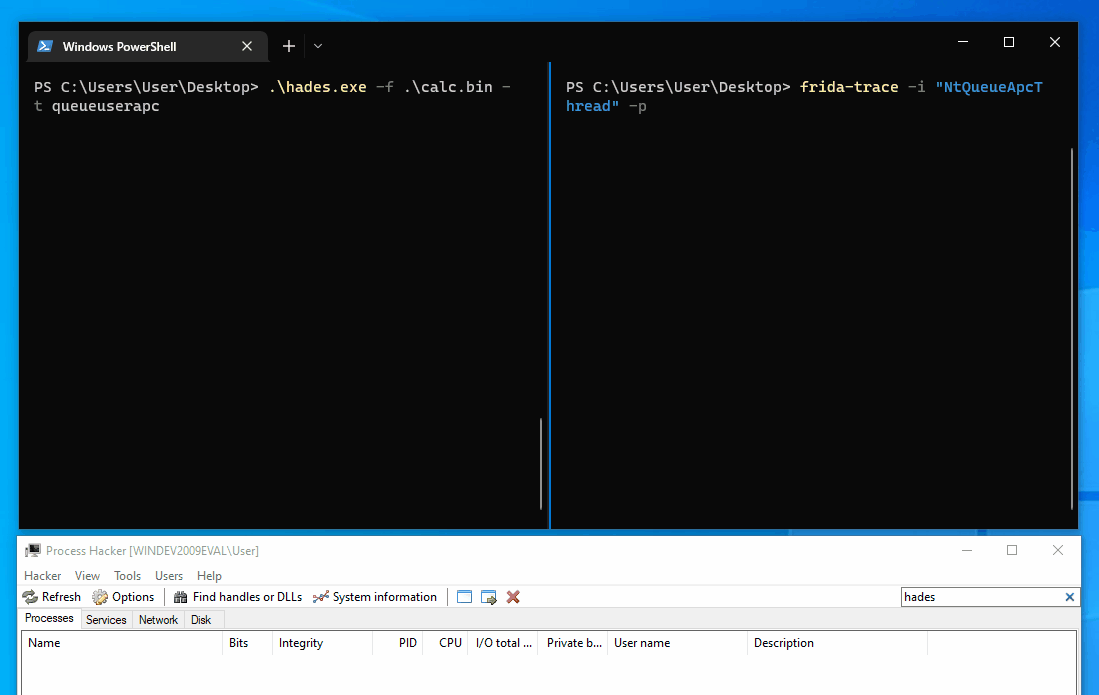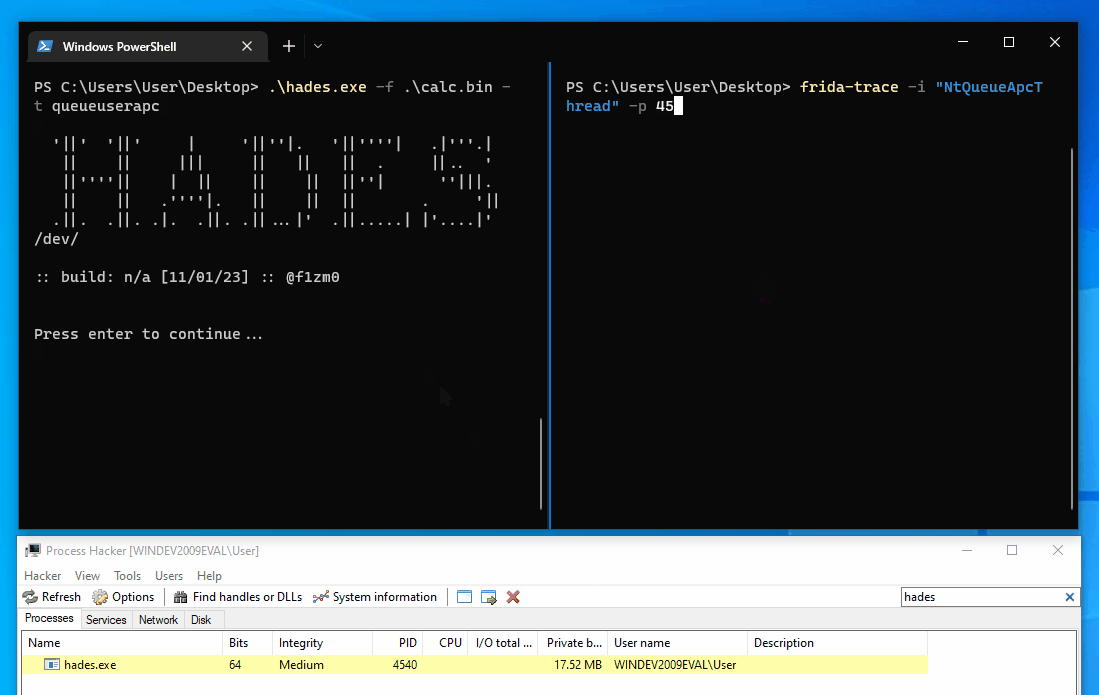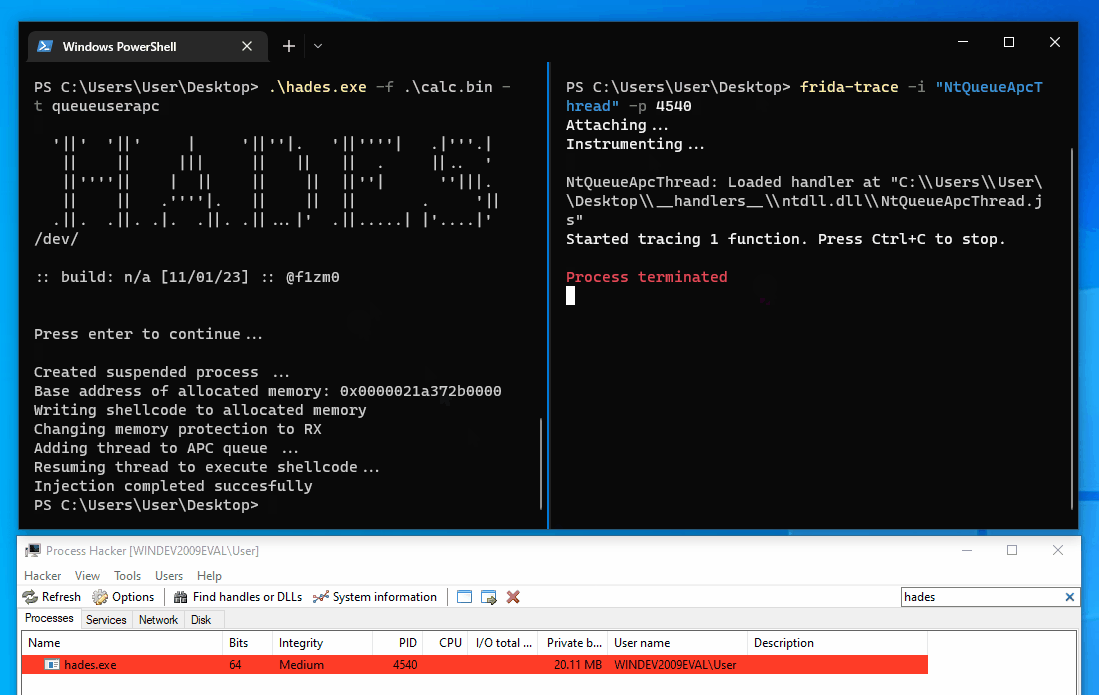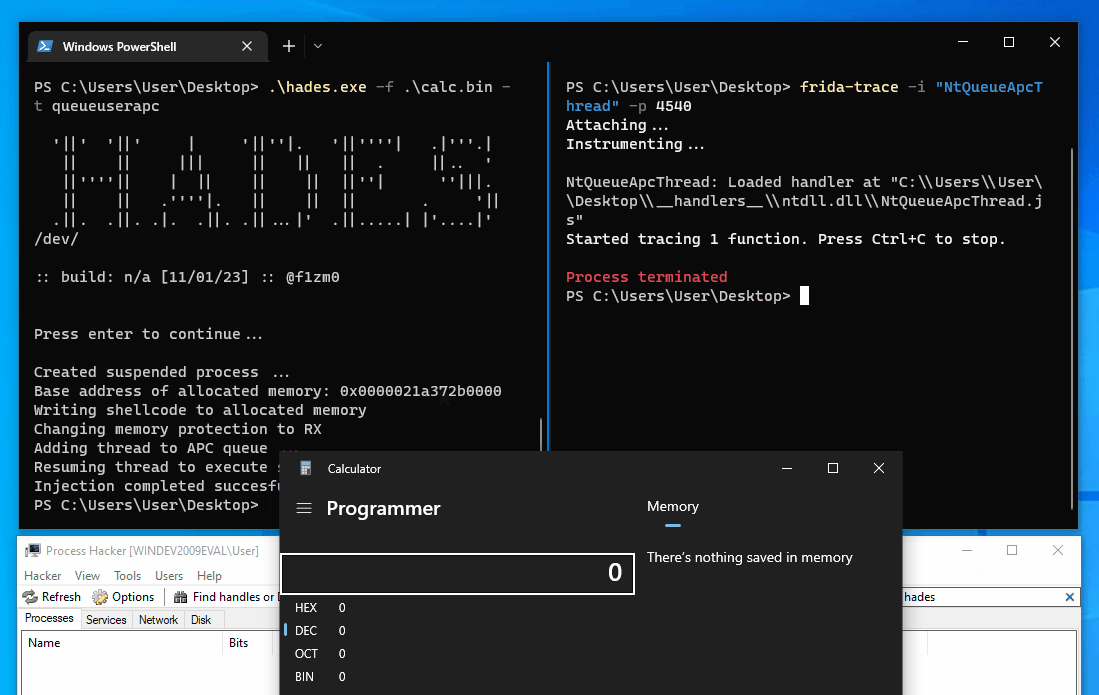 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
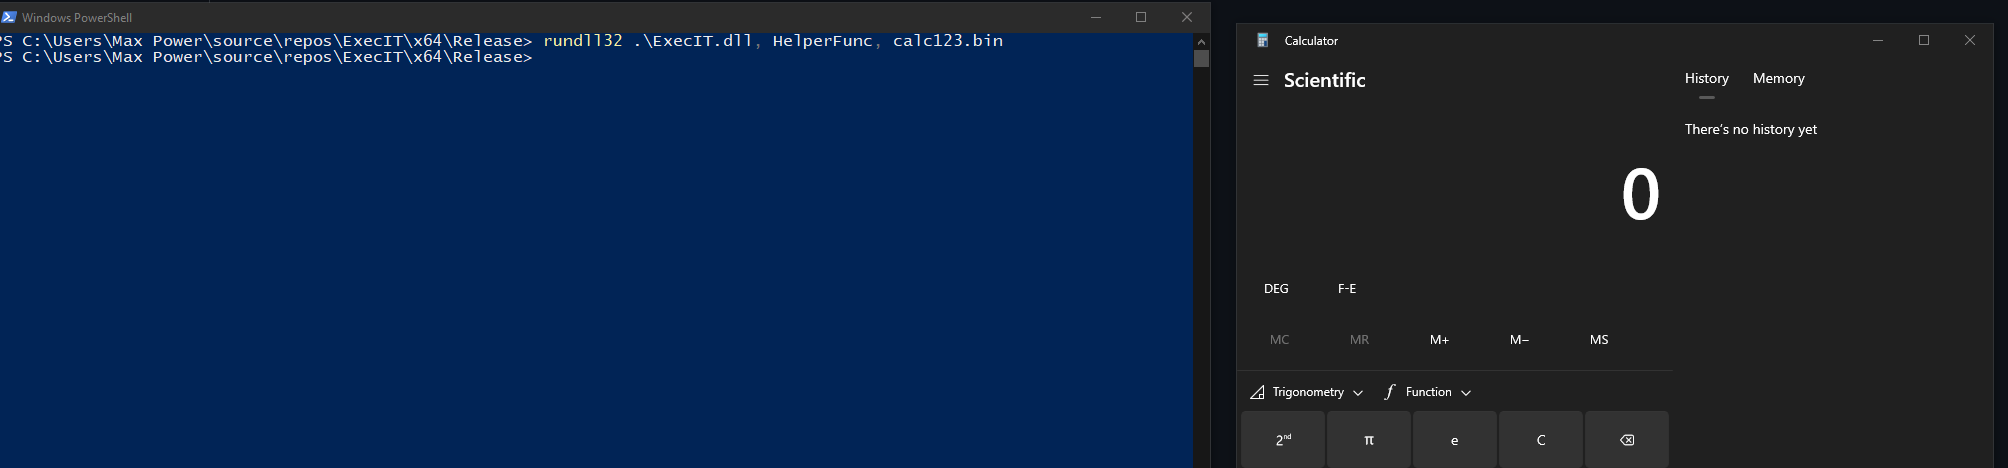 florylsk/execit
Execute shellcode files with rundll32