
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
251 results
HandleKatz preview

HandleKatz

GitHubcodewhitesec/handlekatz

PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…

defensive-toolsmemory-forensicspayload-generation+3
596
3 years ago
DKMC preview
Archived

DKMC

GitHubmr-un1k0d3r/dkmc

DKMC - Dont kill my cat - Malicious payload evasion tool
command-and-controlpayload-generationpenetration-testing+3
1.4k6 years ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
542 years ago
LiquidSnake preview

LiquidSnake

GitHubriccardoancarani/liquidsnake

Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
lateral-movementpayload-generationred-teaming+1
3505 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
632 months ago
ruler preview

ruler

GitHubsensepost/ruler

A tool to abuse Exchange services
email-securityexploitationinformation-gathering+3
2.3k2 years ago
Graffiti preview

Graffiti

GitHubekultek/graffiti

A tool to generate obfuscated one liners to aid in penetration testing
payload-developmentpayload-generationpenetration-testing+1
1807 years ago
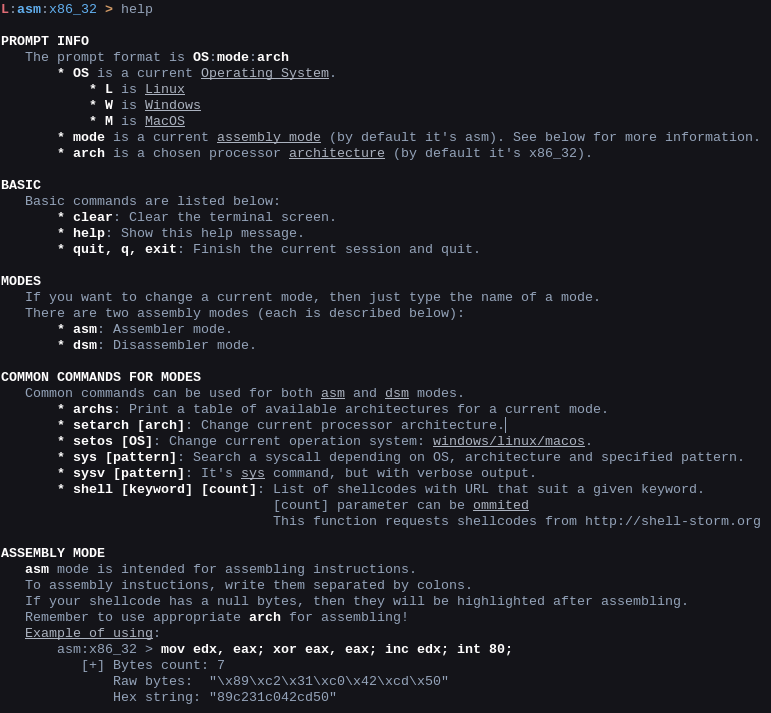
shellen preview

shellen

GitHubkonatabrk/shellen

:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
binary-analysisctfeducation+5
9075 years ago
CVE-2026-31431-Linux-Copy-Fail preview

CVE-2026-31431-Linux-Copy-Fail

GitHubdullpurple-sloop726/cve-2026-31431-linux-copy-fail

Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.

binary-exploitationeducationexploitation+4
32 days ago
BlobRunner preview

BlobRunner

GitHuboalabs/blobrunner

Quickly debug shellcode extracted during malware analysis

debuggersmalware-analysisreverse-engineering+1
6414 years ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
binary-analysisbinary-exploitationmalware-analysis+3
3912 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

exploitationforensicsmalware-analysis+5
2292 years ago
CVE-2021-40449 preview

CVE-2021-40449

GitHubhakivvi/cve-2021-40449

Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
binary-exploitationexploitationmemory-forensics+4
474 years ago
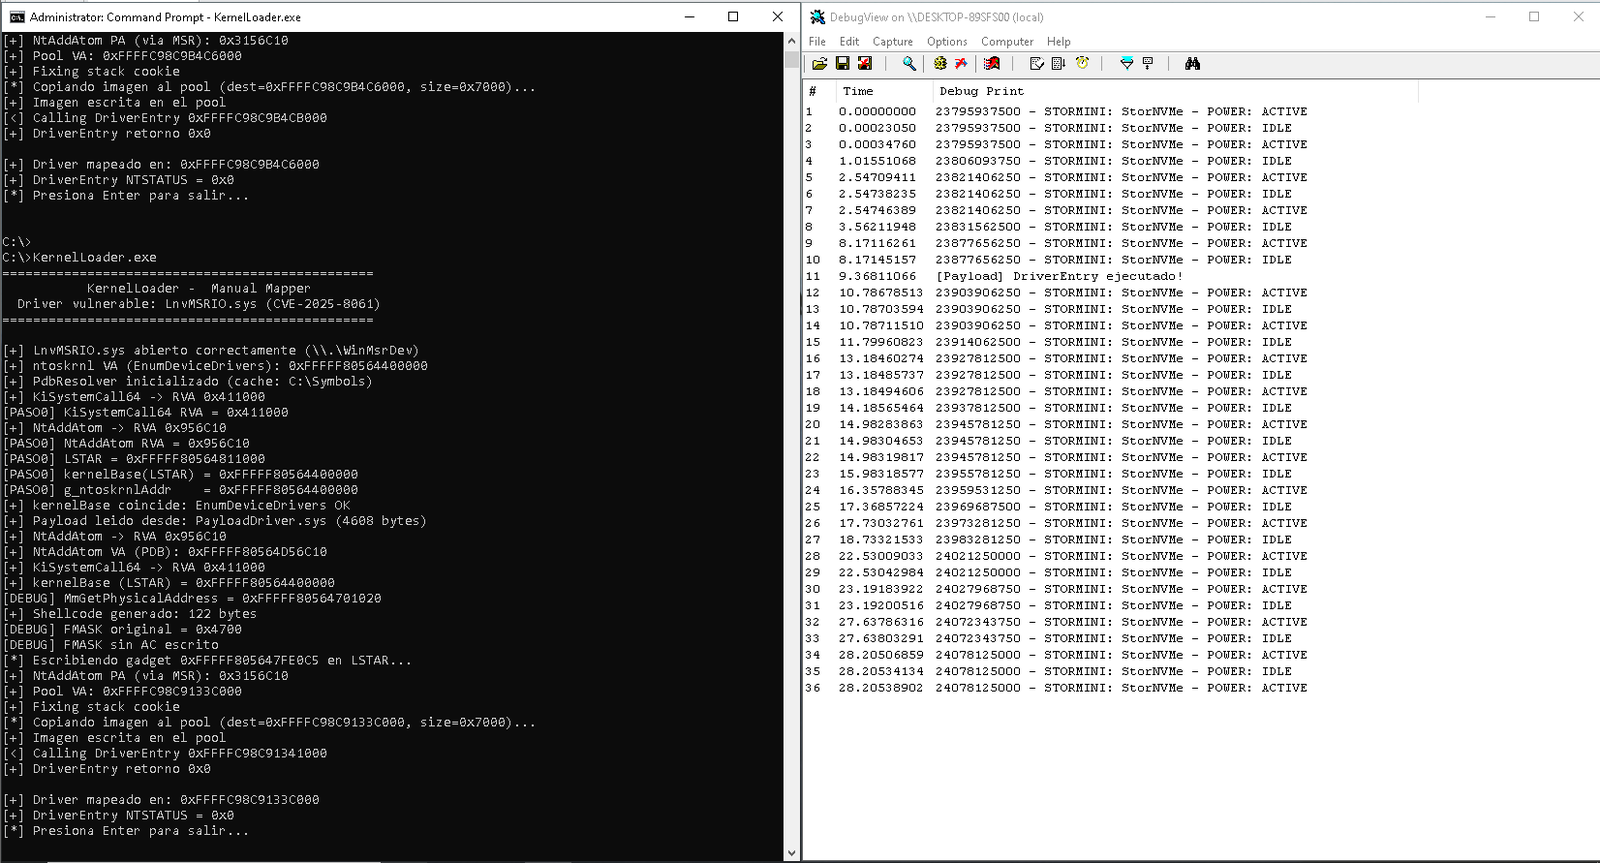
MSRMapper preview

MSRMapper

GitHubull0a/msrmapper

Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
binary-exploitationexploitationmemory-forensics+6
17 hours ago
Killer preview

Killer

GitHub0xhossam/killer

Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.

anti-boteducationexploitation+4
8472 years ago
Shinigami preview

Shinigami

GitHubbuzzer-re/shinigami

A dynamic unpacking tool
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
1523 years ago
CVE-2025-0282-Full-version preview

CVE-2025-0282-Full-version

GitHubanonstorks/cve-2025-0282-full-version

# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
binary-exploitationeducationexploitation+5
41 year ago
SMBRat preview

SMBRat

GitHuboperatorequals/smbrat

A Windows Remote Administration Tool in Visual Basic with UNC paths

command-and-controlexploitationlateral-movement+8
227 years ago
Previous12…14Next