

aether
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
66
0xsp-srd/aetherWindows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 buzzer-re/shinigami
A dynamic unpacking tool
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
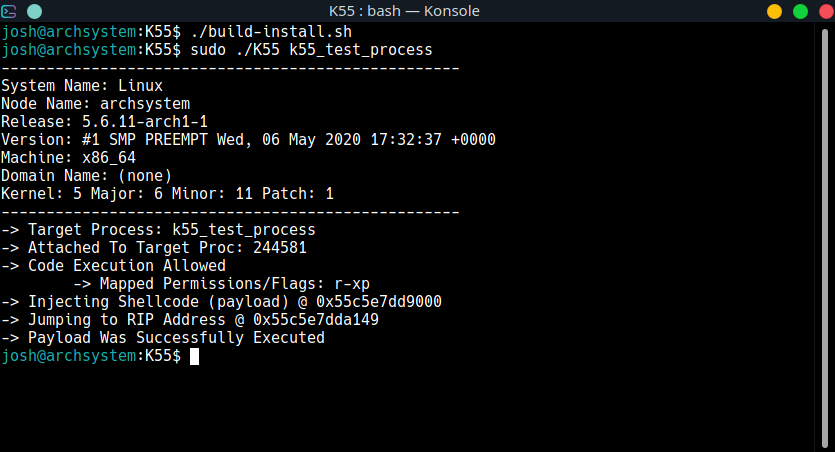
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 trungnguyen1909/cve-2019-8781-macos
Exploit POC for the bug CVE-2019-8781, found by @LinusHenze
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
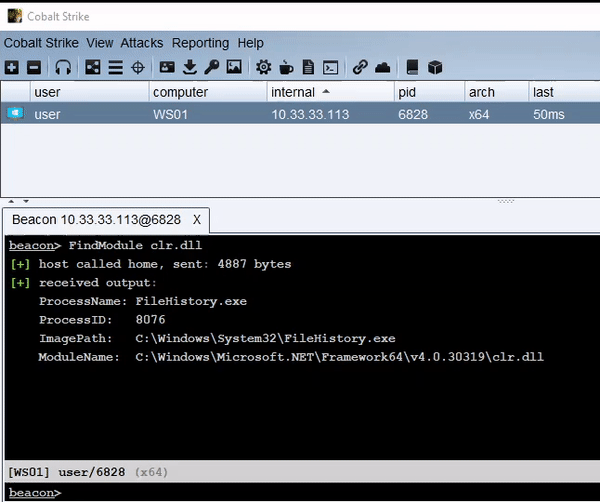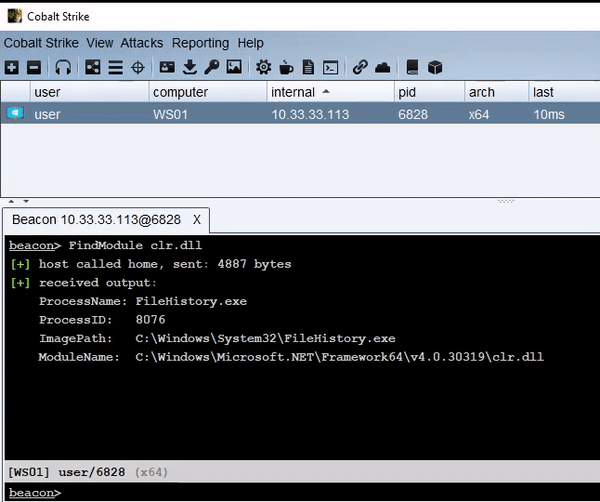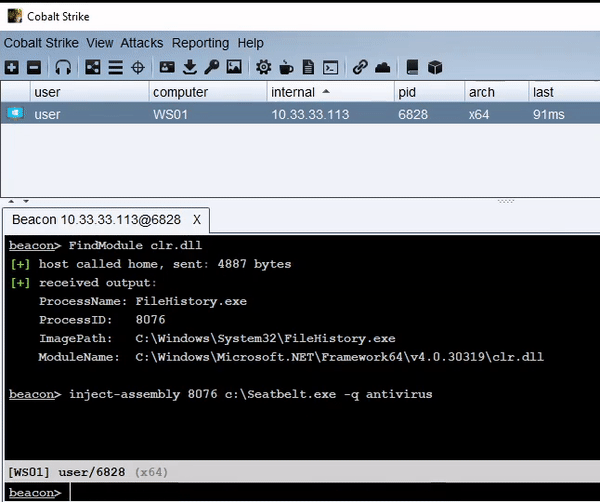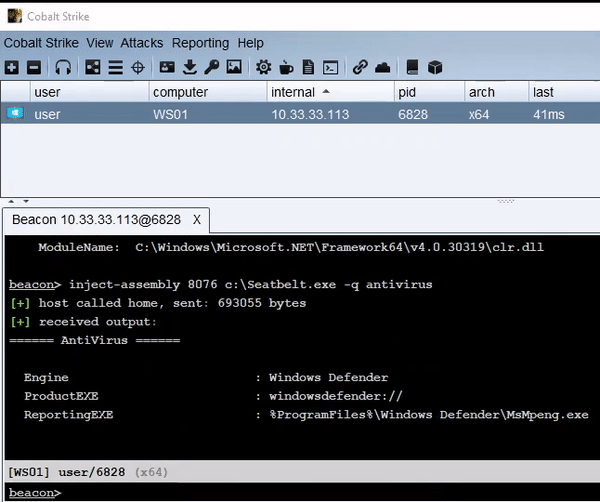 kyleavery/inject-assembly
Inject .NET assemblies into an existing process
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept
 gmh5225/anti_suspend
Protect process by shellcode
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions