
Archived
CVE-2015-8522.RCE
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
binary-exploitationexploitationexploit-frameworks+8
damariion/cve-2015-8522.rceExploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 mrr0b0t19/cve-2024-6387-exploit-poc
Proof-of-concept exploit for CVE-2024-6387 targeting vulnerable OpenSSH servers via heap manipulation and race condition to achieve remote code…
 svchostmm/cve-2024-25600-mass
Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.
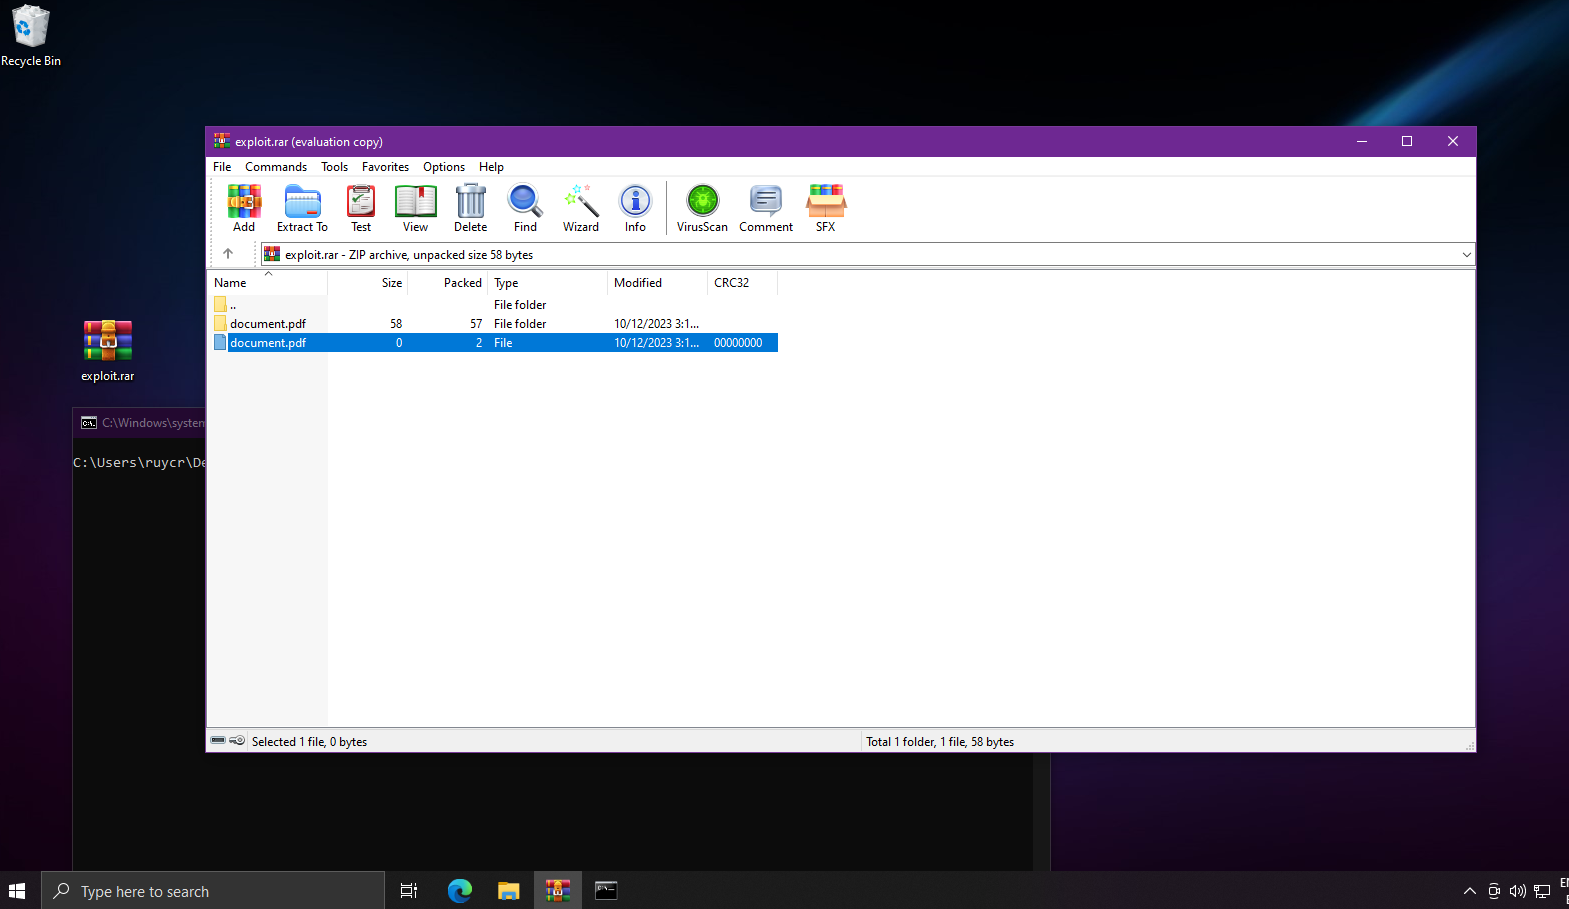 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 tau-hub/firefox-cve-2016-9079
Manual exploit for Firefox RCE CVE-2016-9079 with customizable shellcode, served via HTTP for remote code execution on vulnerable Windows systems.
 engranaabubakar/cve-2023-46818
Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
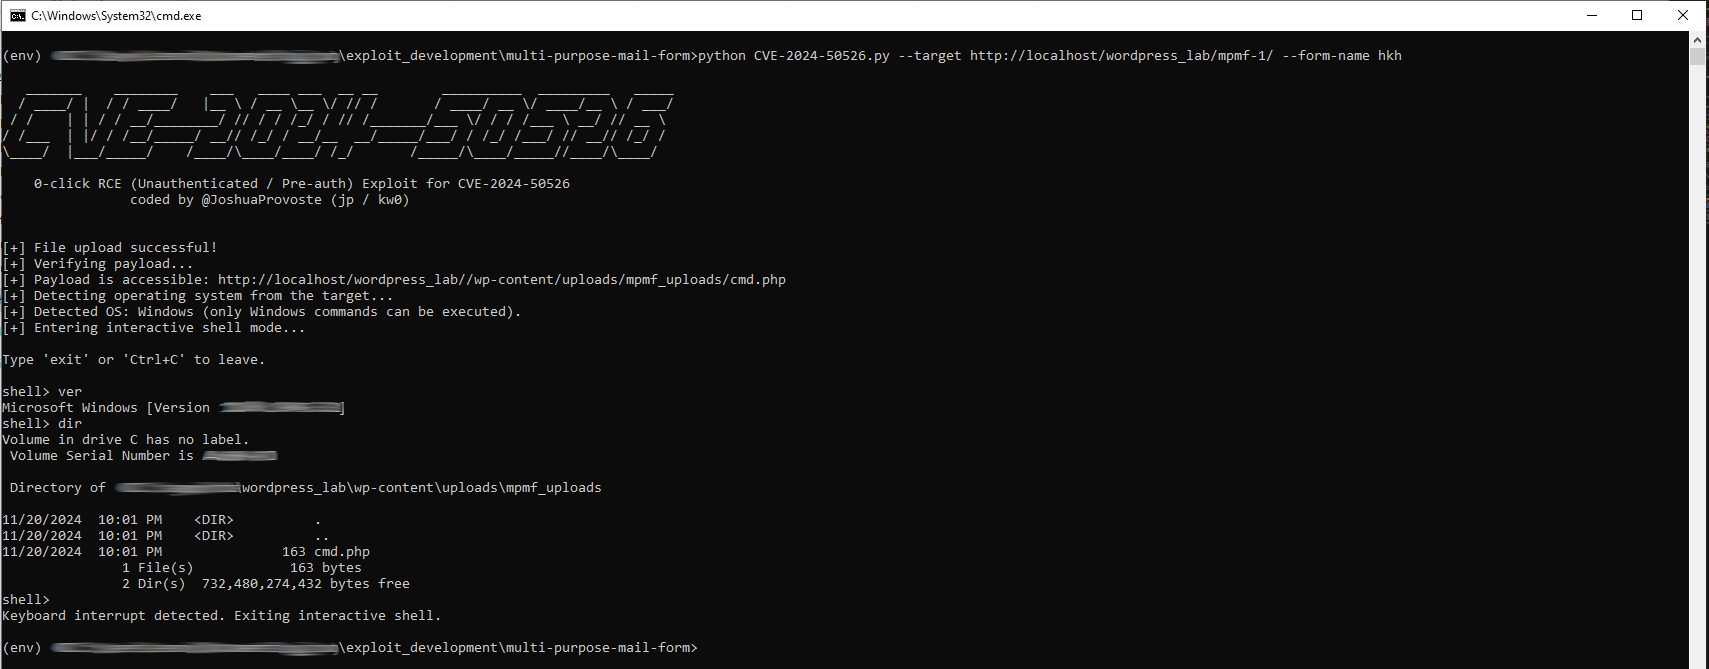 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 pentestical/cve-2020-9484
Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…