
Dirty-Pipe
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
binary-exploitationeducationexploitation+4
3
bytereaper77/dirty-pipeProof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 im-hanzou/jbwper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2022-4061 - JobBoardWP < 1.2.2 - Unauthenticated Arbitrary File Upload
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 bkreisel/cve-2022-41343
🐍 Python Exploit for CVE-2022-23935
 bkreisel/cve-2022-46169
🐍 Python Exploit for CVE-2022-46169
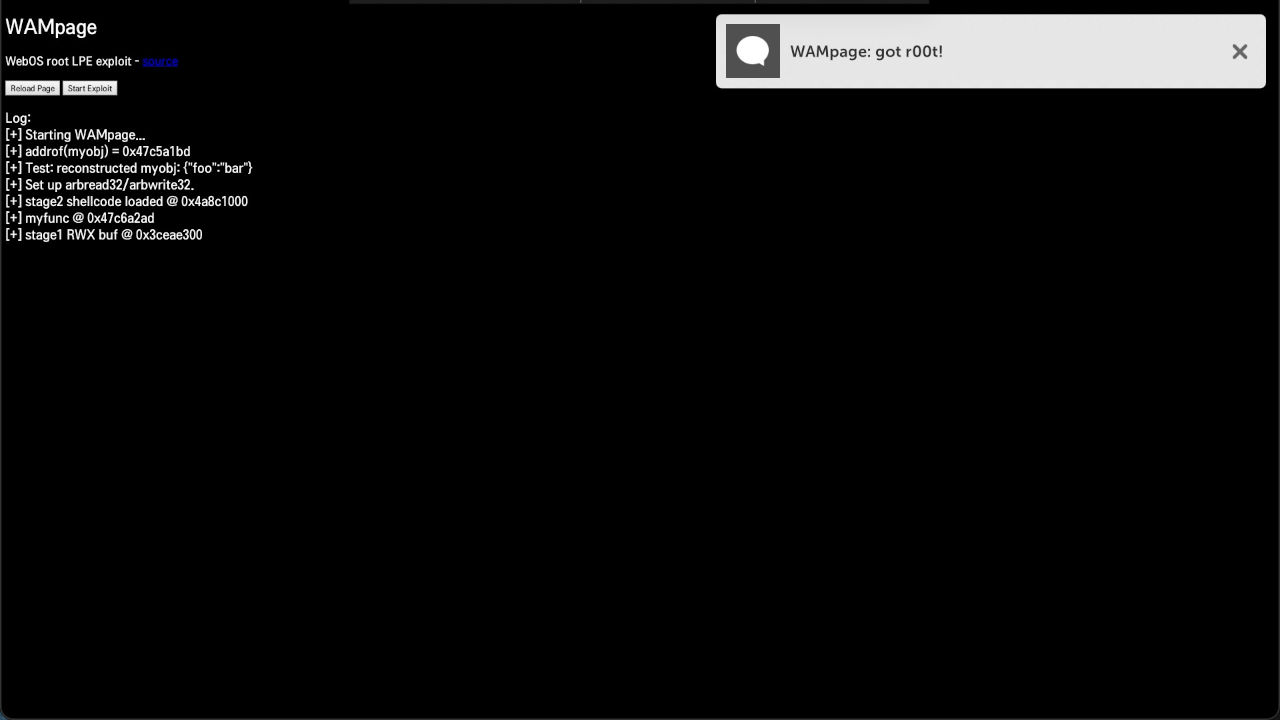 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
 shotokhan/cve_2022_0847_shellcode
Implementation of CVE-2022-0847 as a shellcode
 randallbanner/spring-cloud-function-vulnerability-cve-2022-22963-rce
Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…
 marcingadz/spring-rce-poc
Testing CVE-2022-22968
 kmahyyg/cve-2022-22947
Exploit for CVE-2022-22947 in Spring Cloud Gateway, enabling remote code execution via maliciously crafted requests with integrated Godzilla memshell…
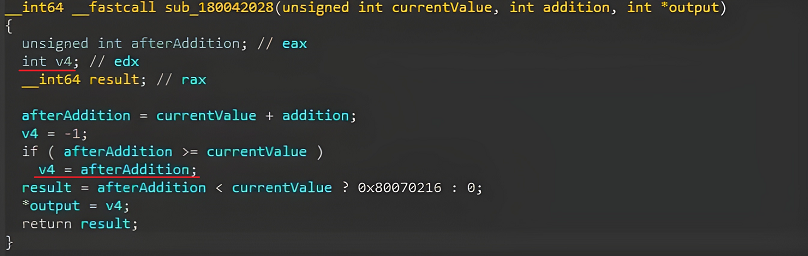 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 0xsojalsec/cve-2022-1609
Bash poc for CVE-2022-1609 WordPress Weblizar Backdoor
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
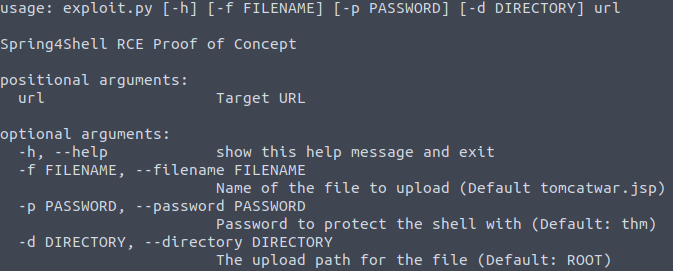 lucaspdiniz/cve-2022-22965
Spring4Shell Vulnerability RCE - CVE-2022-22965
 catherines77/activemq-exptools
Apache ActiveMQ漏洞综合利用工具(CVE-2015-5254,CVE-2016-3088,CVE-2022-41678,CVE-2023-46604,CVE-2024-32114,CVE-2026-34197,CVE-2026-40466, CVE-2026-42588)
 0x7n6/cve-2022-24500
Standalone exploit for CVE-2022-24500 targeting Windows SMB, generating and executing shellcode to deliver a reverse Meterpreter payload.