
ROP_ROCKET
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
binary-exploitationexploitationexploit-frameworks+4
182
bw3ll/rop_rocketROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 darthton/blackbone
Windows memory hacking library
 nccgroup/winpayloads
Undetectable Windows Payload Generation
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
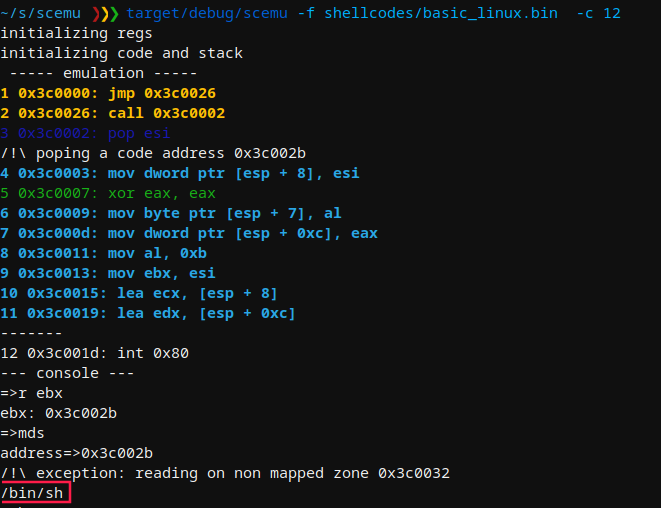 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
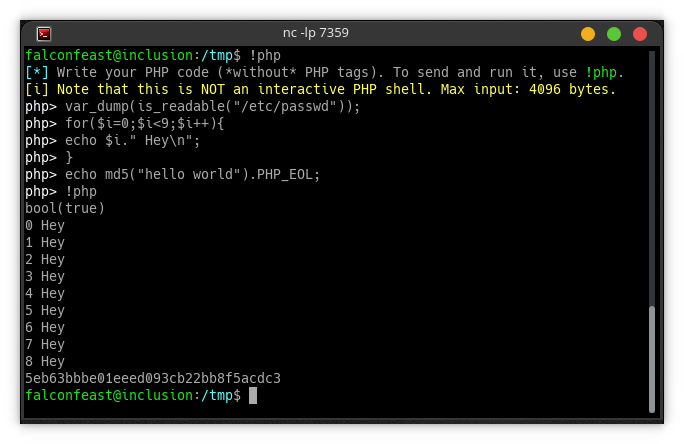 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
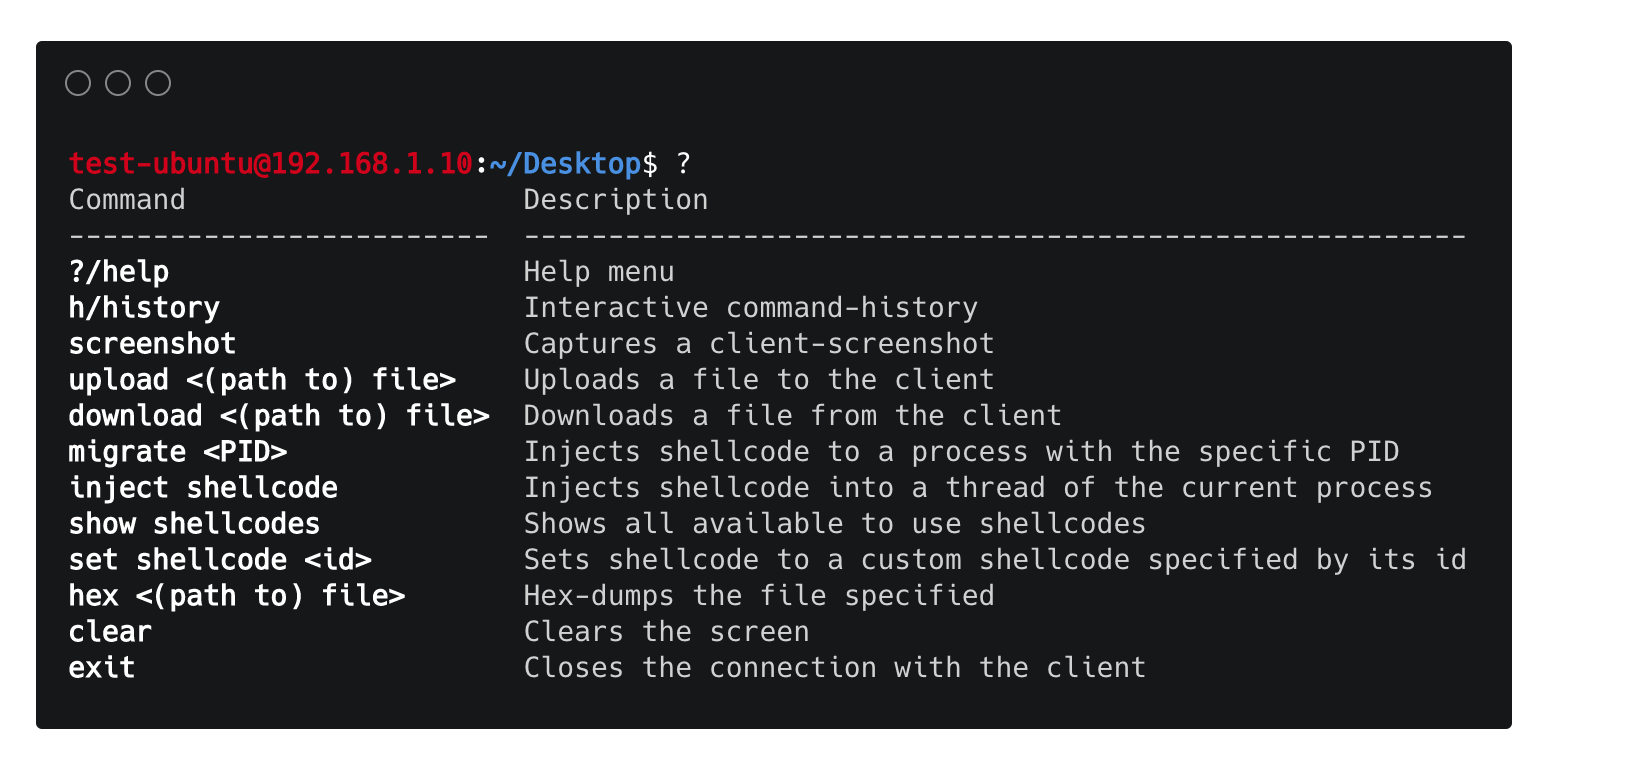 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
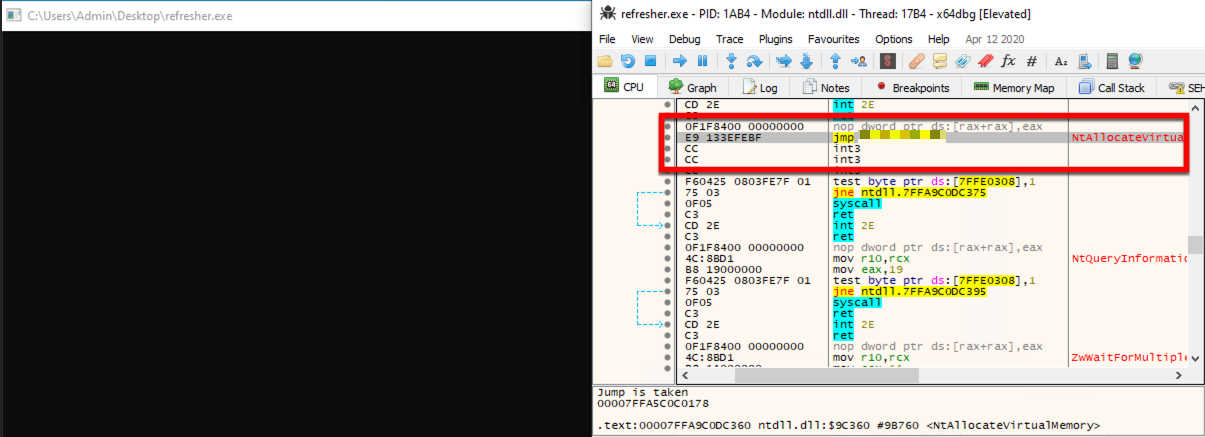 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
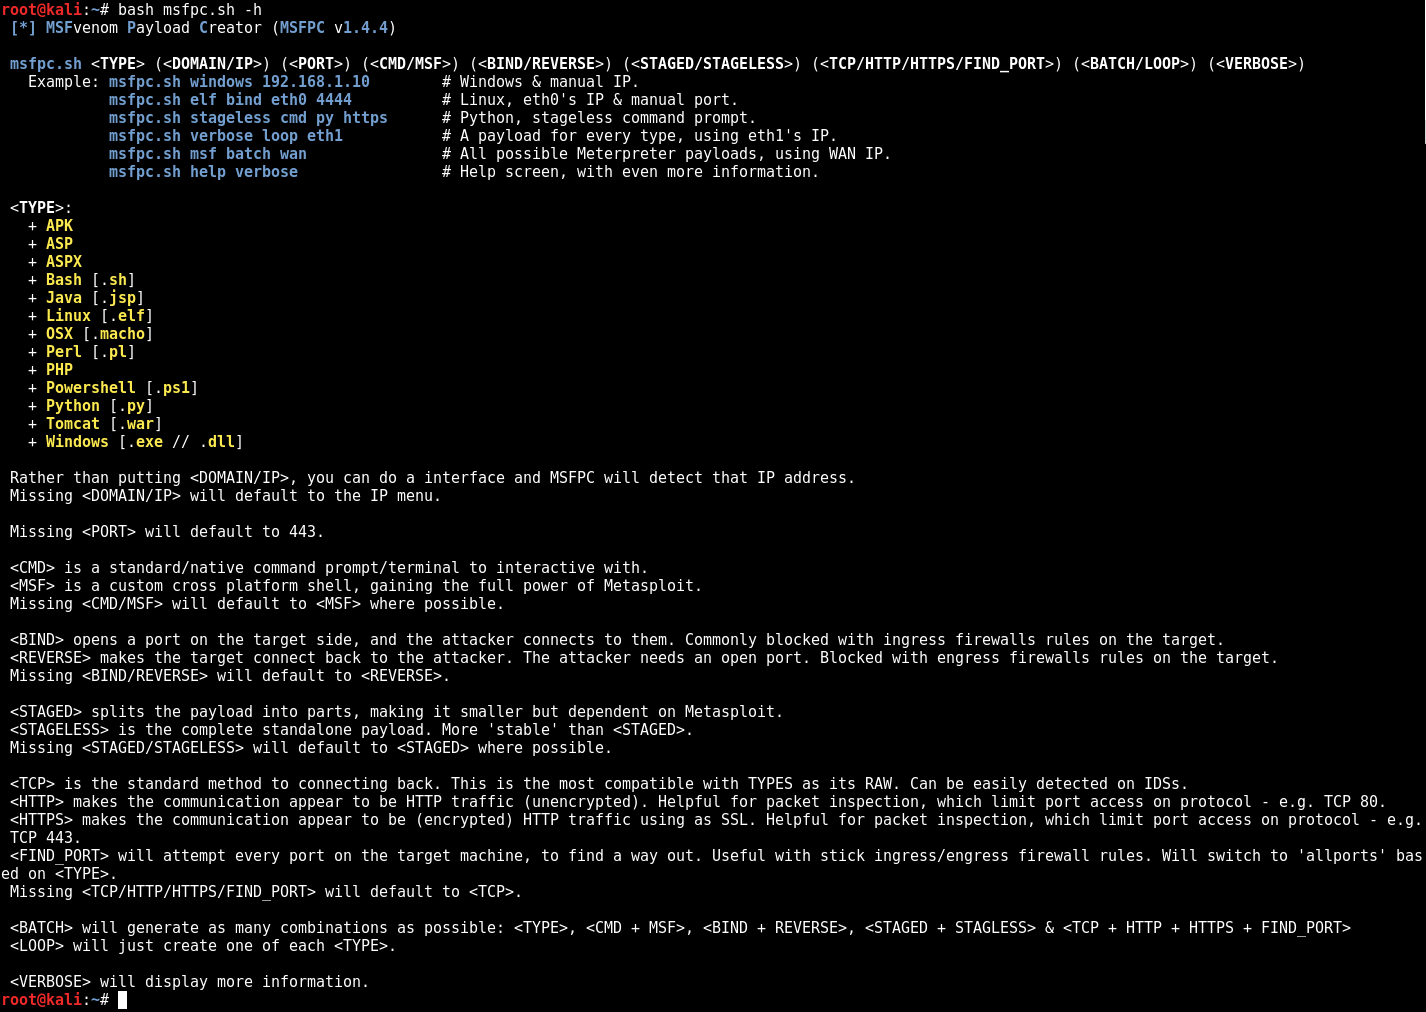 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit