

unicorn
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
command-and-controlexploit-frameworksids-ips-evasion+8
3.9k
trustedsec/unicornUnicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
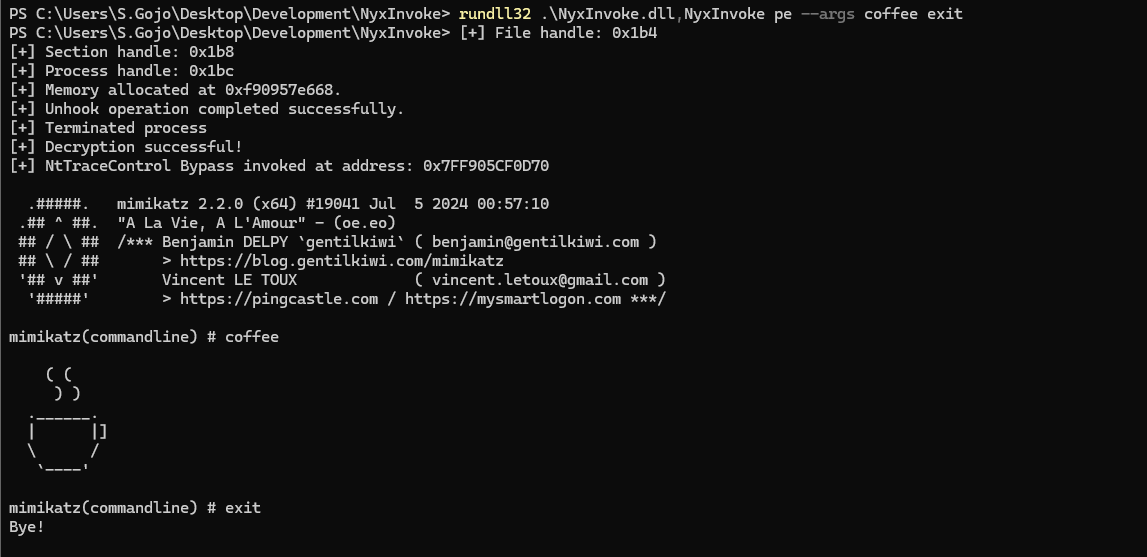 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 w01fh4cker/cve-2020-0688-gui
GUI Exploit Tool for CVE-2020-0688(Microsoft Exchange default MachineKeySection deserialize vulnerability)
 im-hanzou/jbwper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2022-4061 - JobBoardWP < 1.2.2 - Unauthenticated Arbitrary File Upload
 giovannipajeu1/cve-2024-23743
Automated exploit tool for CVE-2024-23743 targeting Notion macOS via RunAsNode and enableNodeClilnspectArguments, enabling remote code execution and…
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
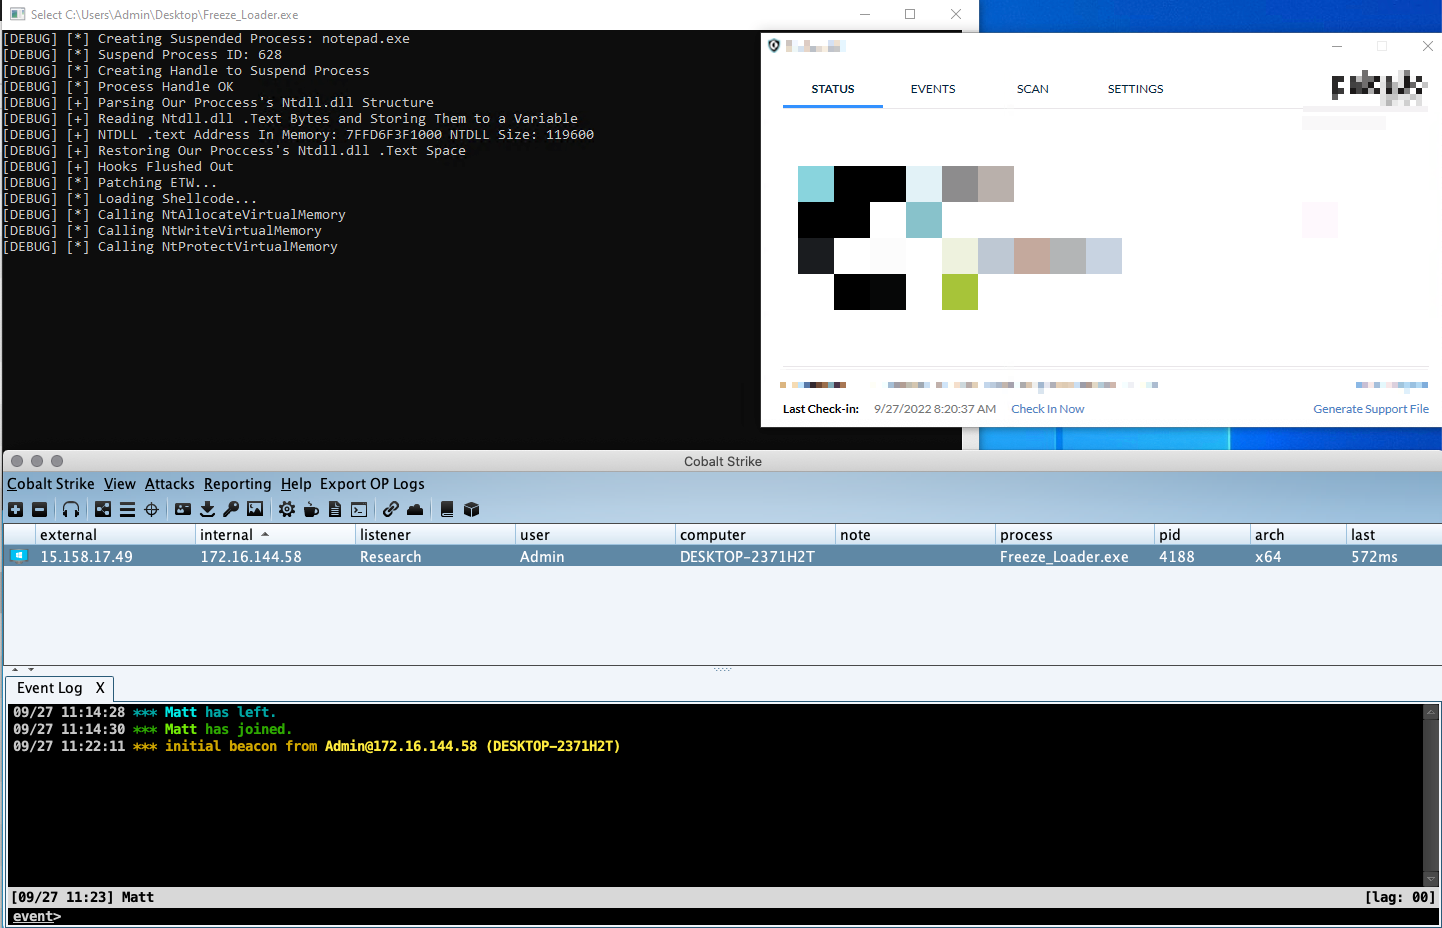 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 optiv/freeze.rs
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST
 stivenhacker/ghoststrike
C++ process hollowing injector that encrypts and obfuscates shellcode with XOR, Base64, and dynamic API resolution to deploy stealthy reverse shells…