

OffensiveCpp
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
adversarial-attackcurated-resourcesexploitation+6
773
lsecqt/offensivecppThis repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
 bishopfox/sliver
Adversary Emulation Framework
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
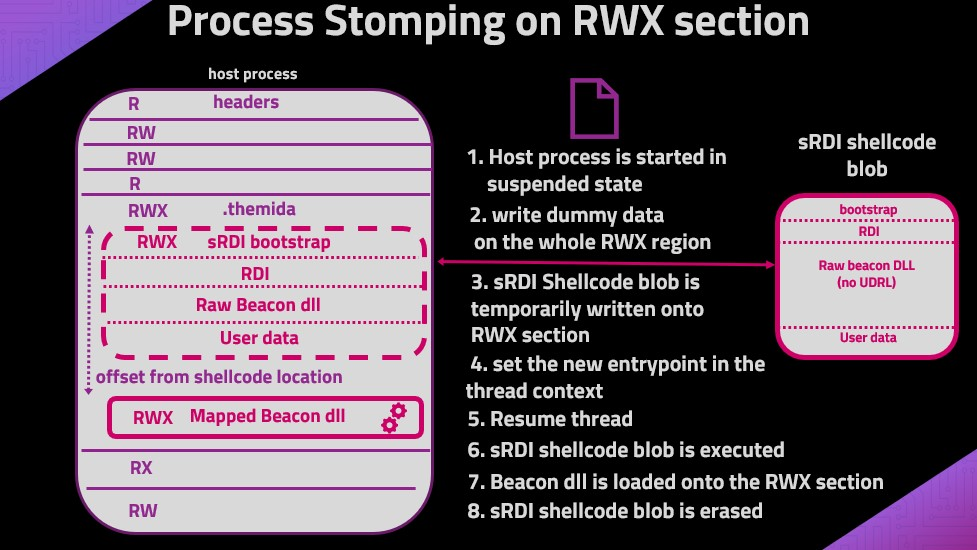 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 damariion/cve-2015-1925.rce
Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 mrk336/cve-2025-27480
CVE-2025-27480 exposes a buffer overflow in OpenSSH 8.9p1 via a malformed SSH_USERAUTH packet. Attackers can inject shellcode and gain SYSTEM-level…