
nimvoke
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
ids-ips-evasionpayload-developmentpost-exploitation+2
nbaertsch/nimvokeIndirect syscalls + DInvoke made simple.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
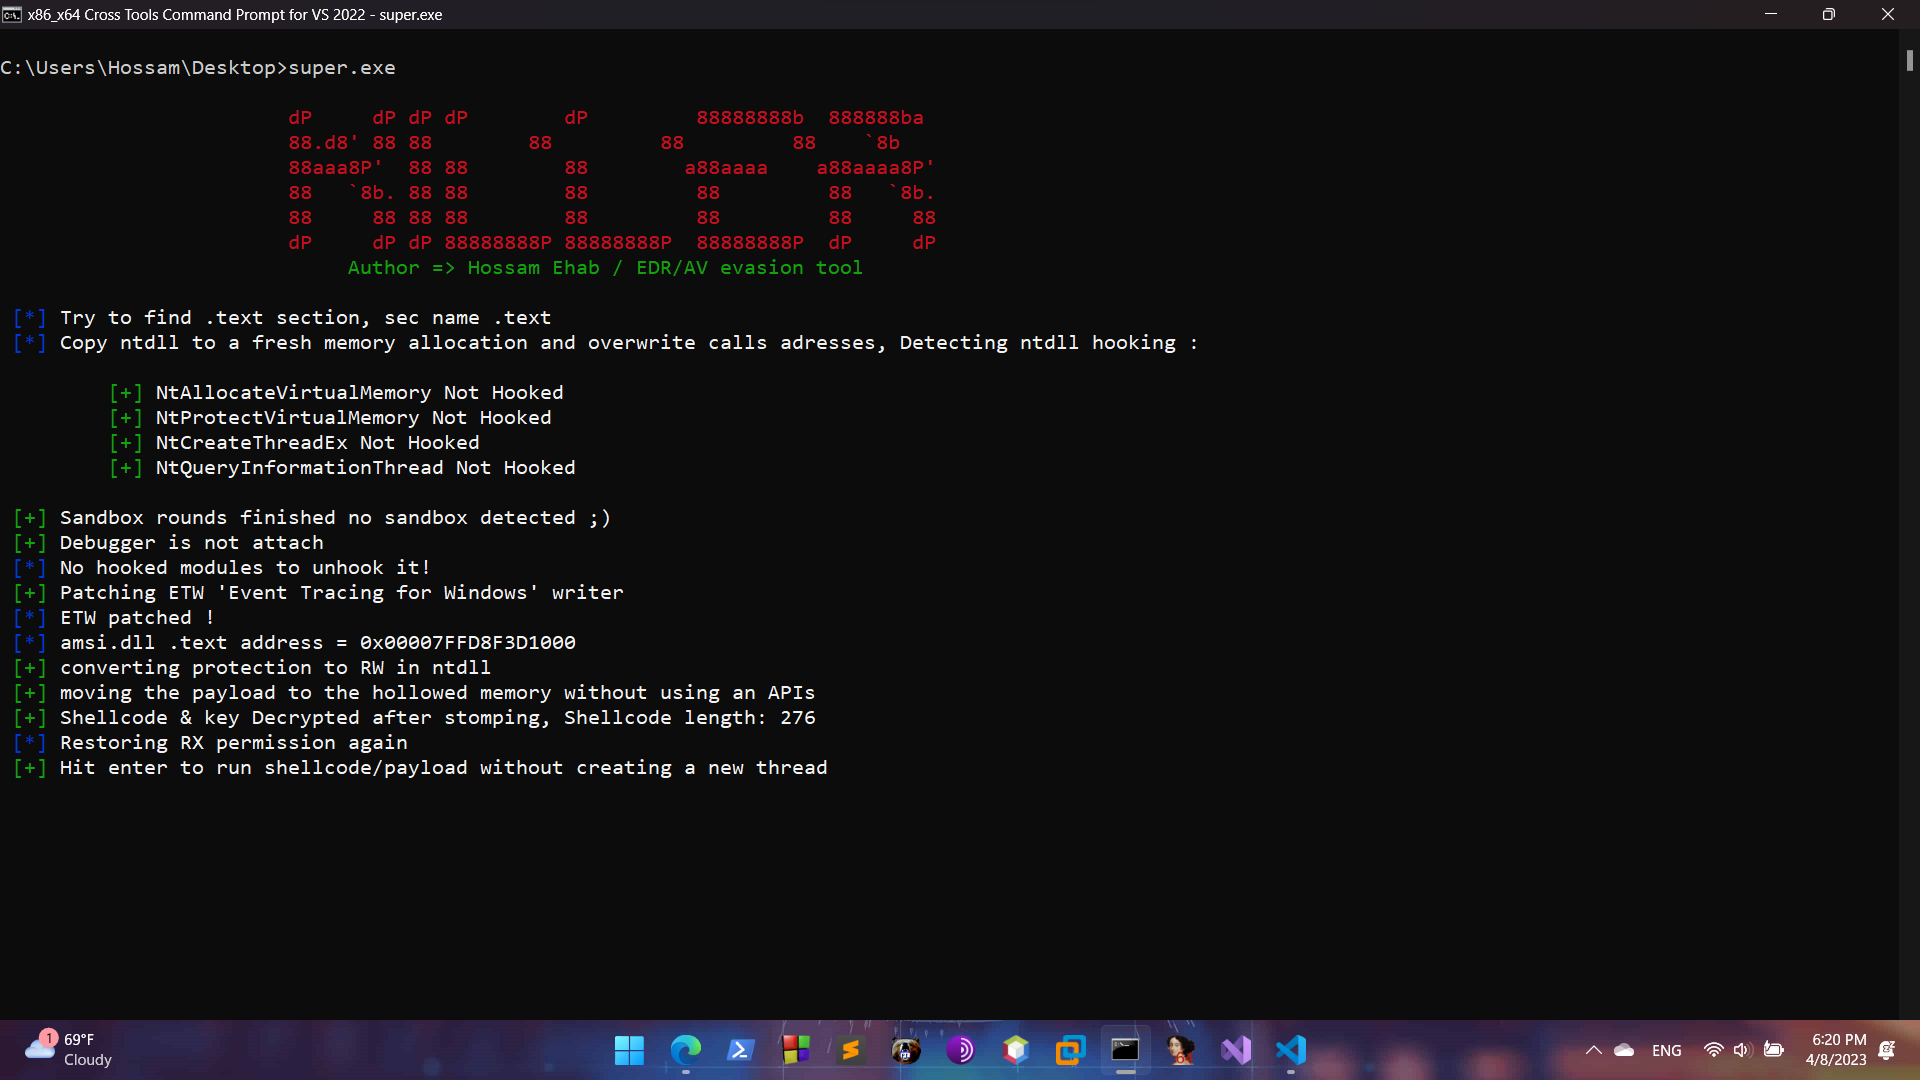 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
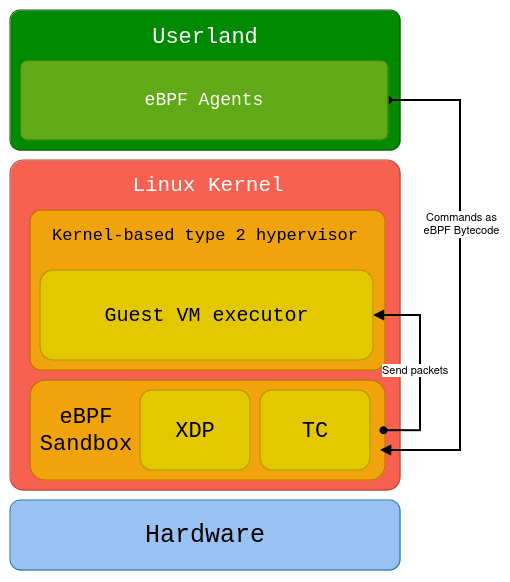 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 tachibana51/cve-2013-2028-x64-bypass-ssp-and-pie-poc
this is not stable
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 k3ystr0k3r/cve-2026-24061
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass